
If your Jira environment relies on integrations, automation, scripts, or any external services, your REST APIs are probably bridging them together. But if you're relying on basic security measures like passwords, you're creating unnecessary risk, especially in SSO-enabled environments.
According to TechTarget's report Securing the API Attack Surface, 92% of surveyed organizations experienced at least one API security incident in 2023.
Even the average number of API attacks per organization per year has increased by 113% in 2025.
That's why securing Jira APIs without breaking integrations should be on top of your priority list in 2026.
Why Jira REST API Security Matters More Than Ever
Every REST API endpoint is a potential entry point to your system's sensitive data. Jira REST APIs provide access to:
- Issue Data
- Project Information
- Workflows
- Users
- Permissions
- Configuration Settings
- Administrative Operations
For example, APIs often rely on default authentication methods, such as basic username and password setups. These are highly vulnerable to attacks like credential stuffing and brute force. This isn't just a risk for large organizations; 50% of all API traffic is unmonitored, leaving many endpoints exposed to attacks like injection, DDoS, and man-in-the-middle exploits.
Common Jira API Security Risks
Several security challenges emerge when Jira APIs aren't secured properly.
Password-Based Authentication Creates Unnecessary Risk
This is one of the oldest API authentication practices. But the risk of credential exposure is always there. You can rotate passwords, but that can potentially break multiple downstream integrations unexpectedly.
Overly Broad API Access Expands Risk
In some Jira environments, authenticated integrations end up with access that is broader than necessary. Over time, it can become difficult to govern. That's why security is more than just authentication. It's also about defining how much access should be provided.
Unmanaged Tokens Create Governance Problems
Token-based authentication is generally stronger than password-based authentication. But you still have to manage them. Or else you'll end up with tokens being active long after their usage.
How miniOrange Enhanced API Security App Protects Your Data
The miniOrange REST API Authentication for Jira app addresses these challenges head-on, providing a comprehensive security layer for your REST APIs. It's a practical way to strengthen API authentication without rebuilding their integration ecosystem from scratch.
Rather than relying on password-centric authentication models, the app enables you to implement multiple secure authentication approaches suited to different operational needs.
Support for Multiple Authentication Methods
The miniOrange REST API Authentication app supports several modern approaches for Jira REST API authentication, including:
API Tokens
Secure Jira REST APIs using API tokens instead of vulnerable passwords.
The app allows you to create and manage API tokens for integrations, giving you better control over API access.
OAuth Tokens
Authenticate Jira API requests using OAuth tokens for stronger, modern API security.
The app supports OAuth-based authentication for environments where external services or SSO-enabled workflows need secure access to Jira APIs without depending on password-based authentication.
Client Credentials Grant
Enable secure machine-to-machine authentication for backend services and automated workflows.
This enables applications, scripts, and backend systems to authenticate without depending on human login processes. It's especially effective for automation-heavy Jira environments.
Integrate with Third-Party OAuth/OIDC Providers
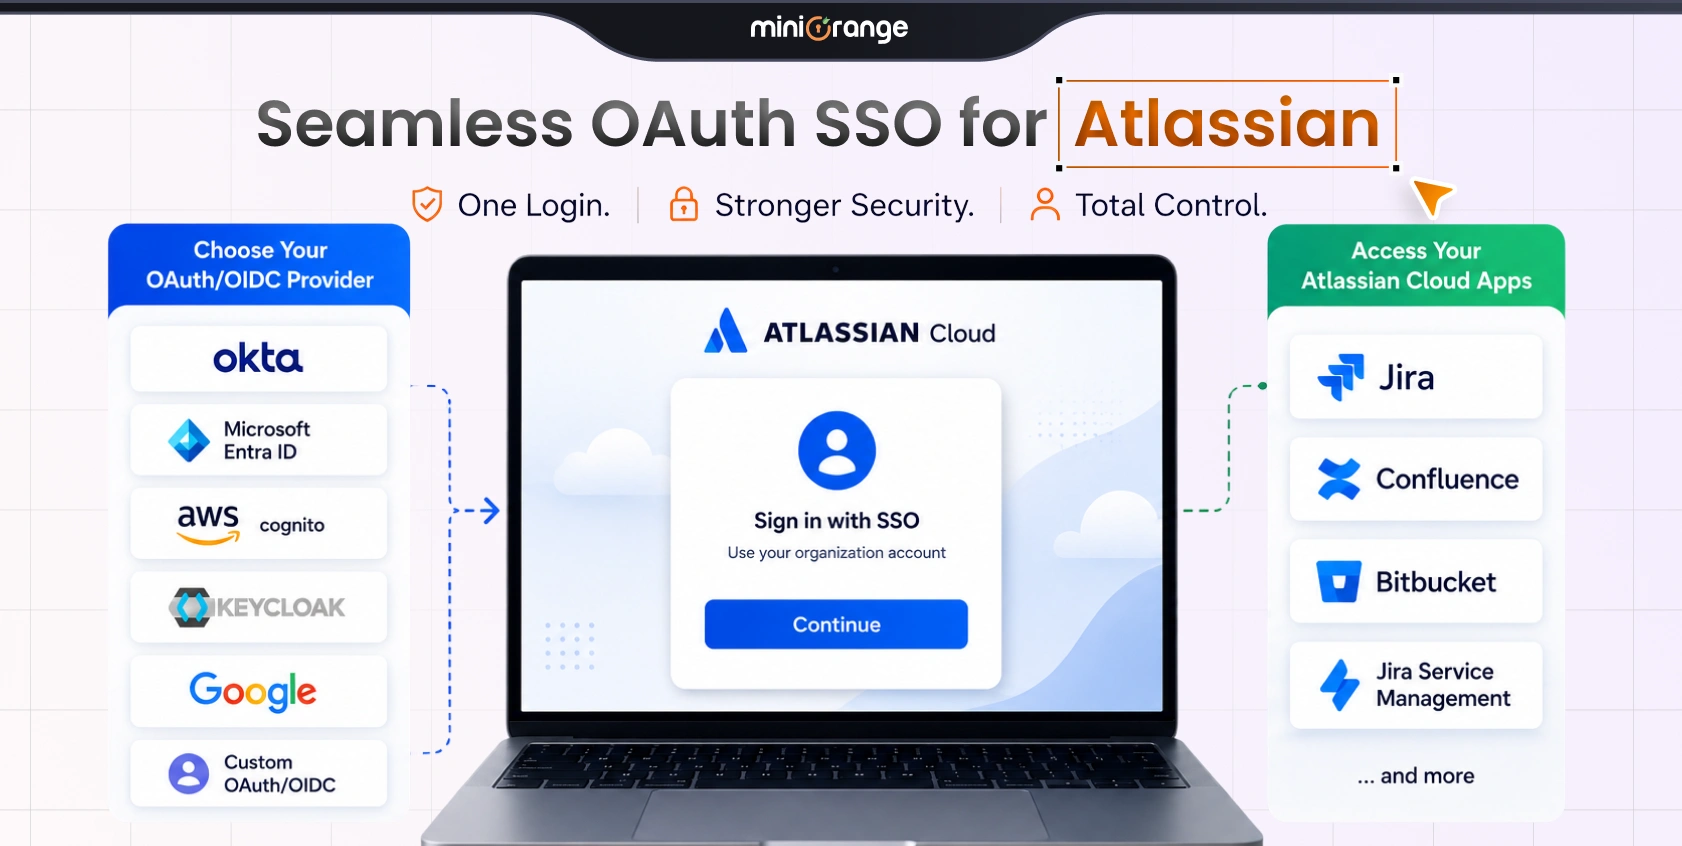
If you're relying on external identity platforms for authentication, the miniOrange app supports multiple OAuth/OIDC providers, including:
- Azure AD
- Okta
- ADFS
- and other supported OAuth/OIDC providers
The Jira API authentication will align naturally with your existing enterprise identity infrastructure.
Secure Scripts and Services in SSO Environments
SSO environments often create API authentication friction for automation workflows.
The app helps you securely integrate scripts, services, external apps, and automation tools without reverting to password-based authentication.
This removes a common operational roadblock.
Granular Access Controls for Stronger Governance
Security is equally about authorization as it is about authentication. Our solution supports granular access management capabilities that help you govern API behavior.
You can define APIs and methods to implement tighter permission controls around access behavior. This ensures that only trusted users can interact with specific APIs.
The miniOrange REST API Authentication app provides additional access restriction capabilities to support stronger governance across integration-heavy environments.
API Token Management and Visibility
Operational security depends on credential lifecycle management. The app gives you complete visibility and control over who can generate API tokens. You can understand how API credentials operate across your Jira environment. This ensures that only your most trusted team members can grant or manage API access, reducing the chances of unauthorized token creation.
Real World Use Cases
Jira APIs power workflows across enterprise applications. Here's how the miniOrange REST API Authentication for Jira app can help you in practical, day-to-day environments.
Secure CI/CD and DevOps Workflows
Your DevOps team wants deployment tooling to update Jira tickets after builds automatically. Traditionally, that workflow depends on stored credentials that are difficult to rotate and risky to manage at scale.
With the miniOrange REST API Authentication app, you can authenticate the workflow using API Tokens, OAuth Tokens, or Client Credentials Grant instead of passwords.
Connect Enterprise Applications to Jira Securely
Your organization needs Jira to exchange data with ERPs, CRMs, or HR systems. These integrations may pass operational data between teams.
The app allows you to secure these machine-to-machine communications with modern authentication methods, ensuring that only authorized systems can access your Jira REST APIs.
Protect Jira-Powered Reporting and Analytics Platforms
Your business intelligence platform pulls Jira data every few hours to generate dashboards and reports.
Instead of exposing APIs through broad or unmanaged access patterns, you can use the app to secure how analytics tools authenticate with Jira while maintaining controlled, reliable access to operational data.
Support Multi-Team Jira Environments Without Losing Governance
As you scale, you might have to manage multiple teams in a single Jira environment. These teams may operate their own automations and integration scripts. If you don't have proper API governance, then managing access will become more and more complicated.
The miniOrange REST API Authentication app helps you standardize authentication across teams, manage API access more consistently, and maintain stronger oversight as your integration footprint expands.
Why Choose miniOrange Enhanced API Security App?
The miniOrange REST API Authentication app is designed with one goal: to simplify and strengthen your API security so you can focus on what matters most. Whether you're dealing with sensitive customer data or critical system operations, the app ensures your APIs are locked down without requiring a steep learning curve or technical expertise.
By leveraging the app, you can:
- Create and revoke tokens
- Get clear visibility into API usage
- Control API access on a granular level
- Integrate third-party OAuth/OIDC providers
More importantly, ensure secure integrations without adding complexity.
Start taking proactive steps to secure your REST APIs with the Enhanced API Authentication Plugin for Jira.
Get in touch with our team to learn more or request a personalized demo. Together, we can close the gaps in your API security, effortlessly.
And if your business has unique API security needs? We offer tailored solutions to meet your specific requirements, so you're never left vulnerable.
Reach out to us at support-atlassian@miniorange.atlassian.net or raise a support ticket by clicking here.
FAQs
Can Jira REST APIs be secured without affecting existing integrations?
Yes. Jira REST APIs can be secured without disrupting integrations by using authentication methods designed for automation and service workflows, such as API Tokens, OAuth Tokens, or OAuth Client Credentials.
How can Jira admins reduce API credential sprawl?
Jira admins can reduce API credential sprawl by centralizing token management, limiting who can generate credentials, removing unused tokens, assigning clear ownership to integrations, and using authentication methods that support stronger lifecycle governance.
What should Jira admins evaluate before choosing an API authentication approach?
Jira admins should evaluate integration type, security requirements, SSO usage, identity architecture, automation needs, credential governance expectations, and operational scalability before selecting an API authentication model.
Leave a Comment