Hello there!
Need Help? We are right here!

Your DPDP Compliance Deadline Is Approaching. May 2027 is closer than you think.
Need Help? We are right here!
Search Results:
×
DPDP breach notification requirements call for timely communication, documented decisions, and clear accountability
across the incident response process.

Maintain incident details, assessment findings, and supporting evidence to facilitate accurate regulatory reporting within applicable timelines.

Communicate the breach, its likely consequences, mitigation measures, recommended protective steps, and relevant contact information in clear, accessible language.

Monitor notification milestones, approvals, and remediation activities while maintaining a traceable record of response decisions and actions.
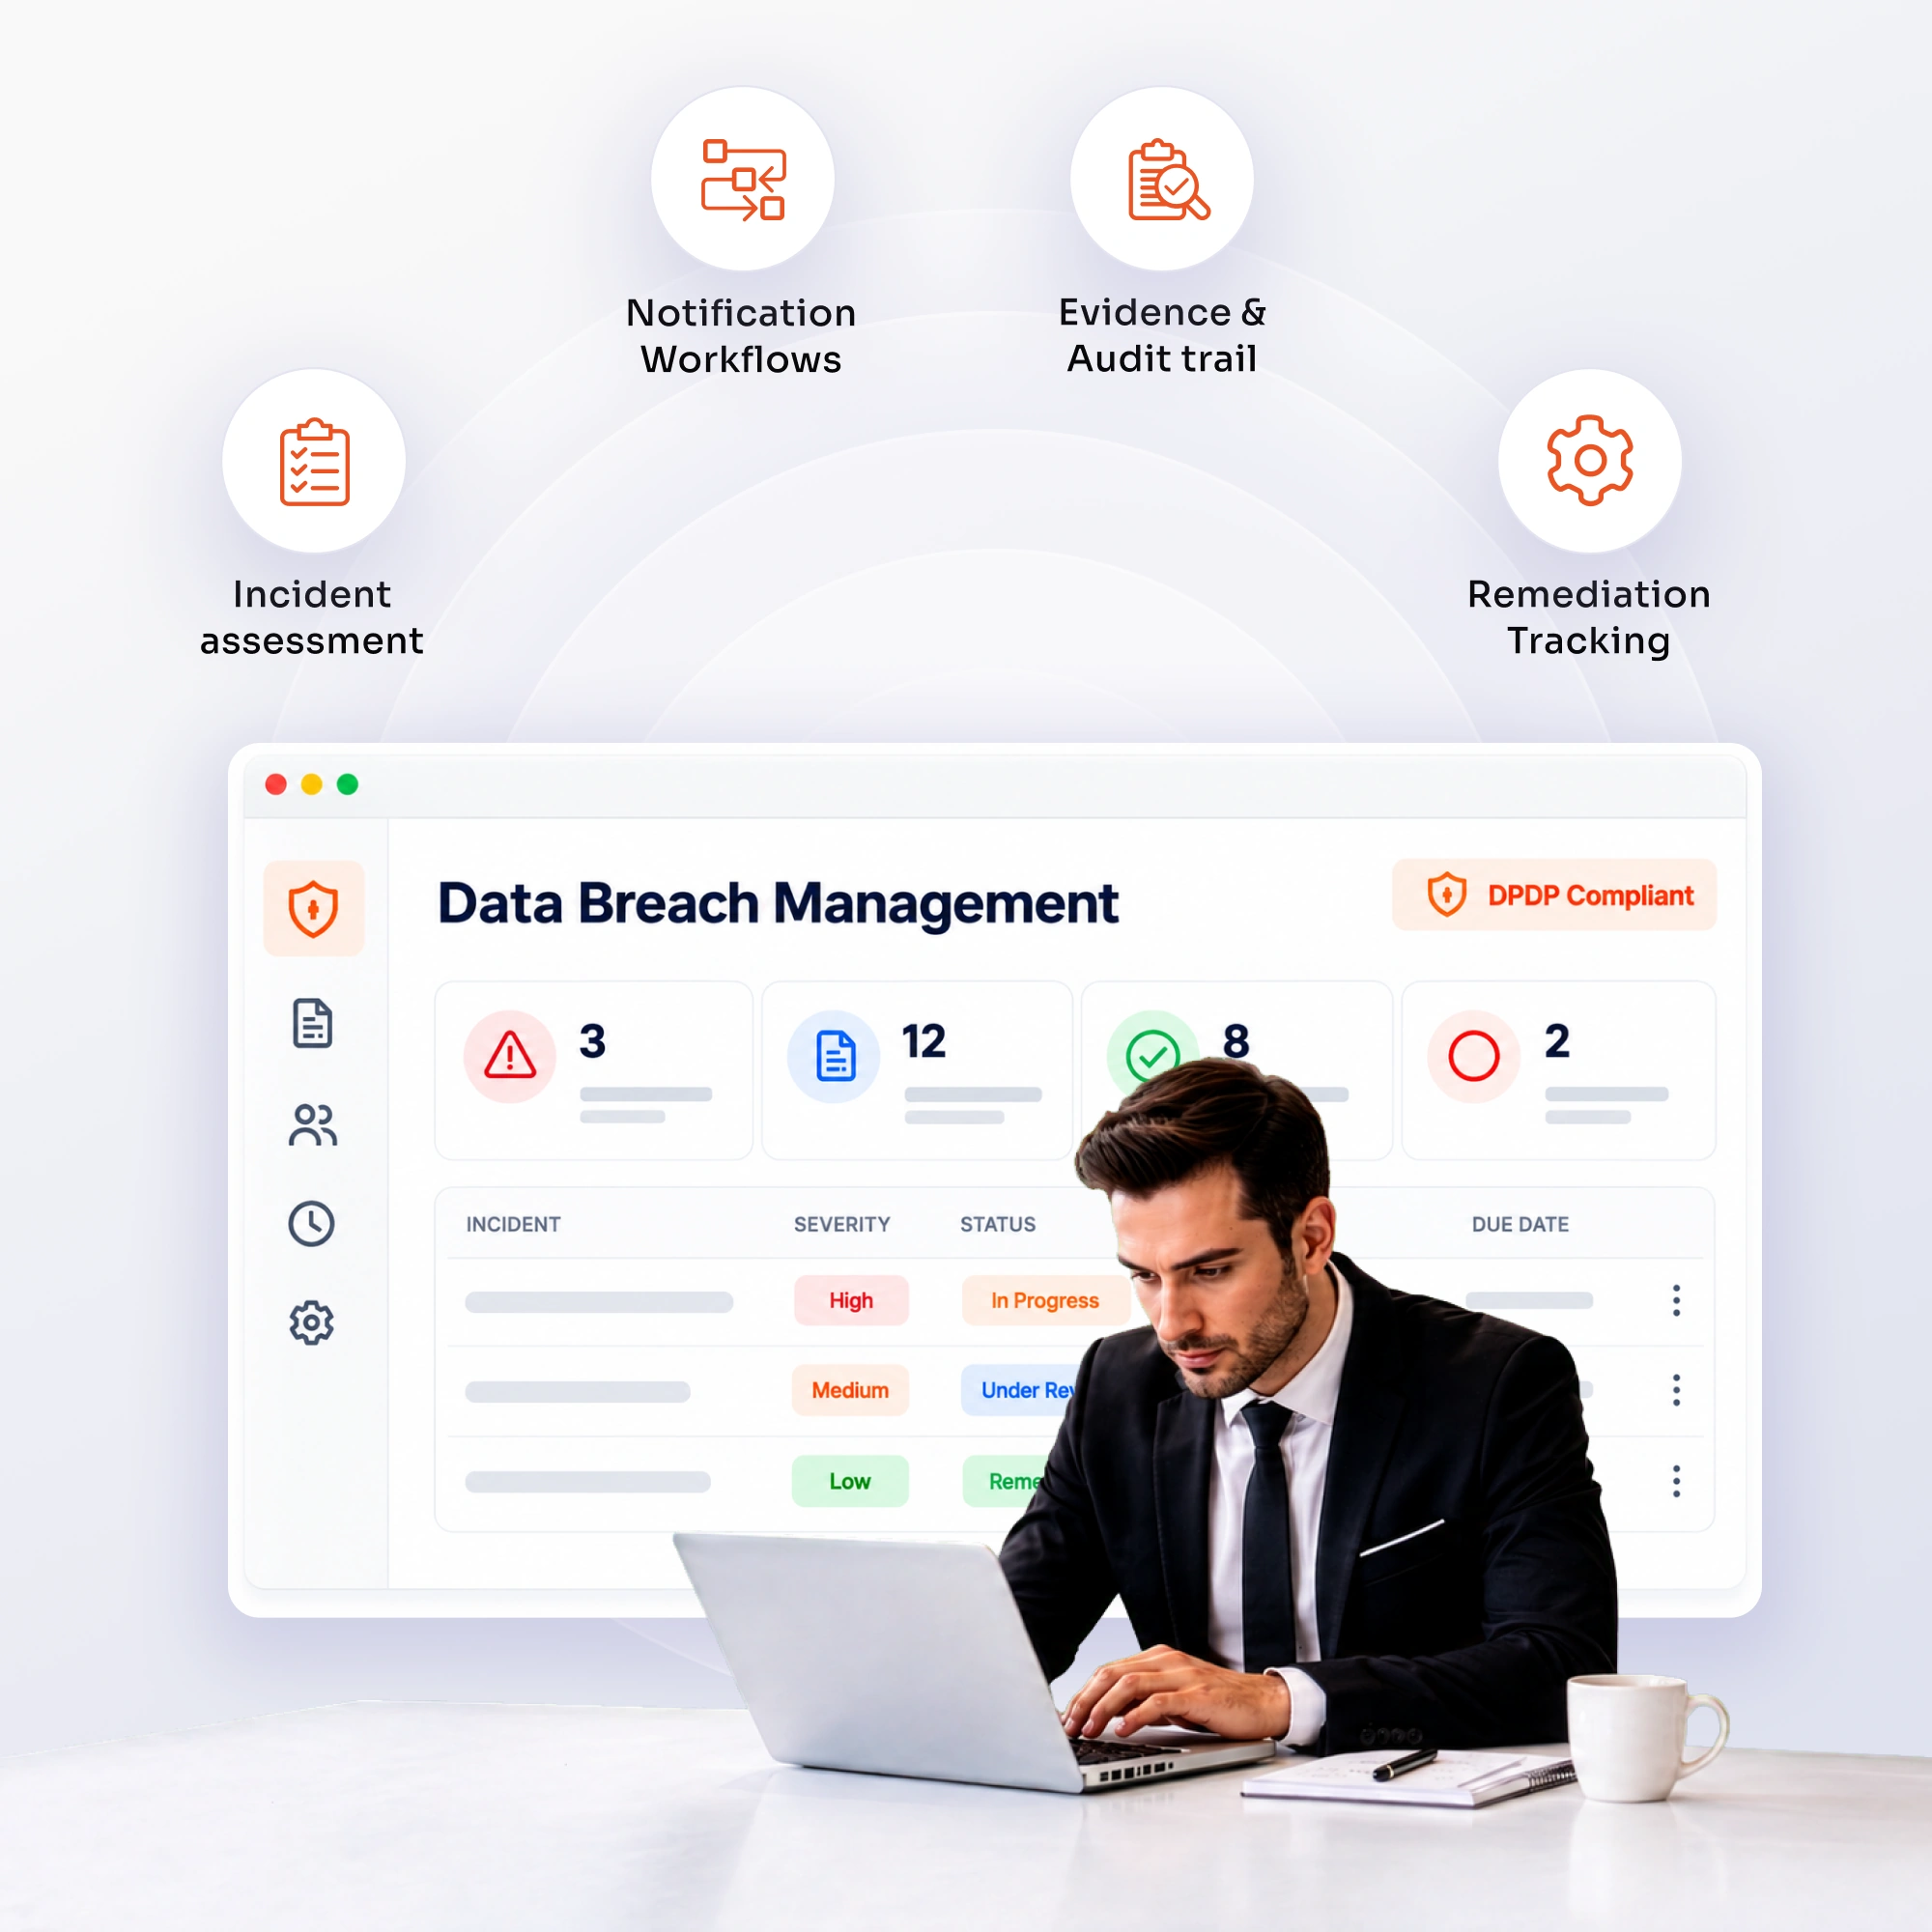
Coordinate breach assessments, notification decisions, investigation evidence, and remediation through structured workflows that connect incident records with accountable privacy operations.
Maintain a consolidated incident record containing breach details, discovery timestamps, affected systems, investigation updates, and response status.
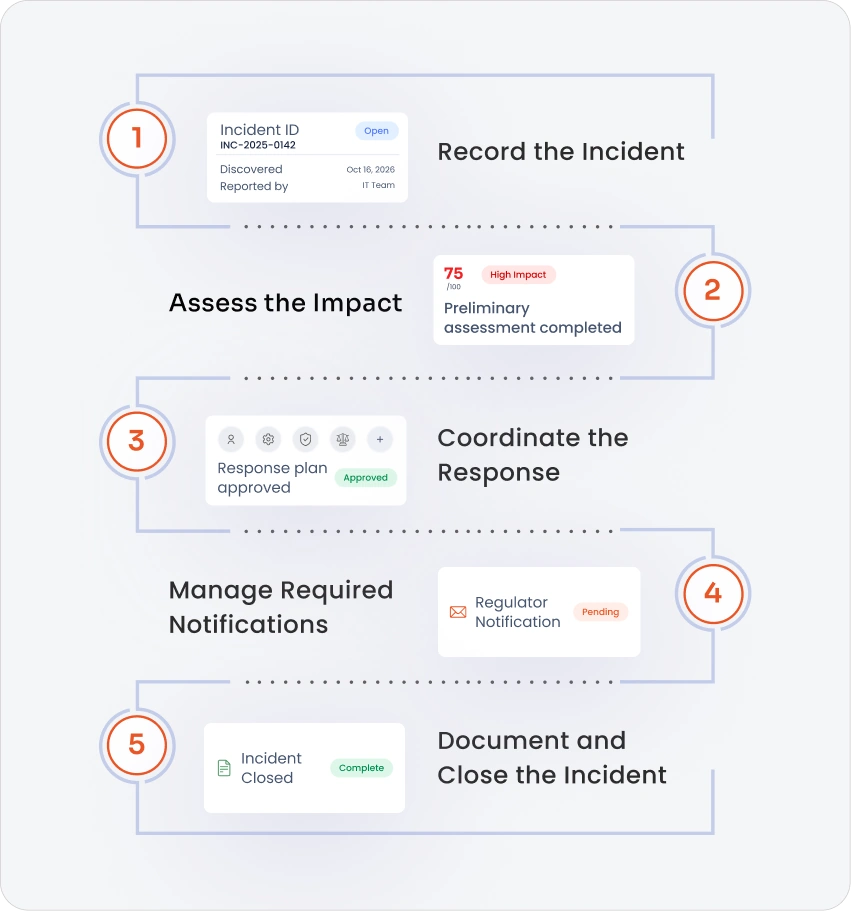
Follow five connected stages from incident intake through assessment, notification decisions, remediation, and documented closure.
Capture the incident description, discovery time, reporting source, potentially affected systems, and known personal data categories. Establish a documented starting point for investigation and review.
Examine available evidence to establish the scope of the incident, potential consequences, and affected individuals where known. Document findings and update the assessment as new information emerges.
Involve relevant privacy, legal, compliance, and technical stakeholders in reviewing findings and determining appropriate actions. Document approvals, responsibilities, and investigation updates against the incident.
Determine applicable notification requirements, prepare recipient-specific information, and track review and communication milestones. Authorized personnel validate and submit required communications.
Record mitigation measures, notification decisions, corrective actions, and closure rationale. Retain supporting evidence according to applicable policies and use investigation findings to improve future response procedures.
Connect incident and breach management with existing security tools, incident reporting systems, and privacy records. Assess supported integrations to identify opportunities for sharing relevant incident information across security, legal, compliance, and privacy operations.
Align deployment with your infrastructure, access controls, existing privacy operations, and operational requirements.

Cloud SaaS

Private Cloud

100% On-Premise

Keep incident evidence, assessment findings, DPO reviews, and approvals linked to a documented history of each response decision.

Connect investigations with data discovery, classification, and privacy governance to give teams context when assessing affected personal data.

Access DPO advisory, regulator liaison, and legal assistance to support breach response planning, notification preparation, and regulatory documentation.
Prepare incident assessments, notification workflows, and response procedures ahead of DPDP breach-notification commencement scheduled for May 13, 2027.
Still have questions? We've got answers to help you make the right decision.