

Passwords and SMS passwords stand strong until they encounter phishing attacks. Security teams keep pushing complex password rules and extra OTP steps, but users still fall for fake login pages. The loophole here is that any secret you can type or copy can be stolen.
WebAuthn fixes this by getting rid of shared credentials entirely. This guide covers how WebAuthn works, its benefits, supported devices, enterprise use cases, and why it's a core building block of phishing-resistant authentication.
What Is WebAuthn?
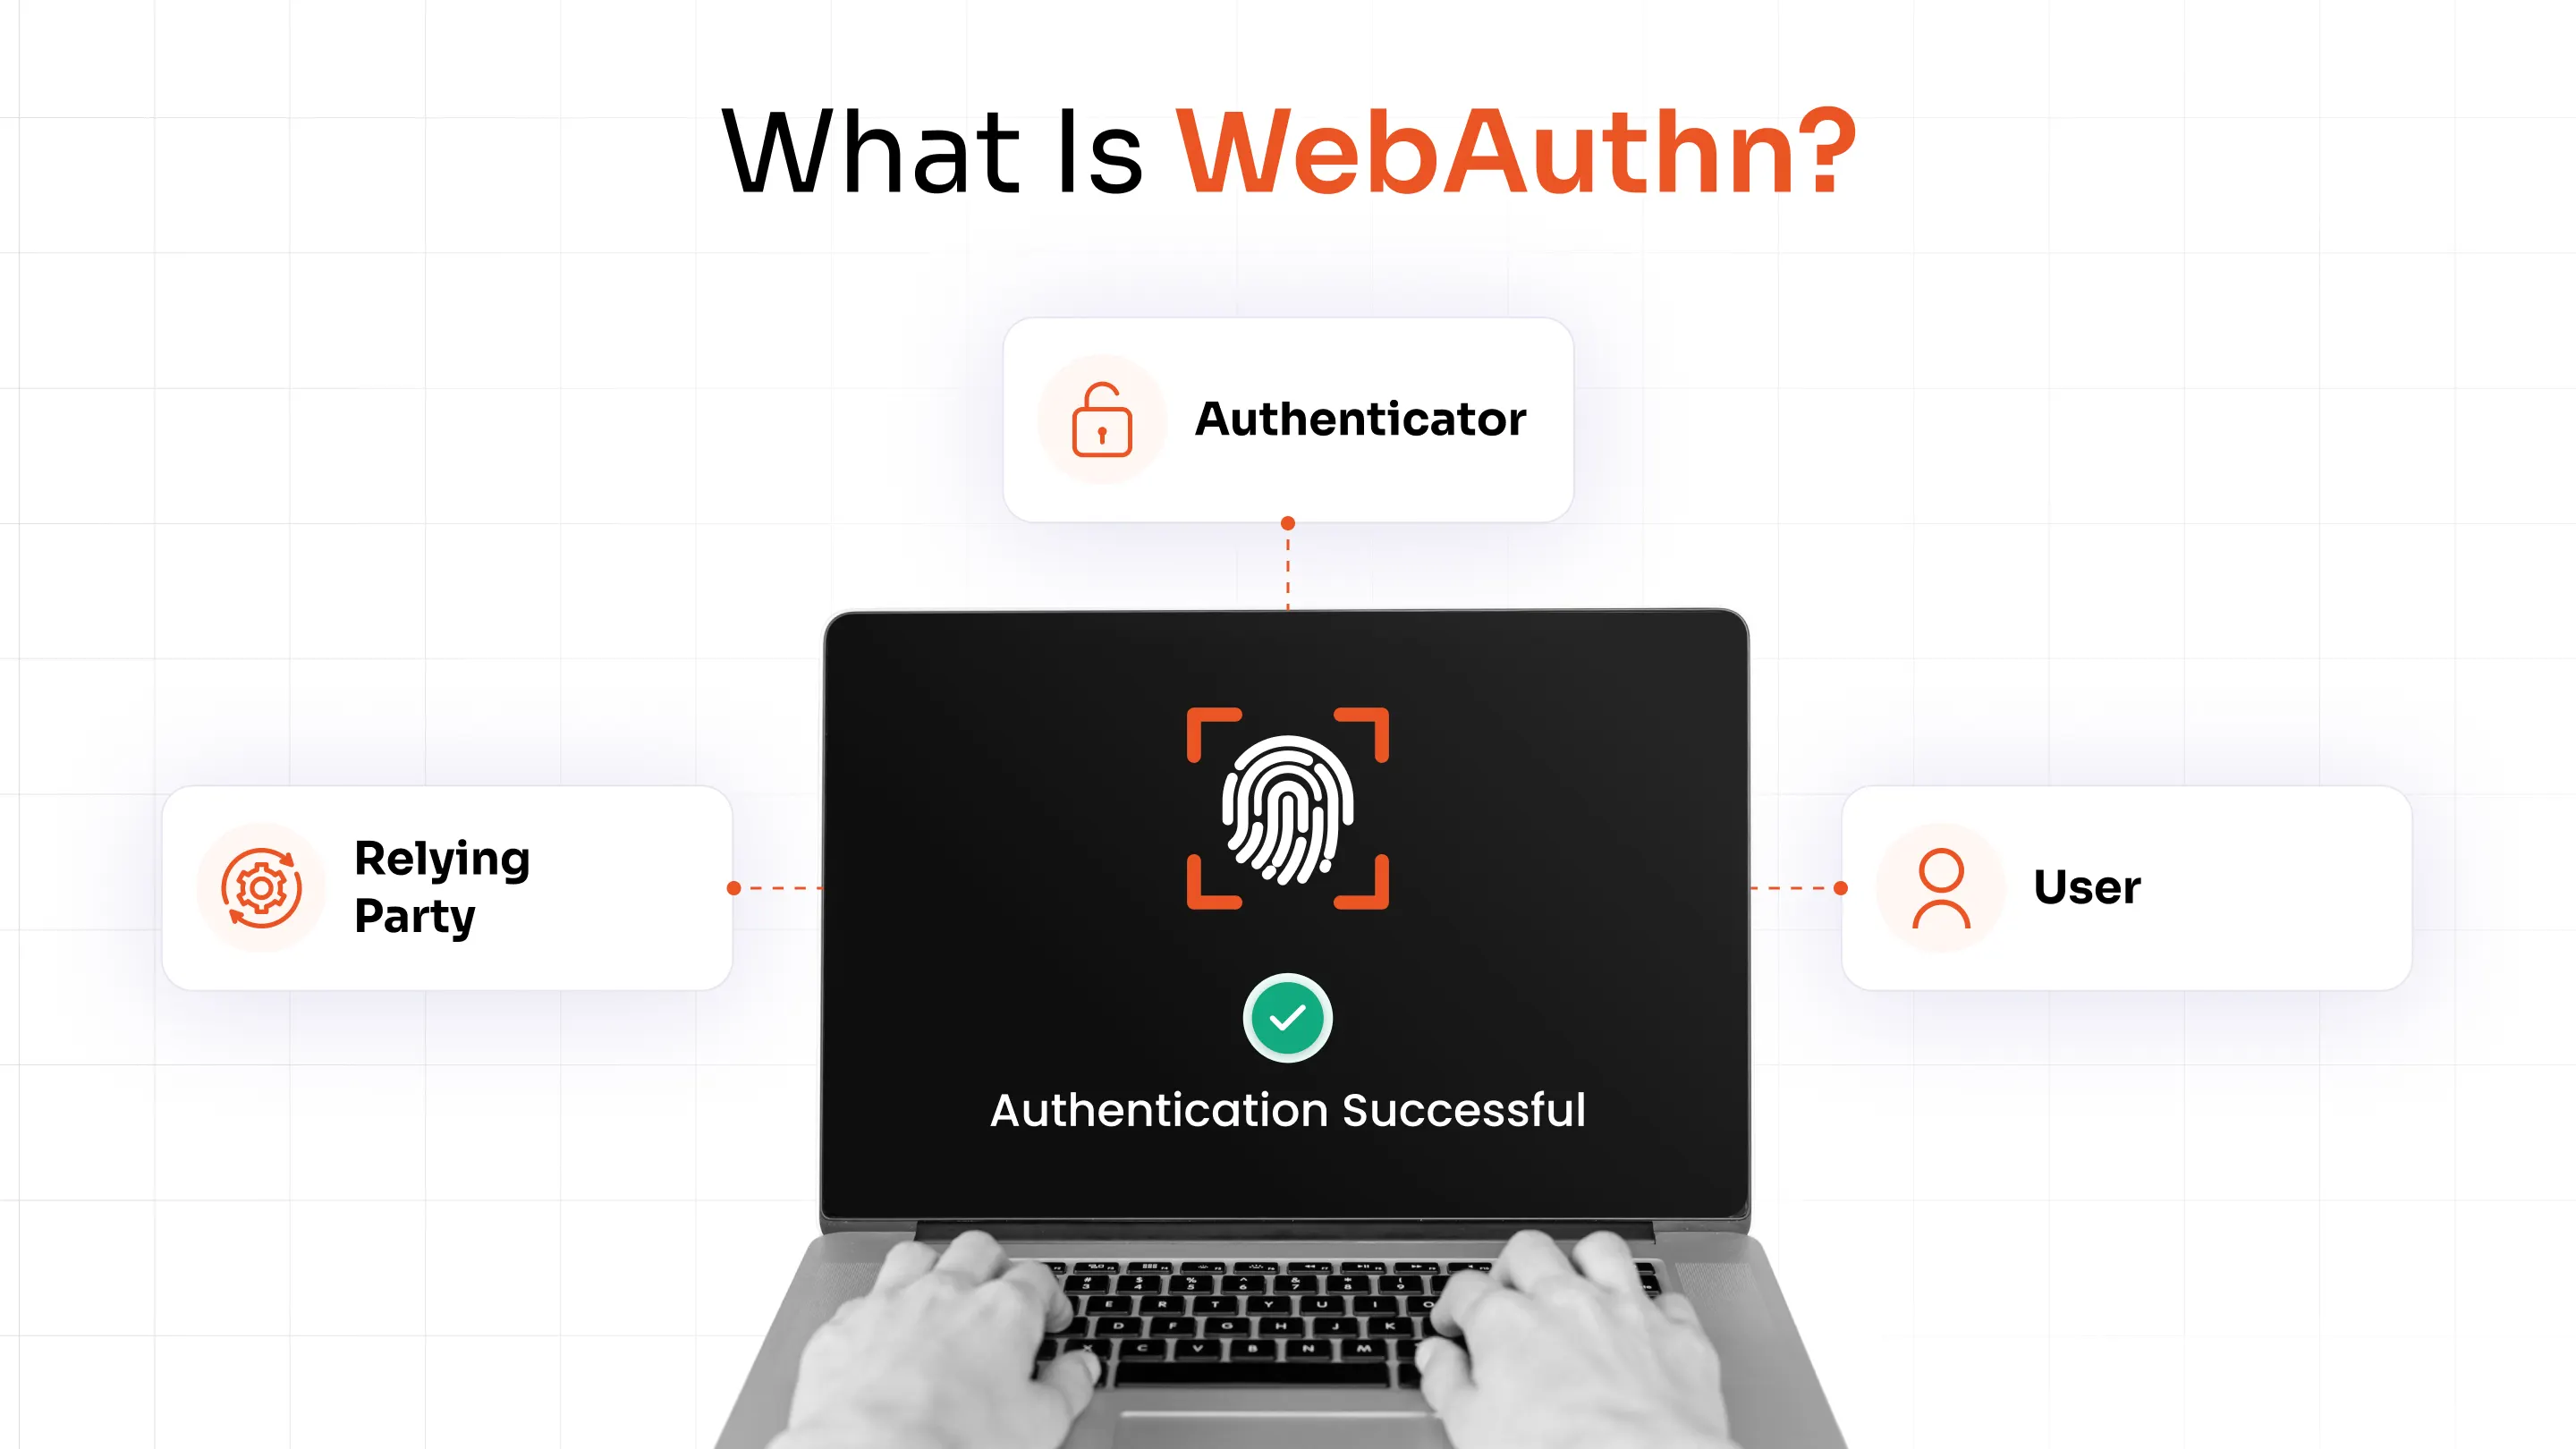
WebAuthn (Web Authentication) is an open web standard published by the World Wide Web Consortium (W3C) and the FIDO Alliance. It lets you log in to websites and applications without typing a password. Instead of a shared secret that travels over the network, WebAuthn uses public key cryptography. A relying party (your website or app) and a client (the browser) work with an authenticator, like a fingerprint reader, facial scanner, security key, or built‑in device credential, to verify the user.
The WebAuthn protocol is a core component of the broader FIDO2 framework, which is why you'll often see WebAuthn, FIDO2, and passkeys mentioned in the same breath. At its core, WebAuthn replaces passwords ("something you know") with a physical device or biometric factor ("something you have or are").
Because modern browsers and operating systems support WebAuthn natively, you do not need to install extra software to use it. That combination of strong security and native support is what has made it the technical foundation for passkeys and passwordless login across the industry.
Why Is Traditional Authentication No Longer Enough?
While passwords are secure, they can’t keep up with the scale of threats organizations face today. Attackers don't need to guess a password when they can buy one. Credential stuffing attacks reuse billions of leaked username-password pairs across services, and phishing kits now automate real-time theft of both passwords and one-time codes.
A few reasons traditional authentication keeps failing:
- Password attacks and credential stuffing: Automated tools test stolen credentials at scale. Password reuse means one breach can compromise many accounts.
- Phishing: Traditional MFA like SMS codes and push notifications can be intercepted or approved by a distracted user. The credential is still something that can be typed, forwarded, or socially engineered.
- MFA fatigue: Attackers bombard users with repeated push notifications, creating MFA fatigue, until the user accidentally approves a fraudulent access request.
- User friction: Password resets, OTP entry, and repeated authentication steps create extra work for users and IT teams.
Passwordless authentication solves this problem at the root. Instead of trying to make passwords harder to steal, it removes the password from the authentication flow. This is why it’s no longer a nice-to-have convenience feature. It’s a security requirement.
WebAuthn does this through public key cryptography. The website never needs the private key, and the credential is tied to the relying party's domain. That is why WebAuthn is designed for phishing-resistant authentication, rather than simply adding another factor around a password.
How WebAuthn Works
WebAuthn runs in two phases: registration and authentication. Both rely on a public/private key pair generated and stored on the user's device.
Registration Flow
1. User registration - You initiate the account setup or add a new authentication method on the relying party's site.
2. Key pair generation - The authenticator generates a unique public/private key pair for that specific website.
3. Private key storage - The private key never leaves the device. It's stored securely in the authenticator's hardware (a secure enclave, TPM, or security key chip).
4. Public key registration - Only the public key is sent to and stored by the relying party's server, tied to the user's account.
Authentication Flow
1. Authentication request - You attempt to log in, and the relying party asks the browser to start a WebAuthn authentication ceremony.
2. Challenge generation - The server generates a unique, random challenge for that login attempt.
3. User verification - The authenticator confirms your presence and identity via biometric scan, PIN, or physical interaction.
4. Challenge signing - The authenticator signs the challenge with the private key stored on the device.
5. Server validation - The relying party verifies the signature using the stored public key. If it matches, access is granted.
Because the private key never leaves the device and no shared secret is transmitted, there's nothing to intercept, phish, or reuse on another site. That's why WebAuthn is phishing‑resistant by design rather than by policy.
Core Components of WebAuthn
WebAuthn depends on five core components:
Relying Party (Website/Application)
The service you log into. It stores public keys and validates signed challenges. It never sees or stores a private key or password.
Client (Browser)
The intermediary between the relying party and the authenticator. Modern browsers, such as Chrome, Edge, Firefox, and Safari, implement the WebAuthn API natively.
Authenticator
The hardware or software component that generates and stores key pairs and performs user verification. It can be built into a device or connected externally.
User Verification
The step that confirms the person present is authorized to use the credential, typically through a biometric scan, device PIN, or security key touch.
Public Key Cryptography
The mathematical foundation of WebAuthn. Each key pair is unique per site. A credential registered with one site can't be replayed against another.
Types of WebAuthn Authenticators
WebAuthn authenticators generally fall into two categories.
Platform Authenticators
Built directly into the device you use and tied to that device.
- Windows Hello
- Face ID
- Touch ID
- Android Biometrics
You typically use the same mechanism you already use to unlock your device. This makes them ideal for everyday logins on a personal or managed device, where convenience and speed matter most.
Roaming Authenticators
External, portable devices that can move between machines.
- YubiKey
- FIDO2 Security Keys
- USB
- NFC
- Bluetooth
Use these for shared workstations, high‑privilege accounts, or when you need one credential that works across multiple devices.
What Devices Support WebAuthn?
WebAuthn has broad, native support across today's major platforms and browsers:
- Operating Systems: Windows, macOS, Linux, Android, iOS/iPadOS
- Browsers: Chrome, Edge, Firefox, Safari
Most modern devices ship with a built-in platform authenticator (Windows Hello, Touch ID, Face ID, or Android biometrics) ready to use out of the box. If you need a consistent credential across personal devices, shared workstations, or legacy hardware, you can pair this with external security keys such as YubiKeys or other FIDO2-certified USB, NFC, or Bluetooth devices.
This level of compatibility makes it easy to enforce strong Linux, macOS, or Windows MFA policies using built-in biometrics or external security keys.
Benefits of WebAuthn
- Phishing-resistant authentication - No passwords travel across the network, leaving attackers with nothing to intercept or steal in a phishing attempt.
- Passwordless login - You authenticate with a biometric or security key as part of a passwordless authentication solution, instead of memorizing credentials.
- Better user experience - A fingerprint or face scan is faster than remembering and typing complex passwords.
- Faster authentication - You can log in in seconds without waiting for OTPs or switching apps.
- Reduced password resets - The chances of you getting locked out and raising tickets are lower as there are fewer passwords in rotation.
- Strong cryptographic security - Public key cryptography is significantly harder to break or replay than shared-secret methods.
- Compliance readiness - Strong authentication supports requirements under frameworks like HIPAA, SOC 2 Type II, PCI-DSS, and NIST SP 800-53.
- Lower operational costs - Less time spent on password support translates directly into IT cost savings.
WebAuthn vs Traditional Authentication Methods
| Method | Phishing Resistance | User Experience | Passwordless Support | Hardware Dependency | Security |
|---|---|---|---|---|---|
| Passwords | Low | Poor (recall burden) | No | None | Weak |
| OTP | Low–Medium | Moderate (manual entry) | No | None | Moderate |
| SMS | Low | Moderate | No | Phone required | Weak–Moderate |
| Push Authentication | Medium | Good | No | Mobile app required | Moderate (fatigue risk) |
| WebAuthn | High | Excellent | Yes | Authenticator required | Strong |
The main difference is the credential model. Passwords and OTPs rely on secrets that users can enter or expose. WebAuthn uses public key credentials and a cryptographic challenge-response process instead.
Push authentication can provide a strong MFA solution, but it is not inherently phishing-resistant. Number matching and other controls can reduce MFA-fatigue risk, but WebAuthn addresses phishing at the credential level.
WebAuthn, FIDO2, Passkeys, and CTAP Explained
These four terms are closely related, and the overlap causes real confusion.
- FIDO2 is the umbrella framework from the FIDO Alliance and W3C. It's made up of two components: WebAuthn and CTAP.
- WebAuthn is the W3C API specification that lets a browser or app create and use public key credentials. It's the piece developers build against.
- CTAP (Client to Authenticator Protocol) governs how a browser or operating system communicates with an external authenticator, such as a security key connected over USB, NFC, or Bluetooth.
- Passkeys are the user-facing term for a WebAuthn/FIDO2 credential. A passkey can be device-bound (tied to one device, as with most security keys) or synced across a user's devices through a platform cloud account.
In simple terms, FIDO2 is the overarching system, WebAuthn is the web API, CTAP is the device bridge, and passkeys are what your users interact with during login.
Enterprise Use Cases of WebAuthn
Workforce Authentication
Use WebAuthn to reduce password dependence for employees accessing business applications and systems. Users can authenticate with platform credentials, passkeys, or security keys.
Customer IAM (CIAM)
Give customers a faster, safer login experience with a CIAM solution for consumer-facing apps and portals, without adding unnecessary friction.
VPN Access
WebAuthn and FIDO2 authentication can be part of MFA for VPN access. You can secure remote network access with hardware-backed authentication instead of password-plus-OTP combinations.
Cloud Applications
Extend WebAuthn across SaaS and cloud platforms through SSO integrations for consistent, strong authentication everywhere. Give users a consistent authentication experience without requiring each application to manage authentication separately.
Remote Workforce
Support distributed teams with authentication that doesn't depend on a corporate network perimeter.
Zero Trust Security
WebAuthn reinforces a "never trust, always verify" model by tying every access request to a verified device and user, rather than a shared credential.
Regulatory Compliance
Support audit and compliance requirements under HIPAA, SOC 2 Type II, PCI-DSS, and similar frameworks that call for strong, phishing-resistant authentication.
Best Practices for Implementing WebAuthn
- Support multiple authenticators so users can choose biometrics, platform credentials, or security keys based on their device and role.
- Enable account recovery paths that don't reintroduce weak, phishable fallback methods.
- Enforce user verification on every authentication, not just at initial registration.
- Combine with adaptive authentication to add risk-based checks for unusual login contexts.
- Monitor authentication activity to catch anomalies and failed verification attempts early.
- Educate users on how to register and use authenticators correctly, especially for roaming keys and what to do if they lose their device.
- Plan fallback authentication methods for lost devices or damaged security keys, without falling back to plain passwords wherever possible.
How miniOrange Enables Phishing-Resistant Authentication with WebAuthn
miniOrange brings WebAuthn support directly into its identity and access management platform. You get a practical path to passwordless, phishing‑resistant login. You can use FIDO2 authentication, passkeys, and security keys so employees and customers authenticate with Windows Hello, biometrics, or a hardware key of their choice.
Rather than treating passwordless login as a standalone feature, miniOrange combines WebAuthn with an adaptive MFA solution. Authentication decisions can factor in device posture, location, and risk signals in addition to the cryptographic credential itself.
Centralized policy management lets IT and security teams define authentication requirements once and apply them consistently across VPNs, cloud applications, and on-premises systems, backed by enterprise integrations that work with your existing identity stack.
Conclusion
WebAuthn has moved from an emerging W3C standard to the practical foundation of passwordless, phishing-resistant login across the web.
It uses public key cryptography, relying-party-scoped credentials, and authenticators such as platform credentials and security keys. You can use it for passwordless sign-in while strengthening protection against phishing and credential-based attacks.
WebAuthn also fits into the wider FIDO2 ecosystem alongside CTAP and passkeys. For organizations, that makes it useful across workforce authentication, customer-facing applications, VPN access, and cloud environments.
The key is to treat WebAuthn as part of a broader authentication strategy. Pair strong credentials with thoughtful recovery, policy controls, monitoring, and adaptive authentication to build a rollout that works for both your users and your security team.
FAQs
Is WebAuthn secure?
Yes. WebAuthn uses public key cryptography instead of shared secrets, so private keys never leave the user's device and nothing sensitive is transmitted during login. This design makes it resistant to phishing, credential stuffing, and replay attacks that affect passwords and OTPs.
What devices support WebAuthn?
WebAuthn is natively supported on Windows, macOS, Linux, Android, and iOS/iPadOS, and across major browsers including Chrome, Edge, Firefox, and Safari. Support comes through built-in platform authenticators (like Windows Hello or Face ID) or external roaming authenticators such as USB, NFC, or Bluetooth security keys.
What is the difference between WebAuthn and FIDO2?
FIDO2 is the broader authentication framework made up of two parts: WebAuthn, the W3C API used by browsers and relying parties, and CTAP, the protocol used to communicate with external authenticators. WebAuthn is a component of FIDO2, not a separate competing standard.
Can WebAuthn replace passwords completely?
WebAuthn is designed to eliminate passwords for day-to-day login, and many organizations use it as their primary or sole authentication method. Most implementations still keep a fallback recovery process in place for lost or damaged authenticators.
How do I enable WebAuthn for my organization?
Enabling WebAuthn typically involves configuring your identity provider or IAM platform to support FIDO2/WebAuthn as an authentication method, then rolling it out alongside supported authenticators like security keys or platform biometrics. Centralized policy management makes it easier to enforce this consistently across applications and user groups.
Why is my WebAuthn security key or biometric login not working?
Common causes include an unregistered authenticator for that specific site, a browser or OS that doesn't support WebAuthn, a security key not properly connected via USB/NFC/Bluetooth, or user verification (PIN/biometric) failing on the device. Re-registering the authenticator or checking browser compatibility usually resolves the issue.



Leave a Comment