Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×
Privileged accounts in government organizations are high-value targets for attackers because of their access to sensitive data. Once compromised, attackers can access critical systems and steal sensitive data, risking national security.
miniOrange PAM helps government agencies centrally manage privileged access across all users, endpoints, servers, databases, and cloud environments. Store privileged credentials in an encrypted vault, grant access through defined policies and JIT workflows, and maintain a clear record of privileged activity.
Explore comprehensive PAM features, integration methods, compliance benefits, and everything you need in one place.
Your download should start now. If not, please email us at idpsupport@xecurify.com.
Please enter a valid email-id

Government agencies handle confidential citizen records and classified information. Uncontrolled privileged access can expose sensitive data to unauthorized users, leading to data breaches, privacy violations, and loss of public trust.

Federal agencies usually rely on legacy systems that lack modern access controls. Replacing them is not practical. You need to tighten privileged access around them while keeping your operations running.

Government agencies often rely on contractors and external vendors. But handing over permanent admin rights is risky. You need a way to grant access without handing over the actual credentials.

Cybercriminals aggressively target government networks with ransomware. One compromised account can expose critical systems and data. And the damage often cascades to the public.

Government environments often involve administrators, IT teams, contractors, and other personnel with access to critical systems, which increases risk if compromised. Once inside, attackers use this excessive access to move laterally across your network.

Government organizations need to demonstrate who accessed sensitive systems, what access they were granted, and what actions they performed. Without centralized audit reports, investigating privileged activity and responding to audit requests can become time-consuming.
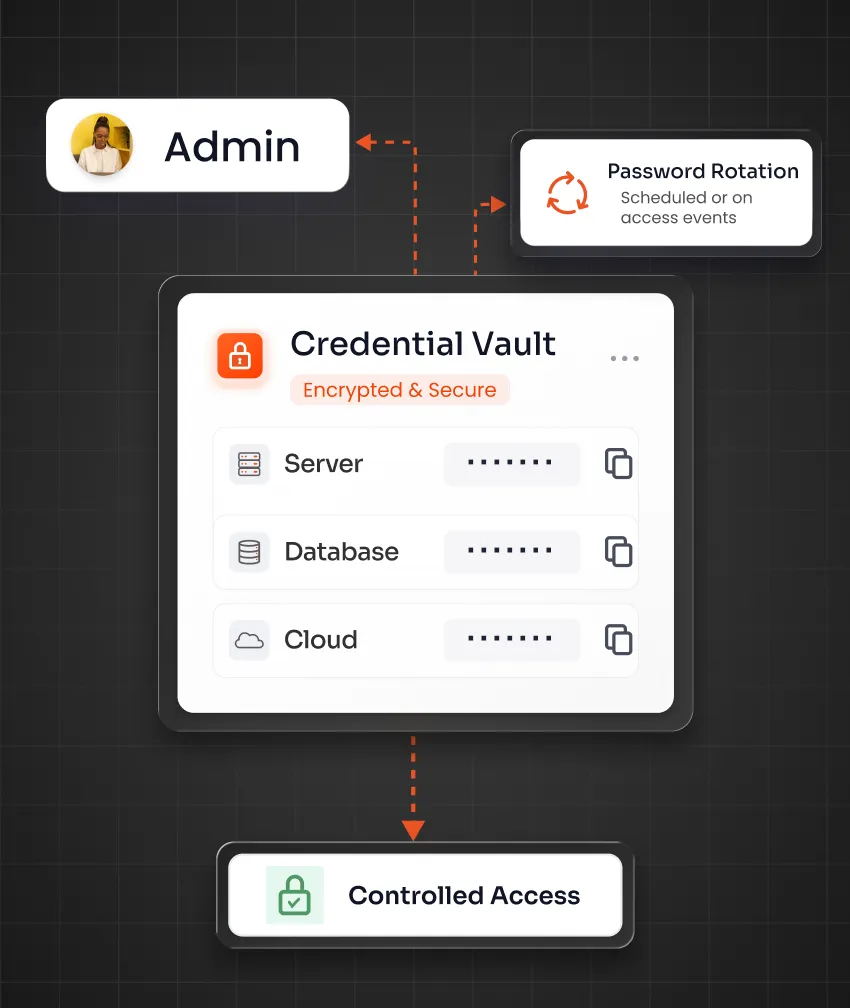
Securely store privileged passwords in an encrypted vault and control who can access them. miniOrange PAM rotates them based on configured schedules or access events to reduce the risk of stale or reused privileged credentials.
Know More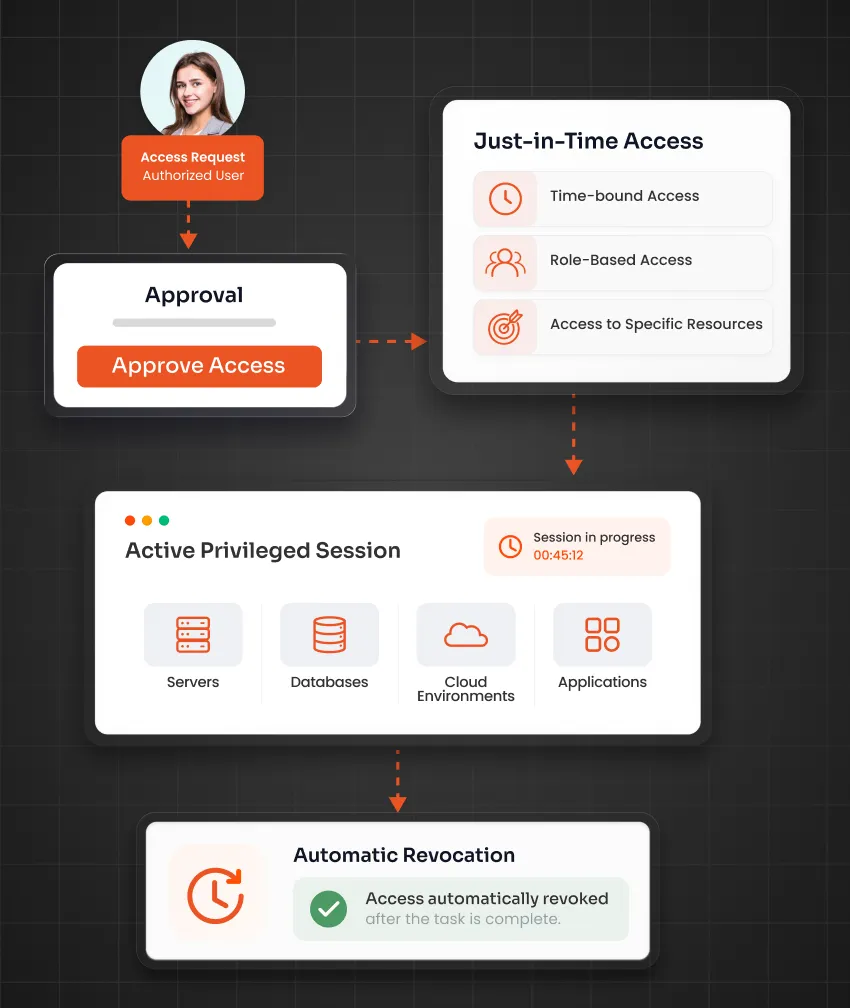
Reduce standing privileges by granting privileged access only when an administrator or authorized user needs it. Automatically revoke that access when the task is complete.
Know More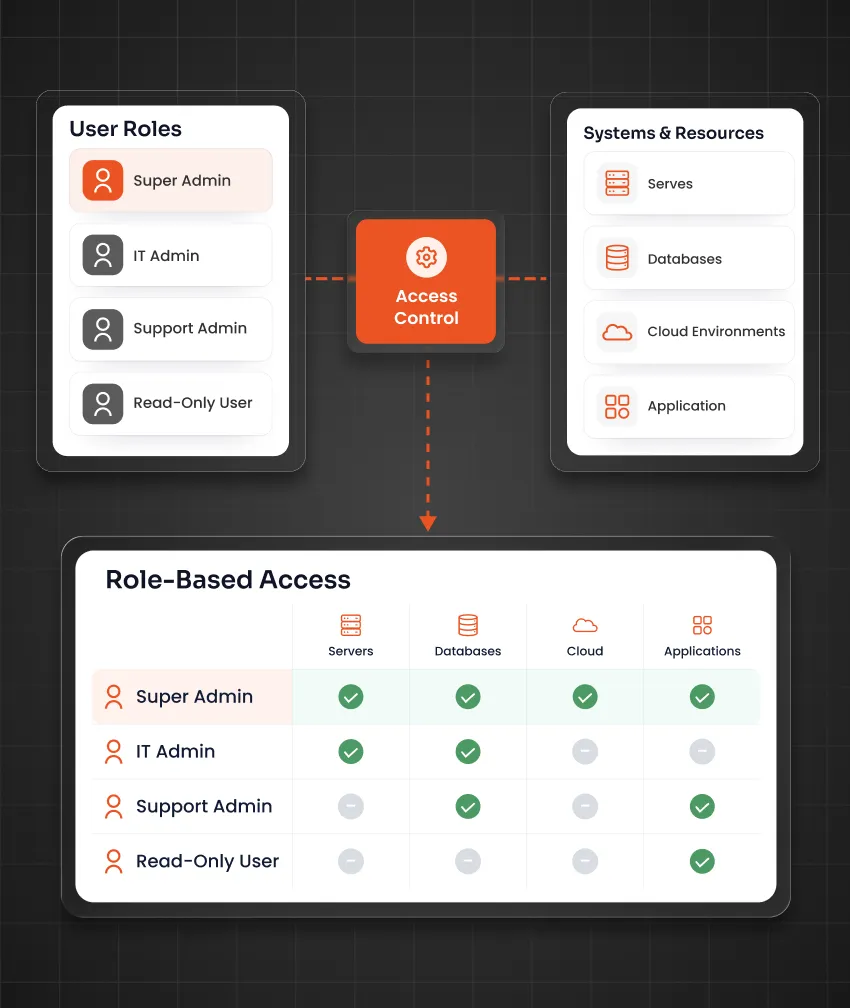
Not every administrator needs the same level of access. Restrict user access based on roles. Ensure users only access the specific systems required to do their jobs rather than everything else.
Know More
Record and monitor every privileged session in real time with privileged session management capability. Investigate suspicious activity and terminate active sessions when necessary.
Know More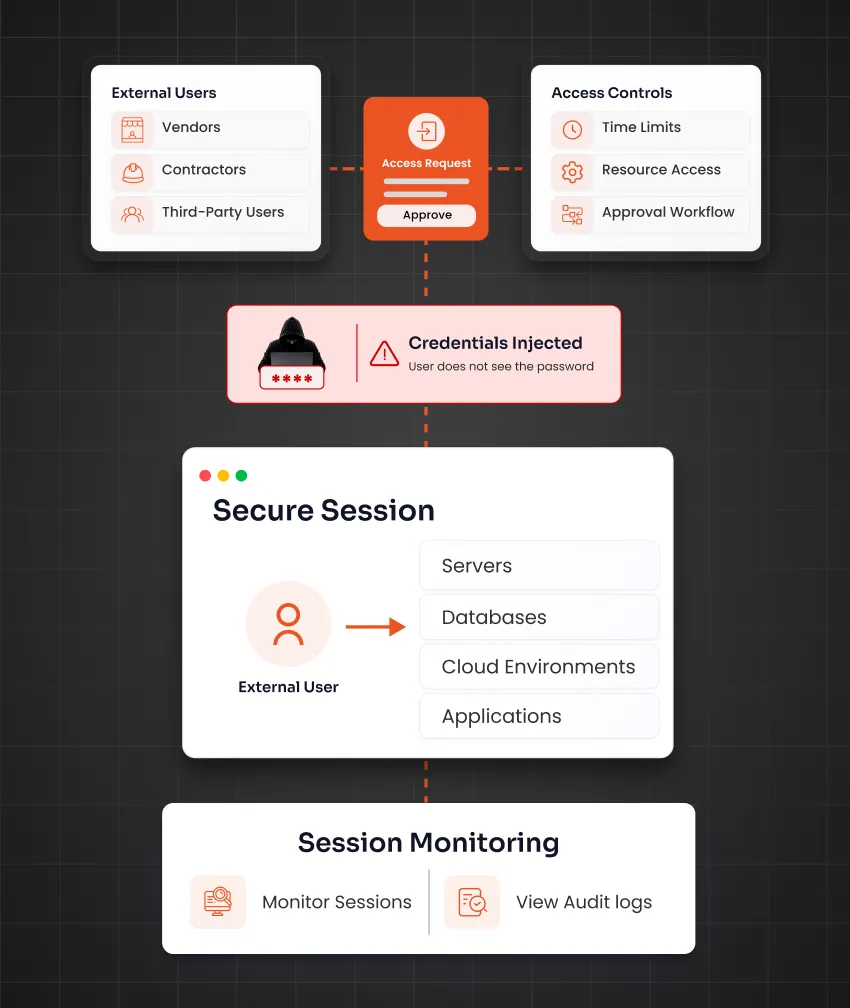
Give external personnel controlled access. Define which resources they can access, add approval and time limits, and monitor their sessions. miniOrange can inject stored credentials into the session so users do not need to see the password.
Know More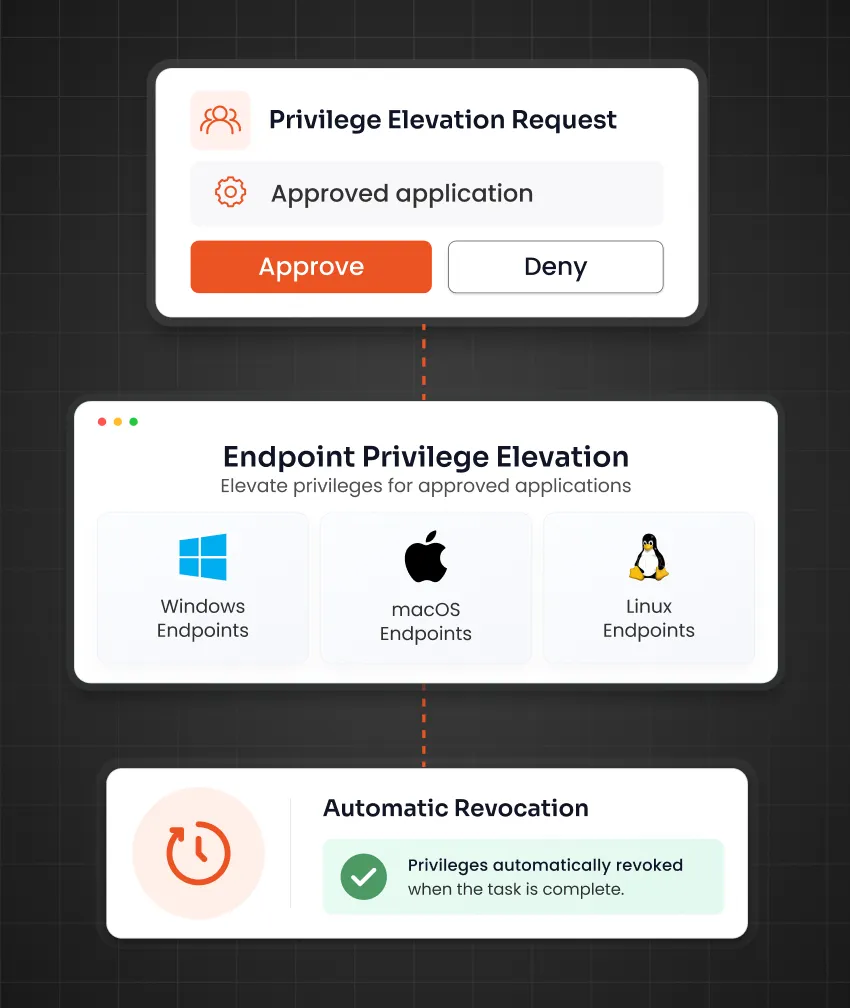
Remove unnecessary local administrator rights and control privilege elevation on Windows, macOS, and Linux endpoints. miniOrange Endpoint Privilege Management elevates privileges for specific, approved applications and revokes them when the work is complete.
Know More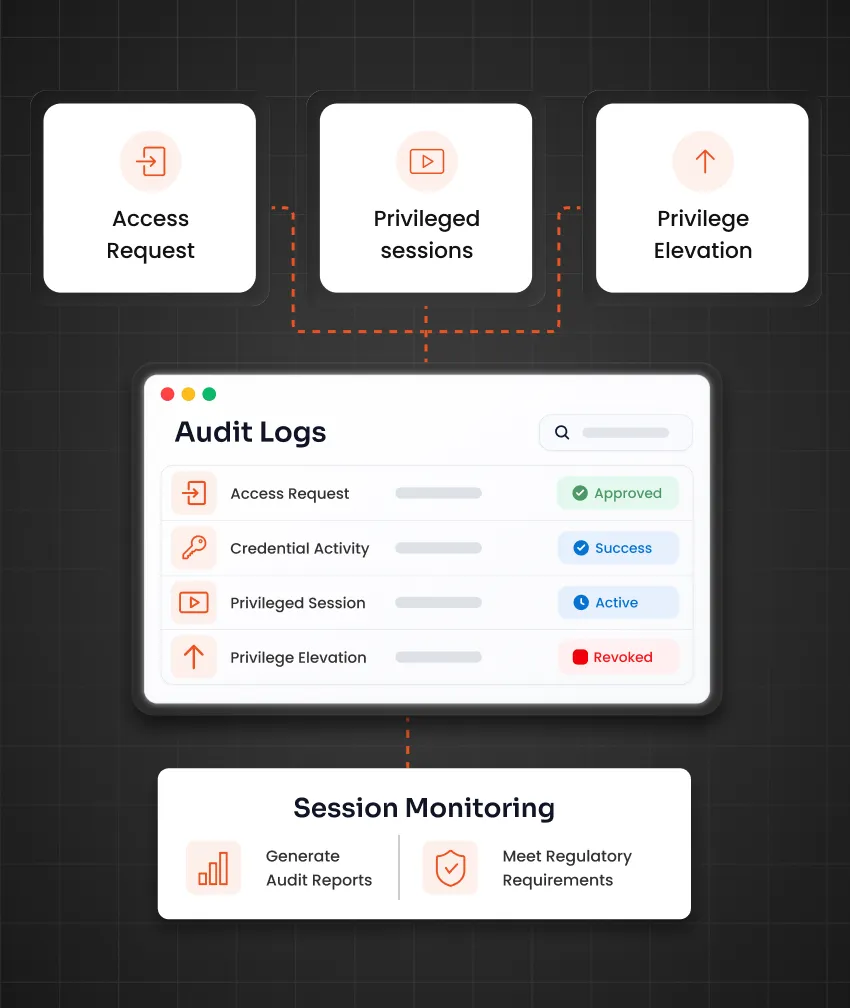
Keep a centralized record of access requests, approvals, credential activity, privileged sessions, and privilege-elevation events. Prove your compliance with federal, state, and local regulatory requirements.
Know MoreControl privileged access to servers, databases, applications, network devices, and other critical infrastructure. A strong PAM solution built for government organizations keeps your core systems locked down.
Provide temporary privileged access to external personnel. Apply access policies, use approvals and time limits where required, and maintain complete visibility into their activities.
Centralize access controls across on-premises infrastructure and cloud environments so security teams have a consistent way to manage privileged access.
Enable administrators to securely access critical infrastructure remotely. Let them manage systems from anywhere without exposing privileged credentials to the public internet.
Control privileged access to databases containing citizen, financial, healthcare, and other highly sensitive information. Keep private data private.
Deploy agentless PAM for supported privileged access workflows without installing agents across every endpoint or server. This can reduce deployment overhead and simplify admin work.
miniOrange PAM supports cloud, on-premises, and hybrid environments, as well as air-gapped deployment options for environments that require network isolation.
Reduce the software footprint required for supported privileged access workflows with an agentless architecture. Bring privileged access controls into a centralized platform without installing endpoint agents everywhere.
Government services never sleep. Get round-the-clock support for deployment, troubleshooting, and ongoing PAM operations from miniOrange.
Government organizations rely on privileged accounts to administer critical systems and infrastructure. PAM helps control who can use those accounts, protect privileged credentials, limit access, and monitor privileged activity.
PAM protects government systems by securing privileged credentials, enforcing granular and time-bound access, monitoring privileged sessions, and maintaining audit records of privileged activity.
Yes. miniOrange PAM provides privileged credential management, JIT access, granular access controls, session monitoring, endpoint privilege management, and flexible deployment options that can support state and local government environments.
Yes. miniOrange PAM supports on-premises deployment for organizations that need to run PAM within their own infrastructure.
Yes. miniOrange offers a 30-day free PAM trial with no credit card required.
miniOrange provides air-gapped deployment options for PAM alongside cloud, on-premises, and hybrid deployment models. The appropriate deployment approach depends on the environment and connectivity requirements.