Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×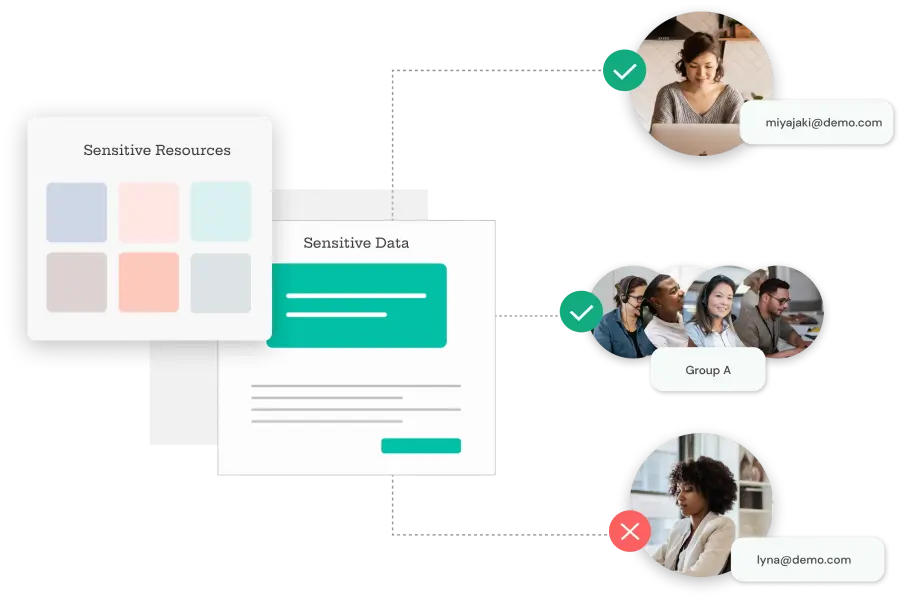
Granular access control means giving specific permissions to users or groups, allowing them access to the resources or data they need, and nothing more. Granular access control aka granular security mechanism enables a business to manage and restrict access levels of their data and resources, in a highly detailed way. Rather than giving complete access to users, it breaks down permissions into specific actions or objectives, ensuring users only have the access they need and no more.
Granular access control is an important component under Identity and Access Management (IAM) and Privileged Access Management (PAM). In simple terms, granular access control acts as a safety net. It separates those who can see or modify data from those who can carry out tasks. This strengthens security and clearly defines roles within an organization or system.
Additionally, through role-based capabilities, PAM limits actions users can undertake on remote applications, including SSH, RDP (Remote Desktop Protocol), and database systems. This strategy effectively reduces standing privileges, ensuring users can only execute operations specifically provisioned to them.

A centralized platform manages credentials, limits access, tracks data, and maintains logs, reducing breach risks and enhancing security.

Enables fine-tuned access rights for users or groups, with custom restrictions on sensitive data based on roles and job functions.

Facilitates detailed documentation and audit trails, ensuring compliance with industry standards and regulations such as HIPAA and GDPR.
Explore comprehensive PAM features, integration methods, compliance benefits, and everything you need in one place.
Your download should start now. If not, please email us at idpsupport@xecurify.com.
Please enter a valid email-id

Command restriction controls what commands users can run. This is crucial for preventing unauthorized access or misuse of sensitive commands. For example, administrators can block specific commands in PowerShell or Command Prompt (CMD) to stop users from running high-risk actions.
Query restriction limits the types of database queries users can execute. For instance, you can allow users to only view data without the ability to change it. Use SQL permissions or Role-Based Access Control (RBAC) to control who can run which types of queries.
Roles define what users or services can do, and capabilities are the specific actions allowed for each role. This approach is known as Role-Based Access Control (RBAC).
App restrictions prevent users from running unauthorized applications when accessing a system remotely, whether through RDP, SSH or VNC.
When determining the specific security requirements for granular permissions within your organization, you have several options to consider
RBAC is based on granular access control that limits access based on the user’s role in an organization, where every role has specific permissions associated with it. Instead of assigning permissions to each user, they are assigned to a role, that defines their level of access.
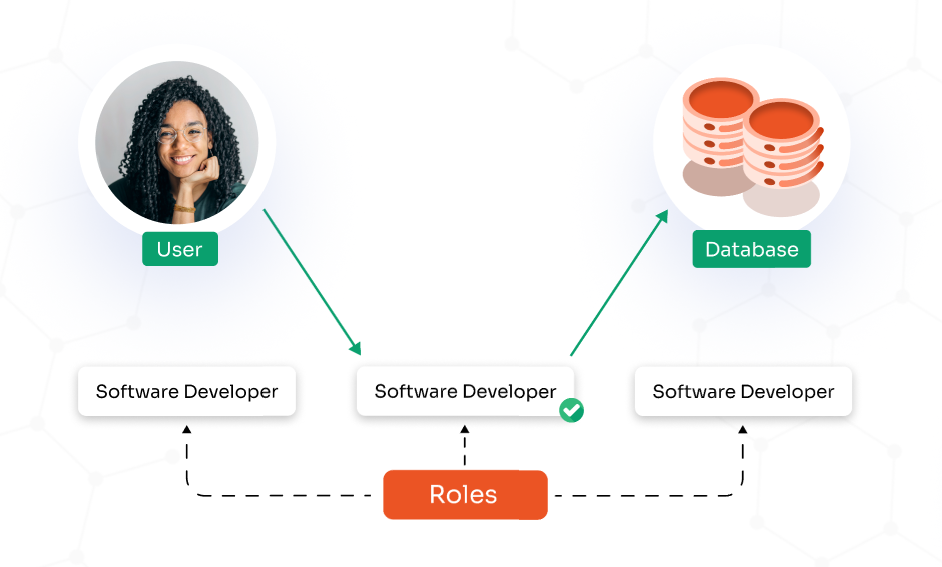
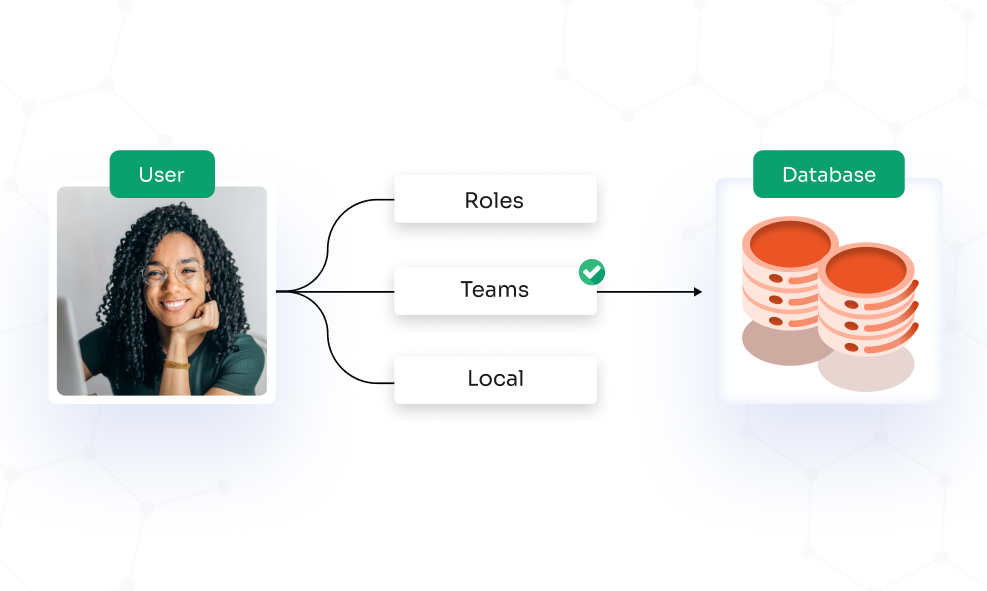
Access control is defined by user attributes like user role, time, rank, location, etc. Access to data and resources is granted based on the combination of these attributes.
In an MBAC system, the administrator implements controls specifically for high-security environments. Access is granted or denied based on the sensitivity of the information within the resources and the user’s security clearance level, such as confidential or top secret.
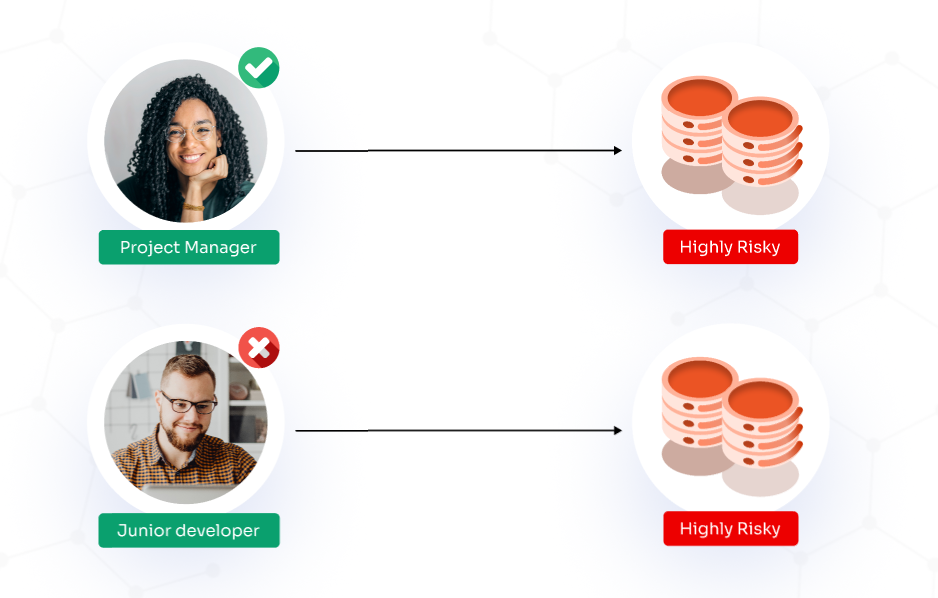
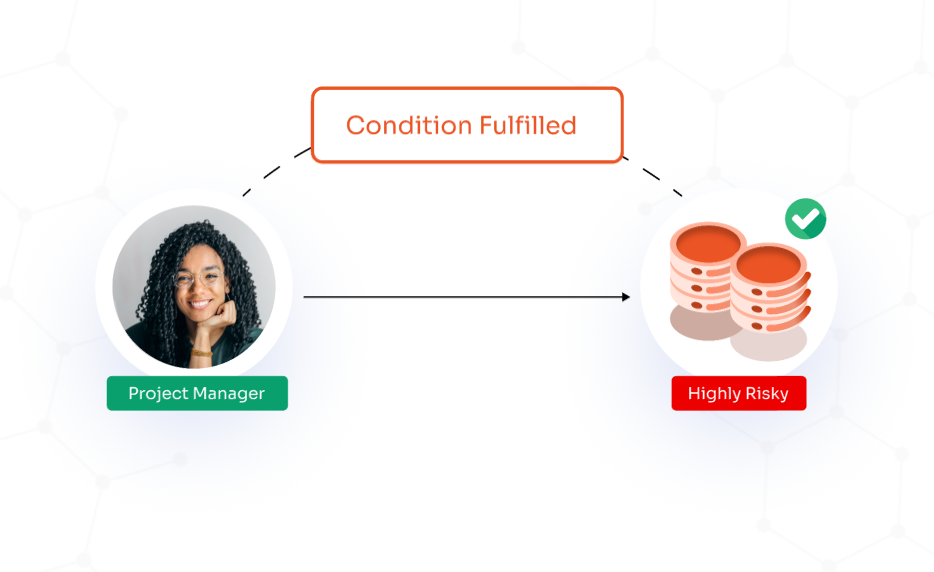
DBAC allows users to manage access to their resources, enabling them to decide who can access their data & under what conditions. Users have the option to set access rights and set the conditions for this access as it can introduce security risks if permissions are not carefully maintained.