Access Reviewer360 vs Jira Native Tools
Complete Access Governance for Jira Cloud
Jira's native tools weren't built for access reviews. The Audit Log only logs changes after the fact, and the Permission Helper checks one user at a time. Access Reviewer360 delivers project-level reviews, automatic risk detection, and audit-ready exports.

Access Reviewer360
vs Jira Native Tools
Jira's native tools weren't built for access reviews. The Audit Log only logs changes after the fact, and the Permission Helper checks one user at a time. Access Reviewer360 delivers project-level reviews, automatic risk detection, and audit-ready exports.
Try Now for FreeComprehensive Comparison
Access Reviewer360 vs Jira Native Tools (Audit Log & Permission Helper) for Jira Cloud
Access Visibility & Coverage

 One user / one item at a time (Permission Helper)
Risk Detection & Governance
Monitoring & Reporting
Records config changes only, after the fact
Administration & Support
Manual cross-referencing required
What Sets Access Reviewer360 Apart?
Explore the key benefits that make Access Reviewer360 the faster, audit-ready way to govern Jira access.
Complete Access Visibility
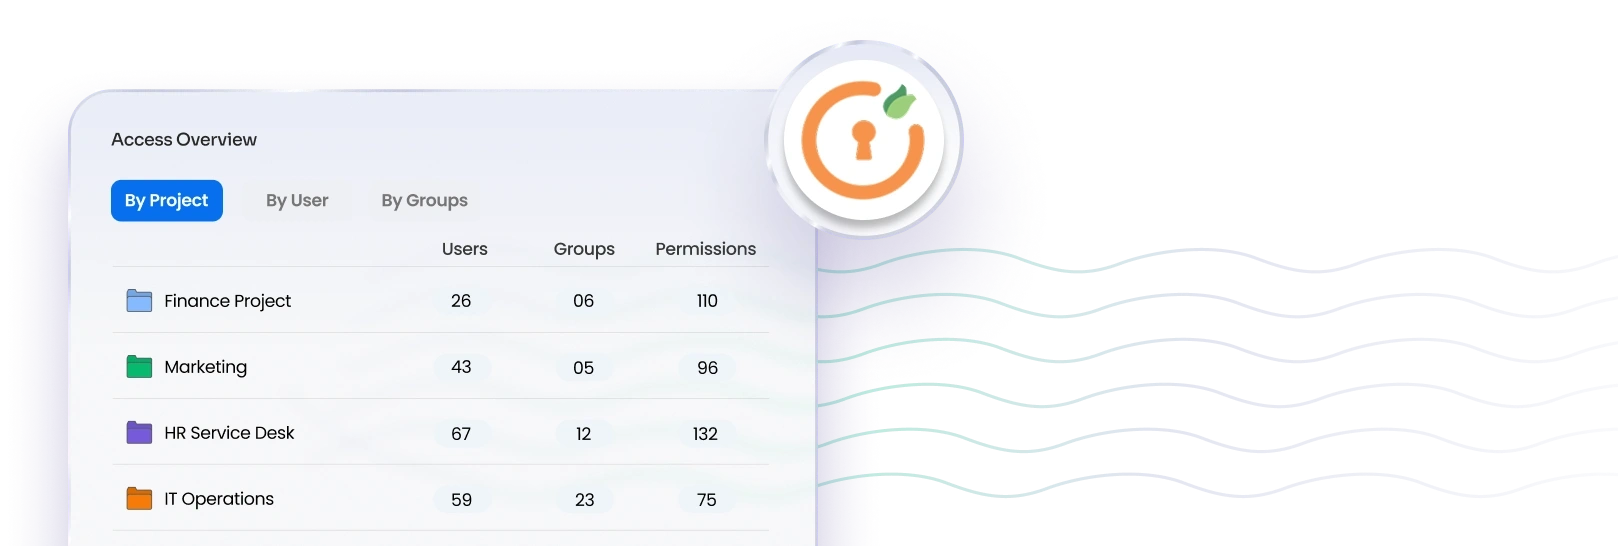
See who holds every global and project permission, by project, by user, or by group. Roles (direct and group-inherited), group memberships, issue security levels, and app / service-account grants are mapped into full access paths.
Access Path Analysis
Trace the exact chain of role, group, and grant behind every permission. When you can see why someone has access, you enforce least privilege by removing the link, not guessing.
Automatic Risk Detection
Dormant access across each project's history, excessive administrators, external users, and privileged accounts surface on their own, 8+ built-in policies, not a spreadsheet you build the night before an audit.
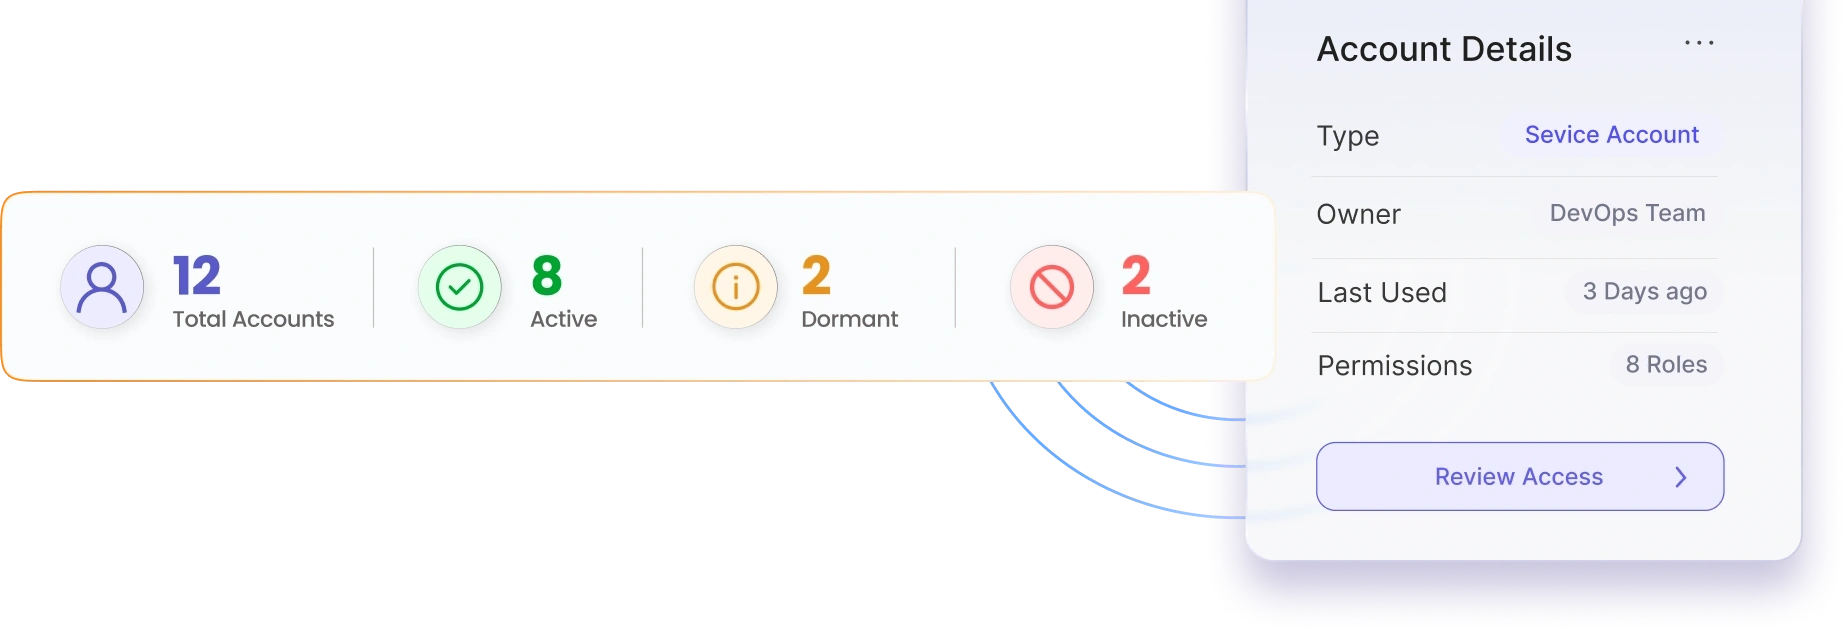
Service Account & Automation Visibility
Non-human access, often the easiest to overlook, is governed with the same rigor as your users, keeping ghost application accounts and ungoverned service accounts front and center.