- Home
- 2FA
- 2FA Documentation
- Two-factor Authentication for JSM

How to Set Up Two-Factor Authentication (2FA) for JIRA Managed and External Users
The miniOrange Two-Factor Authentication (2FA) app lets you enforce 2FA for your Jira managed and external users through Atlassian Guard. This guide walks you through the complete setup, from selecting your region and activating Atlassian Guard Standard, to configuring SAML or OAuth SSO (with or without an external Identity Provider) and enabling 2FA authentication policies.
 Try it for free
Pre-requisites
- A Jira Cloud instance with admin access.
- Atlassian Admin permissions.
Download and Installation
Access Jira Admin
- Log in to your Jira Cloud instance as an administrator.
- Navigate to Settings → Apps → Manage Apps.
Install the App
- Click Find New Apps.
- Search for mO 2FA for Jira (Two Factor Authentication).
- Click Try it free to begin a trial, or Buy now to purchase.
- Select a site if you have multiple sites, then click Review.
- Click Start Free Trial. You will be redirected to MyAtlassian.
- Click Apply license.
Access the Application
- Navigate to Apps → mO 2FA for Jira (Two Factor Authentication).
- You will be redirected to the application in a new tab.
Setup Tab
The Setup tab guides you through the initial configuration in a linear wizard. Complete each step in order: select your region, configure Atlassian Guard, choose whether your users use an external Identity Provider, and finish the Guard integration.
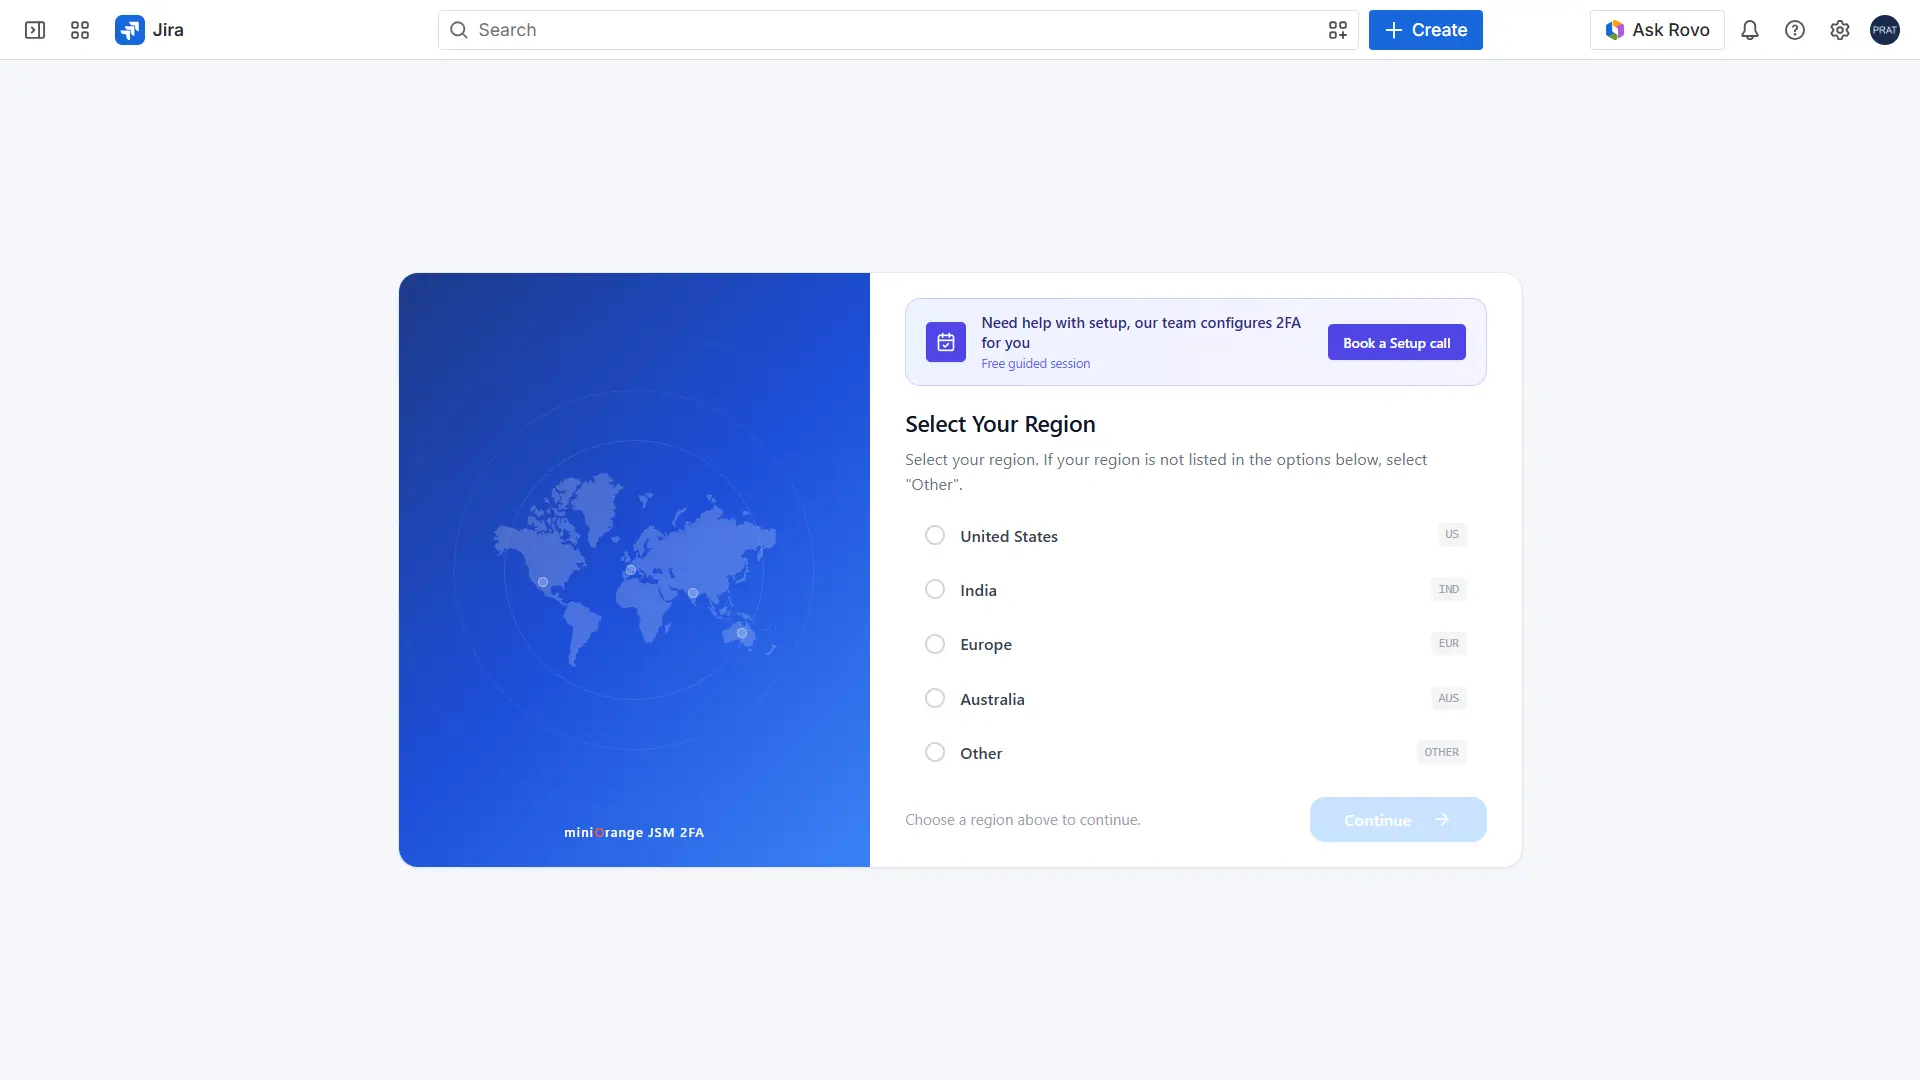
1. Select Your Preferred Region
To ensure optimal performance, low latency, and compliance with data residency requirements, the plugin provides multiple regional server locations. Servers are currently available in the following regions:
- United States
- India
- Europe
- Australia
- Other (for regions not listed above)
Select the region that best matches your organization's data residency requirements, or the one geographically closest to your users, for the best authentication performance and response times.
2. Configure Atlassian Guard
To configure 2FA for your Jira managed and external users, you must have an active Atlassian Guard Standard subscription for your organization.
If Atlassian Guard Standard is already active, you can skip this step and proceed to the next section. If you do not yet have an active Guard subscription, follow the steps below.
Enable Atlassian Guard Standard (Free Trial)
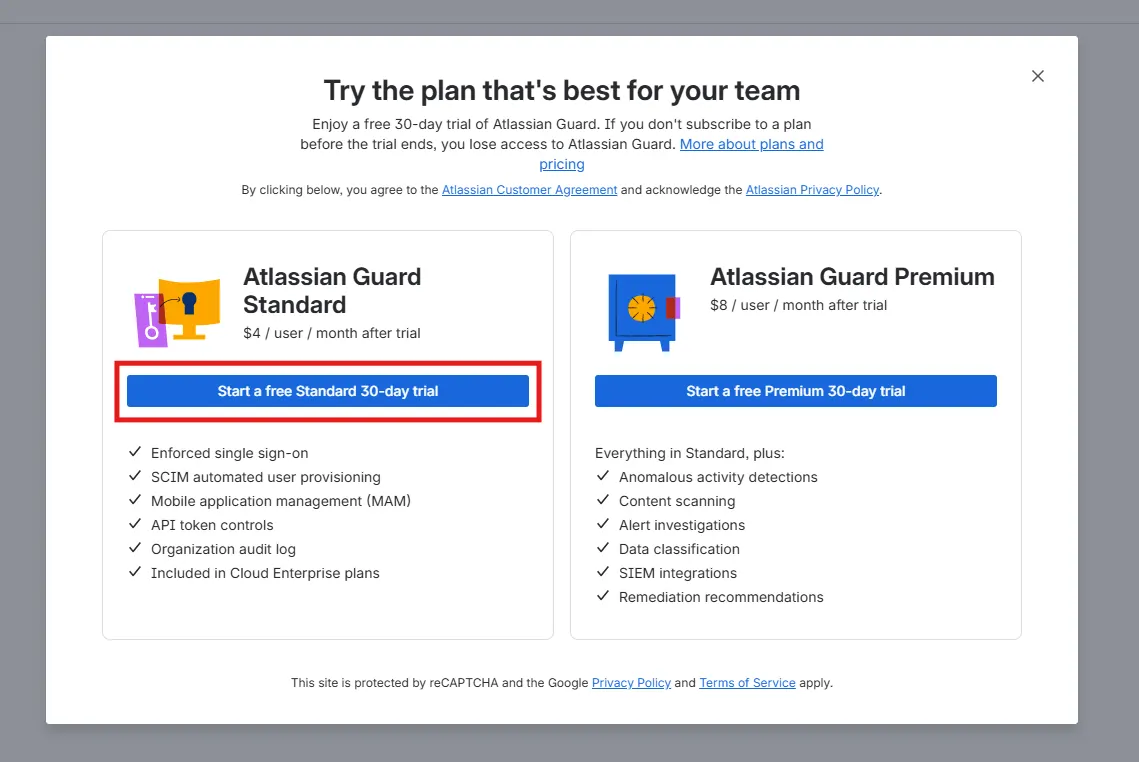
Open the Atlassian Guard admin page: https://admin.atlassian.com/atlassian-guard
- Open the Atlassian Guard admin page (linked above).
- If your account manages multiple organizations, select the organization where you want to configure 2FA for managed and external users.
- Click Start a free Standard 30-day trial to activate the trial for the selected organization.
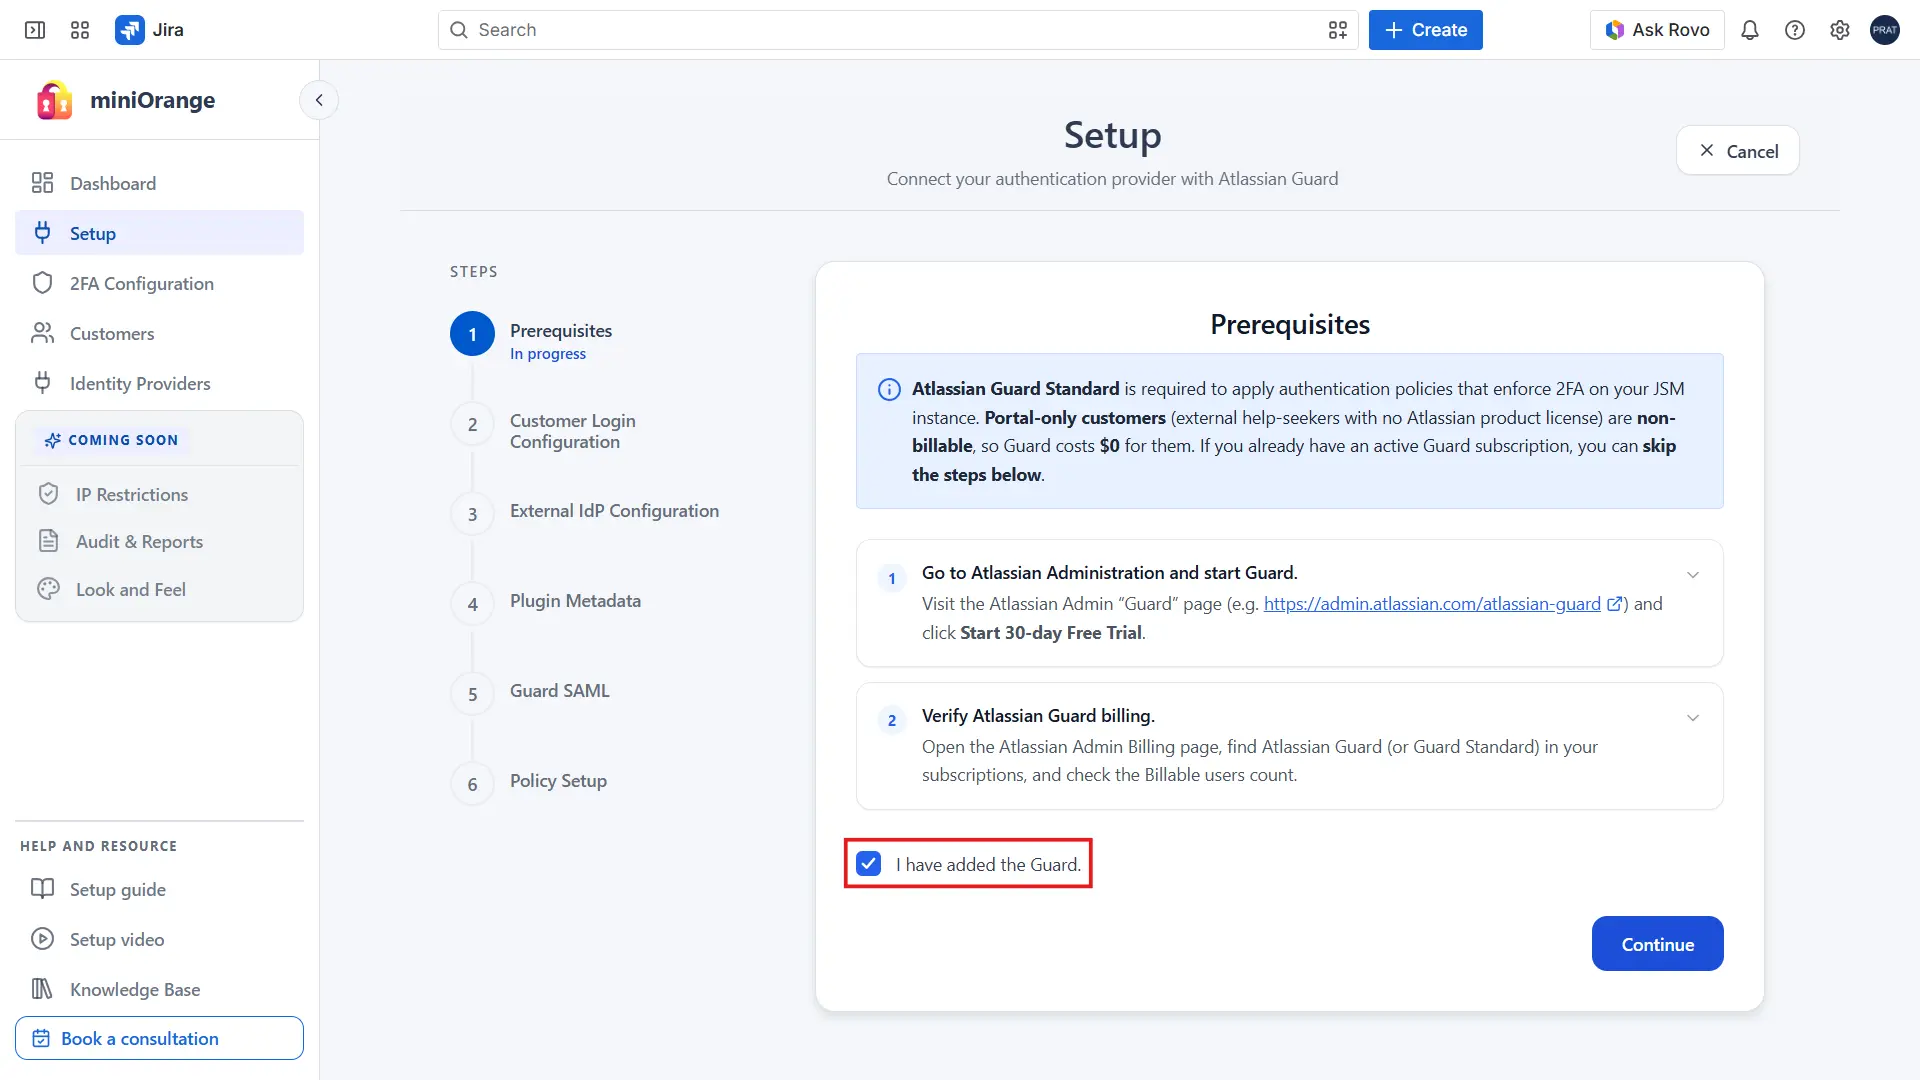
- Return to the 2FA app's Setup tab, select the confirmation checkbox, then click Continue to proceed.
3. Configure External Identity Provider
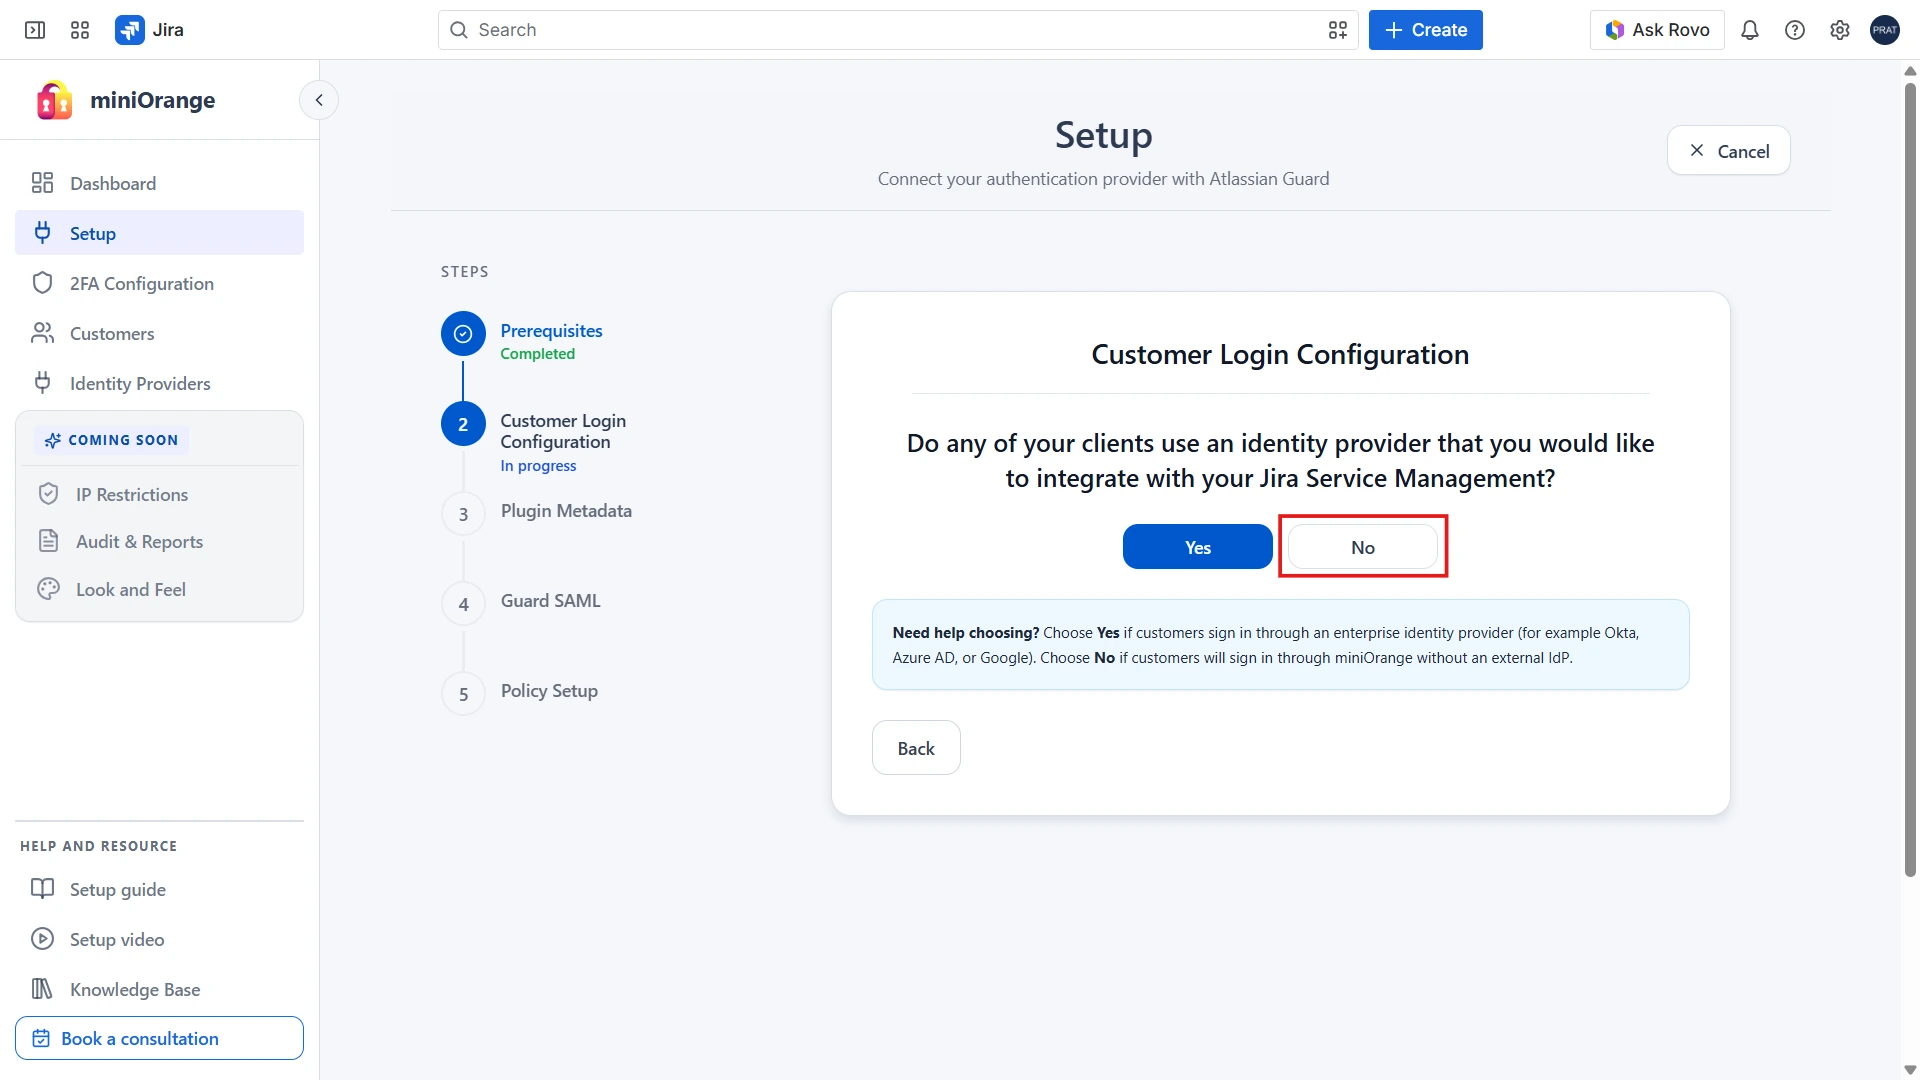
In this step, choose whether your users authenticate using an external Identity Provider (IdP).
- Select Yes if your users use an external Identity Provider, such as Okta, Microsoft Entra ID (Azure AD), Google Workspace, or any other SAML/OAuth provider, to sign in to your Jira site. You will then continue with the Identity Provider configuration below.
- Select No if your users do not use an external Identity Provider. In this case, you can skip the IdP configuration and proceed directly to the Guard Setup step.
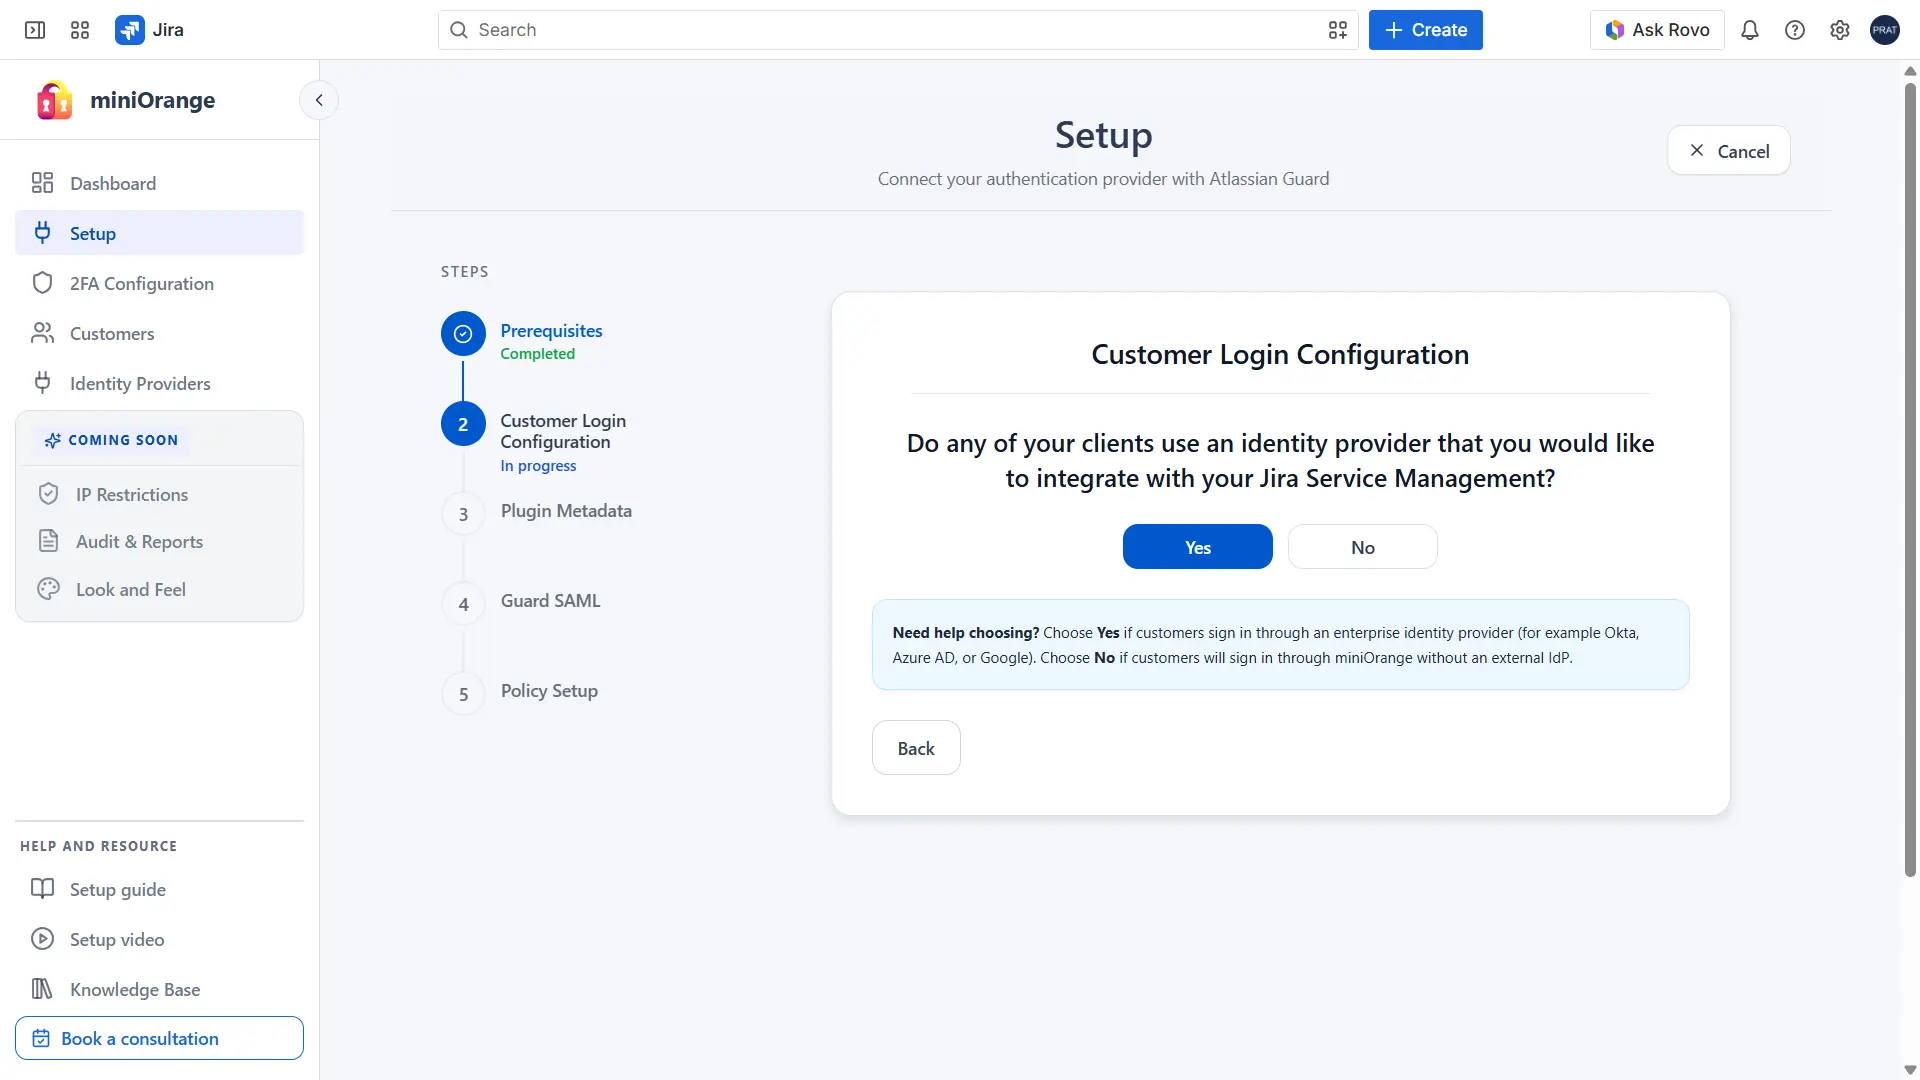
3A. If You Use an External Identity Provider
If you selected Yes, configure your external IdP using either SAML or OAuth/OIDC, depending on what your provider supports.
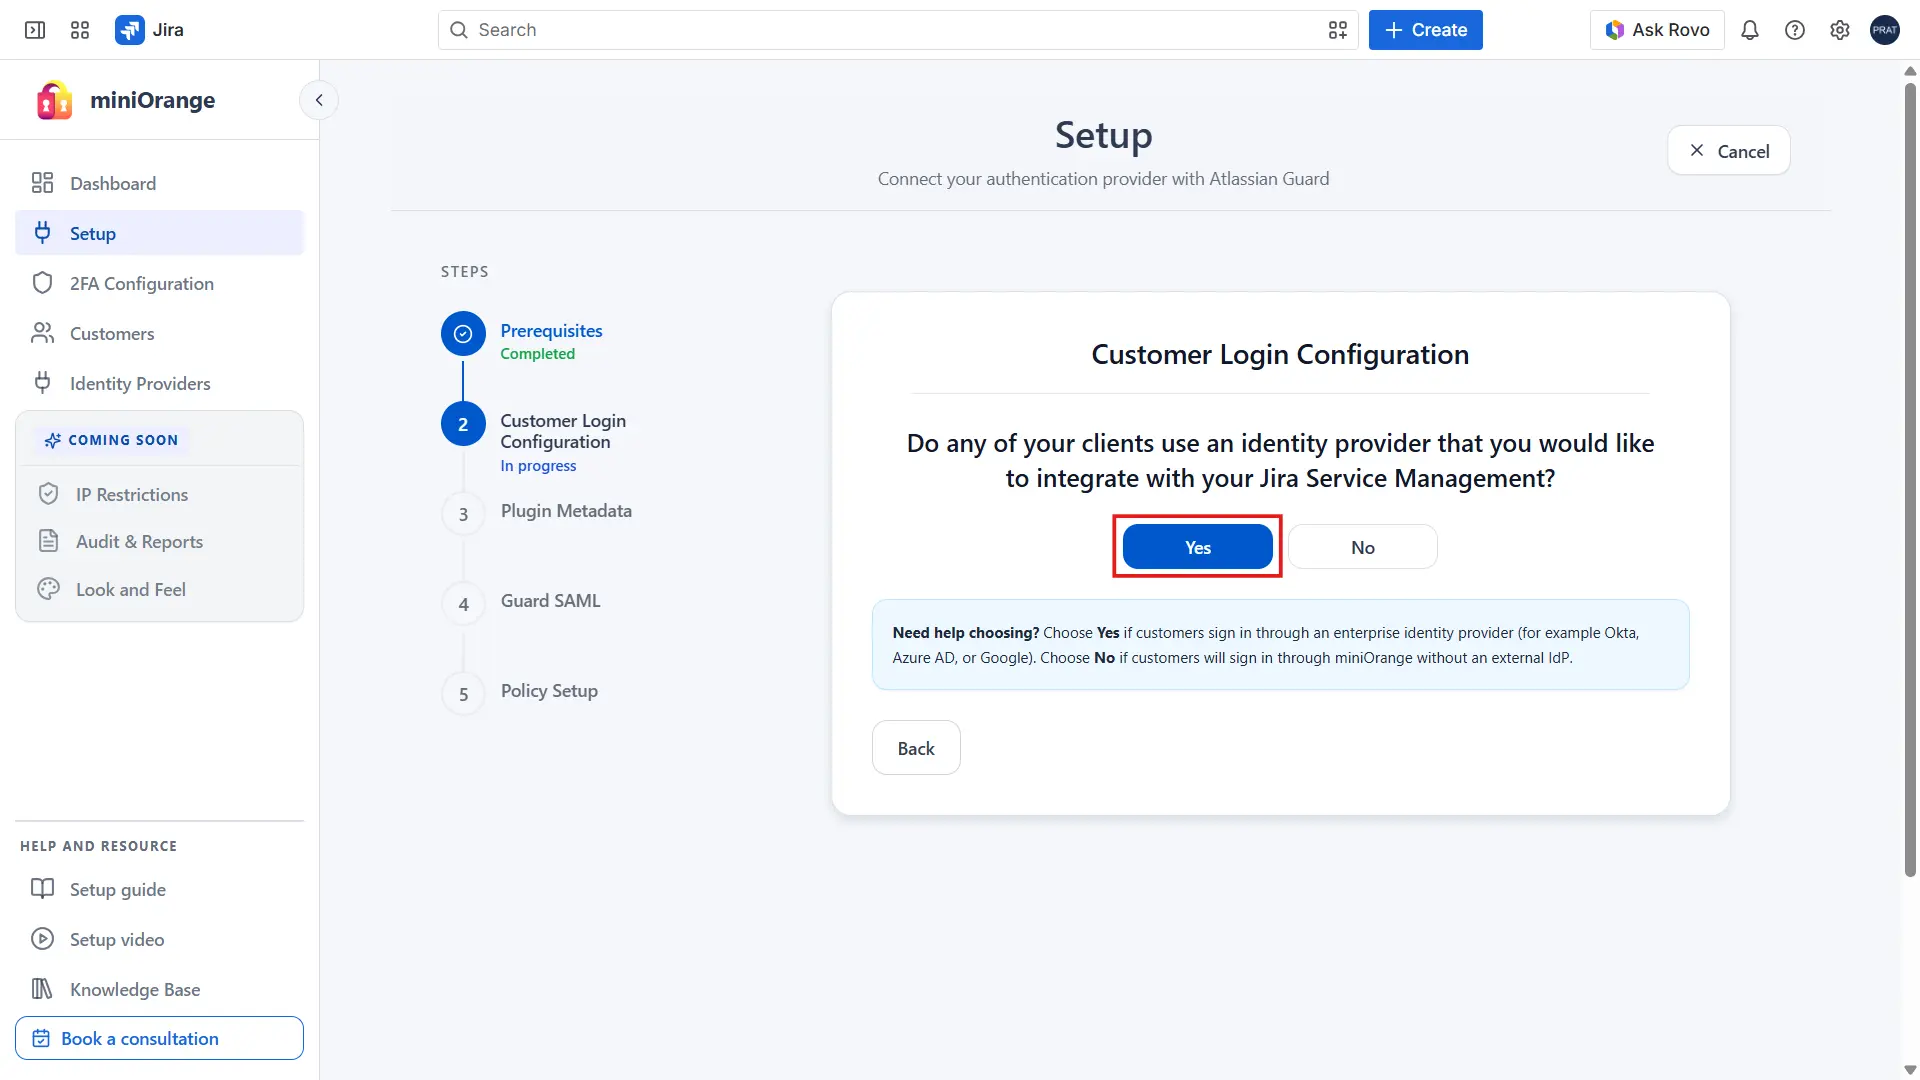
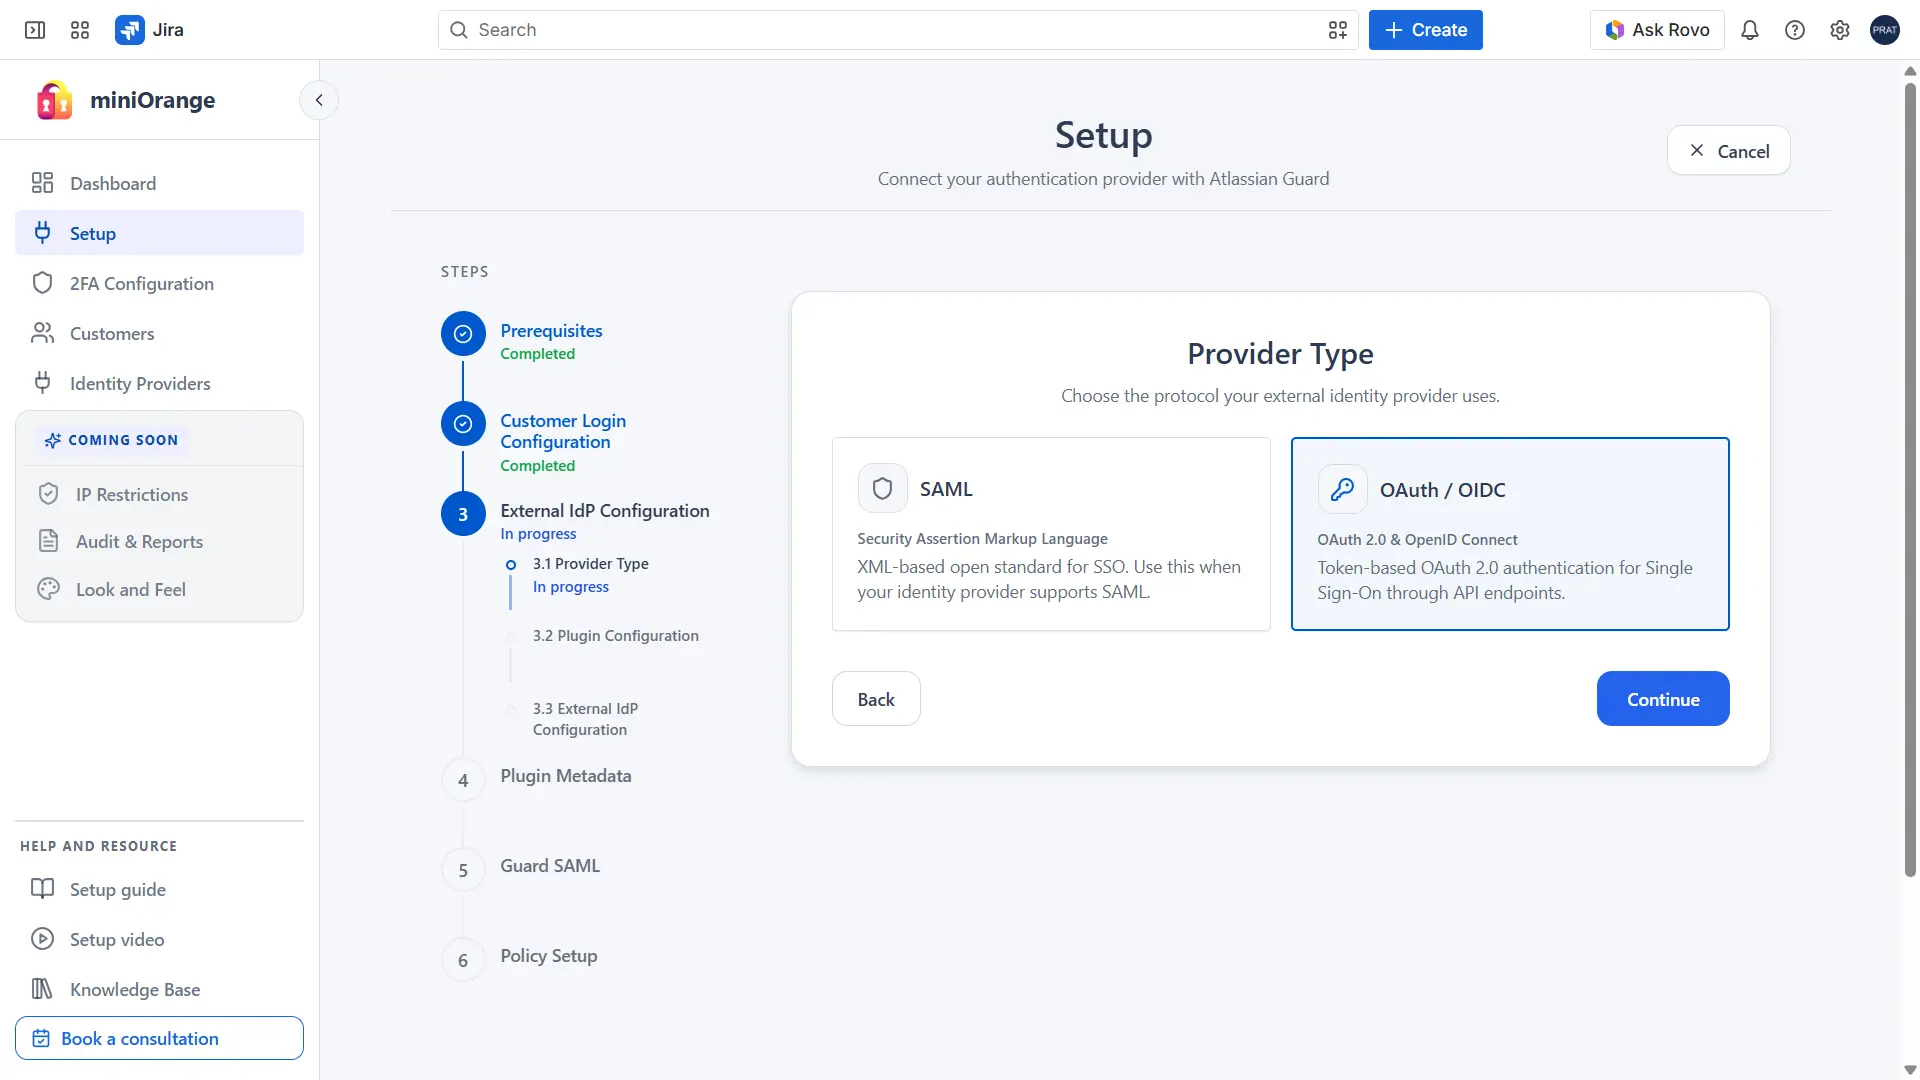
Select the Identity Provider Protocol
Select the authentication protocol used for Single Sign-On (SSO). The plugin supports:
- SAML
- OAuth / OpenID Connect (OIDC)
Choose the protocol supported by your Identity Provider and follow the matching configuration below.
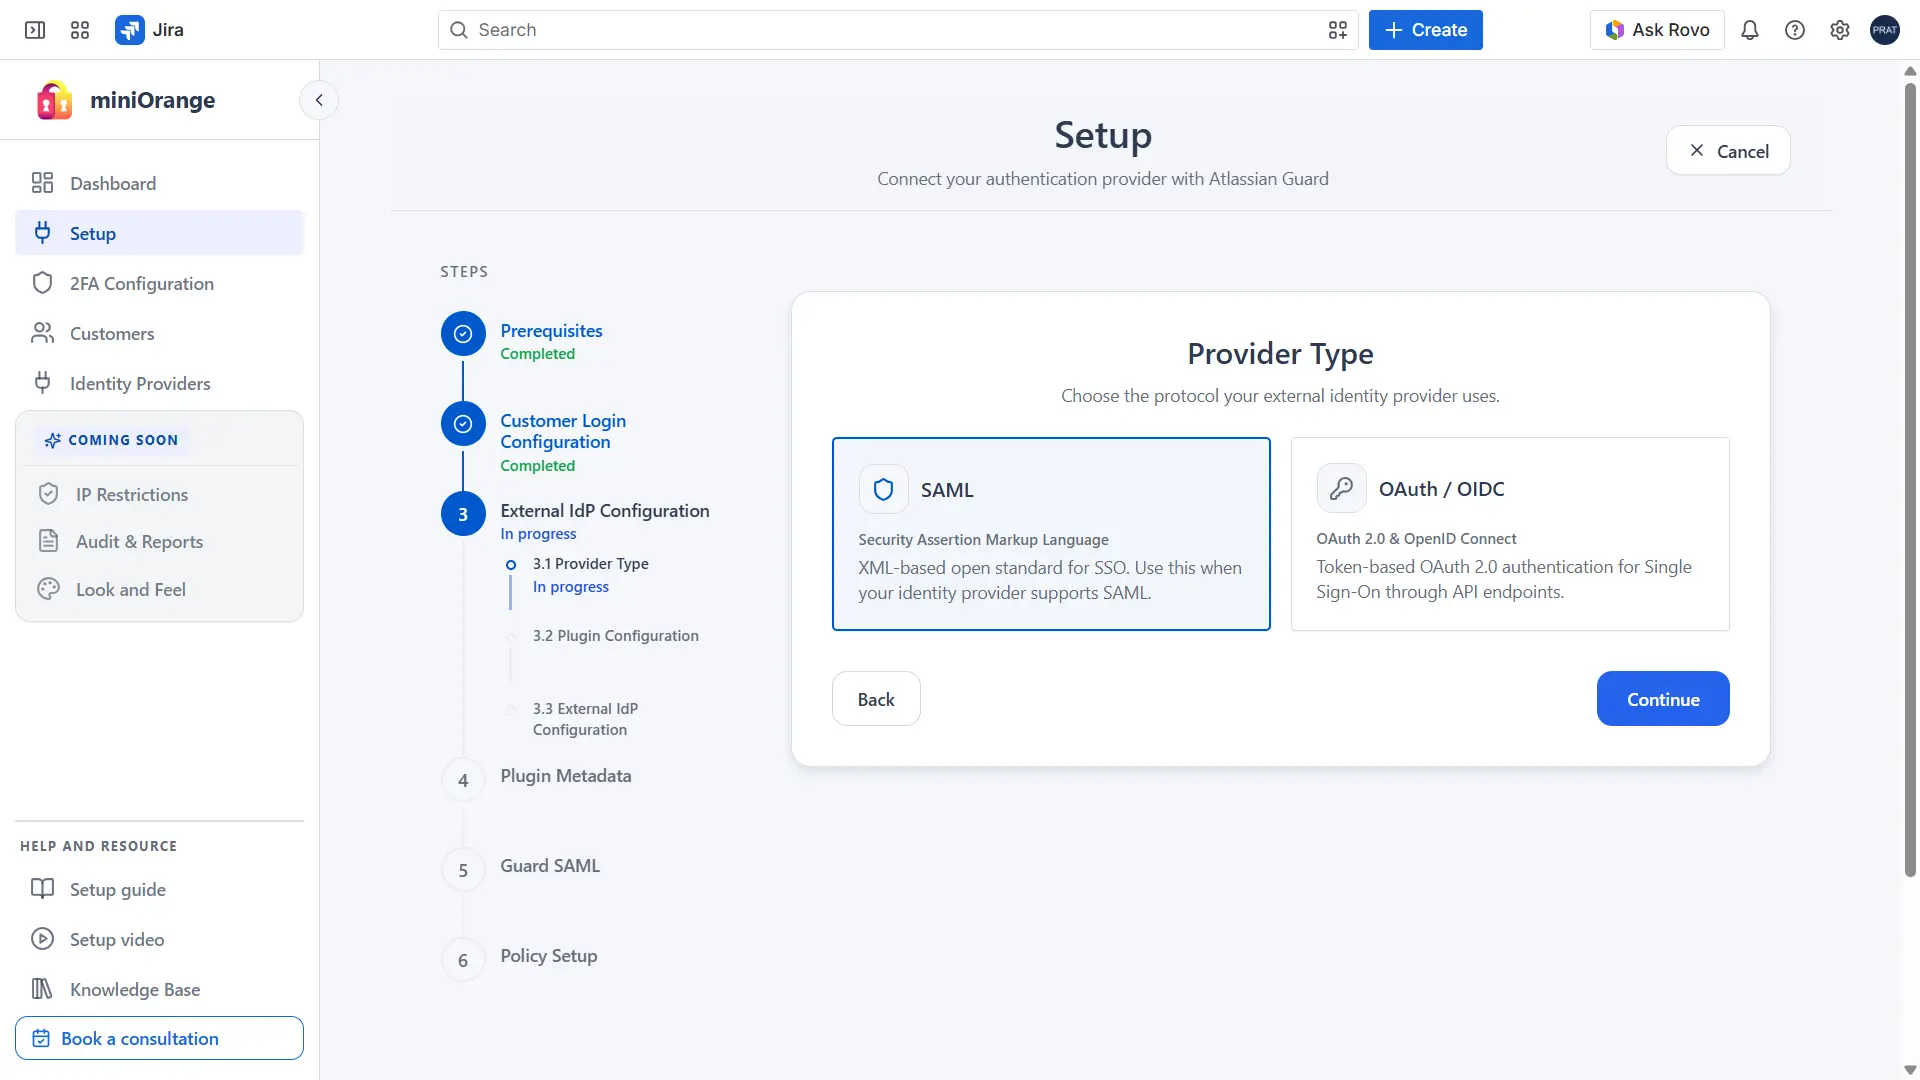
Option 1: SAML Configuration
i. Configure Your Application in the Identity Provider (IdP)
Create a SAML application in your Identity Provider using the Service Provider (SP) details provided by the plugin.
- Copy the SAML Service Provider (SP) configuration metadata displayed by the plugin.
- Log in to your Identity Provider's administrator dashboard and navigate to the Applications section.
- Click Create Application (also called Create App Integration, or the equivalent in your IdP).
- When prompted for a sign-in protocol, choose SAML 2.0 and proceed.
- Enter the requested details, Application Name, Audience URI (SP Entity ID), Single Sign-On (ACS) URL, and any other SAML settings. These values are shown in the SAML Plugin Configuration step within the plugin.
- Review the configuration and complete the application creation process.
- Assign the required users and/or groups to the application so they can access your Atlassian instance via SSO.
- Return to the plugin setup wizard and click Continue to proceed to the SAML External IdP Configuration step.
ii. Configure Identity Provider Details in the Plugin
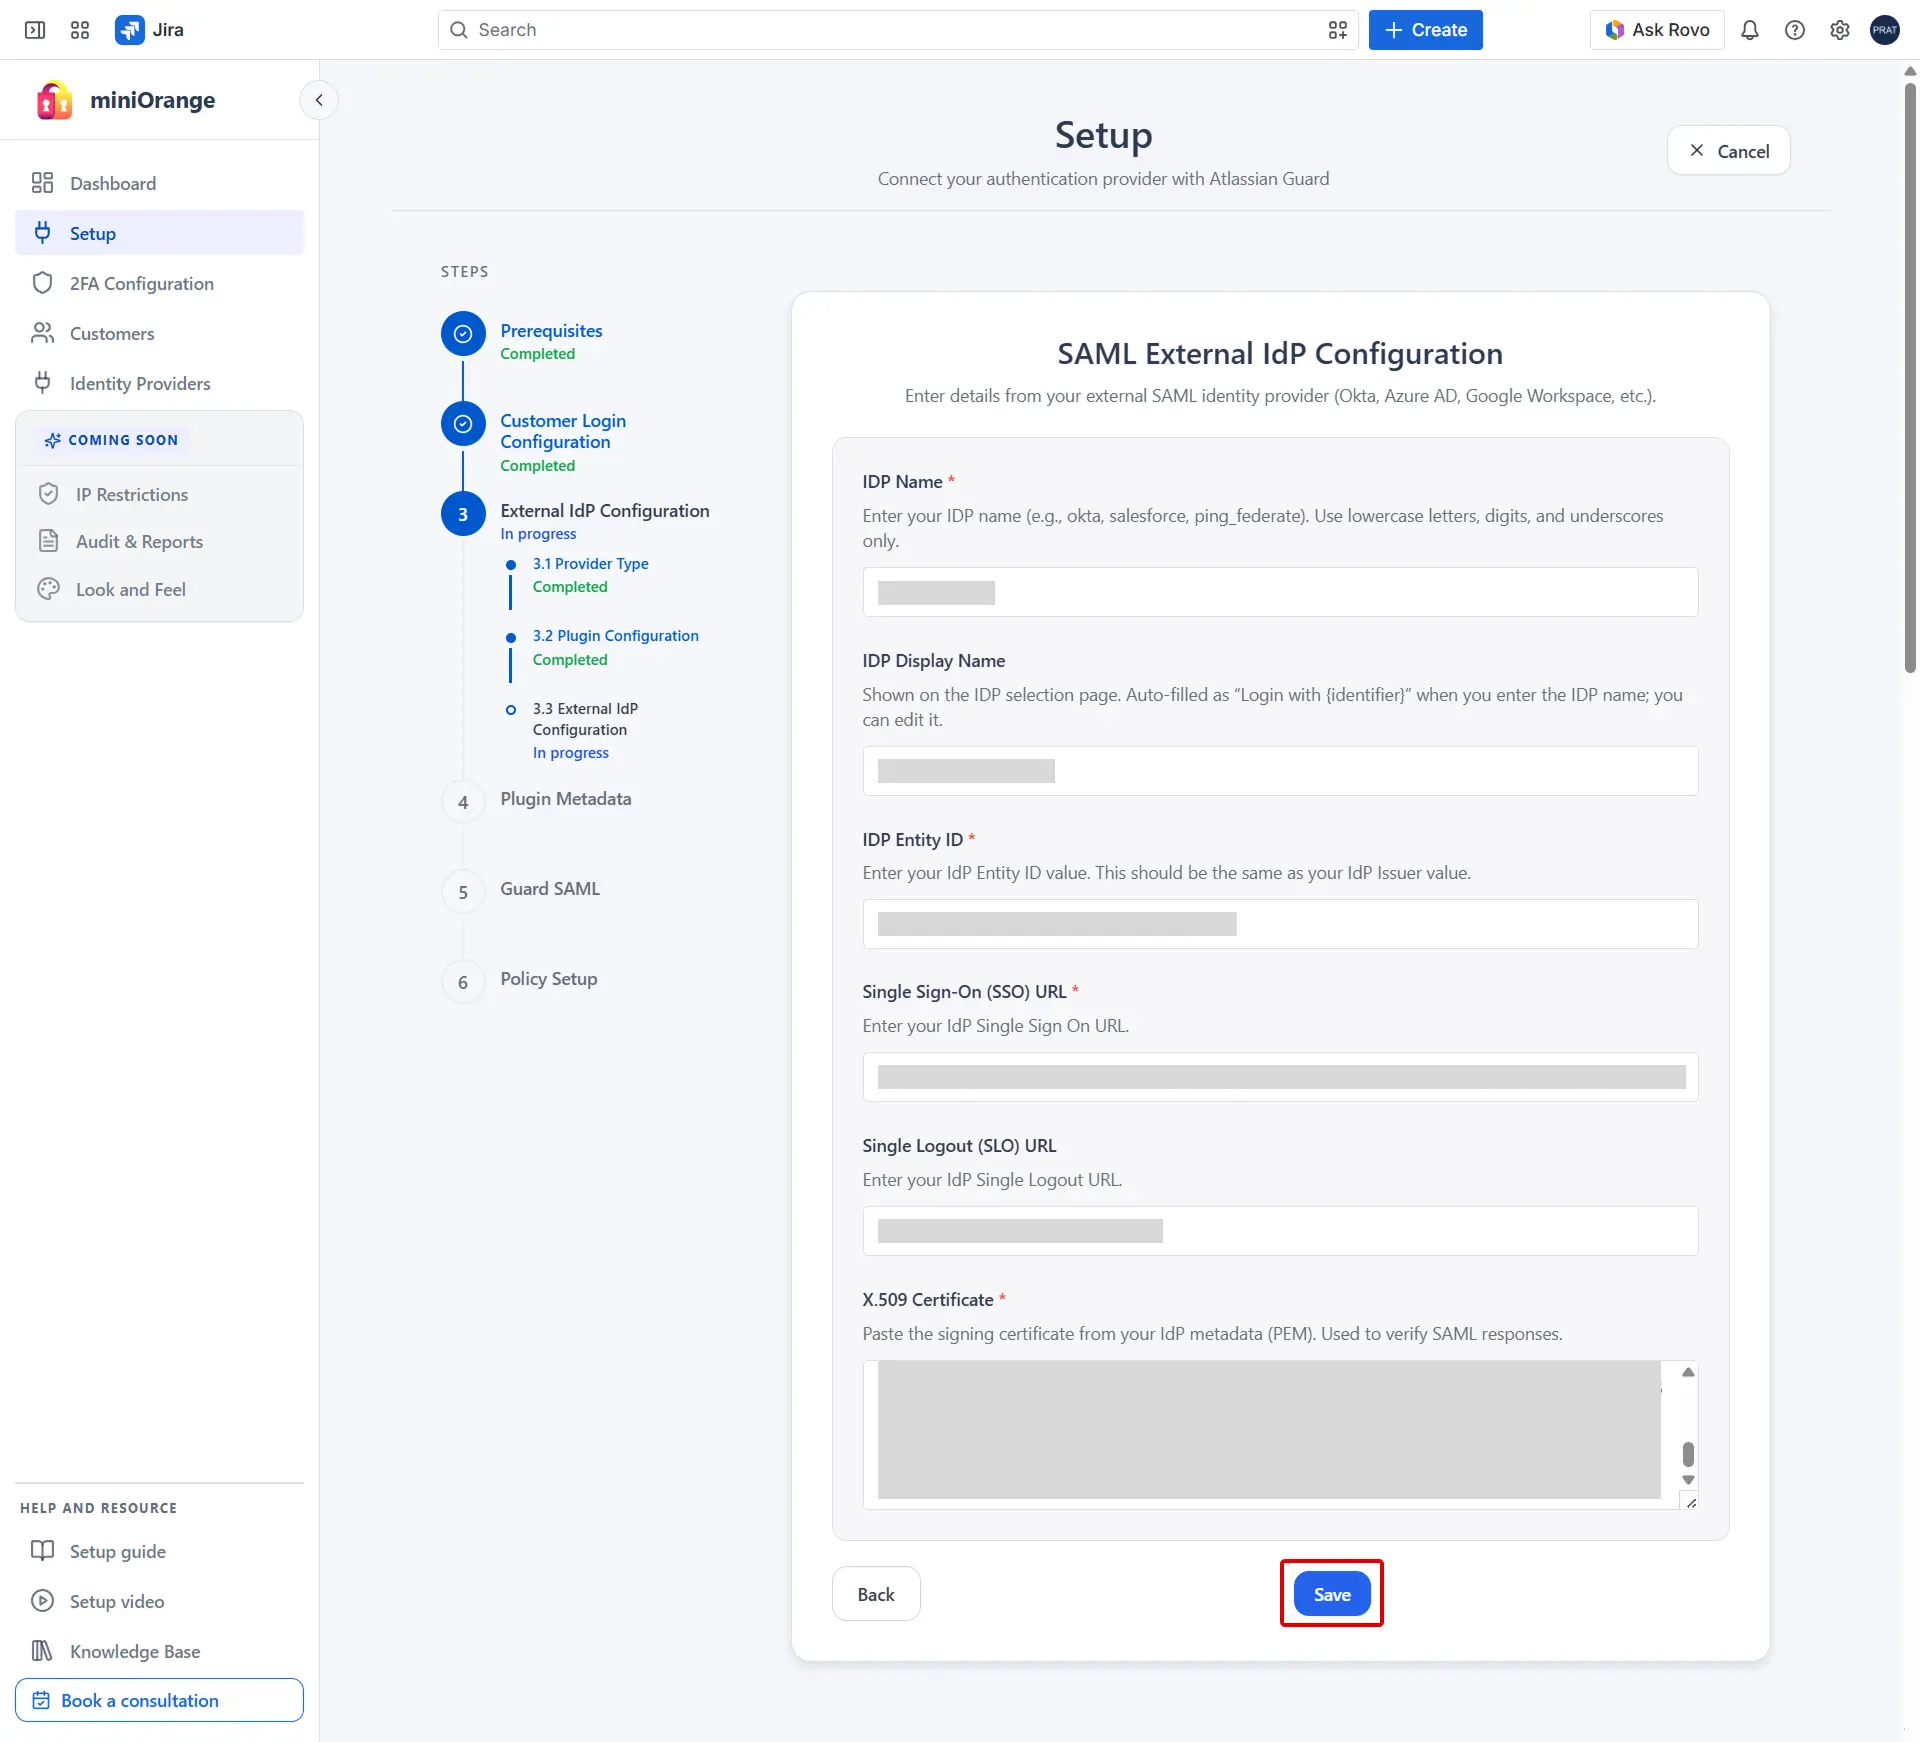
Configure the plugin on the SAML External IdP Configuration step. The following values are required:
- IdP Name
- Idp Display Name
- Idp Entity ID (Issuer)
- Single Sign-On (SSO) URL
- X.509 Certificate
These values are typically found in the SAML configuration or metadata section of your IdP after the application has been created.
- Locate the required SAML configuration values in your IdP dashboard.
- Paste the copied values into the corresponding fields in the SAML External IdP Configuration step and click Save.
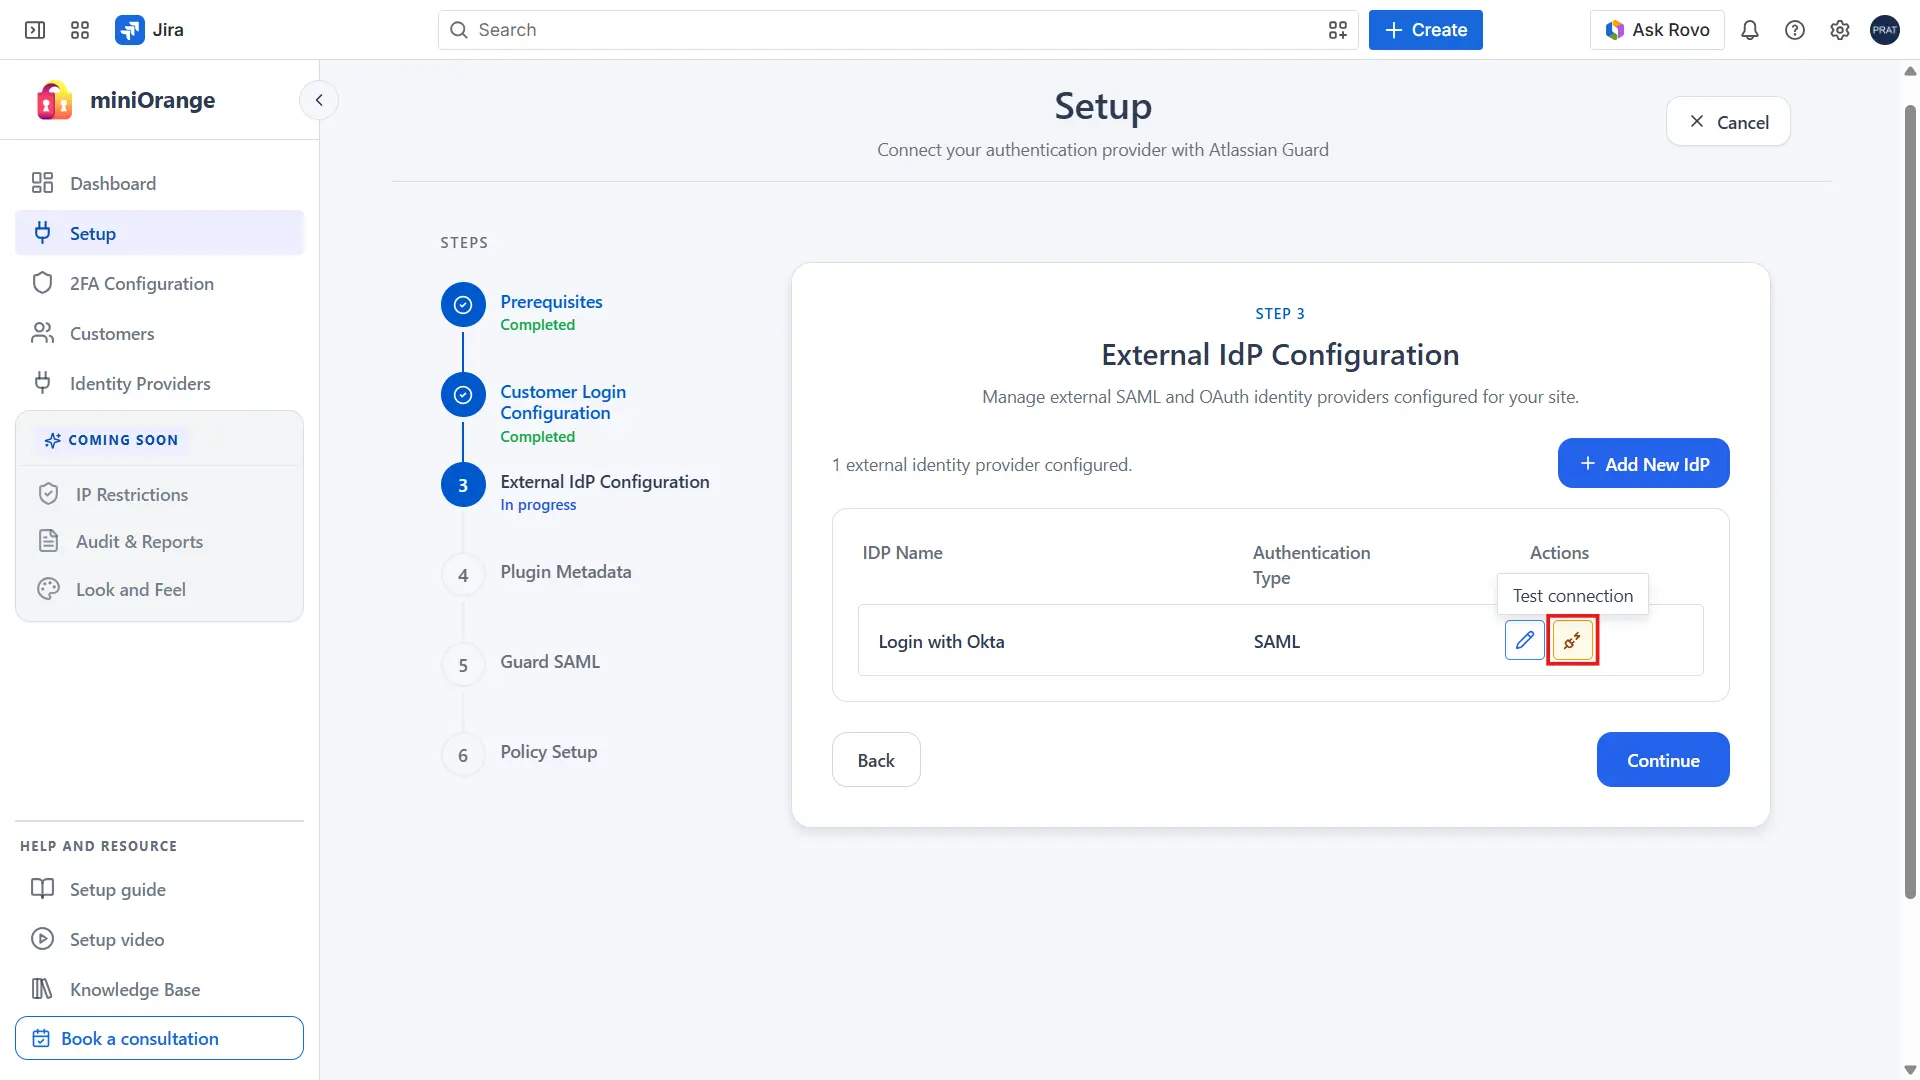
- After saving, the Identity Provider will be listed on the Configured IdPs page, where you can edit it, test the SSO connection, add more Identity Providers, or manage existing configurations.
iii. Test the SAML Connection
- Click Test Connection on the Configured IdPs page to verify that the plugin can communicate with your Identity Provider.
- If the test succeeds, the SAML integration has been configured correctly.
Option 2: OAuth / OIDC Configuration
i. Configure Your Application in the Identity Provider (IdP)
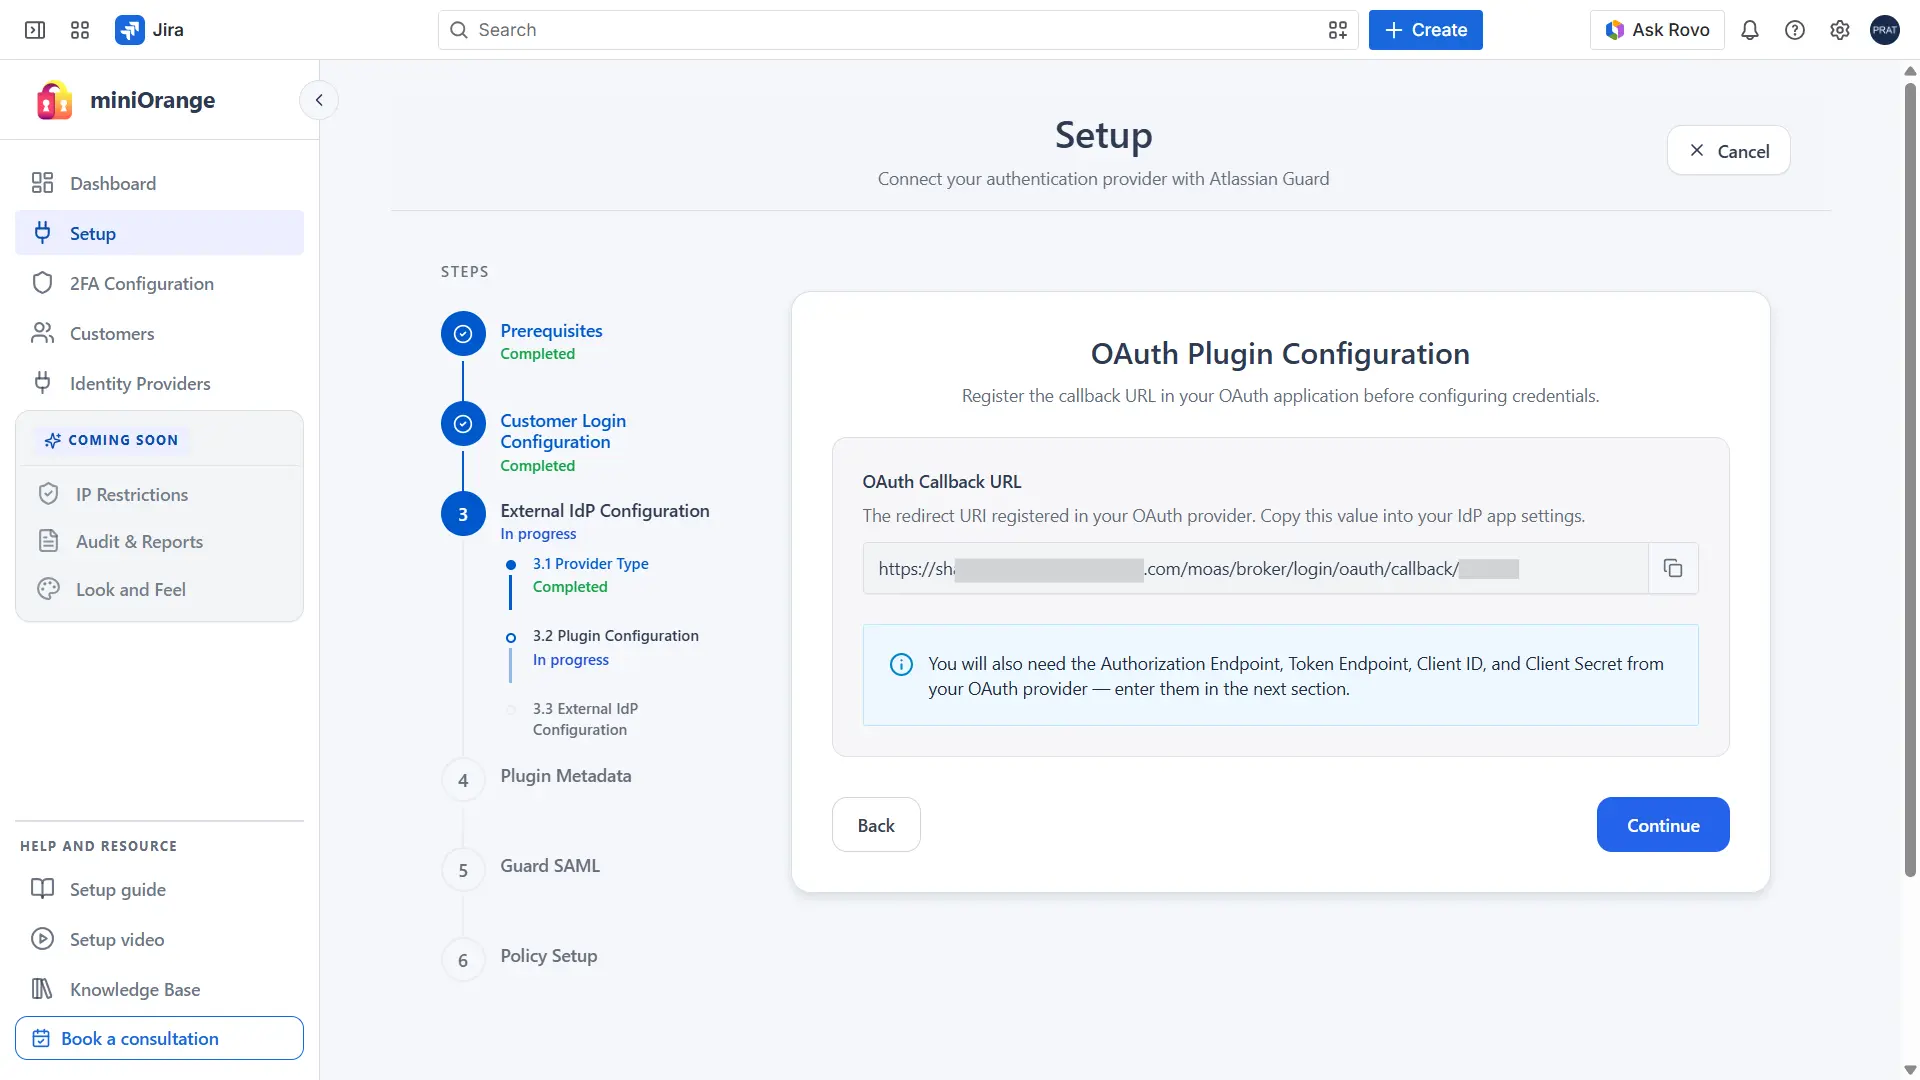
Create an OAuth/OpenID Connect (OIDC) application in your Identity Provider using the callback URL provided by the plugin.
- Log in to your Identity Provider's administrator dashboard and navigate to the Applications section.
- Click Create Application (also called Create App Integration, or the equivalent in your IdP).
- When prompted for a sign-in protocol, choose OpenID Connect (OIDC) or OAuth 2.0, depending on your Identity Provider. If asked for an application type, select Web Application and continue.
- Enter the Application Name and the Sign-in Redirect URL / OAuth Callback URL. The callback URL is shown in the OAuth Plugin Configuration step within the plugin.
- Review the configuration and complete the application creation process.
- Assign the required users and/or groups to the application so they can access your Atlassian instance via SSO.
- Return to the plugin setup wizard and click Continue to proceed to the OAuth External IdP Configuration step.
ii. Configure Identity Provider Details in the Plugin
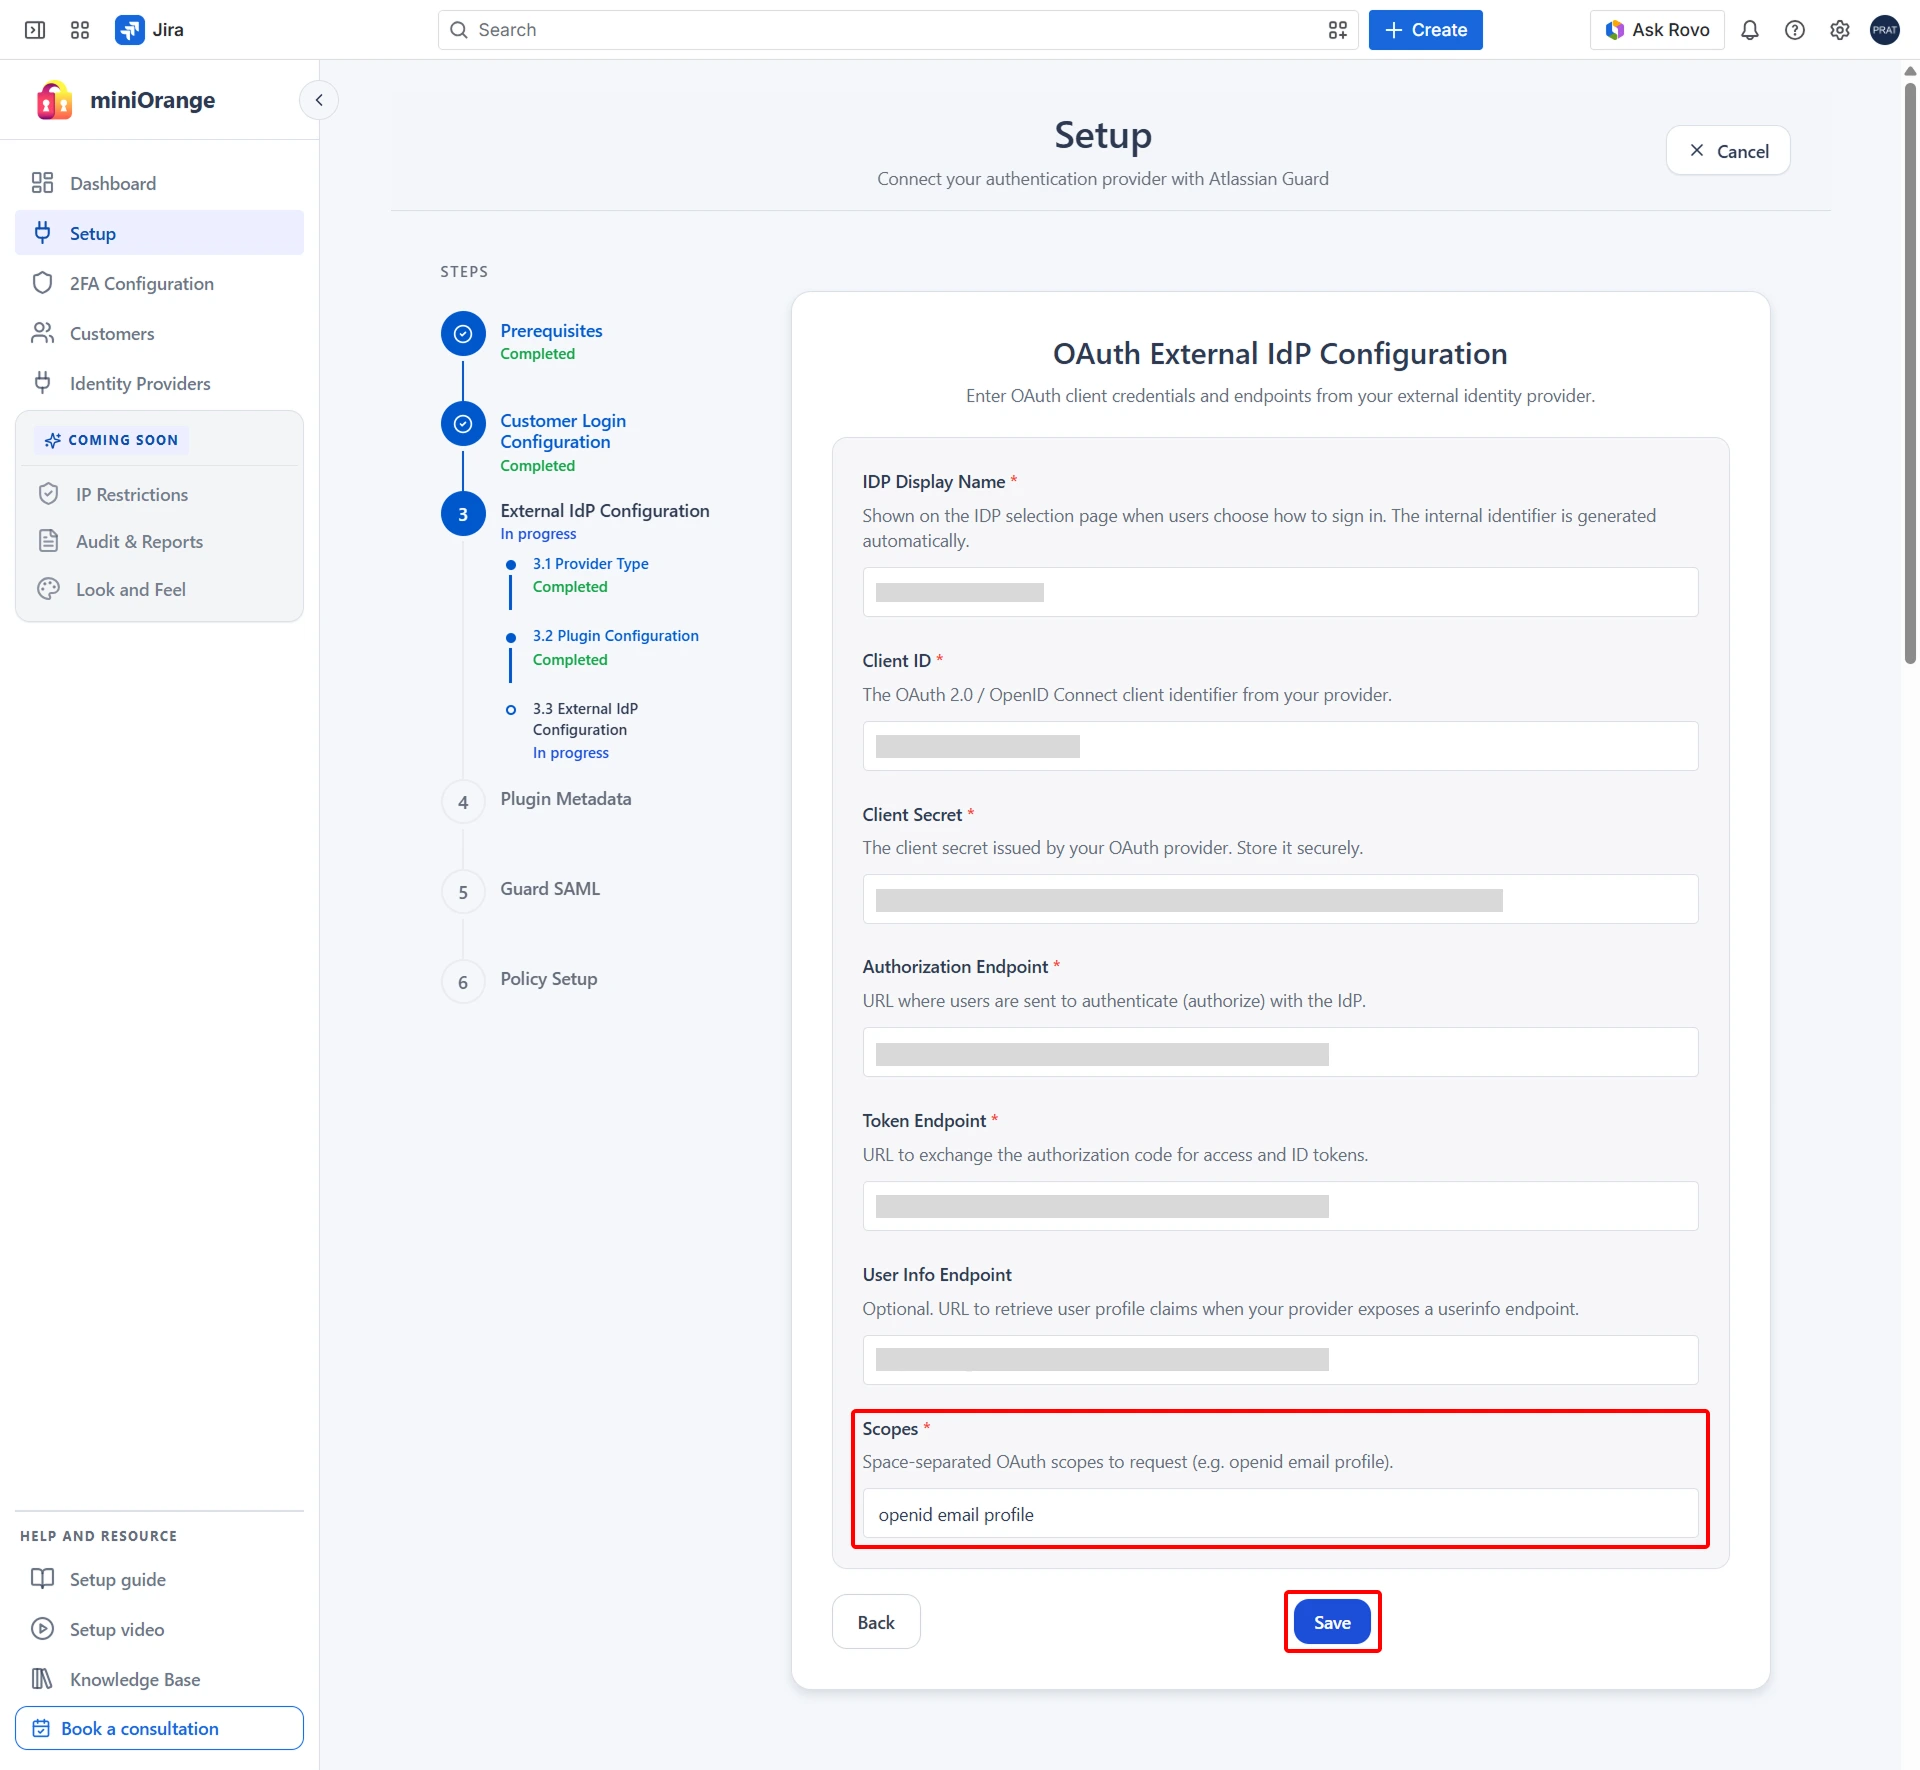
Configure the plugin using the OAuth/OIDC credentials generated by your Identity Provider. The following values are required:
- Idp Display Name
- Client ID
- Client Secret
- Authorization Endpoint
- Token Endpoint
- Scopes (enter at least one scope)
- Locate the required OAuth credentials (Client ID, Client Secret) and endpoints in your IdP dashboard.
- Paste the copied values into the corresponding fields in the OAuth External IdP Configuration step, enter at least one scope, then click Save. For OpenID Connect, include openid and email.
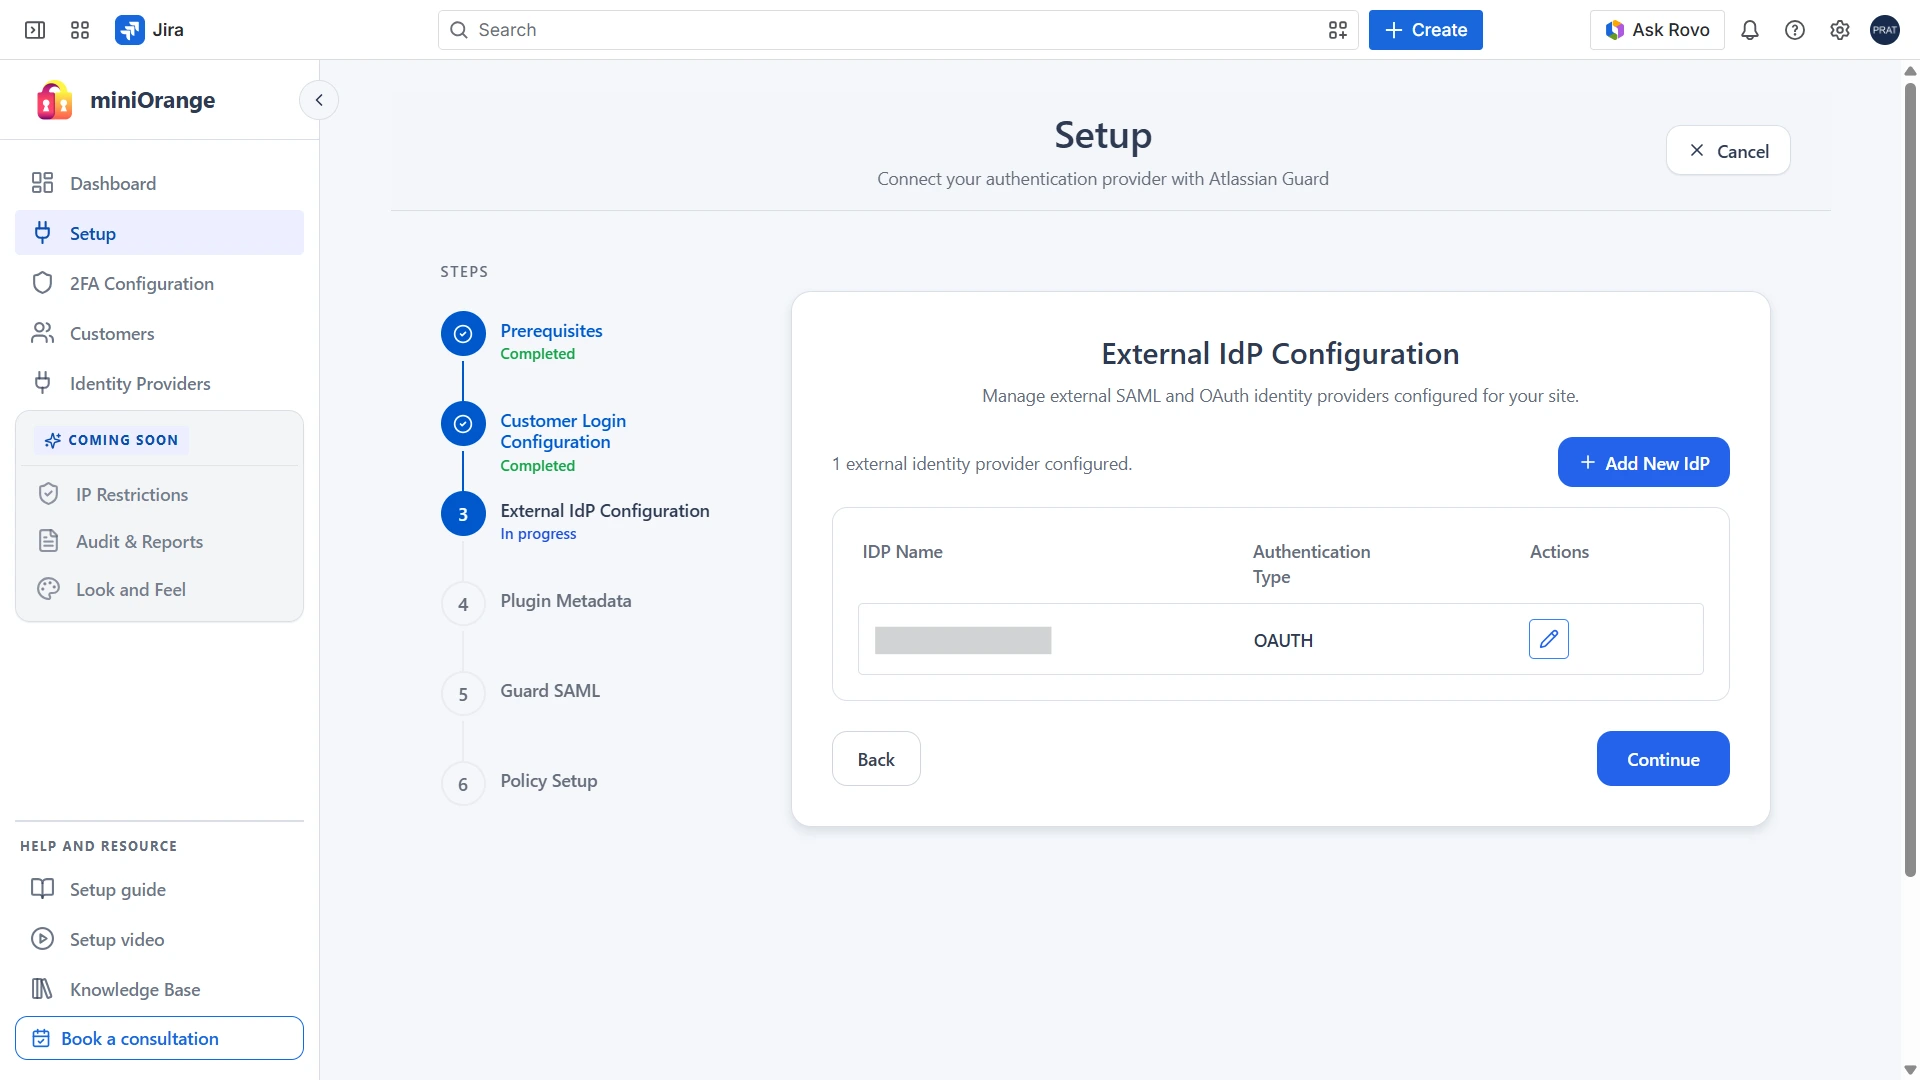
- After saving, the Identity Provider will be listed on the Configured IdPs page, where you can edit it or add more Identity Providers.
iii. Test the OAuth Connection
After saving the configuration, the Identity Provider will be listed on the configured IdPs page. From this page, you can:
- Edit the IdP configuration
- Add additional Identity Providers
3B. If You Do Not Use an External Identity Provider (miniOrange IdP)
If you selected No. Configure the authentication source for managed and external users directly in Atlassian Guard using SAML SSO.
4. Configure the Authentication Source in Atlassian Guard
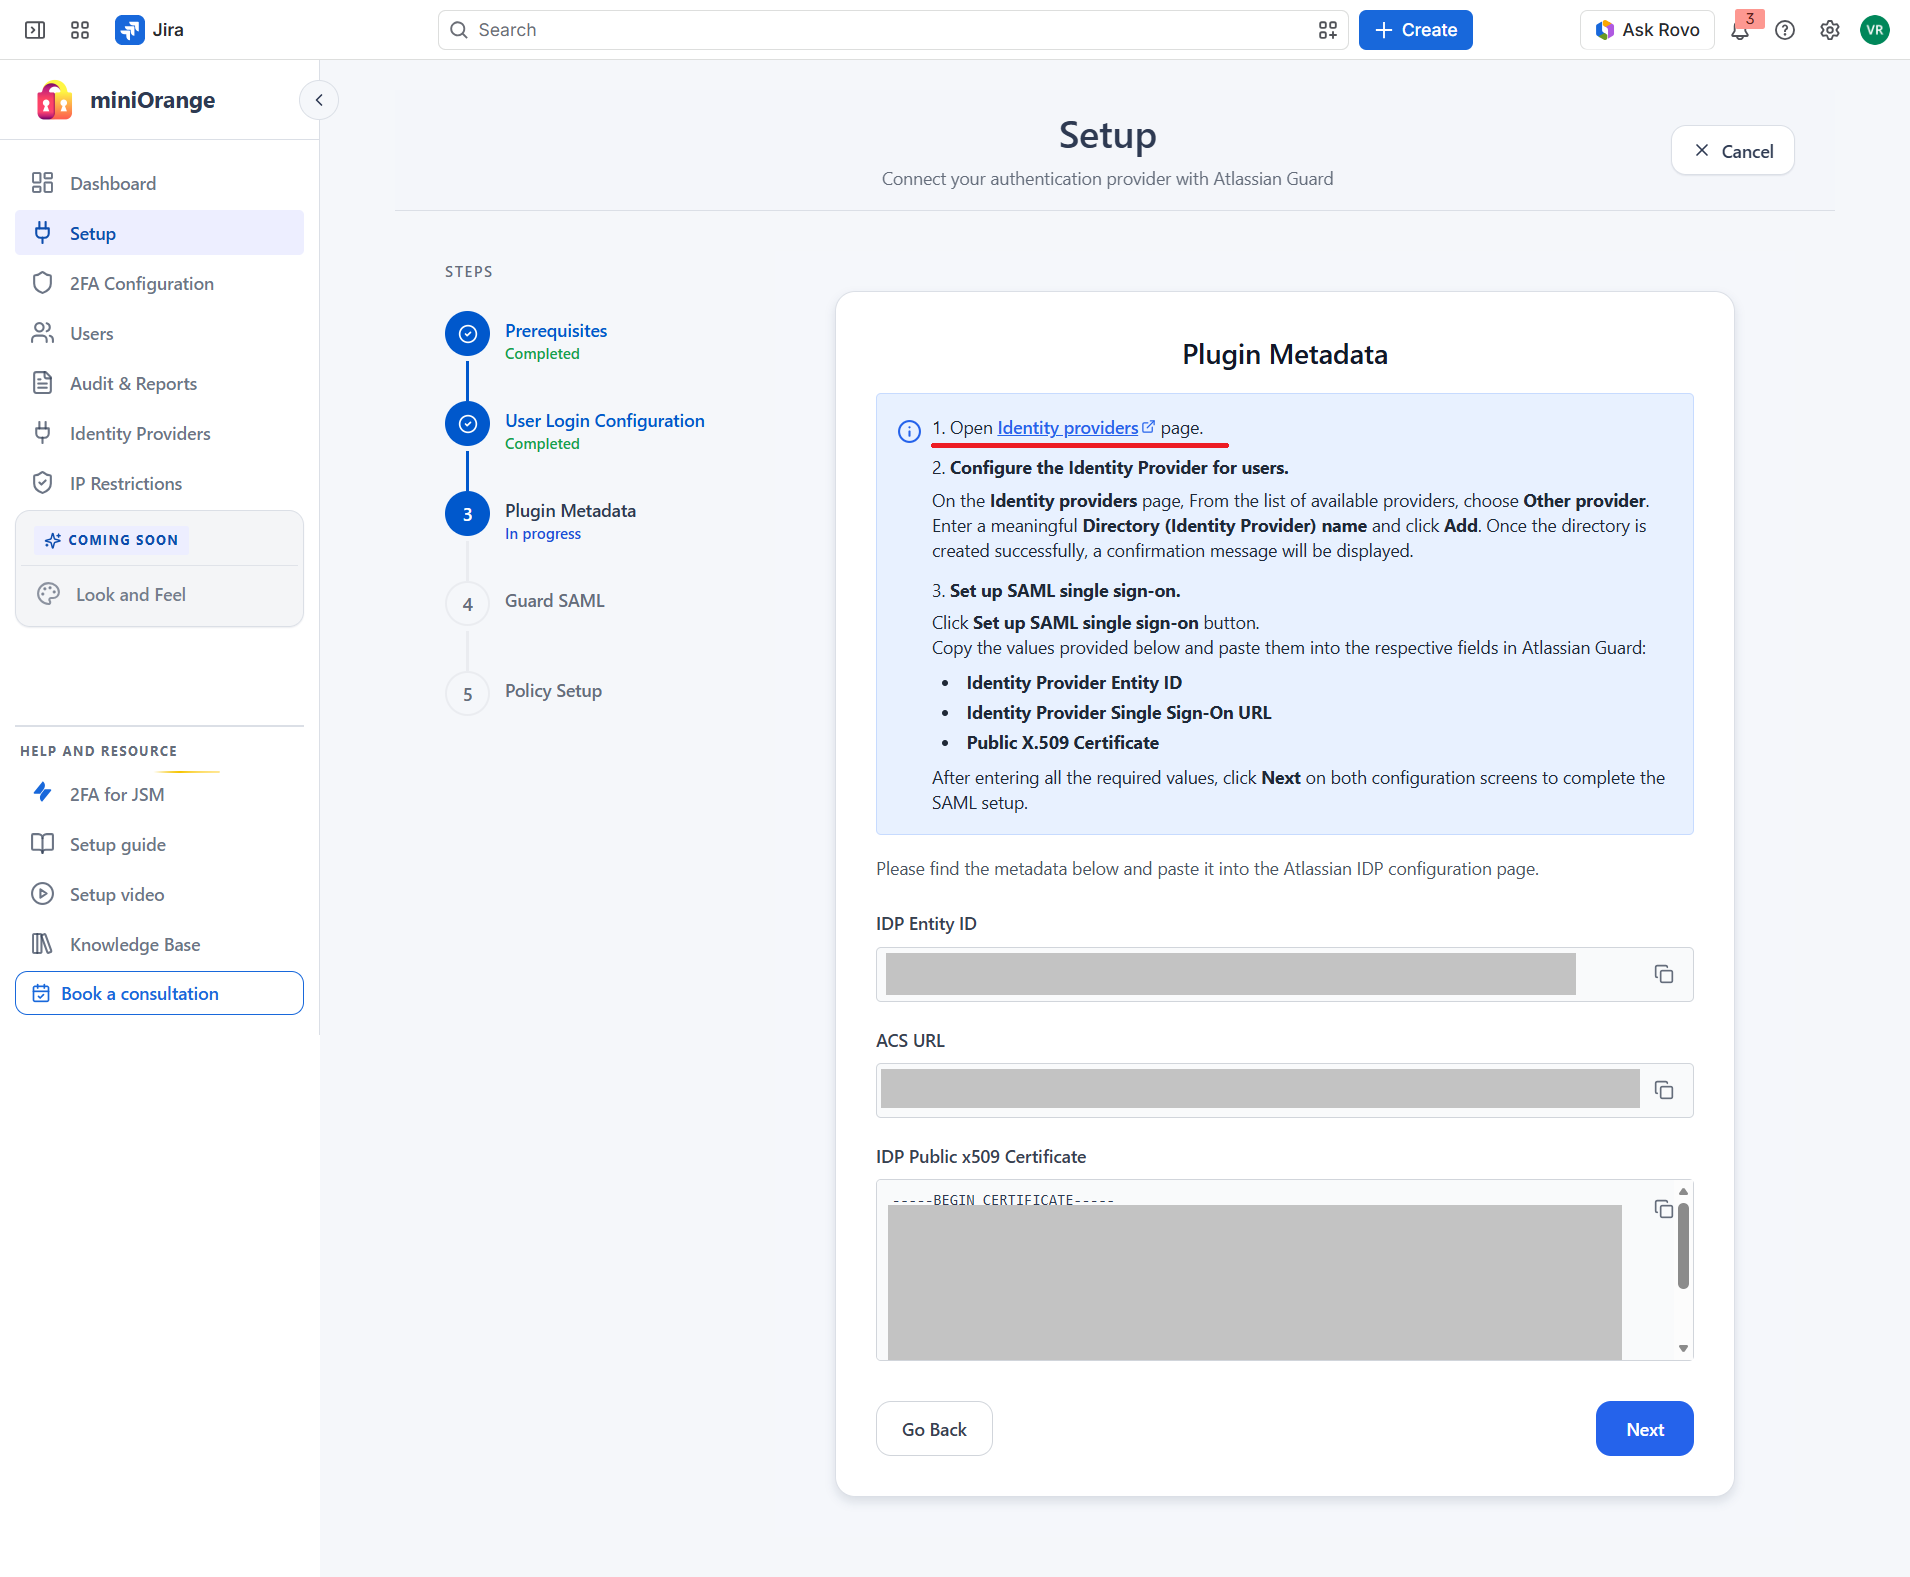
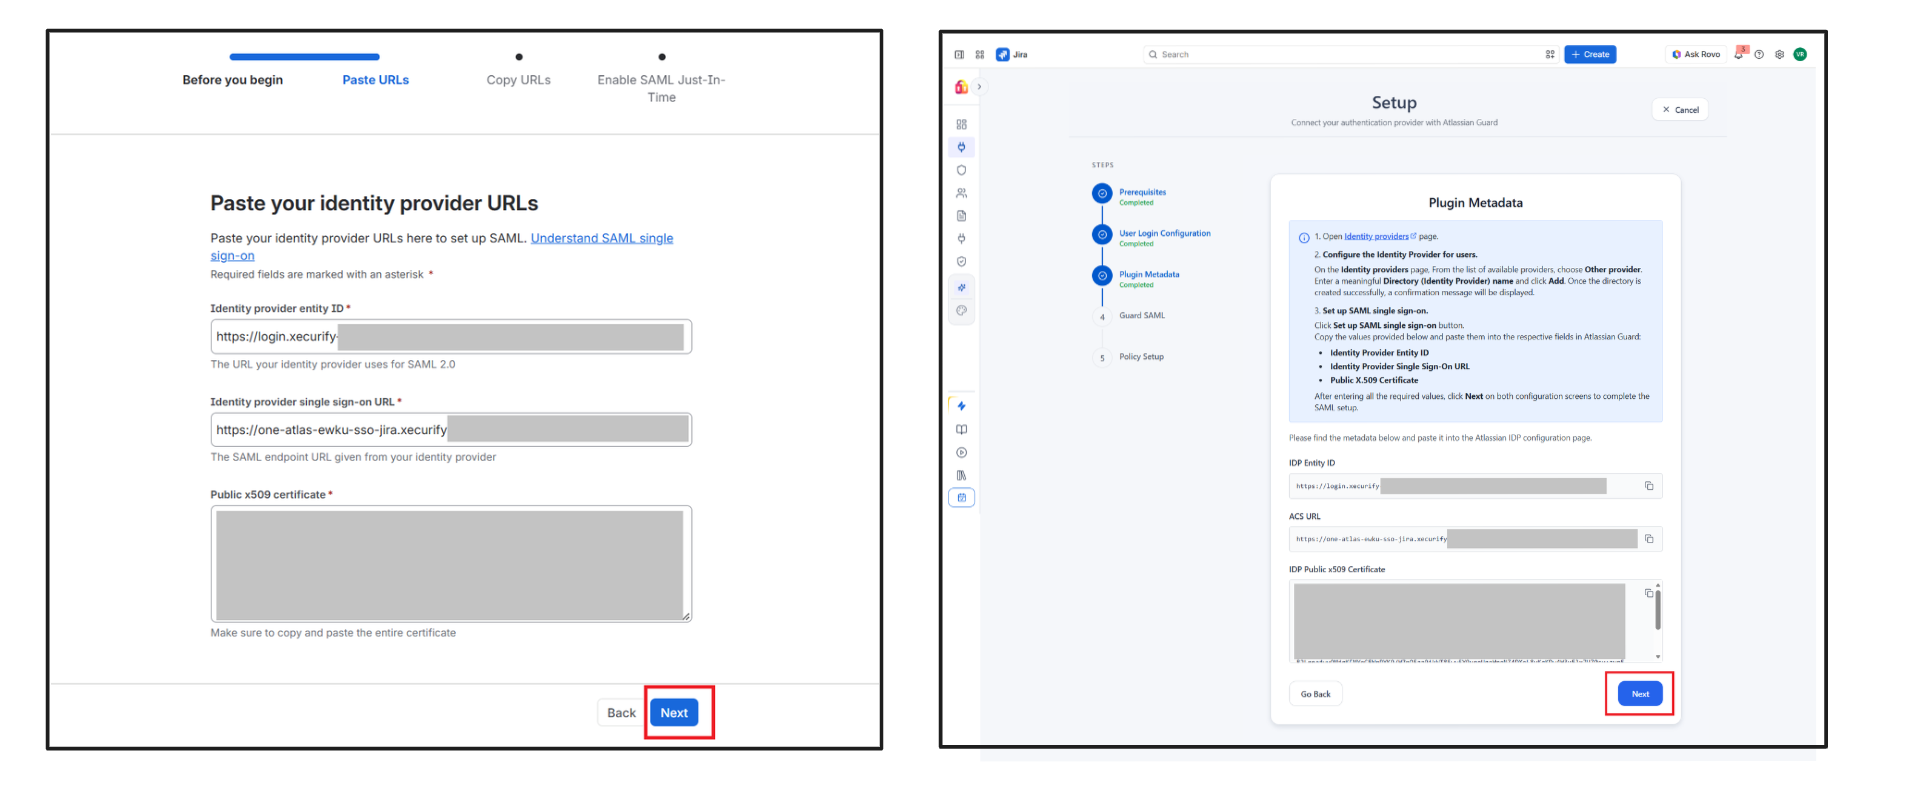
In the app’s Setup tab, the Plugin Metadata step shows the SAML values you need to enter in Atlassian Guard.
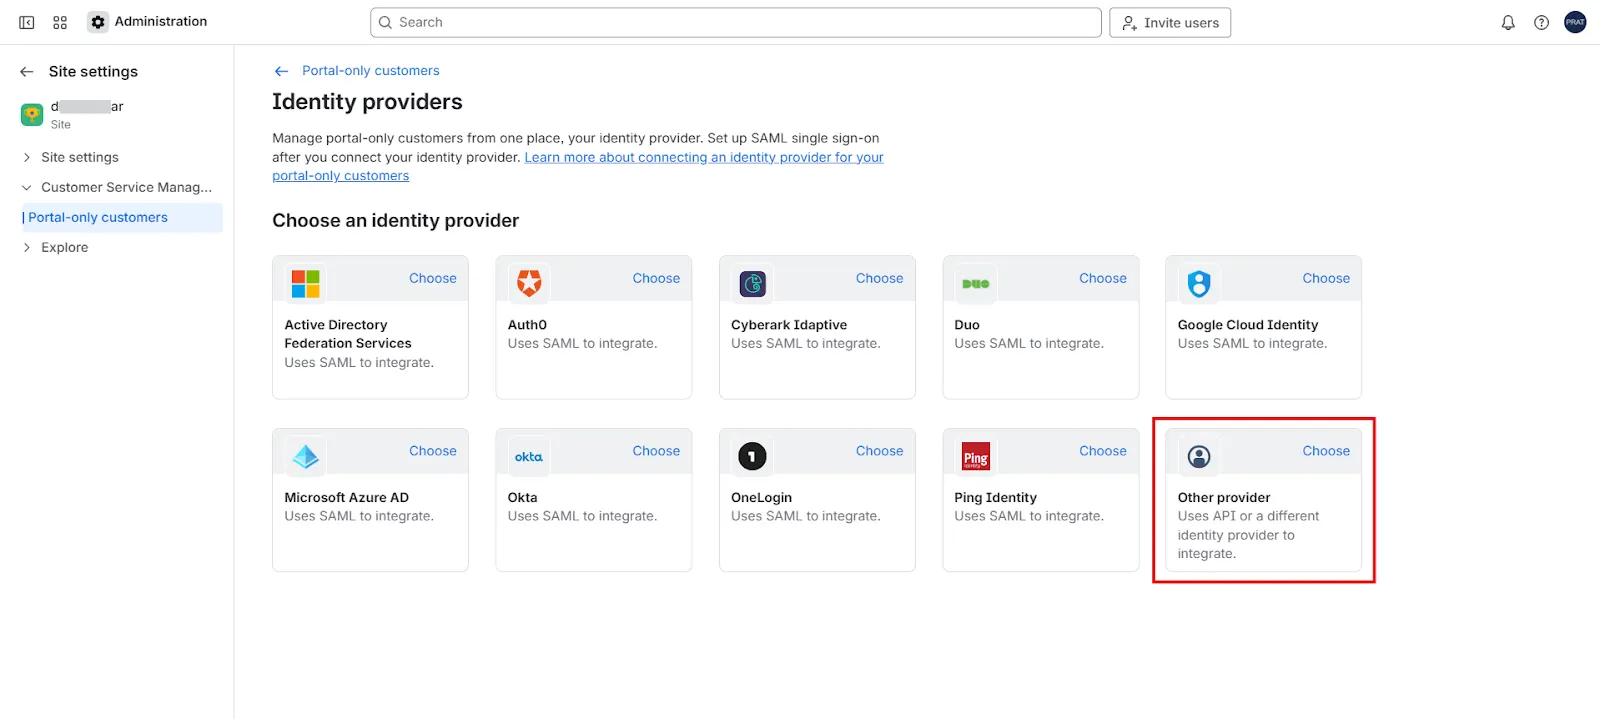
- Click the Identity providers link on the Plugin Metadata step. The Atlassian Guard Identity providers page opens.
- On the Identity providers page, choose Other provider from the list of available providers.
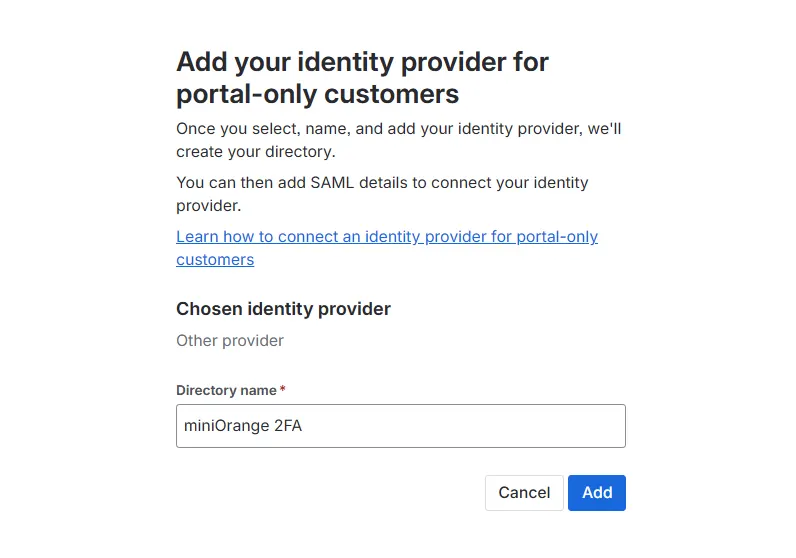
- Enter a meaningful Directory name (identity provider name) and click Add.
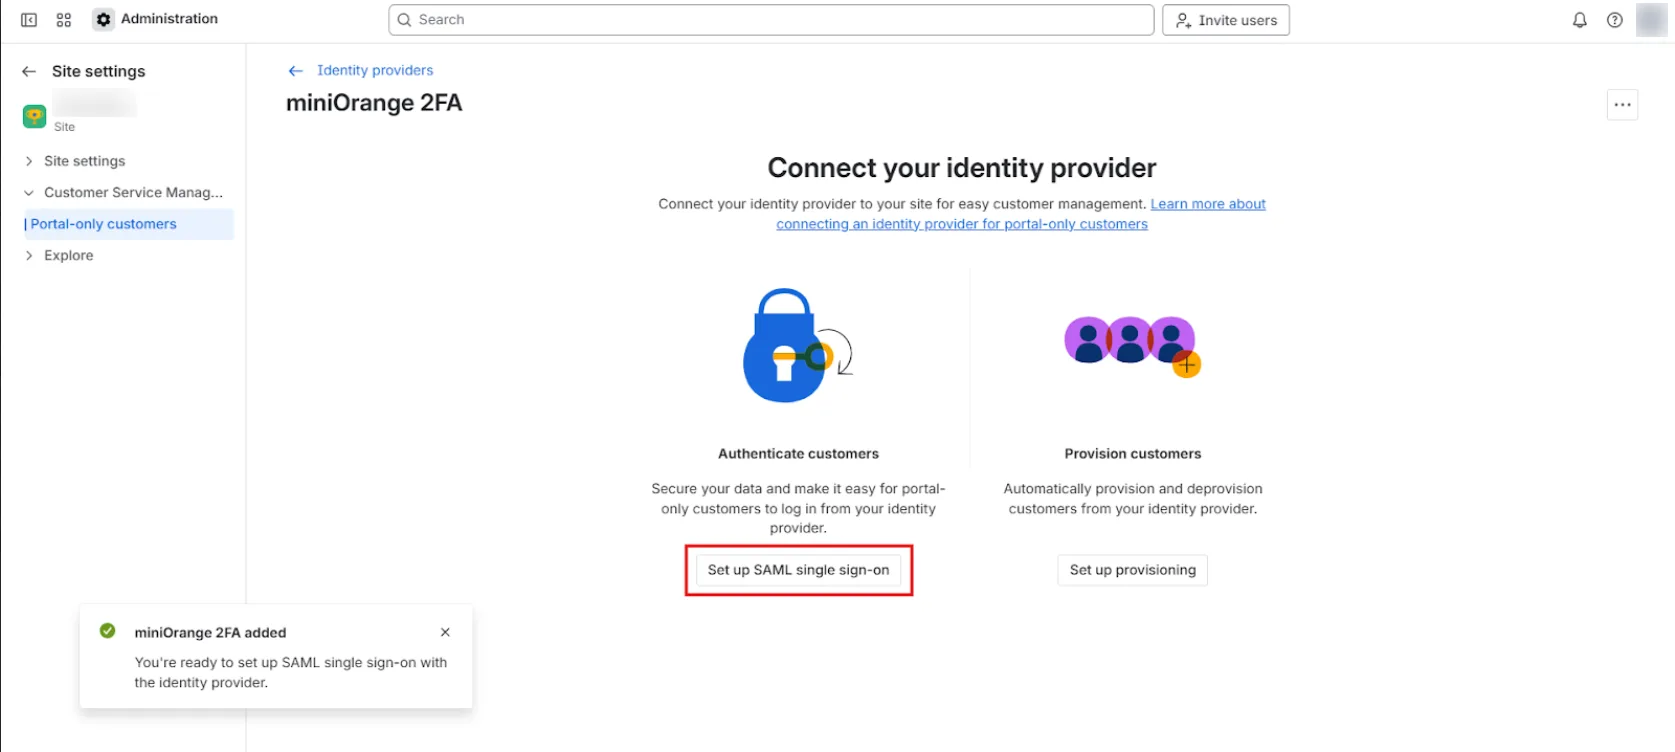
- Click Set up SAML single sign-on.
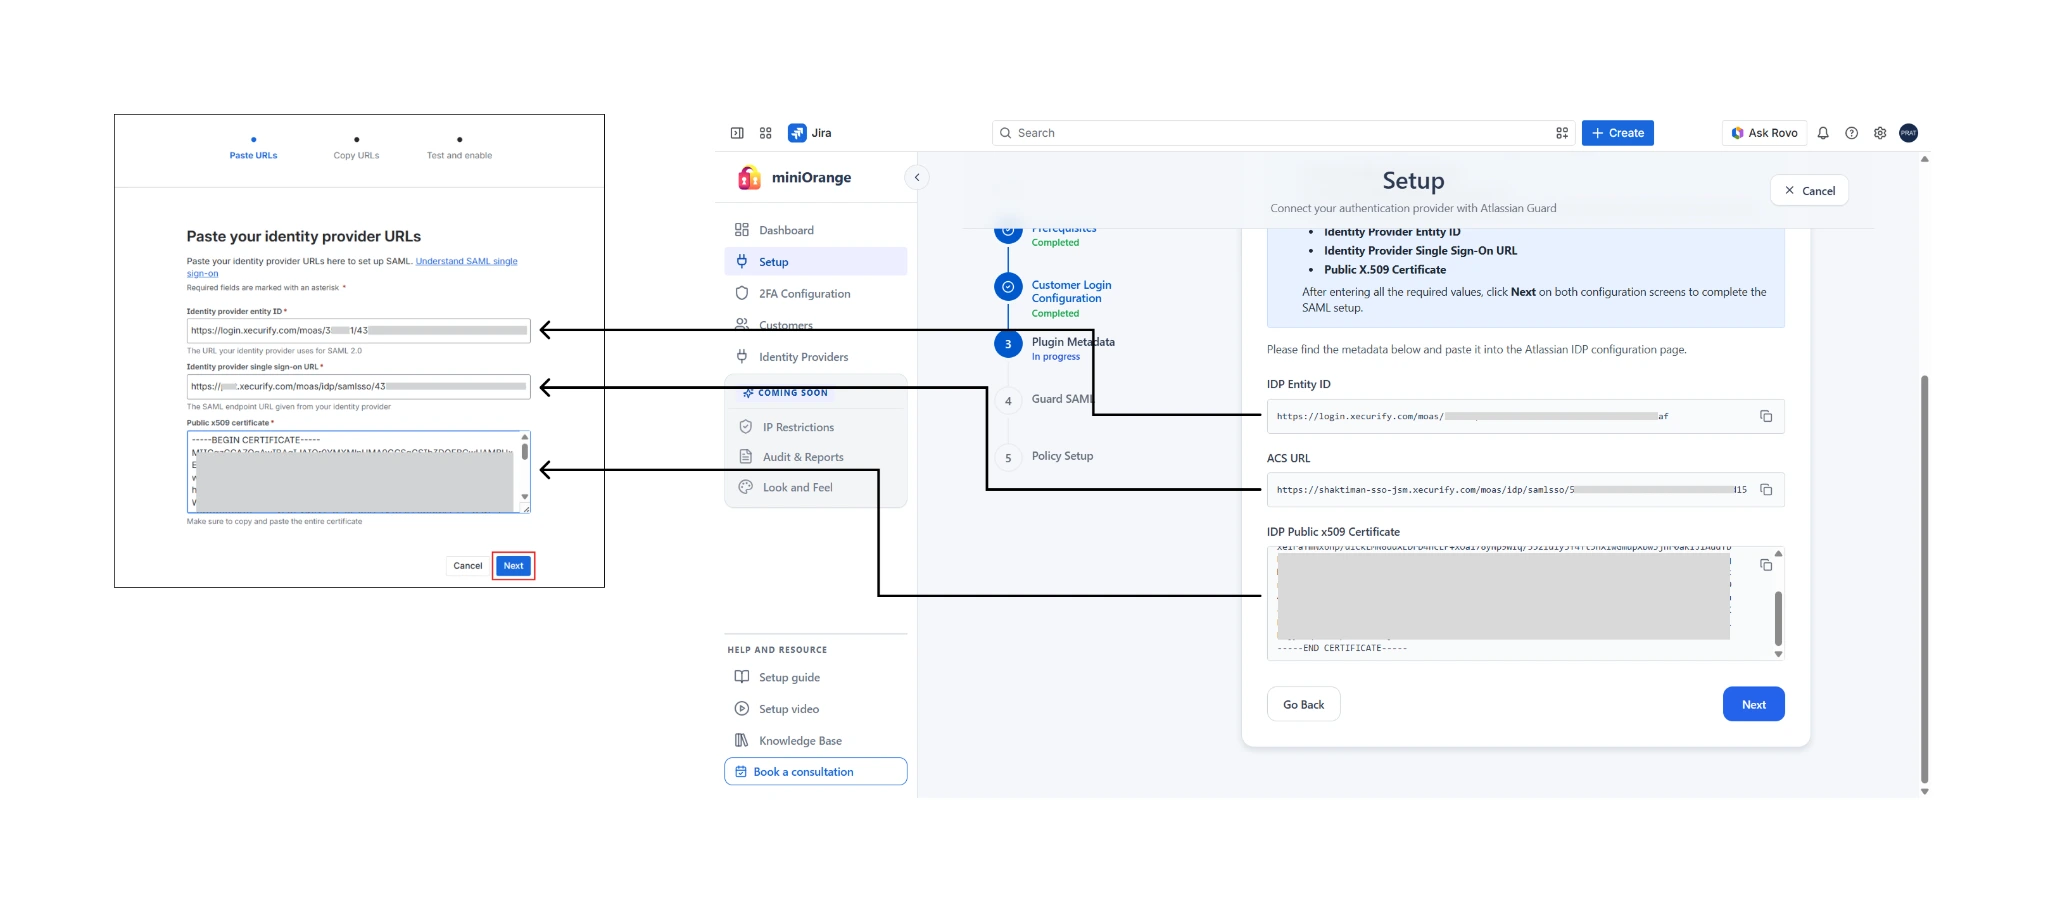
- Copy the following values from the app’s Plugin Metadata step and paste them into the matching fields in Atlassian Guard:
- Identity Provider Entity ID
- Identity Provider Single Sign-On URL
- Public X.509 Certificate
- After you paste the values, click Next on the Atlassian Guard screen. Then return to the app and click Next on the Plugin Metadata screen.
5. Configure Atlassian Guard SAML
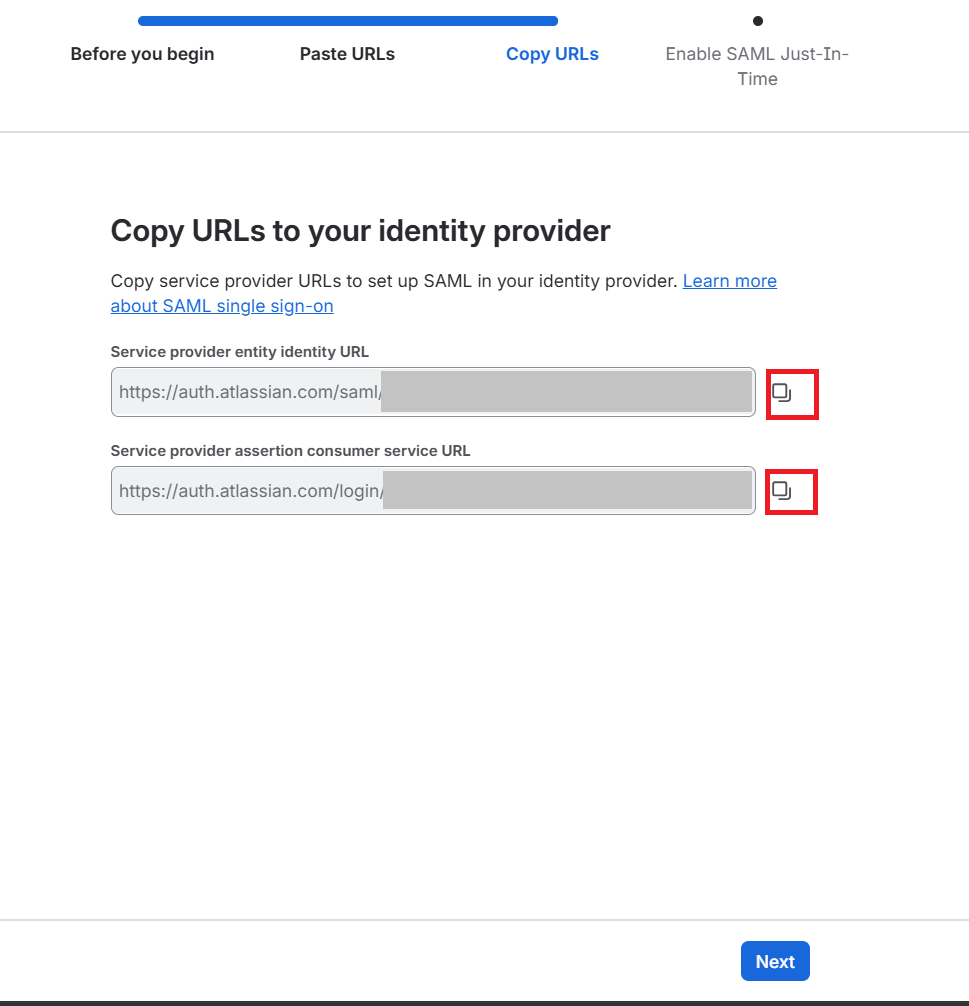
After the SAML setup in Atlassian Guard is complete, Guard generates its own SAML details. Enter them in the app’s Configure Atlassian Guard SAML step.
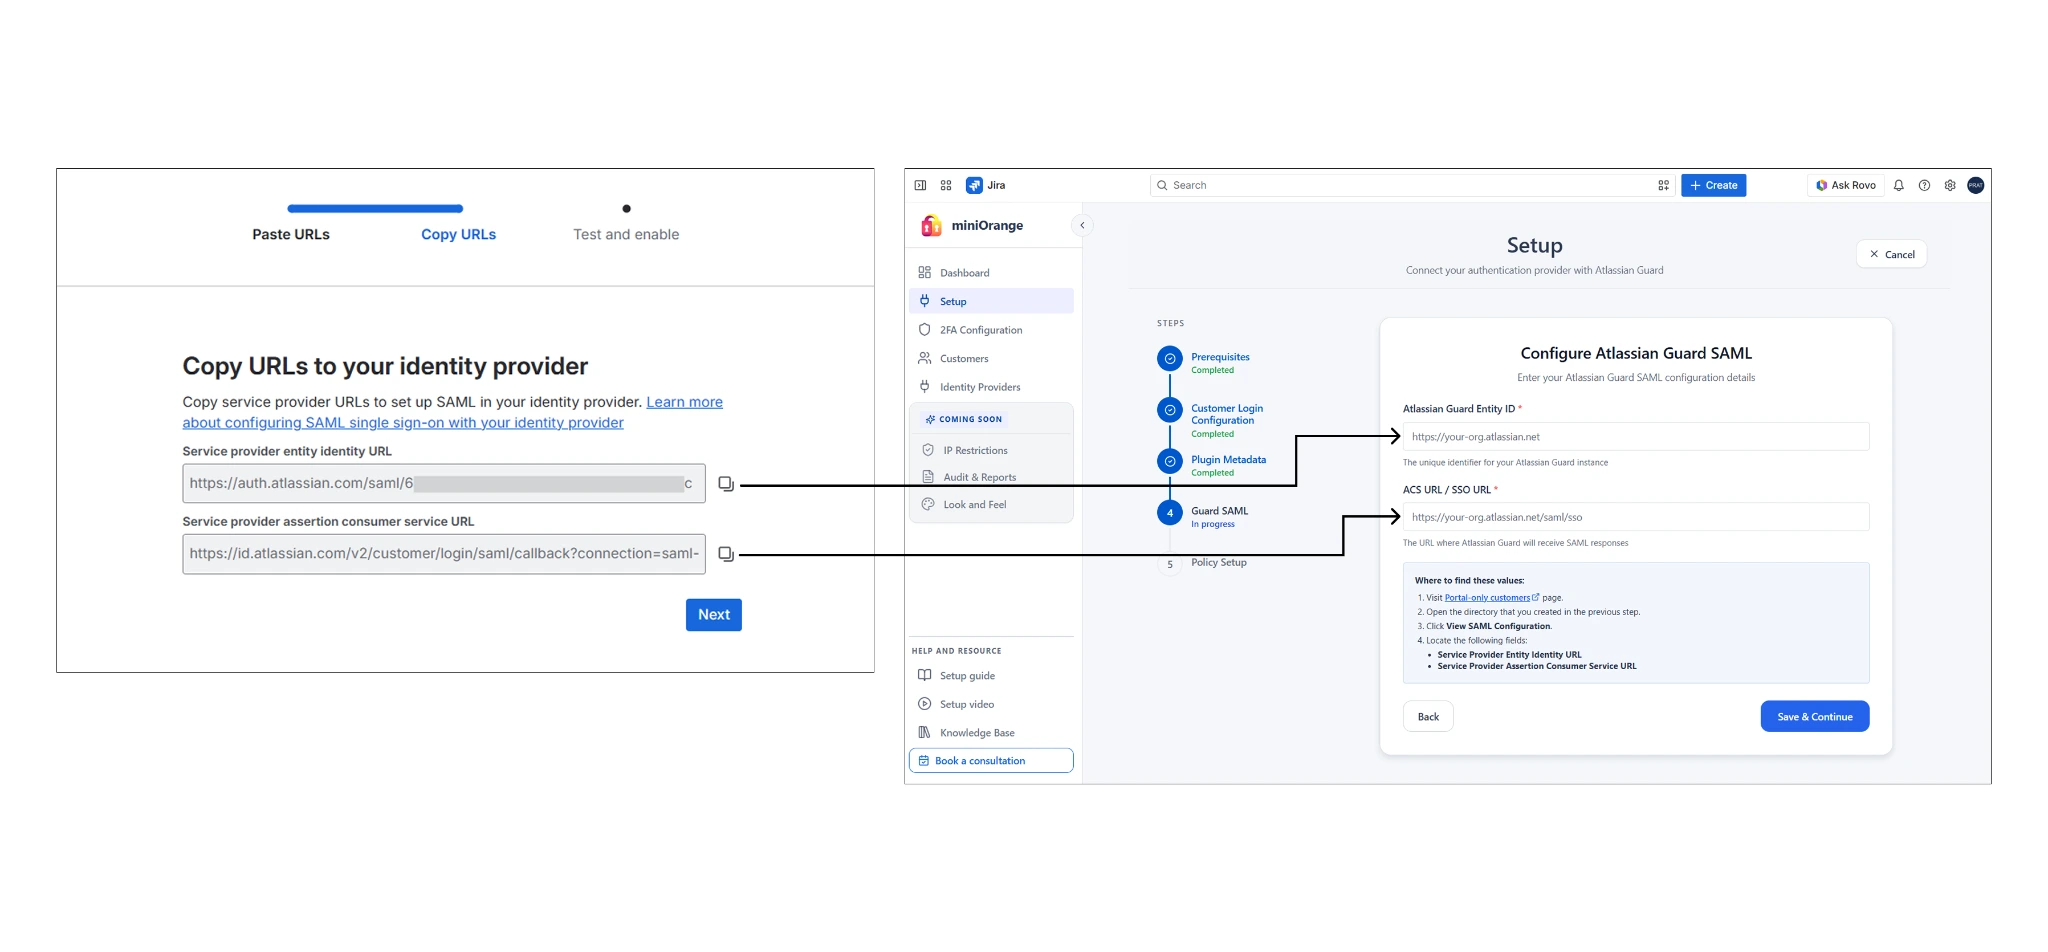
- On the Atlassian Guard page, find the Service Provider Entity Identity URL and the Service Provider Assertion Consumer Service URL, and copy them.
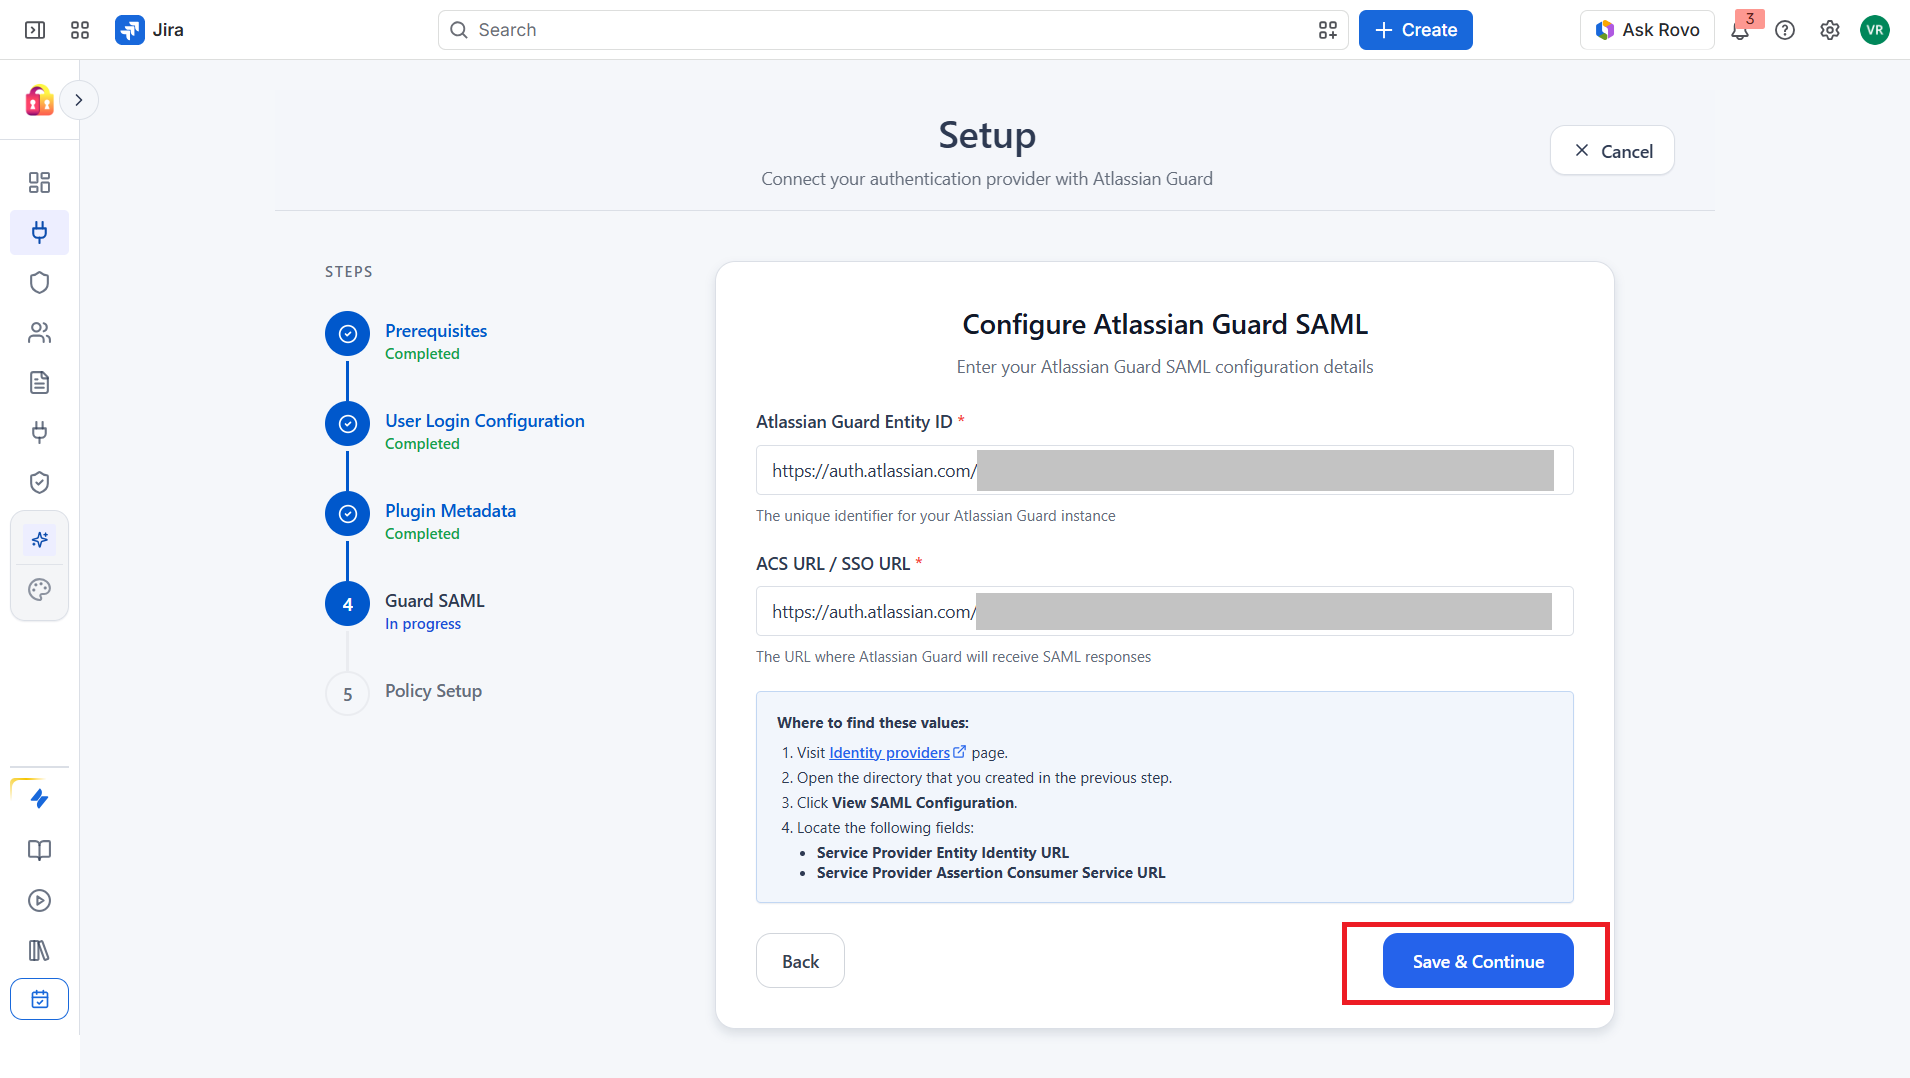
- Return to the app and paste them into the matching fields:
- Service Provider Entity Identity URL → Atlassian Guard Entity ID
- Service Provider Assertion Consumer Service URL → ACS URL / SSO URL
- On the Atlassian Guard page, click Next and Save.
- Return to the app and Click Save & Continue.
6. Configure the Authentication Policy
After the Guard SAML setup, the Policy Setup step enforces single sign-on for the users you want to protect with 2FA. The page has two sections, one for internal (managed) users and one for external users. Complete the section that matches the users you want to protect, or both if you want to cover both types.
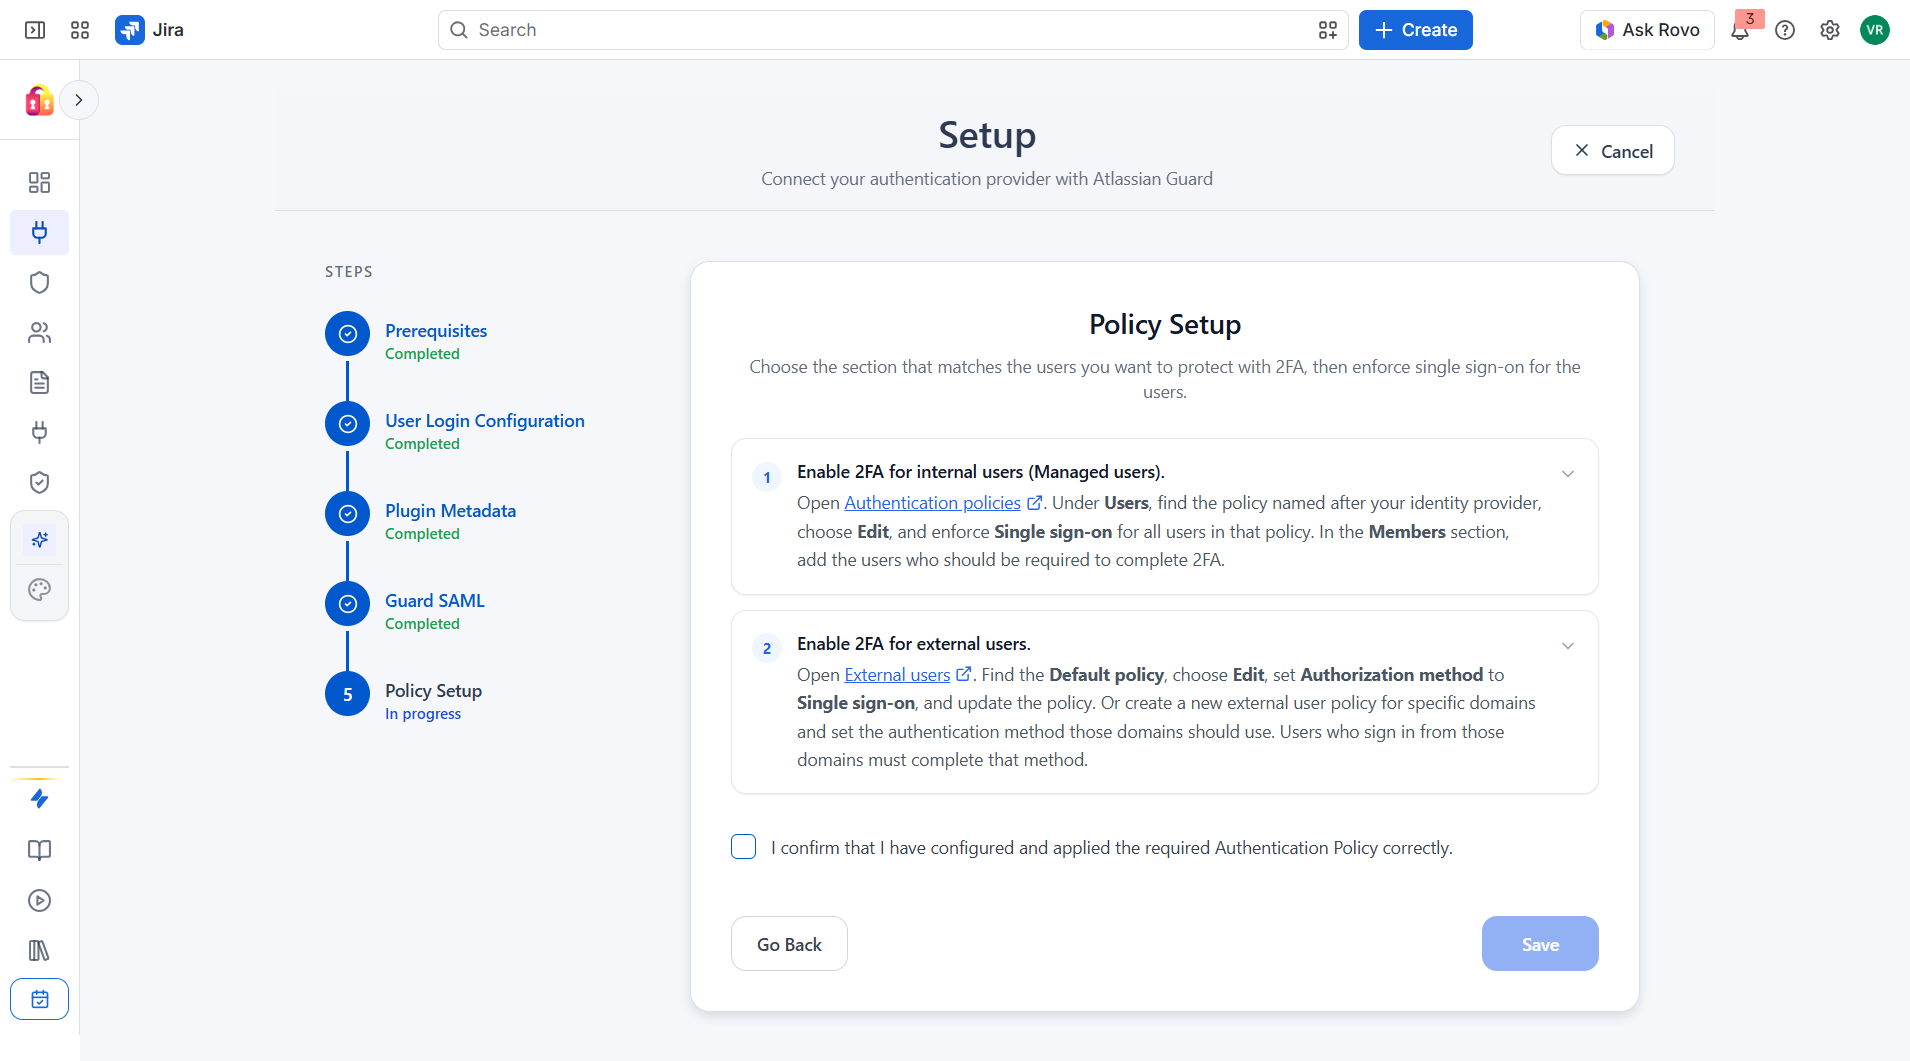
6A. Enable 2FA for Internal Users (Managed Users)
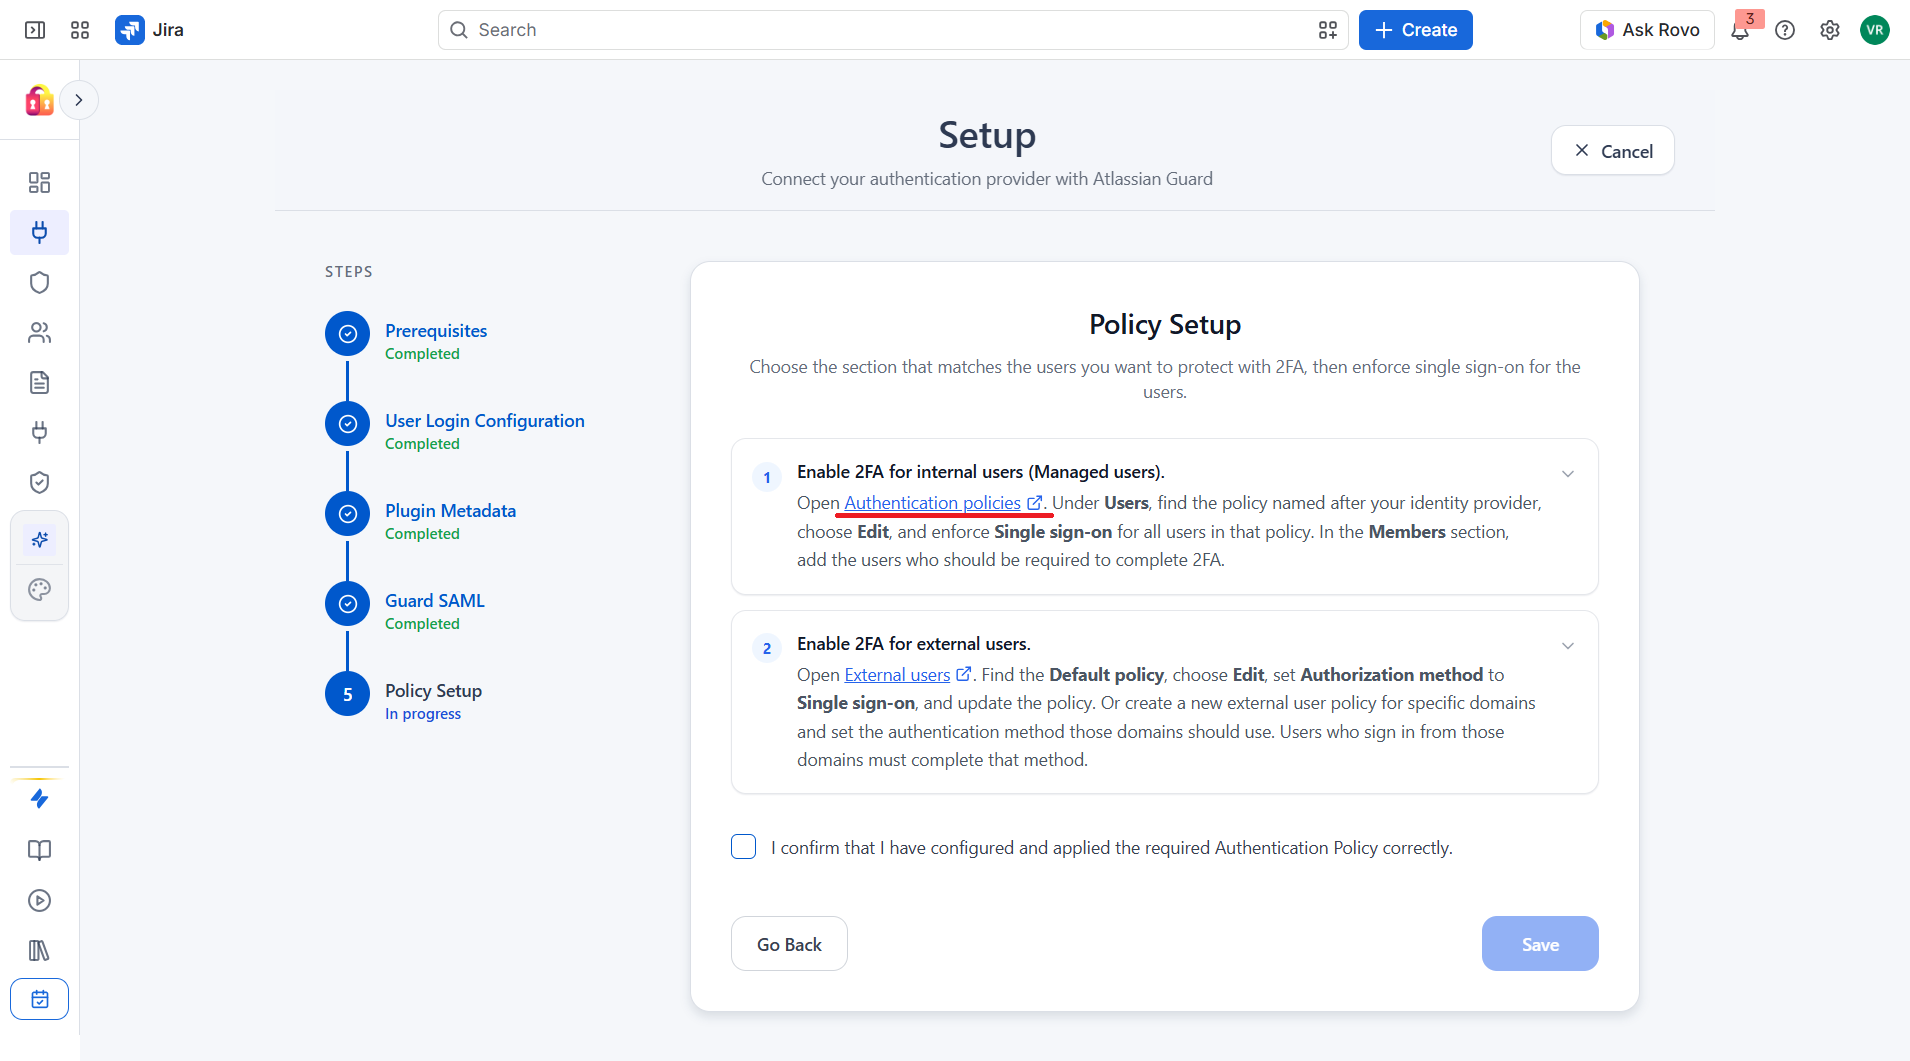
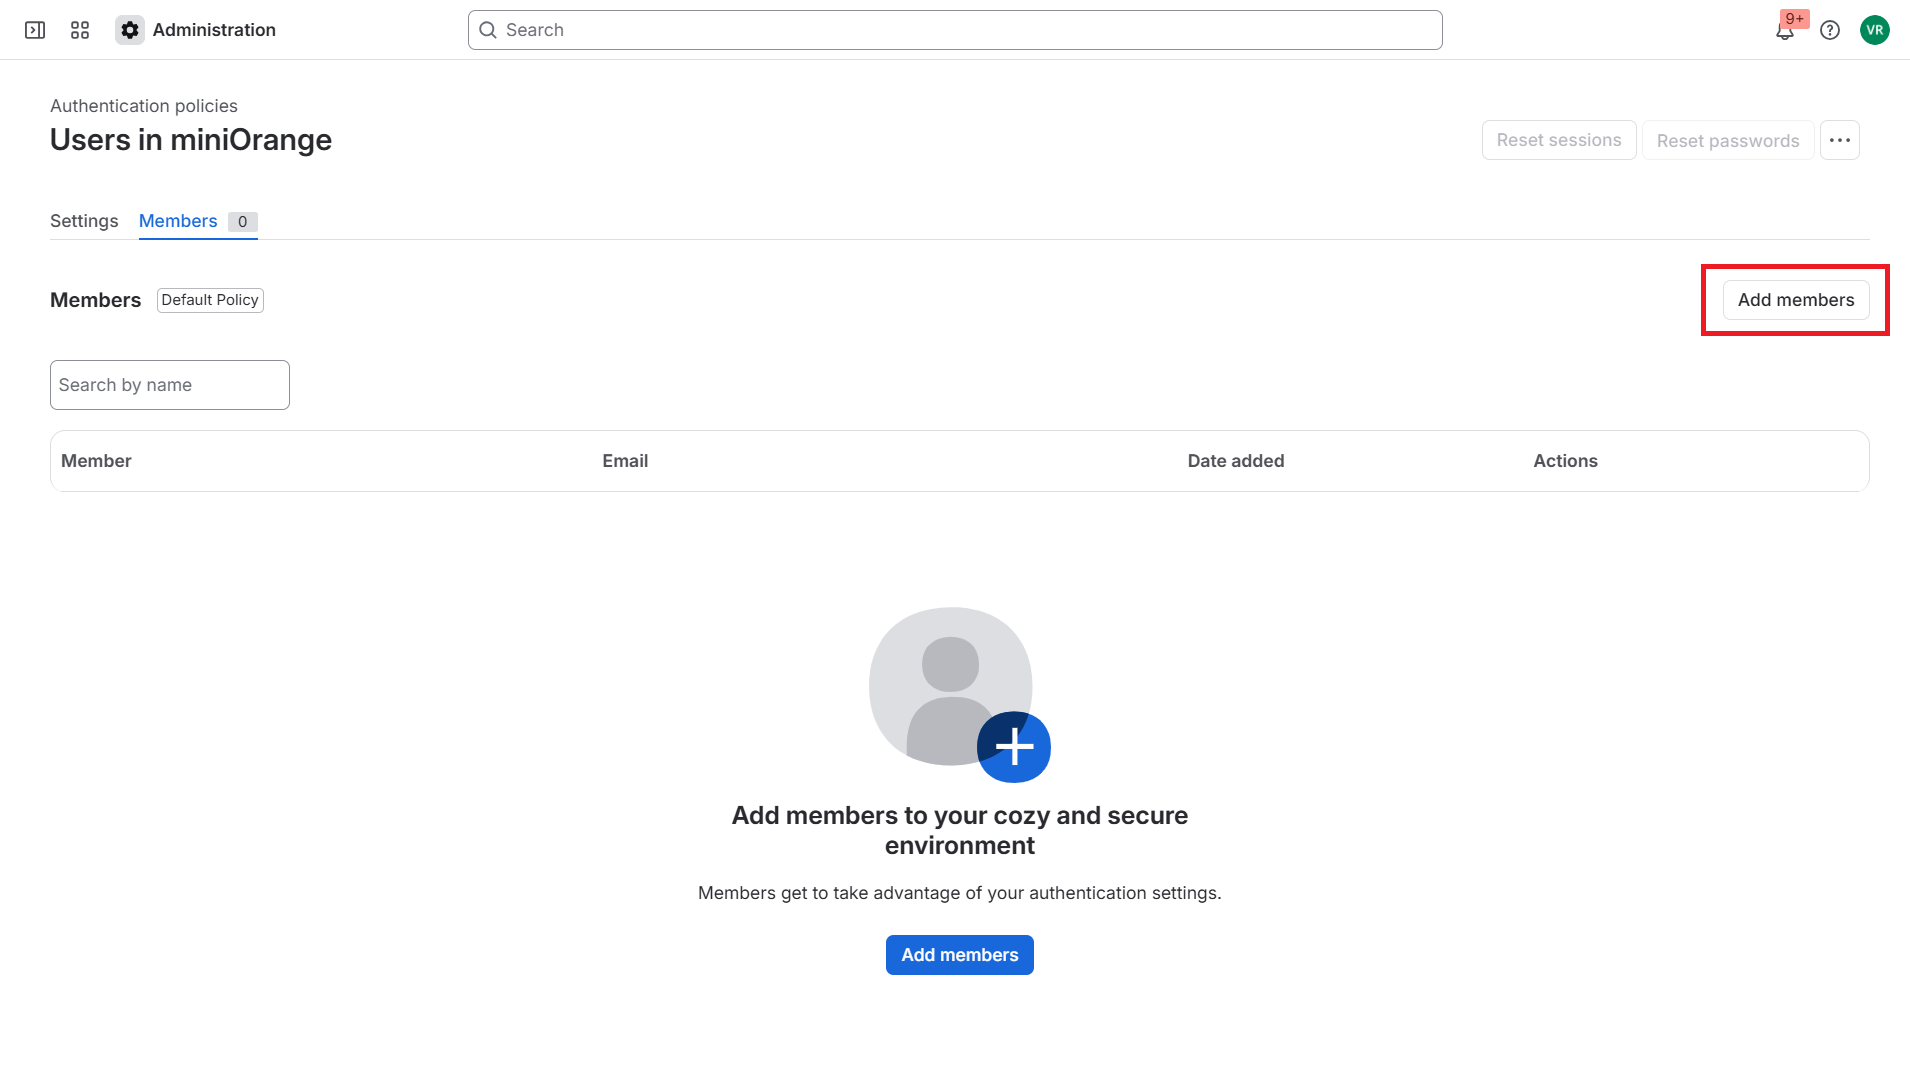
- In the Policy Setup step, open the Authentication policies link. The Authentication policies page opens in Atlassian Admin.
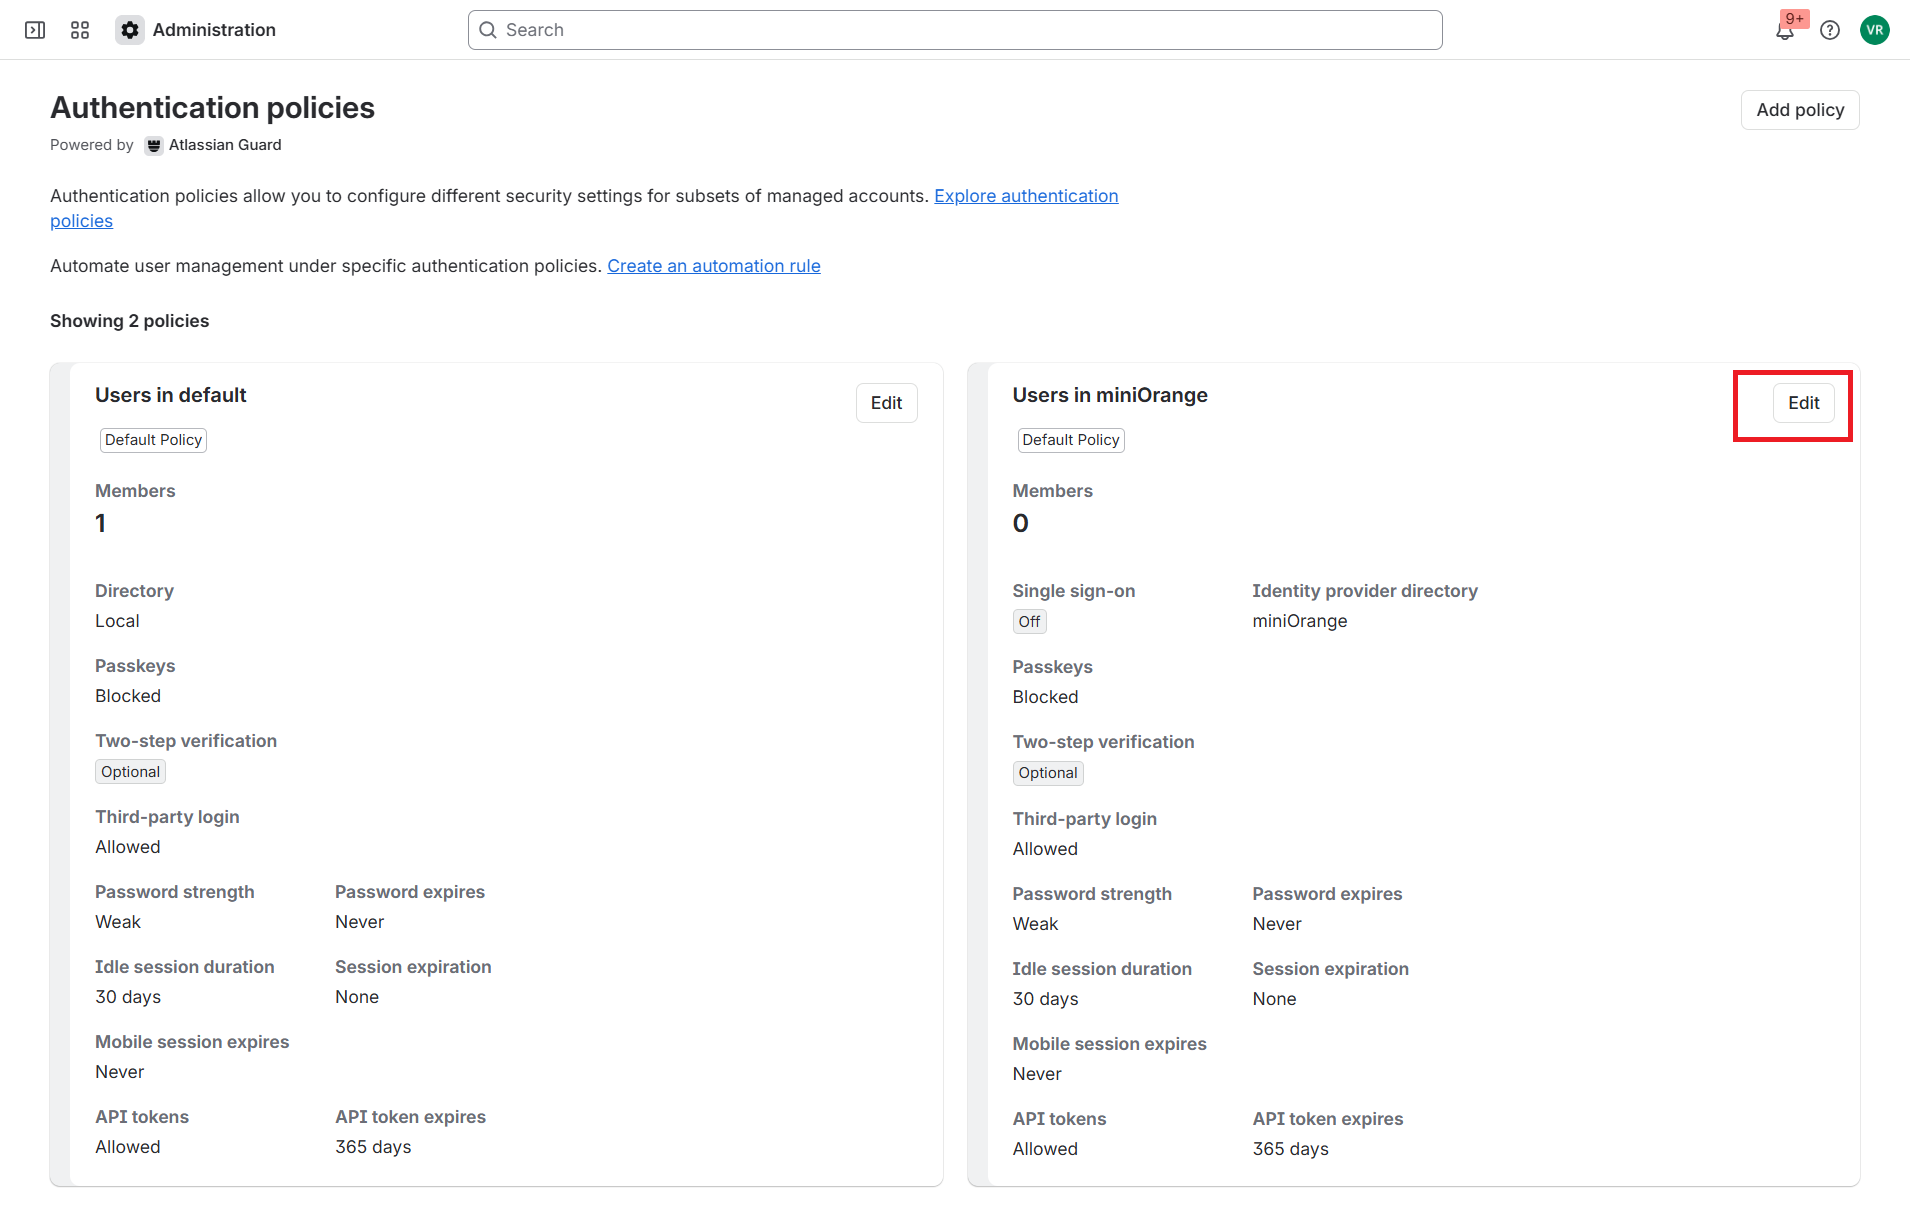
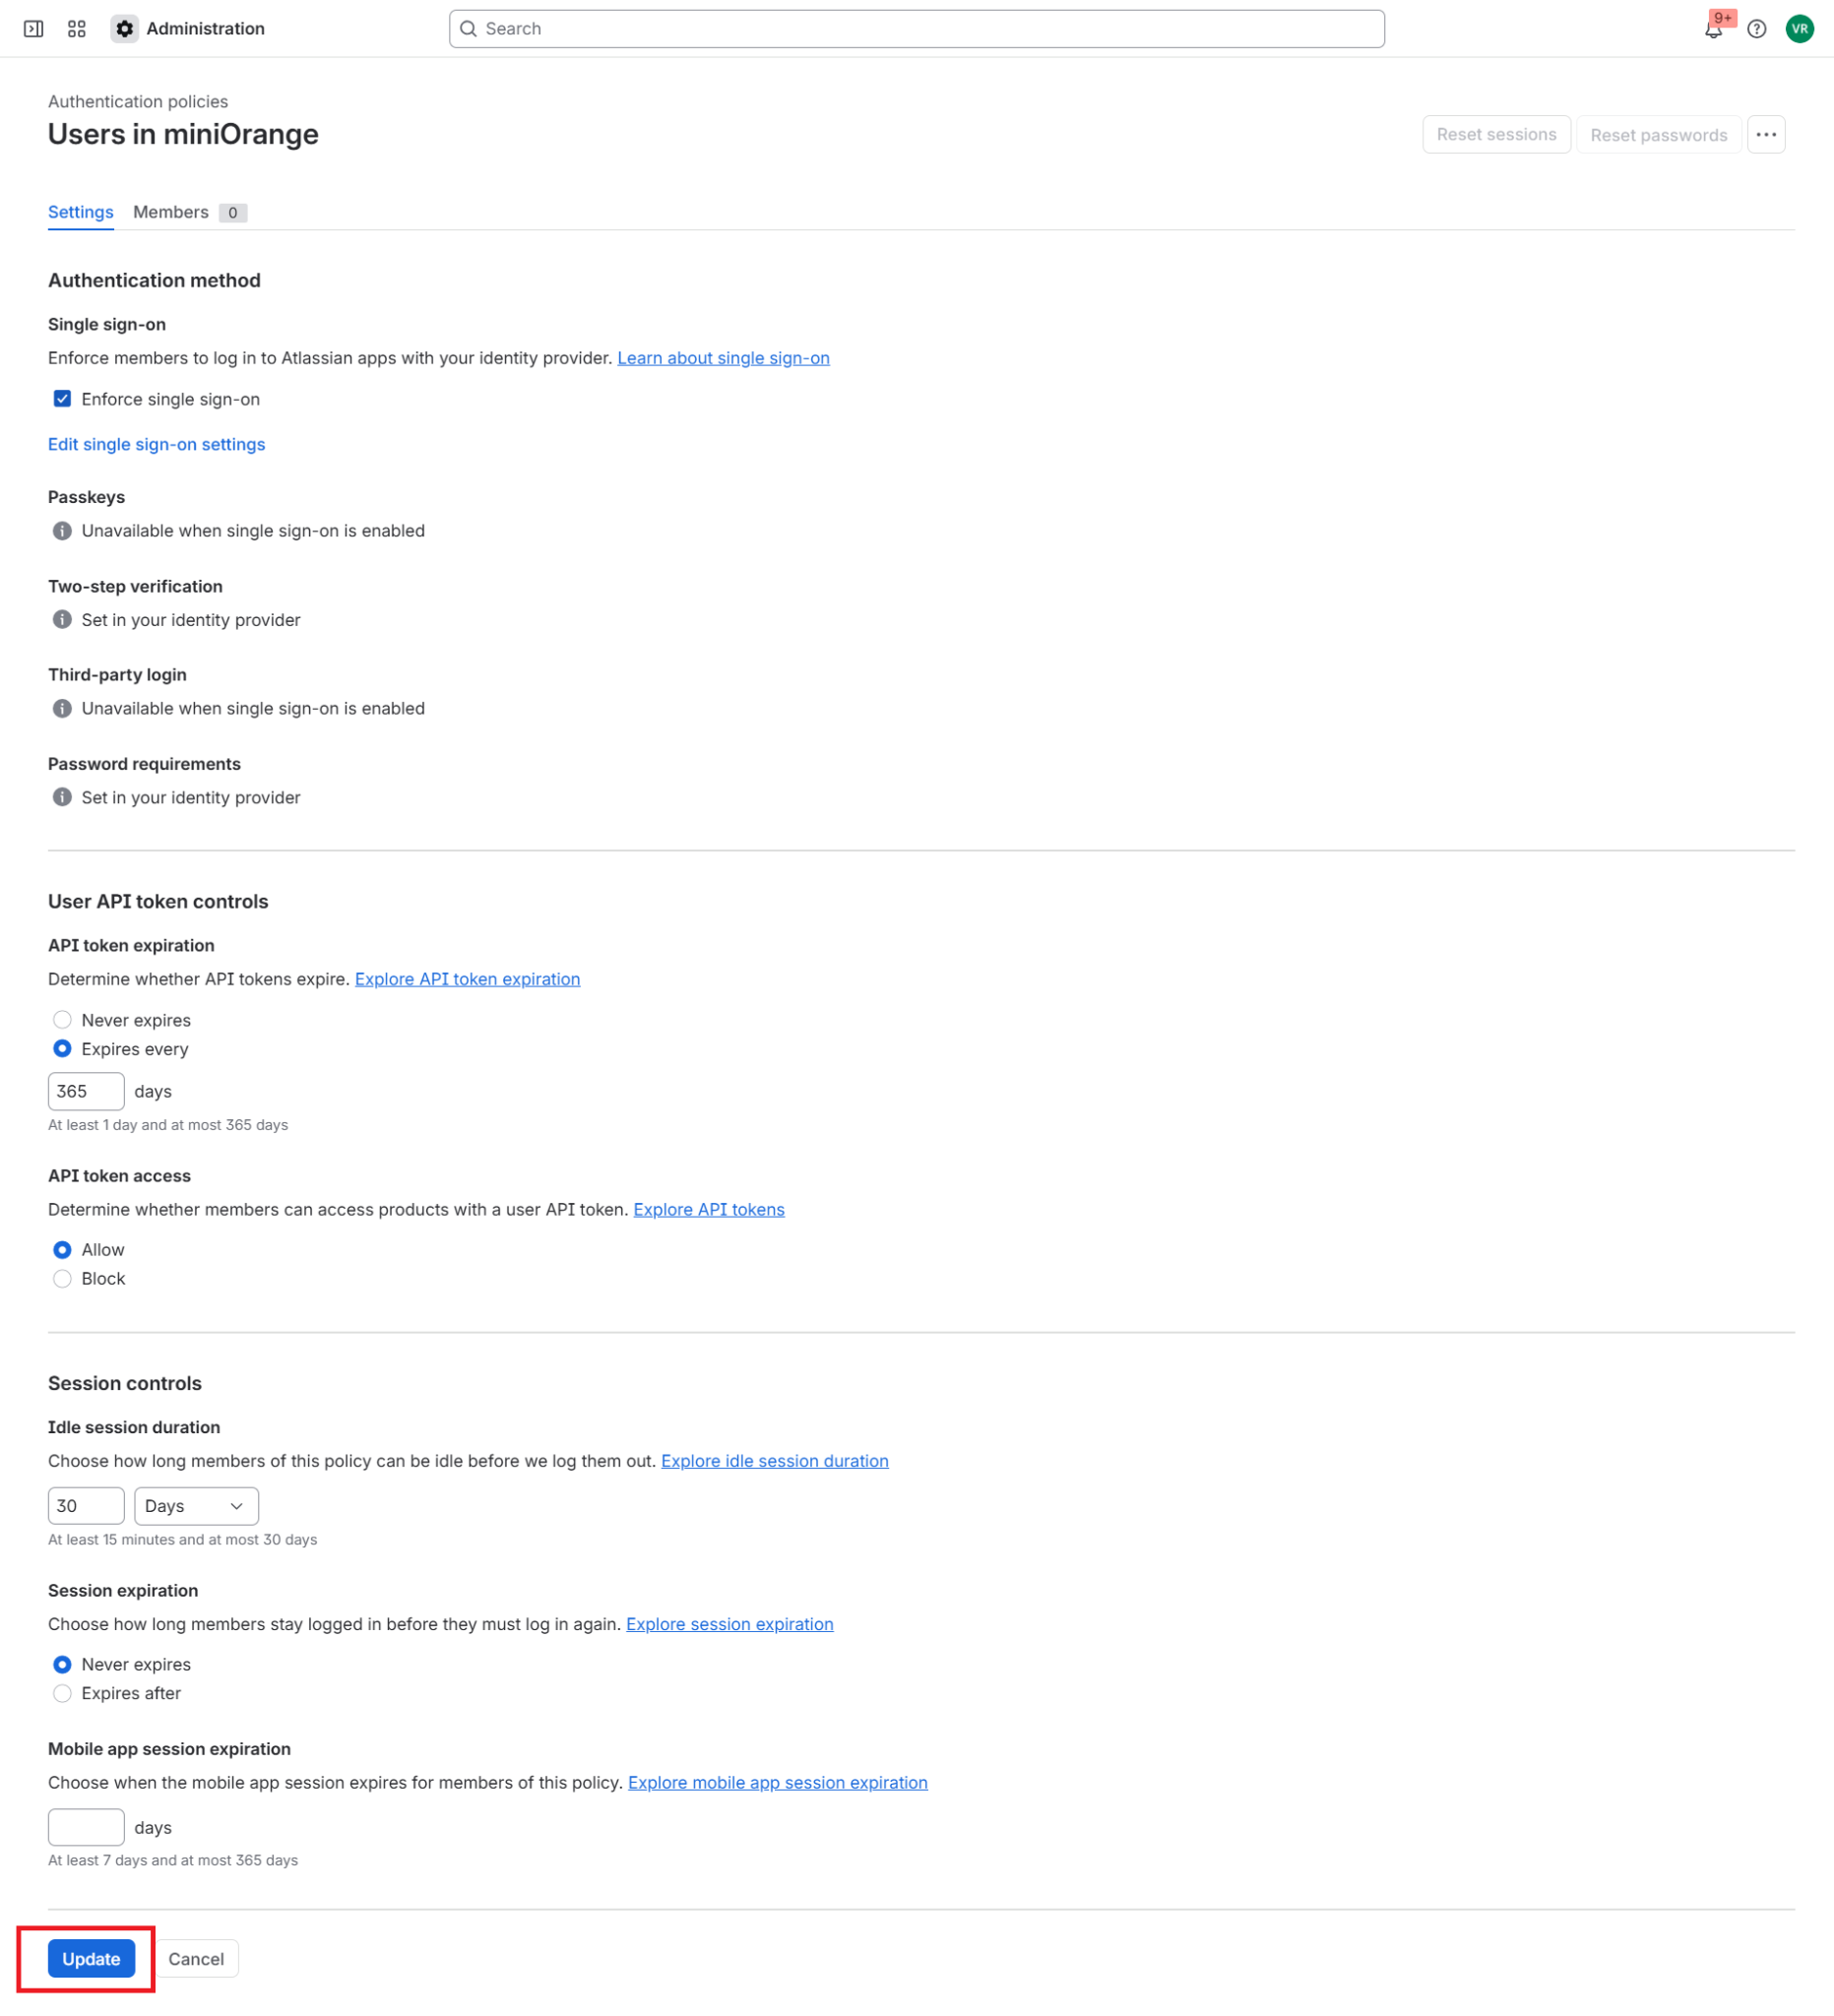
- Under Users, find the policy named after your identity provider and click Edit.
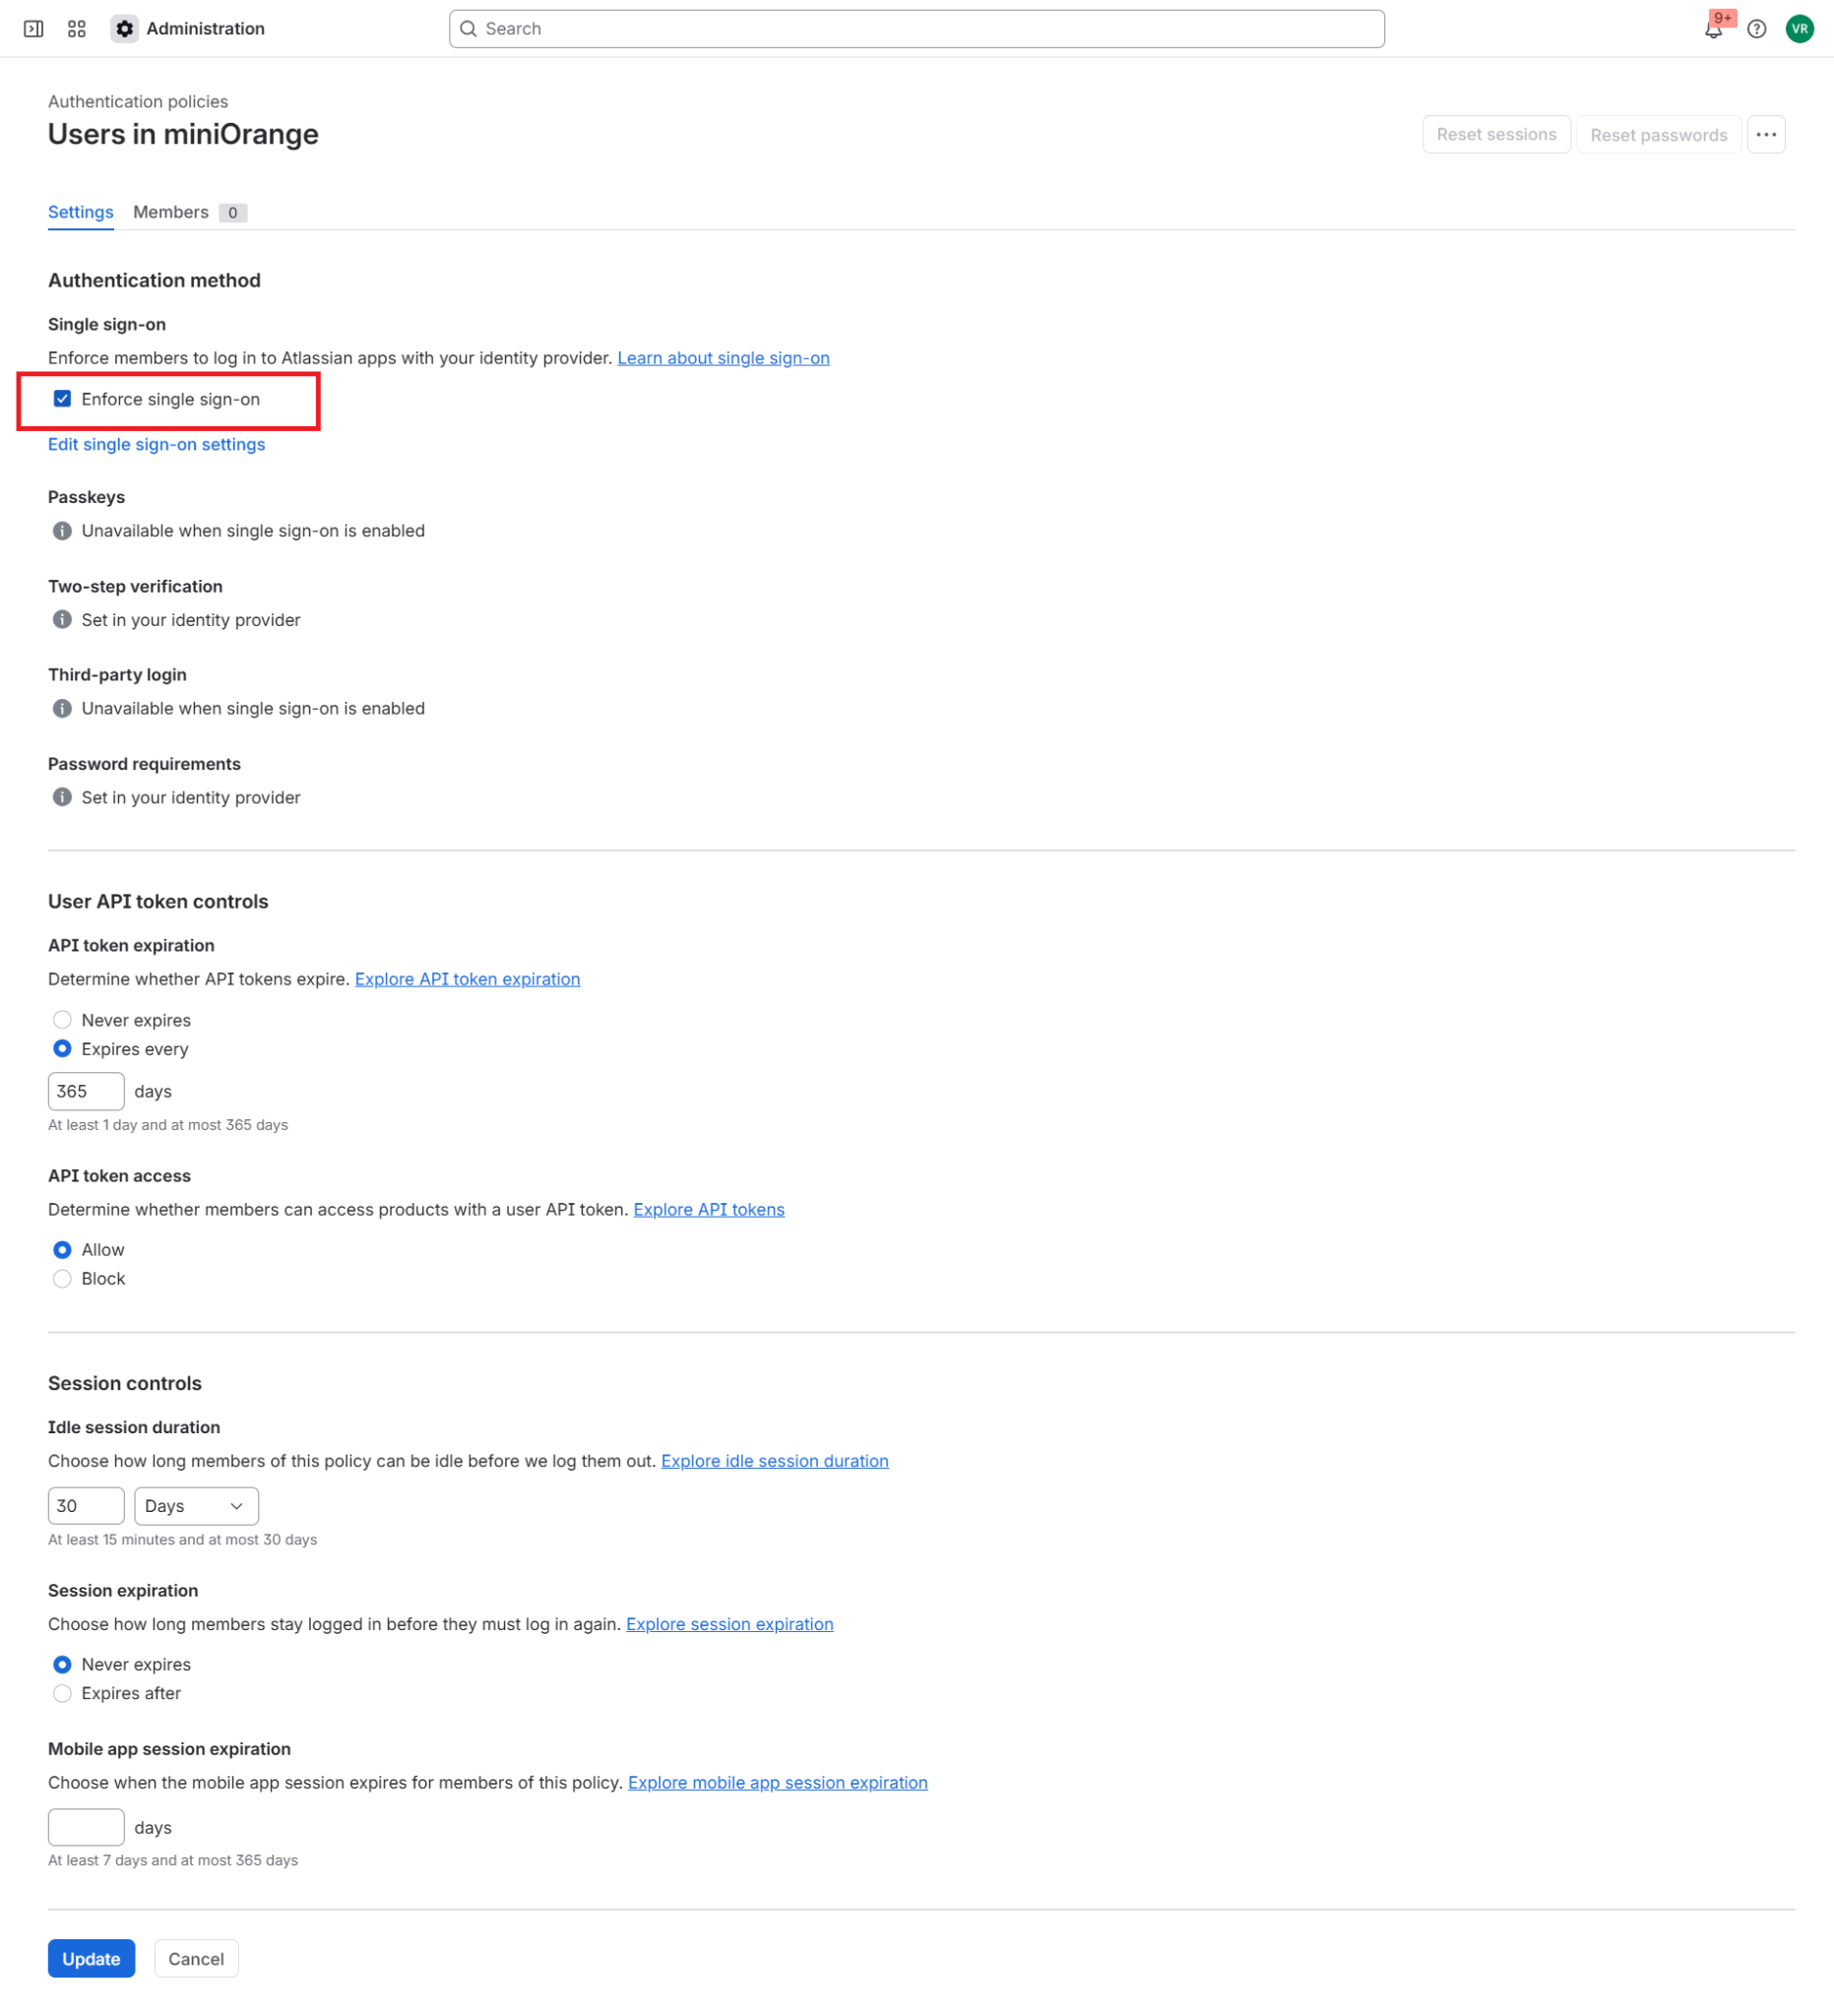
- Enforce Single sign-on for all users in that policy.
- In the Members section, add the users who should be required to complete 2FA.
- Click the Settings tab and click Update to save the policy.
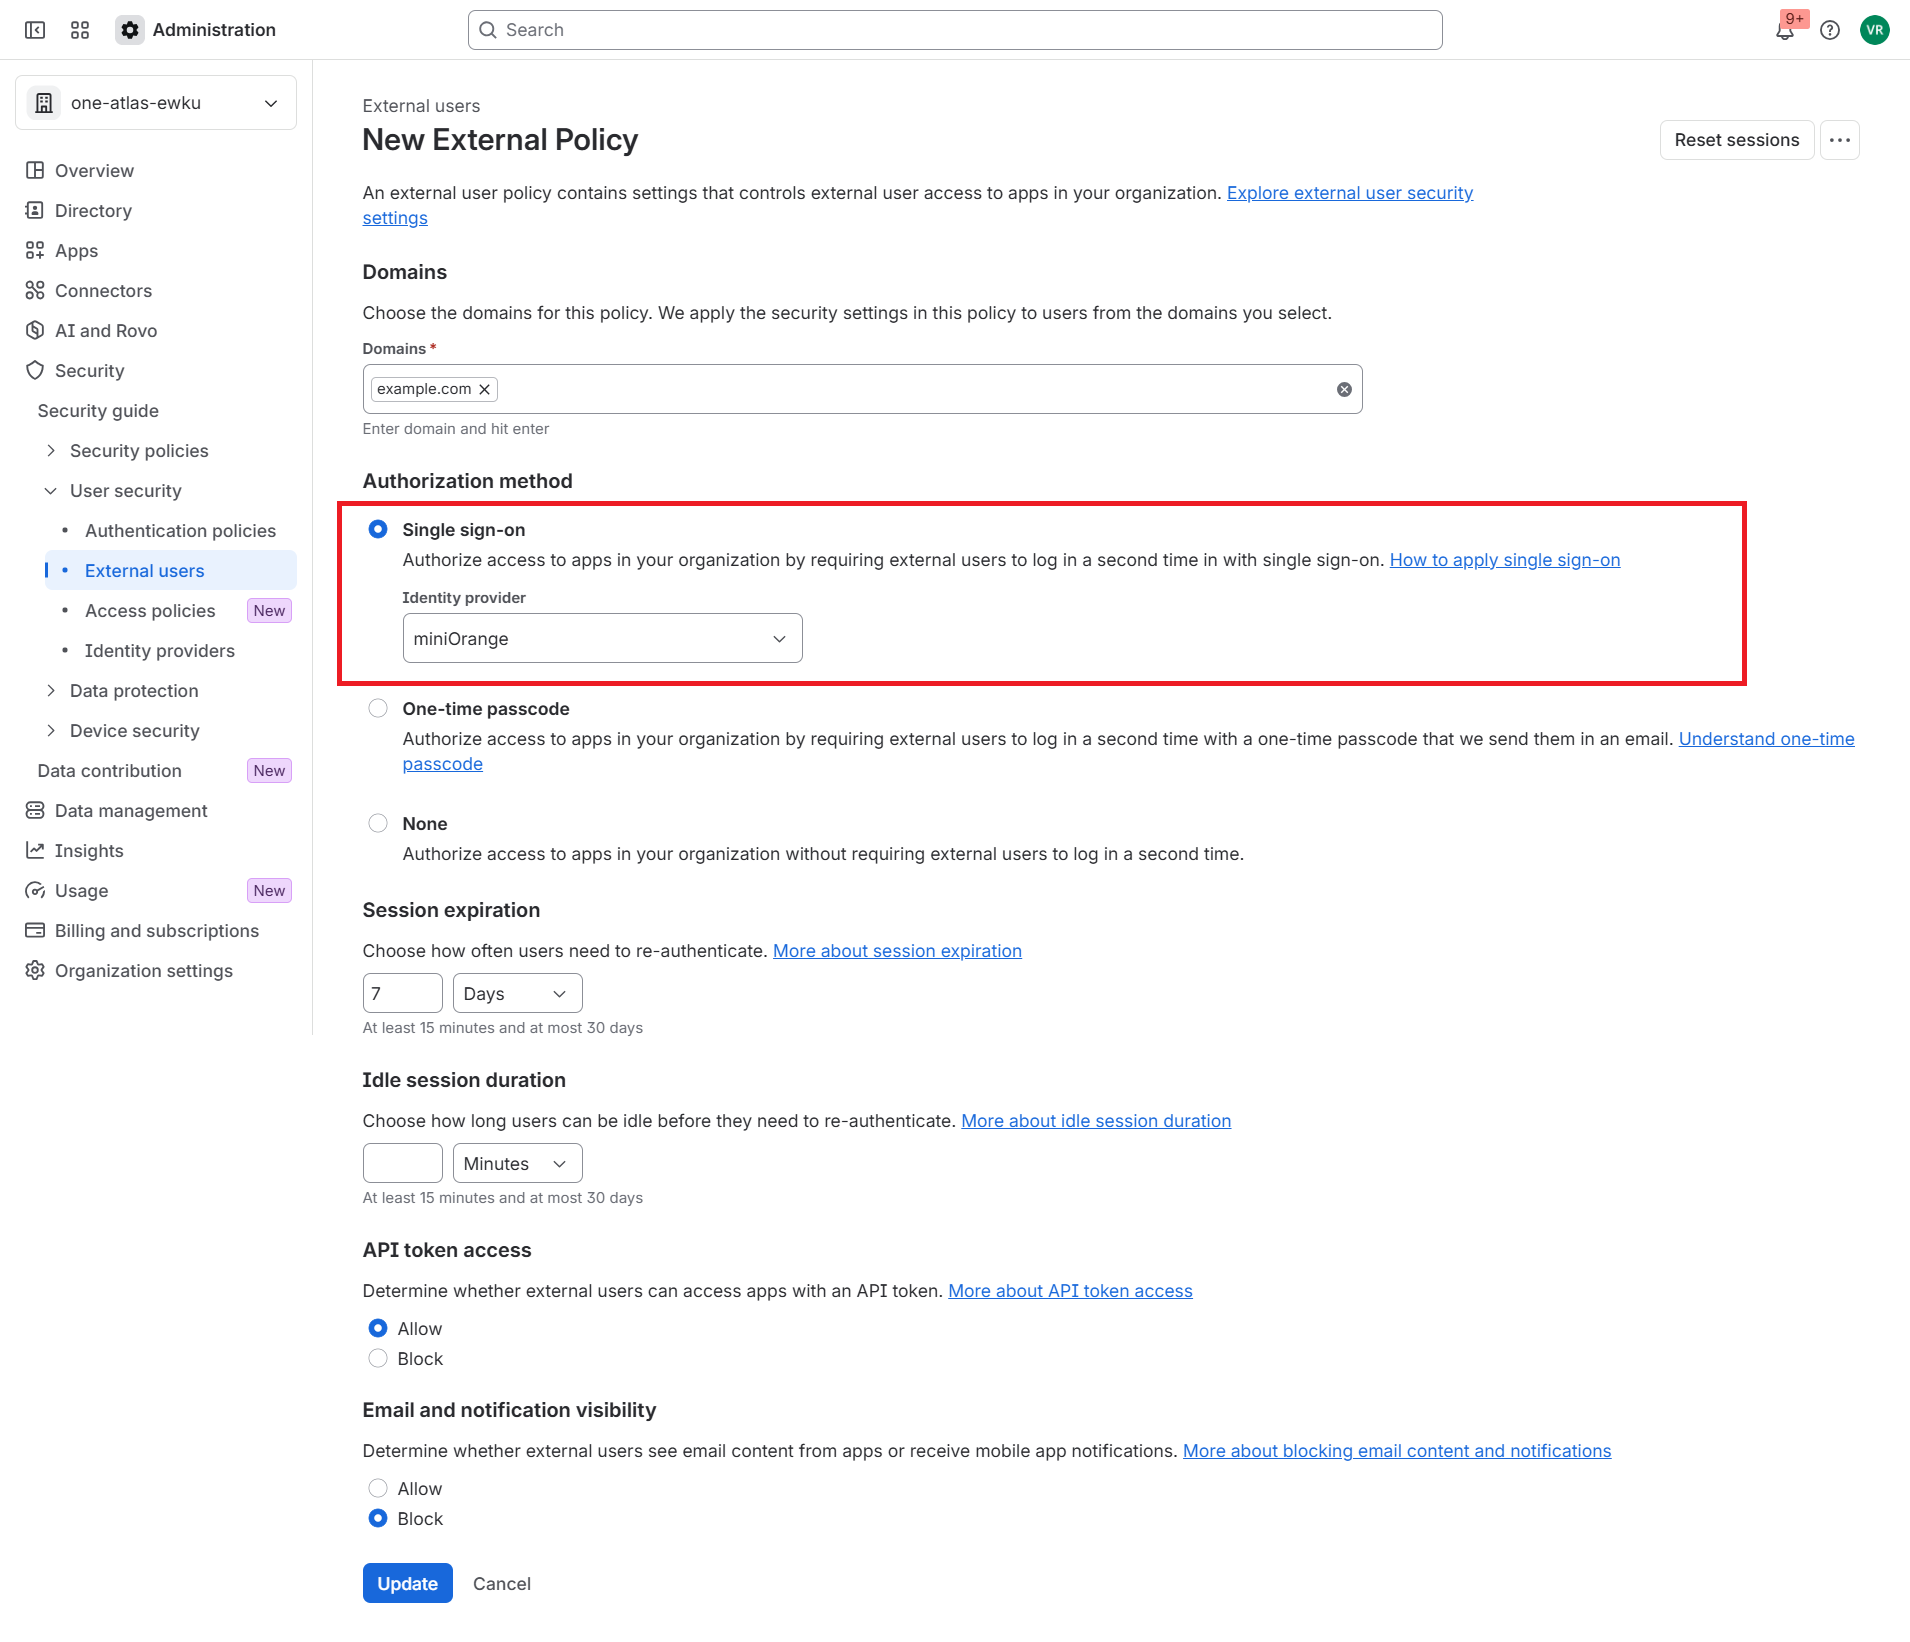
6B. Enable 2FA for External Users
External users are managed on the External users page, separate from the organization’s authentication policies.
- In the app’s Policy Setup step, open the External users link.
- Choose one of the following options:
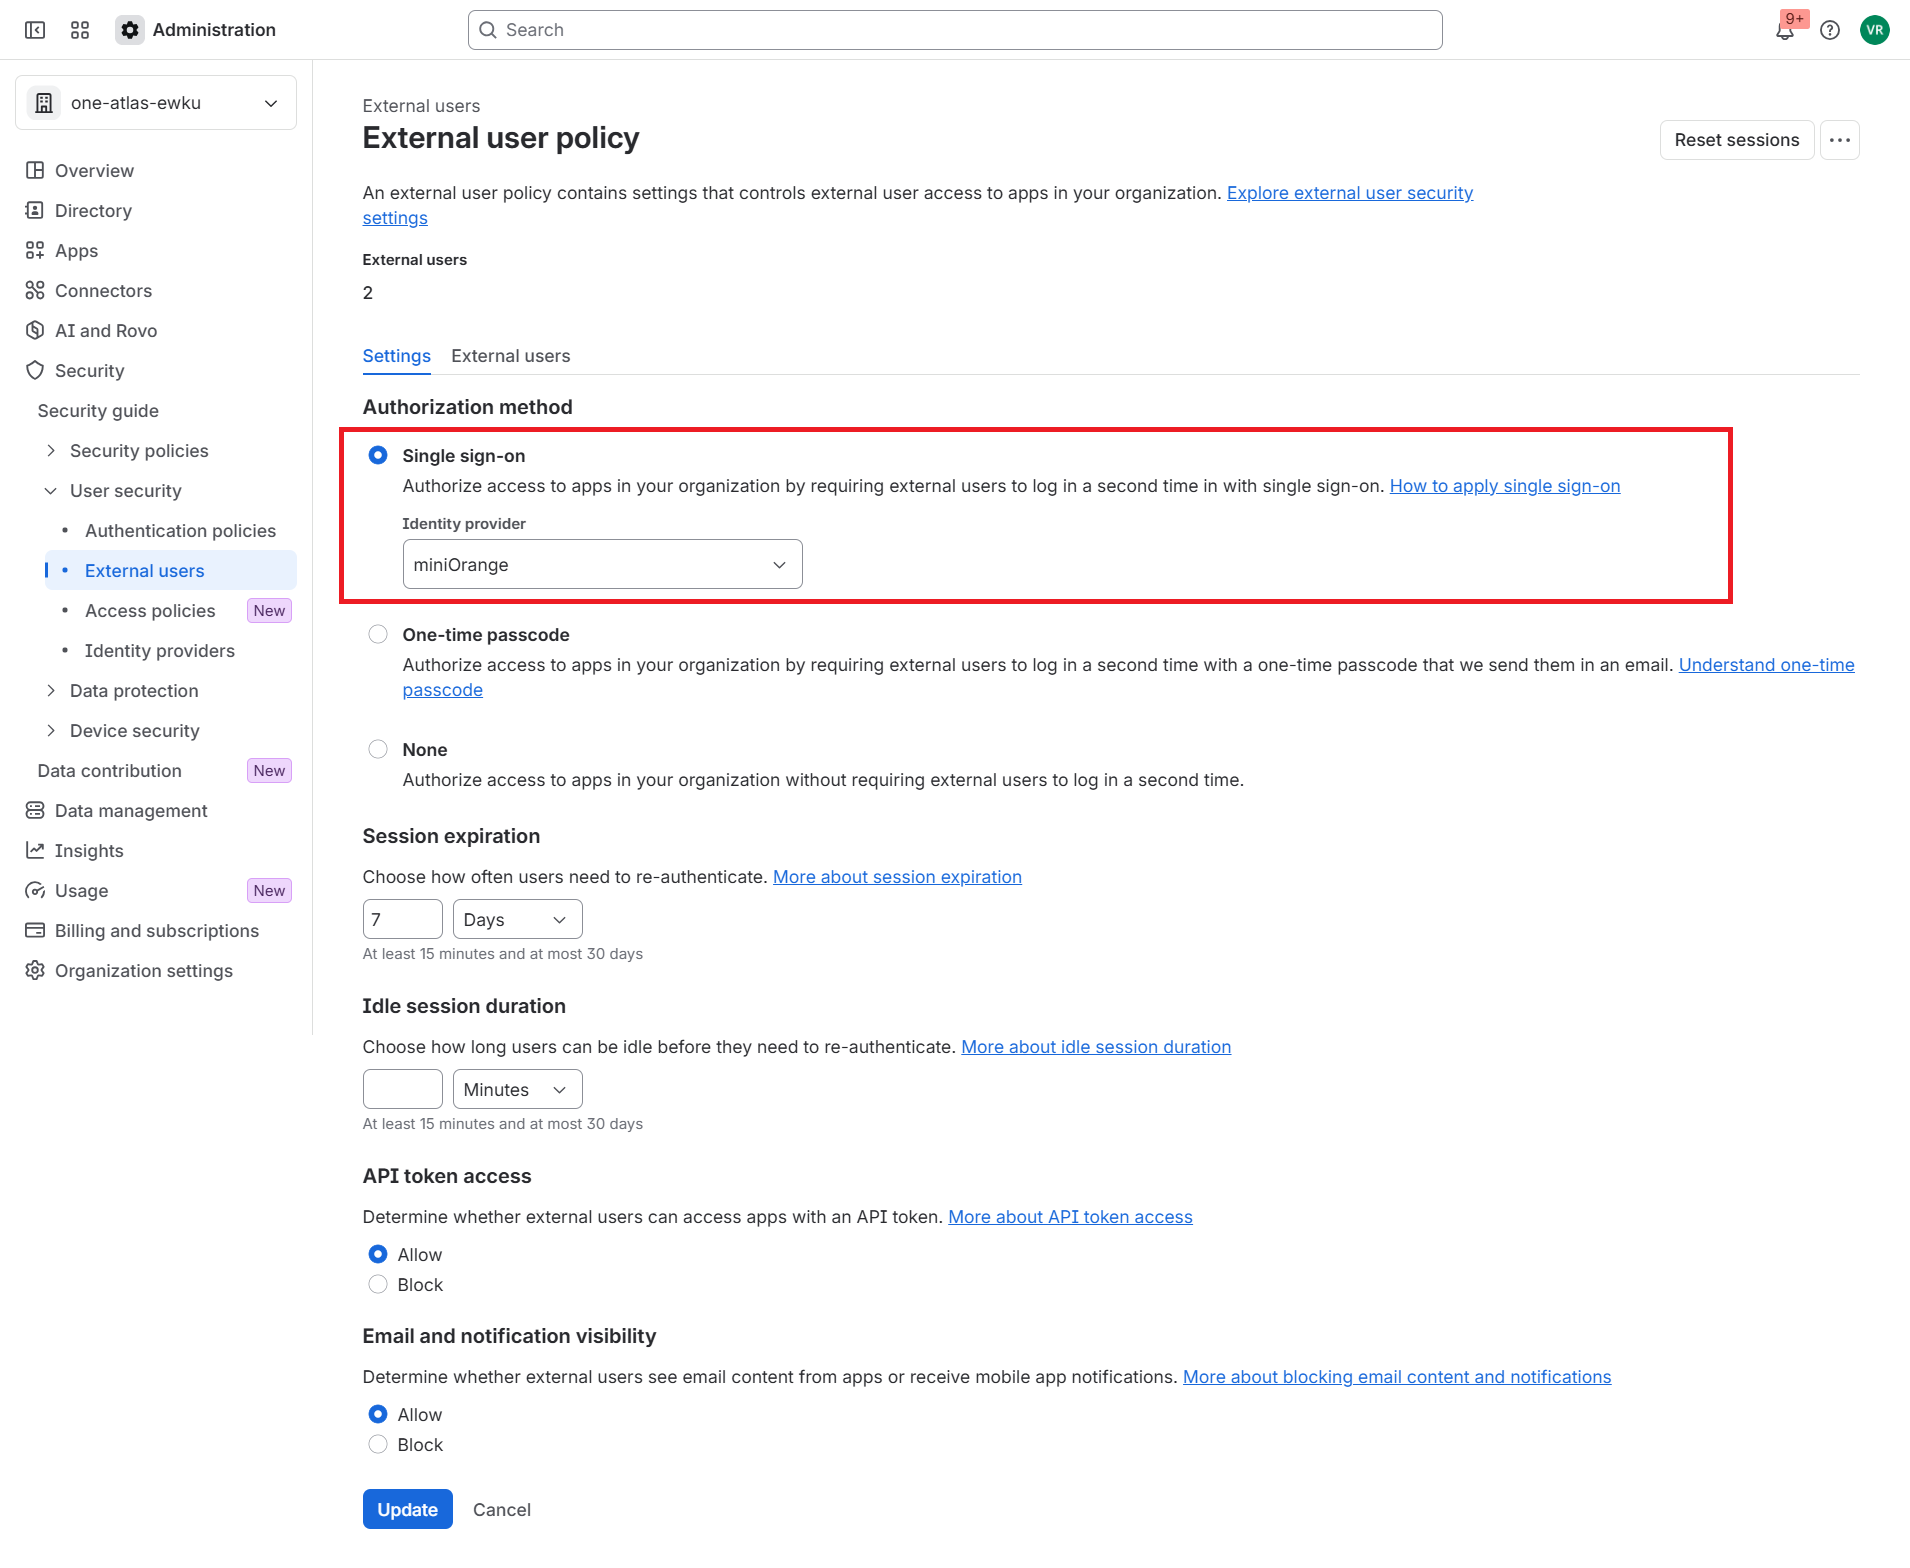
- Find the Default policy.
- Set Authorization method to Single sign-on.
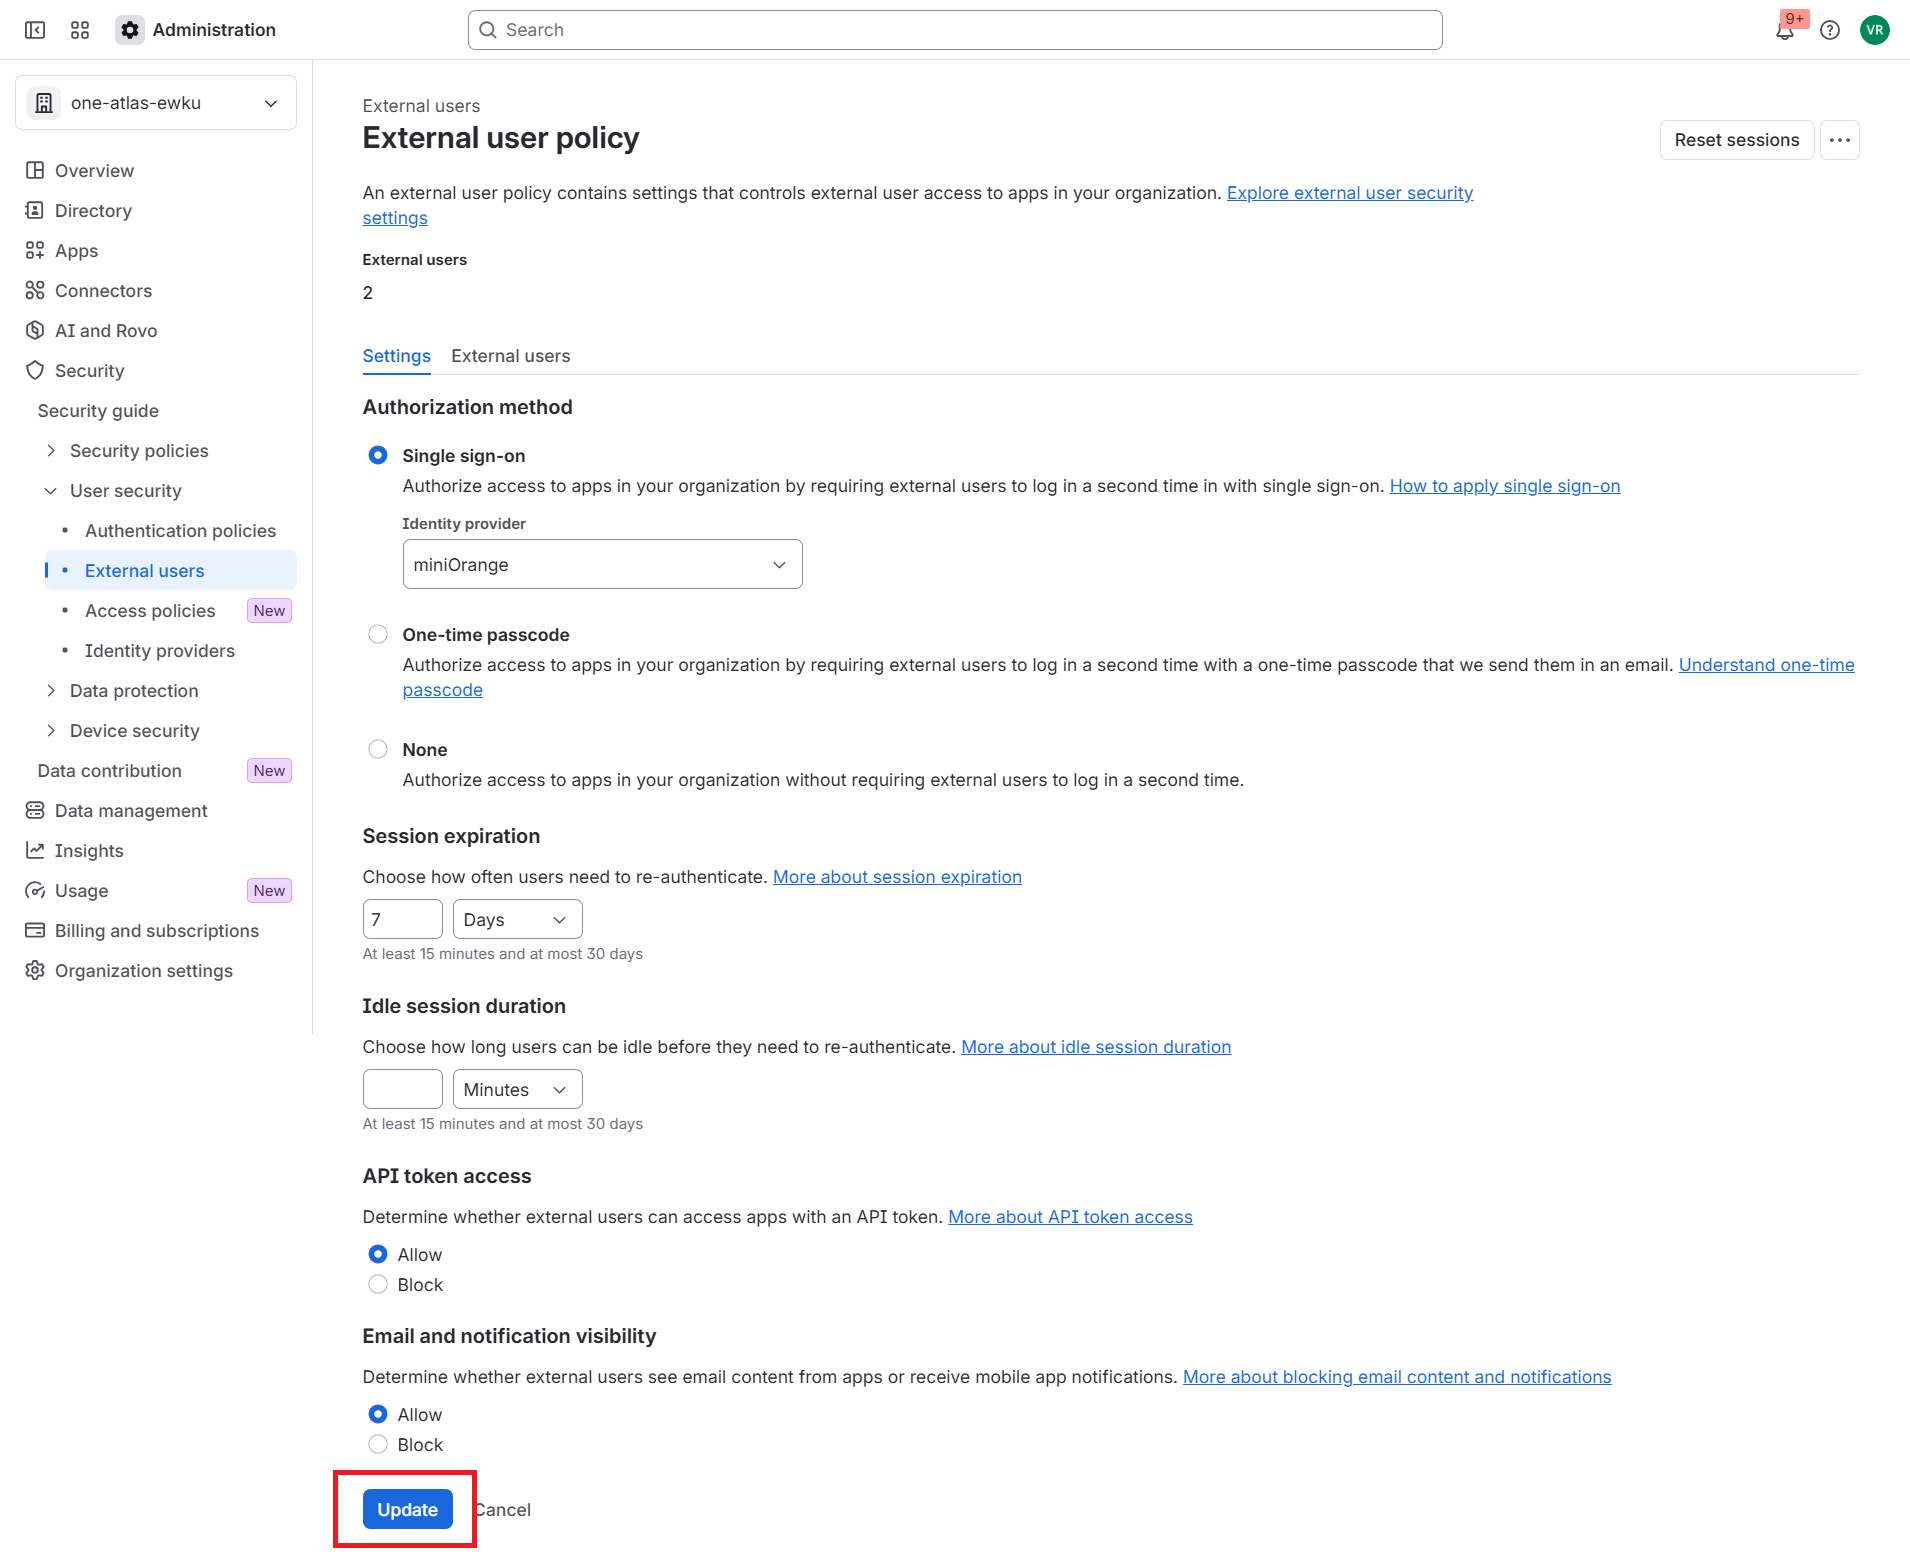
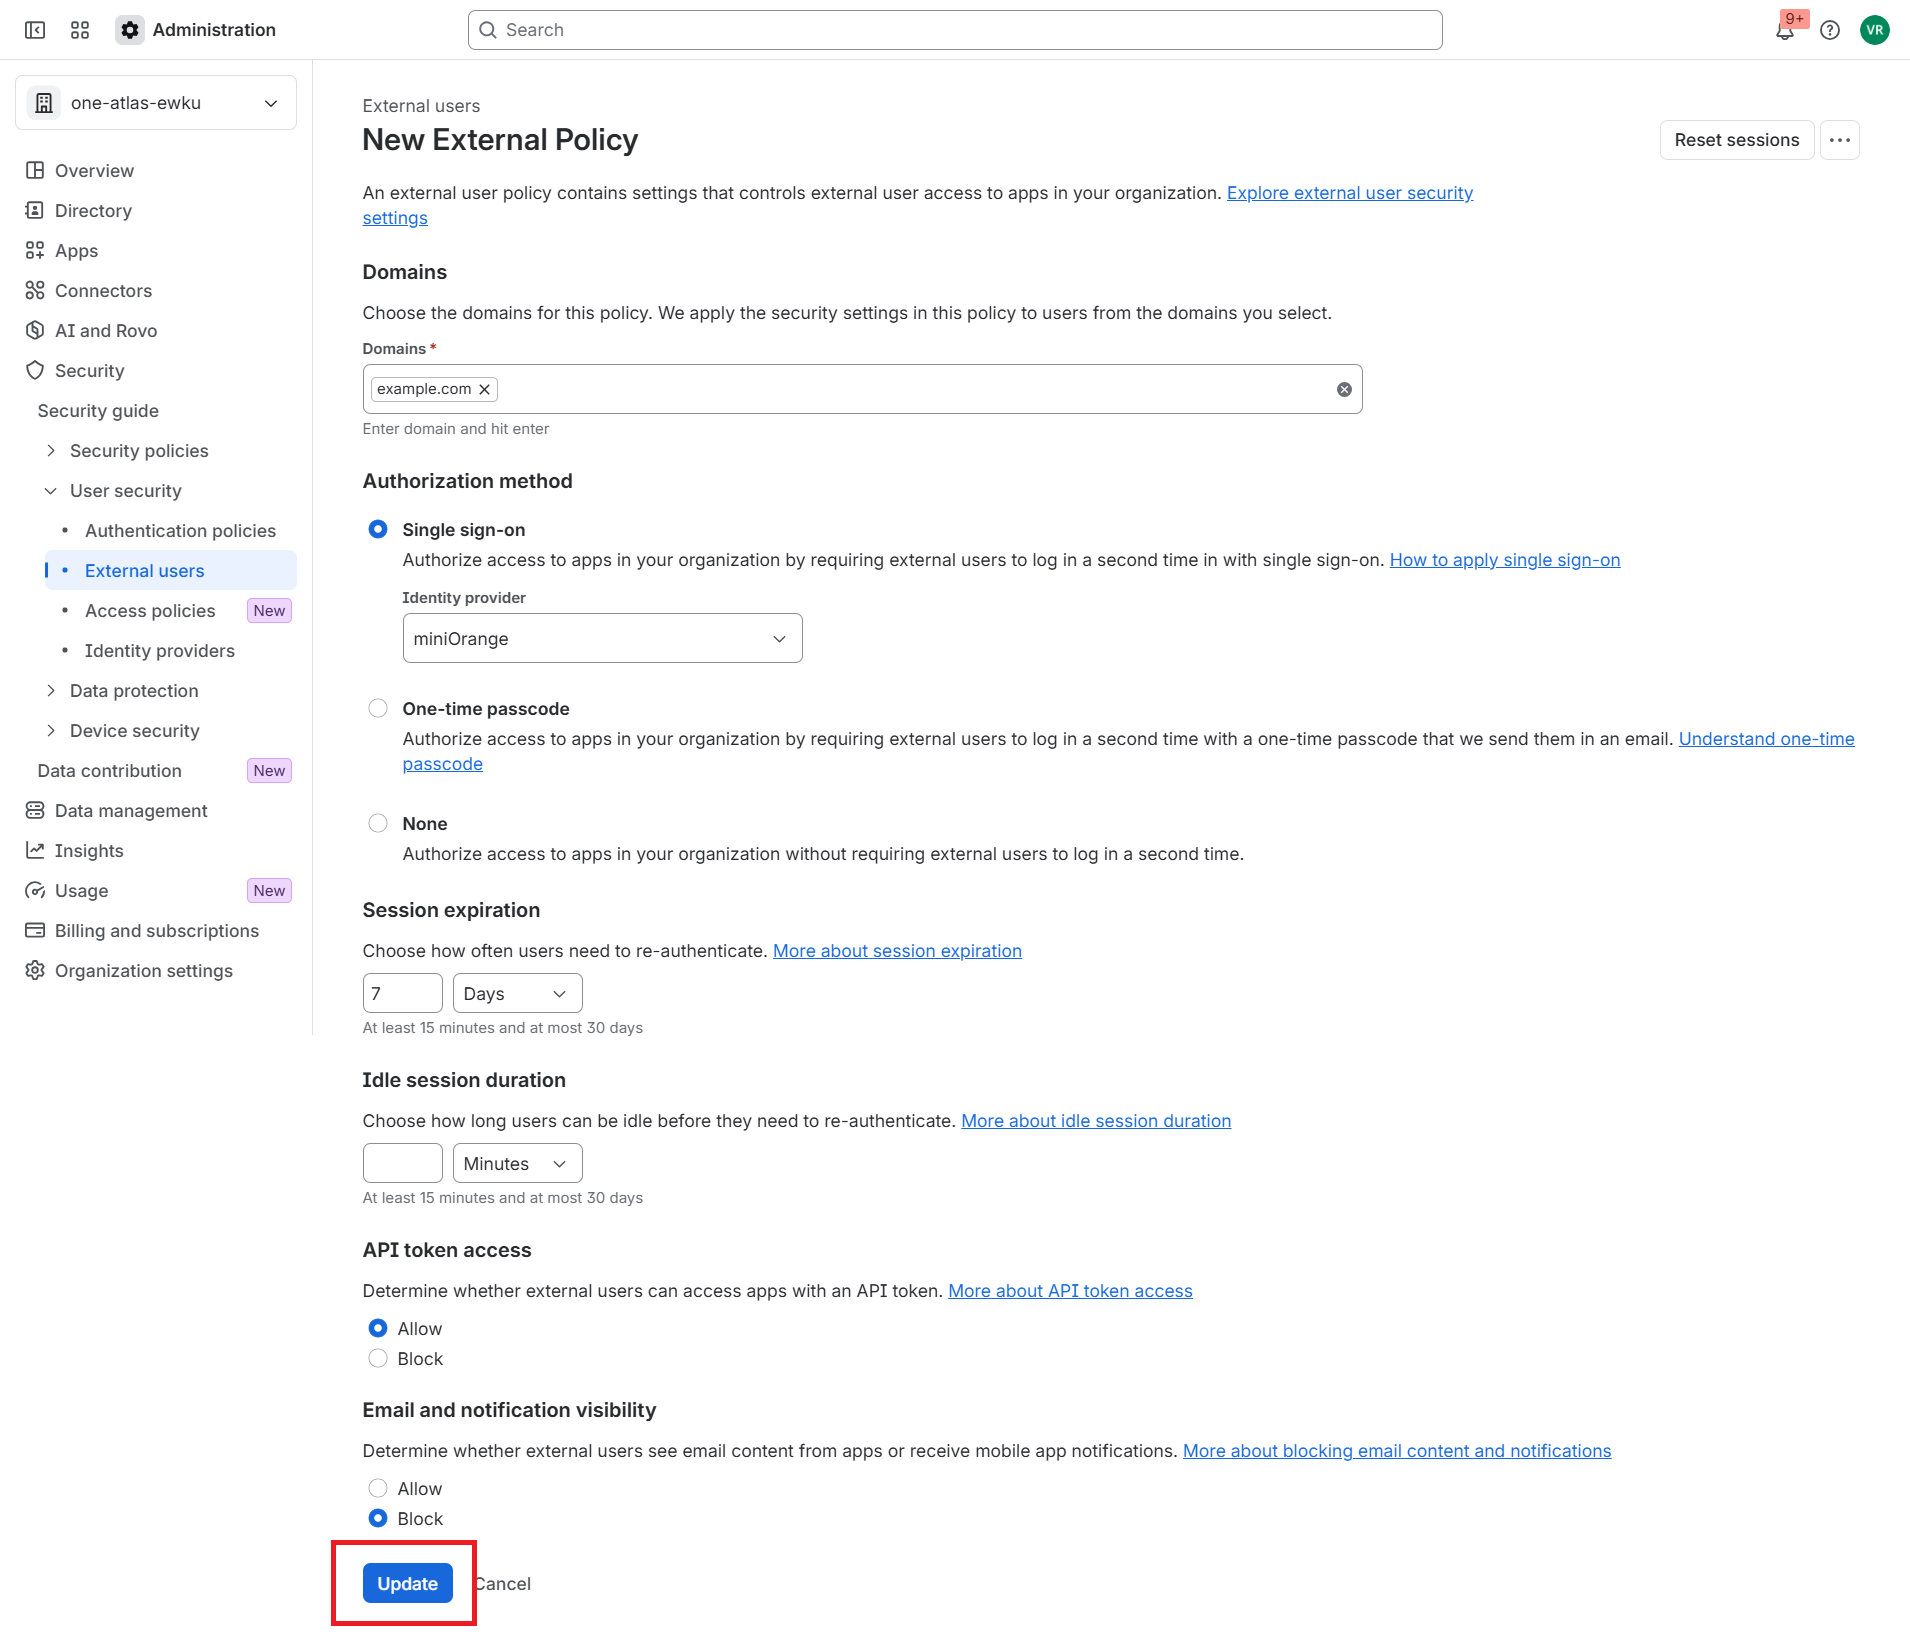
- Update the policy.
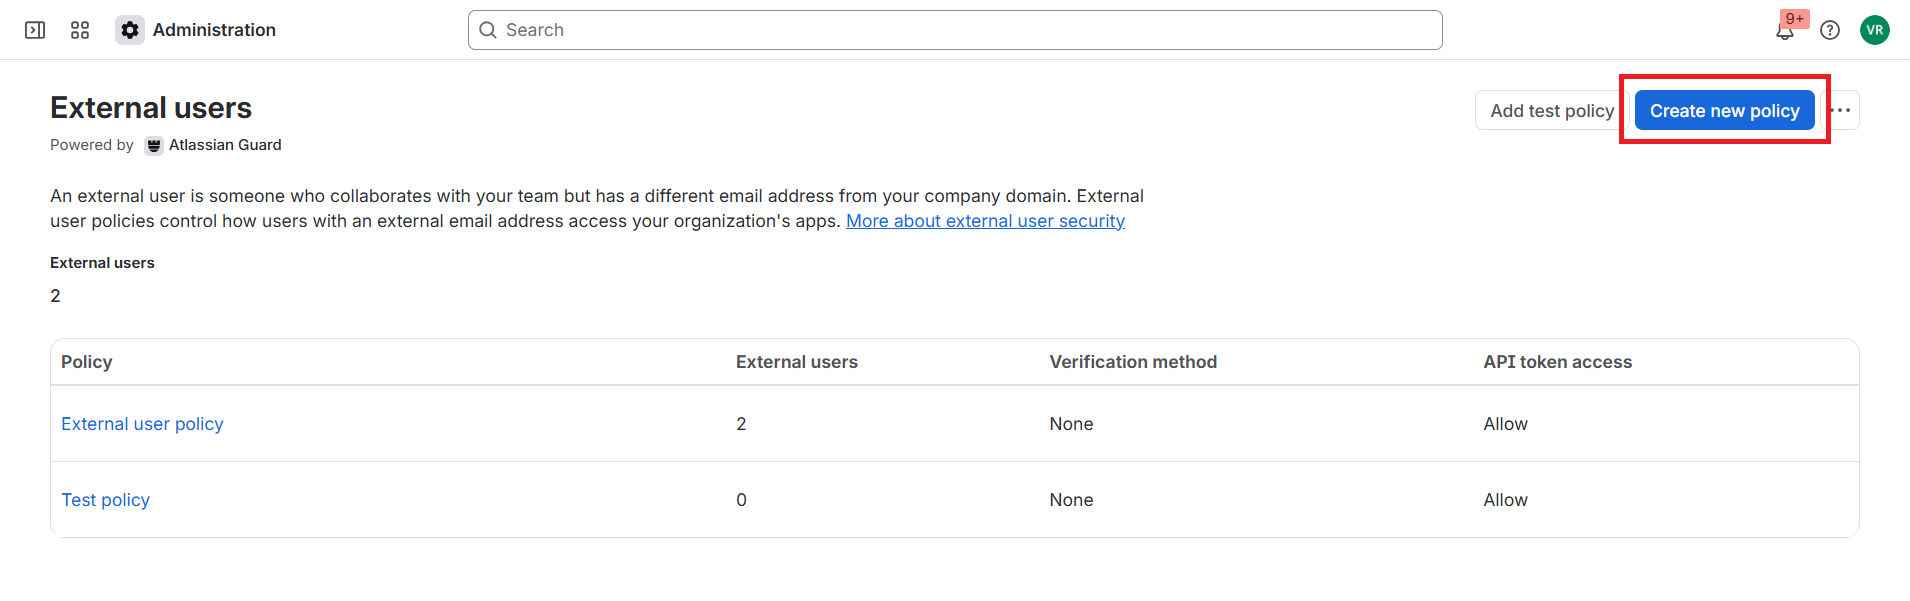
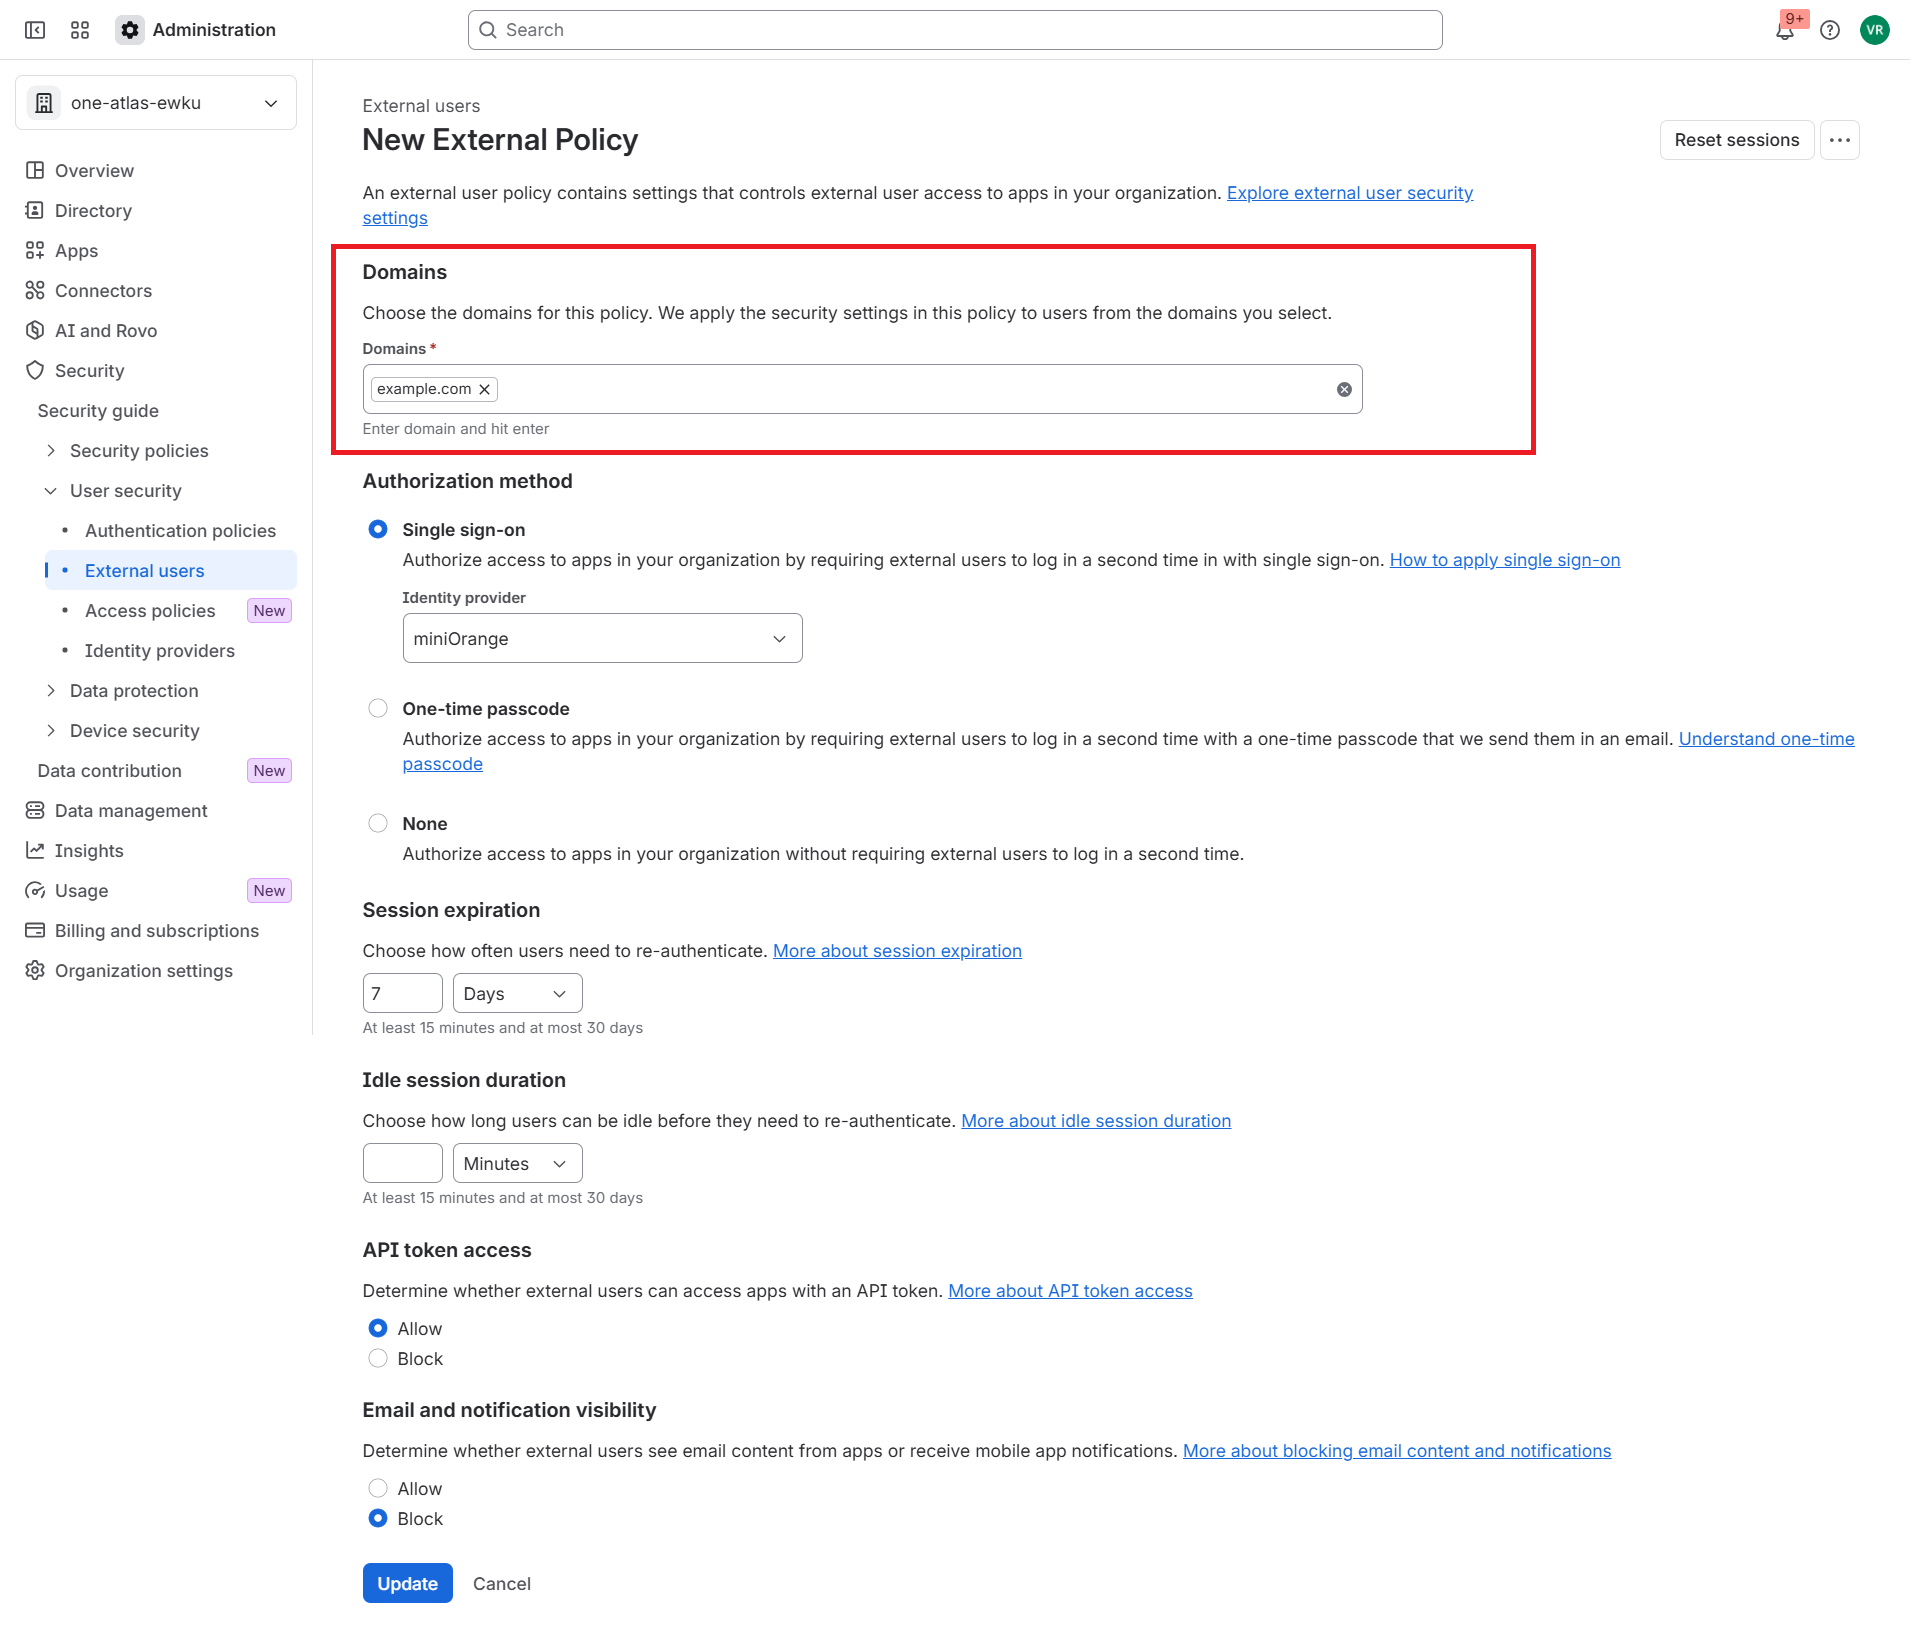
- Create a new external user policy for the specific domains.
- Choose the domains you want for this policy.
- Set the authentication method those domains should use.
- Update the policy.
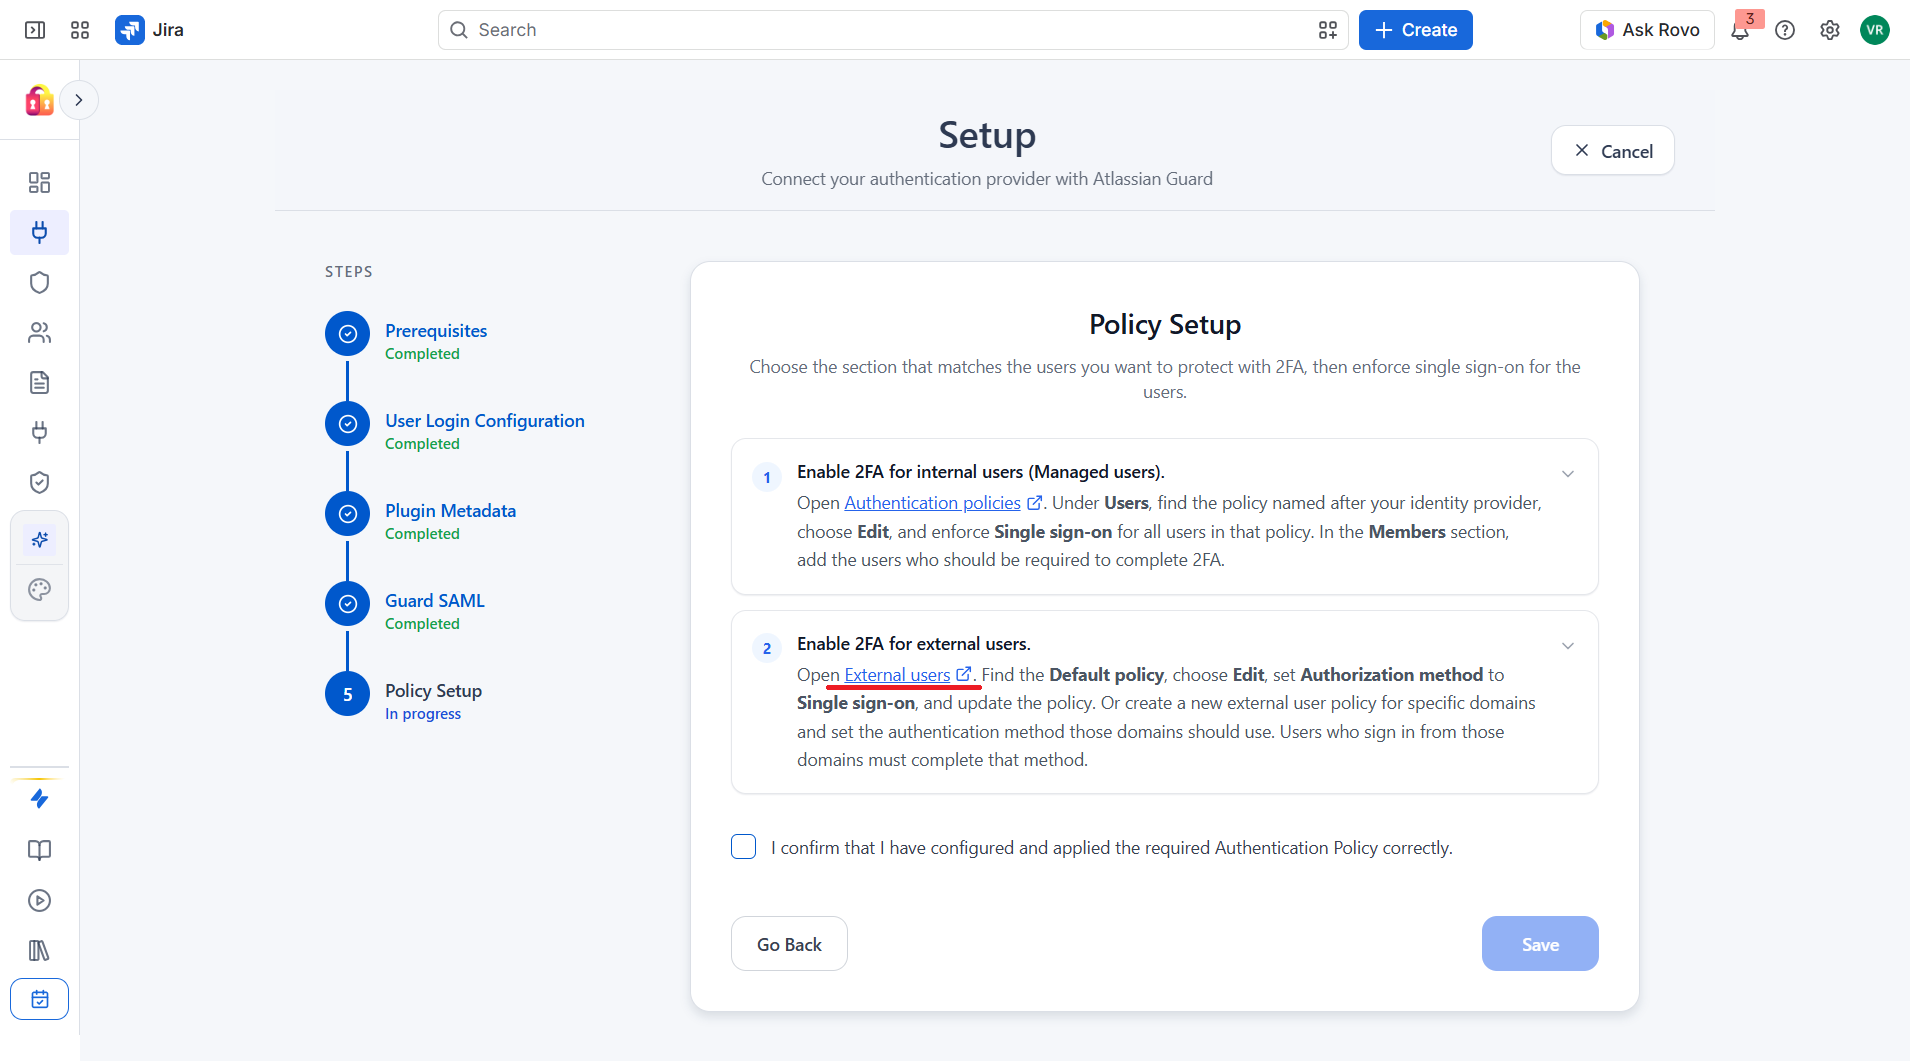
Option 1: Default policy (all external users)
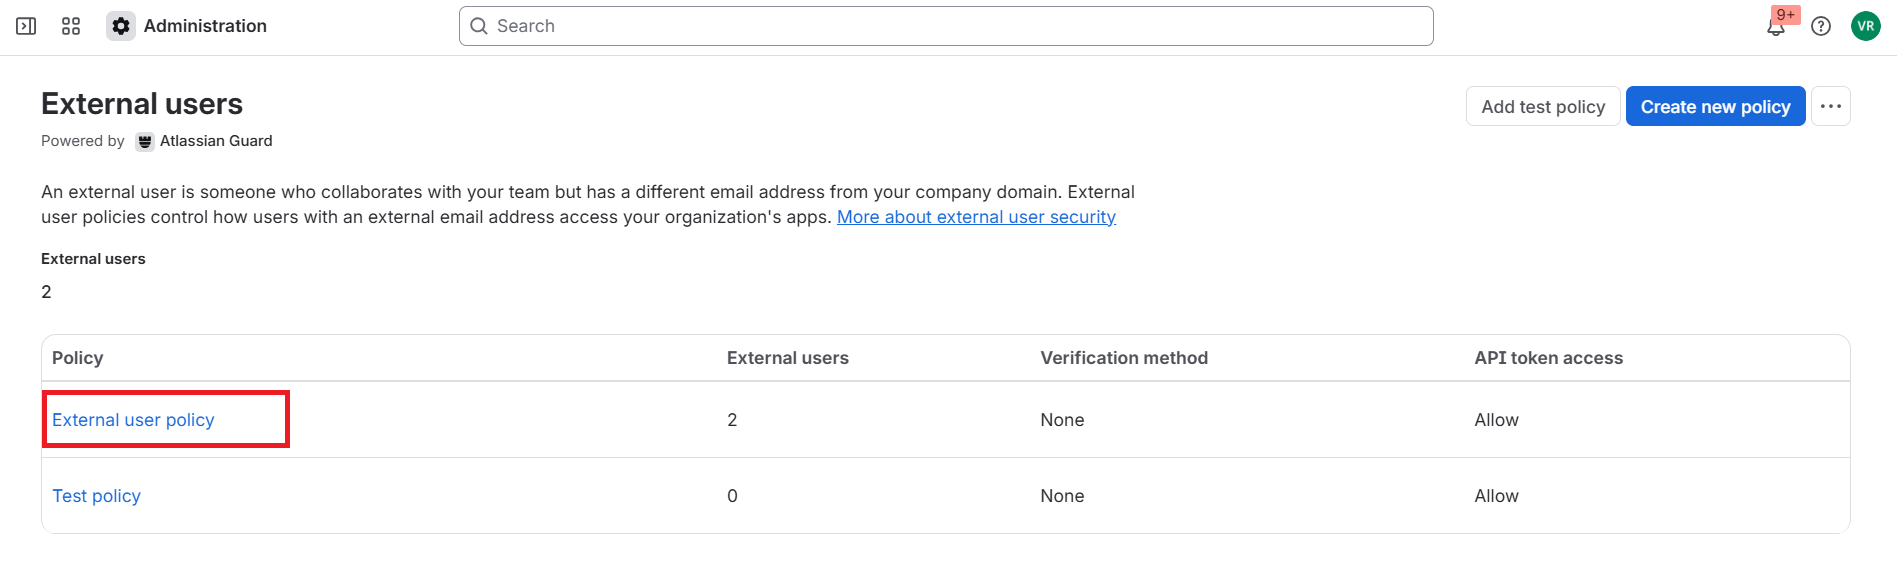
Option 2: Domain-specific policy (selected domains)
Complete the Setup
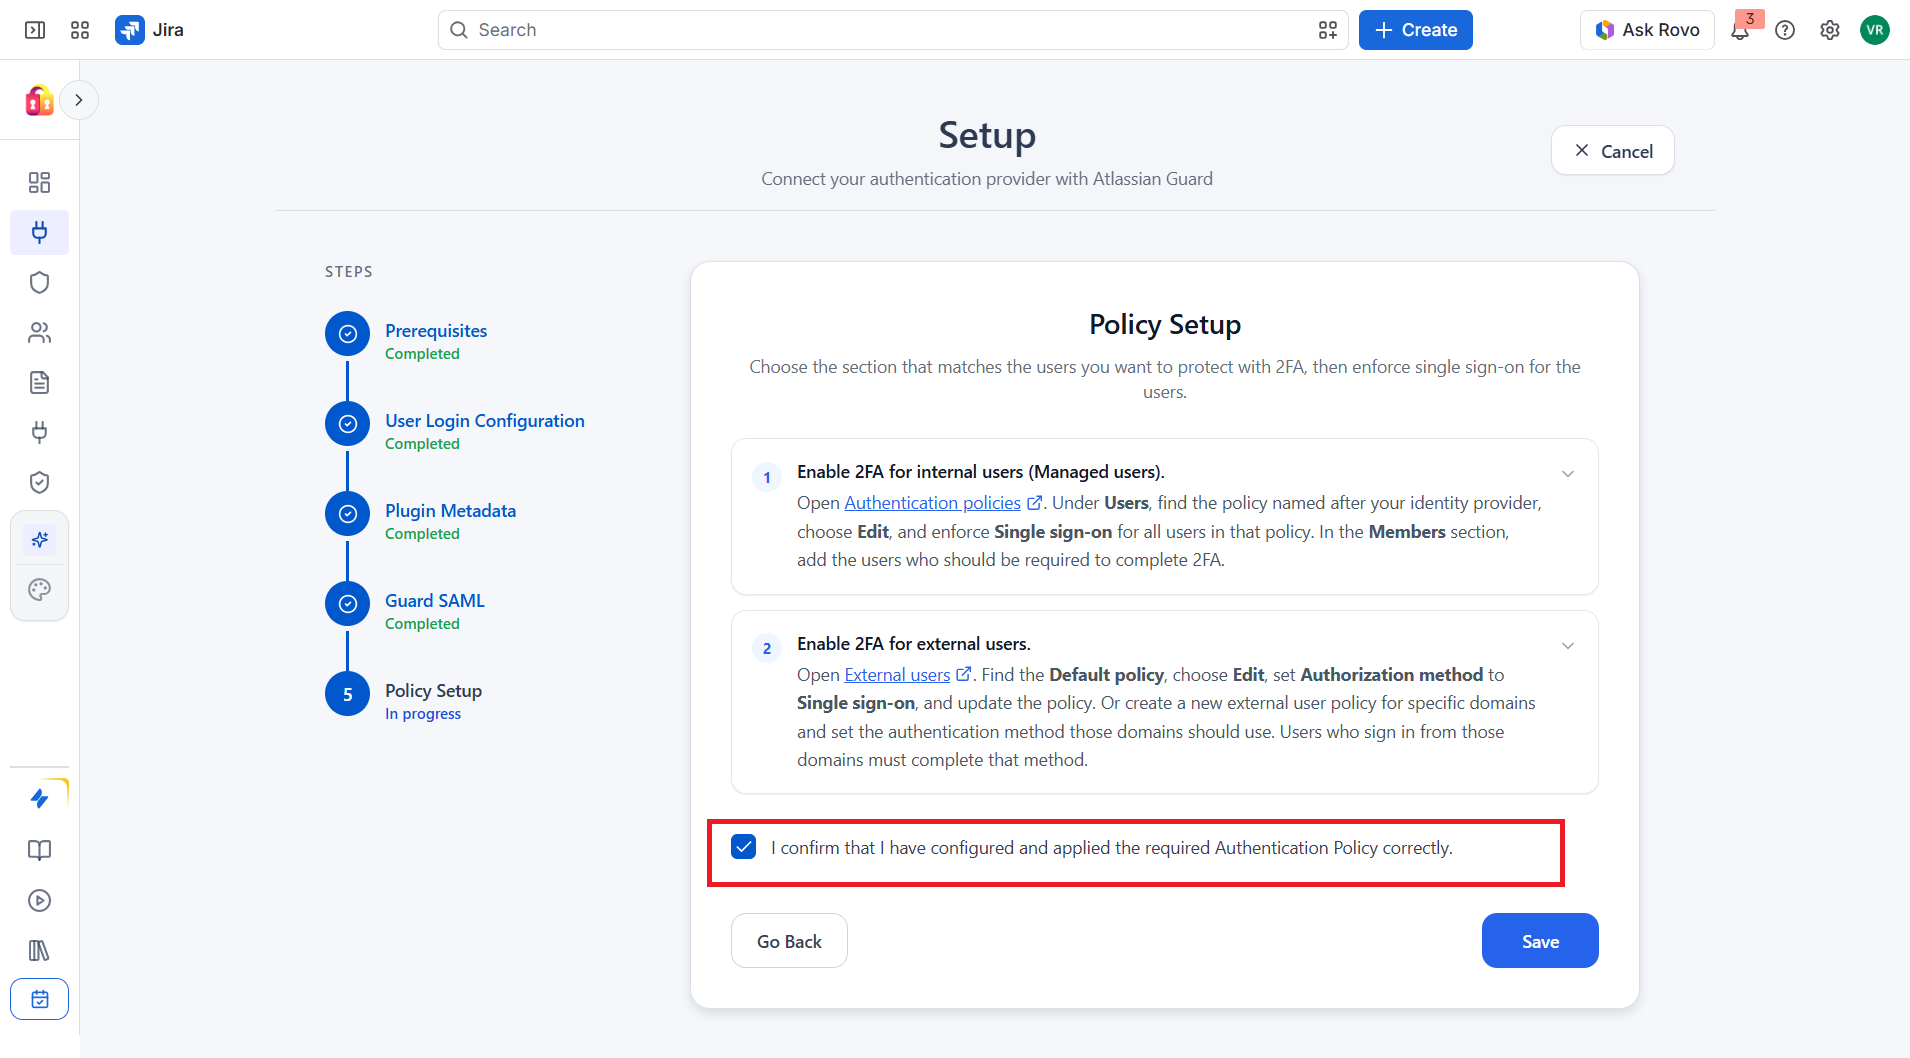
- Return to the app’s Policy Setup step. Select the confirmation checkbox: I confirm that I have configured and applied the required Authentication Policy correctly.
- Click Save.
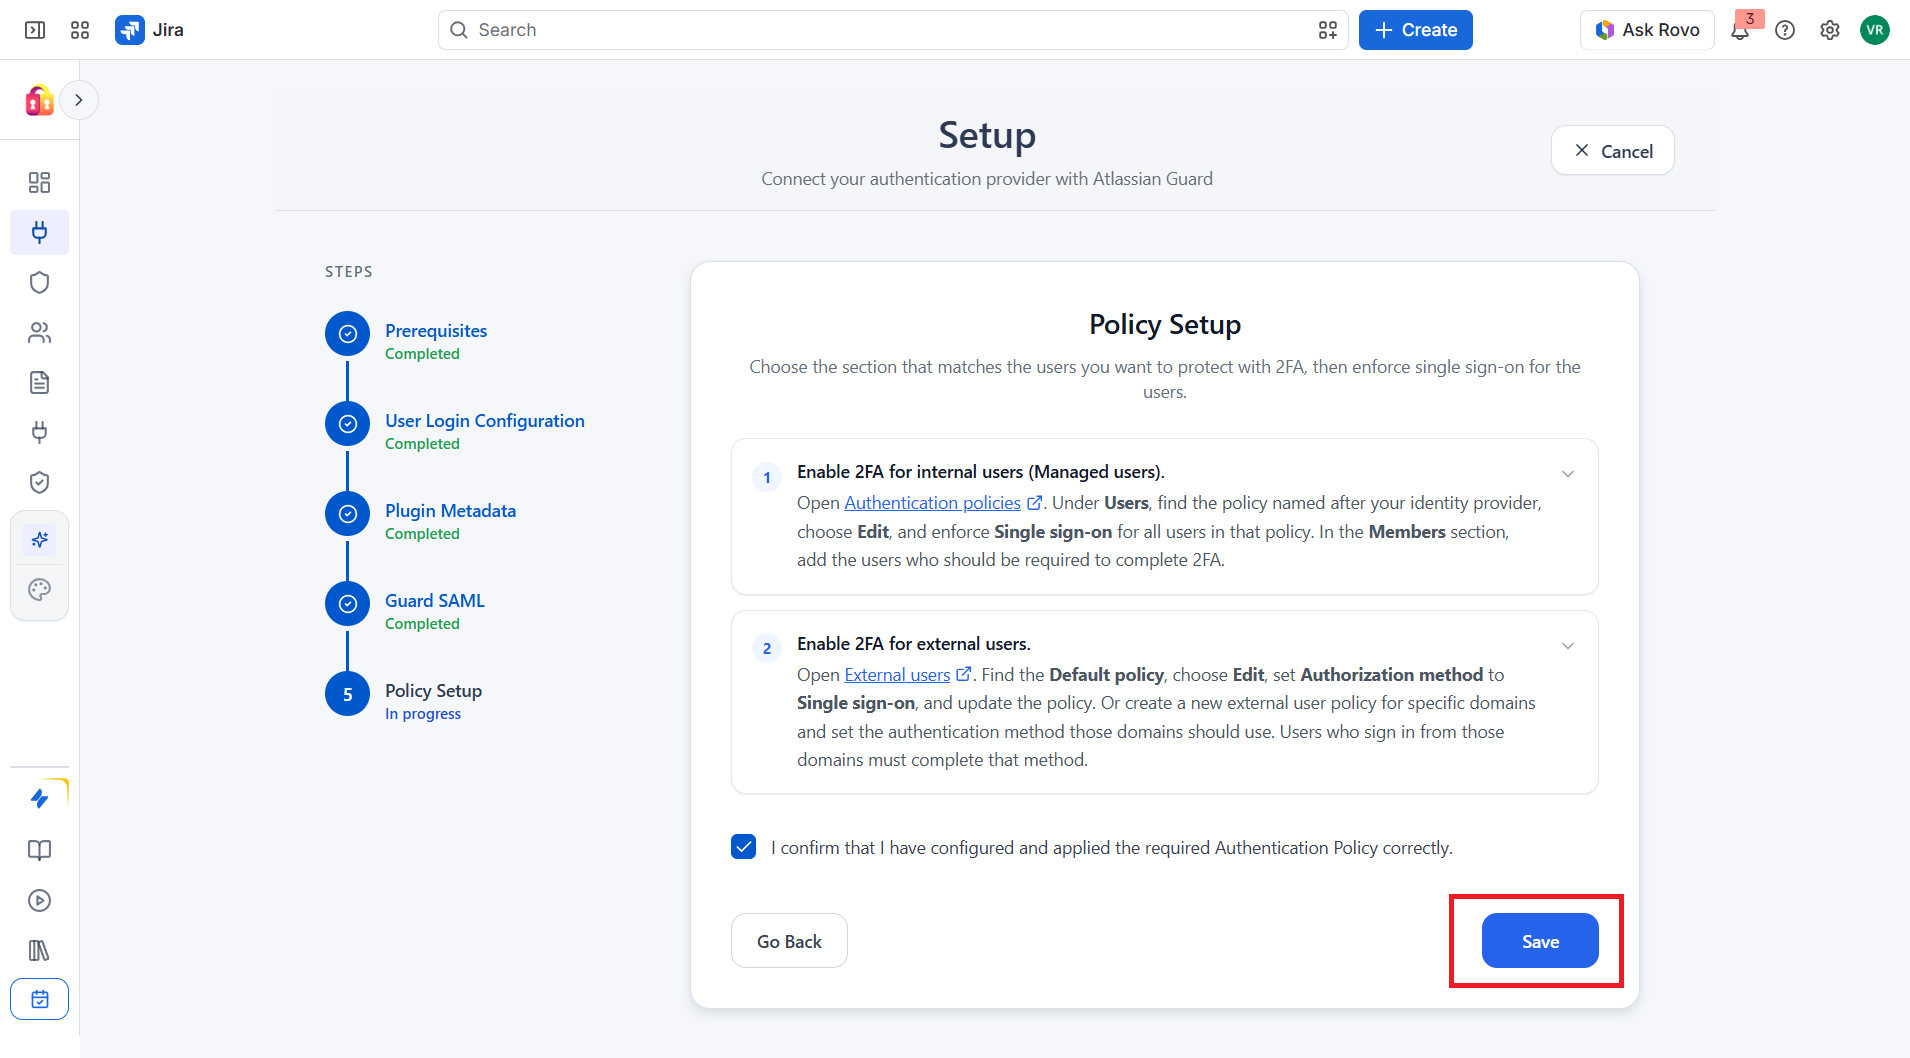
You have now completed the Guard integration setup successfully!
Proceed to the 2FA Configuration tab to configure authentication methods according to your requirements.
2FA Configuration Tab
After completing the Guard integration, navigate to the 2FA Configuration tab to enable and configure Two-Factor Authentication for your managed and external users.
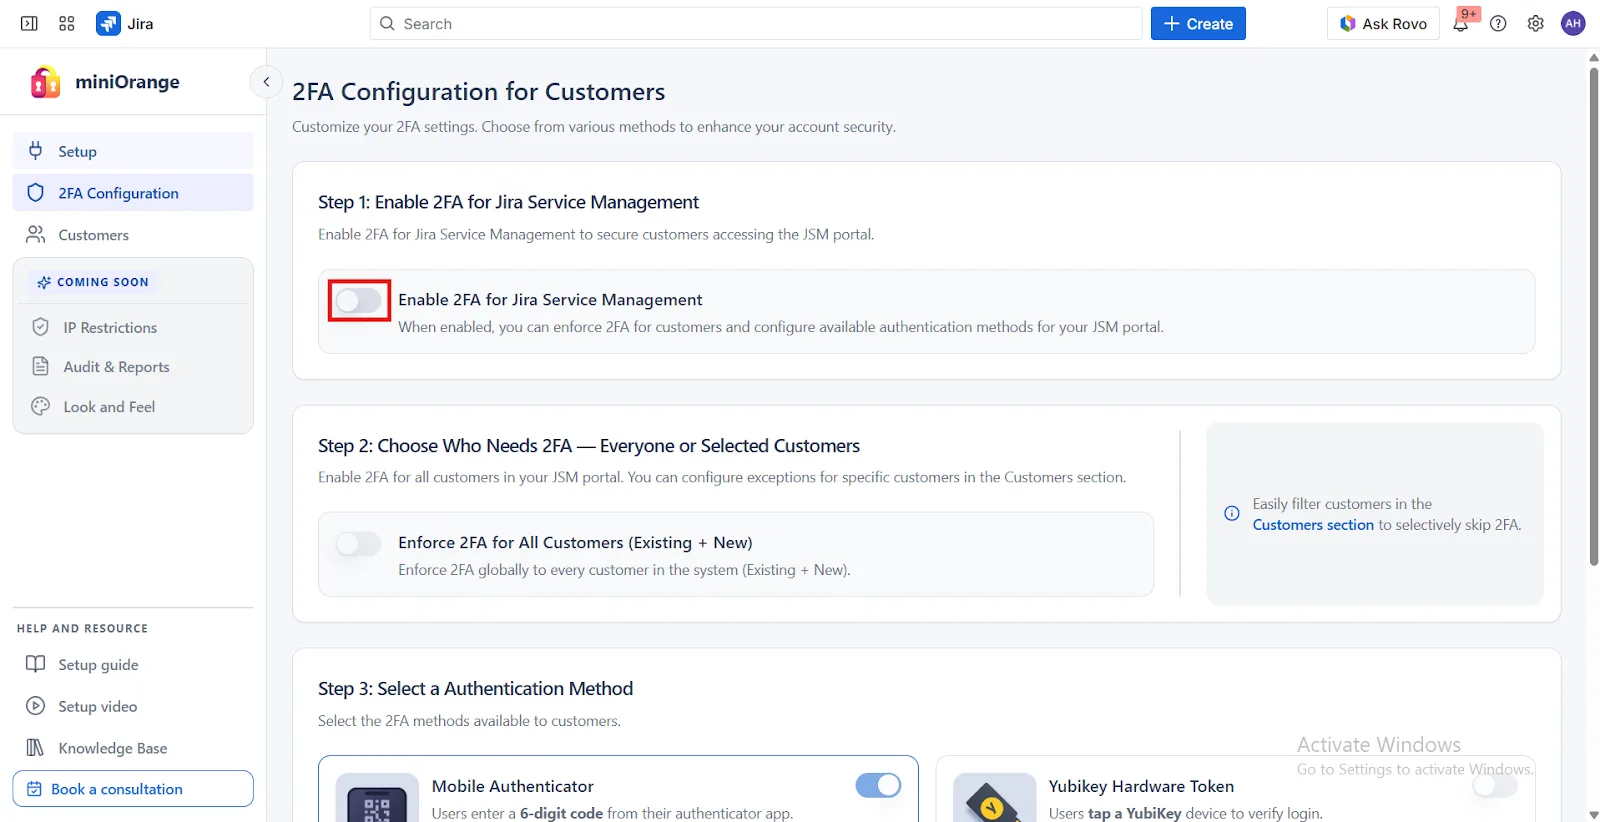
1. Enable 2FA for Jira
Enable the Enable 2FA for Atlassian apps toggle for Jira to activate 2FA for managed and external users. Once enabled, you can configure the available 2FA methods and manage user-level settings.
2. Choose Who Needs 2FA, Everyone or Selected Users
How you enroll users depends on whether you configured an external Identity Provider in the Setup tab.
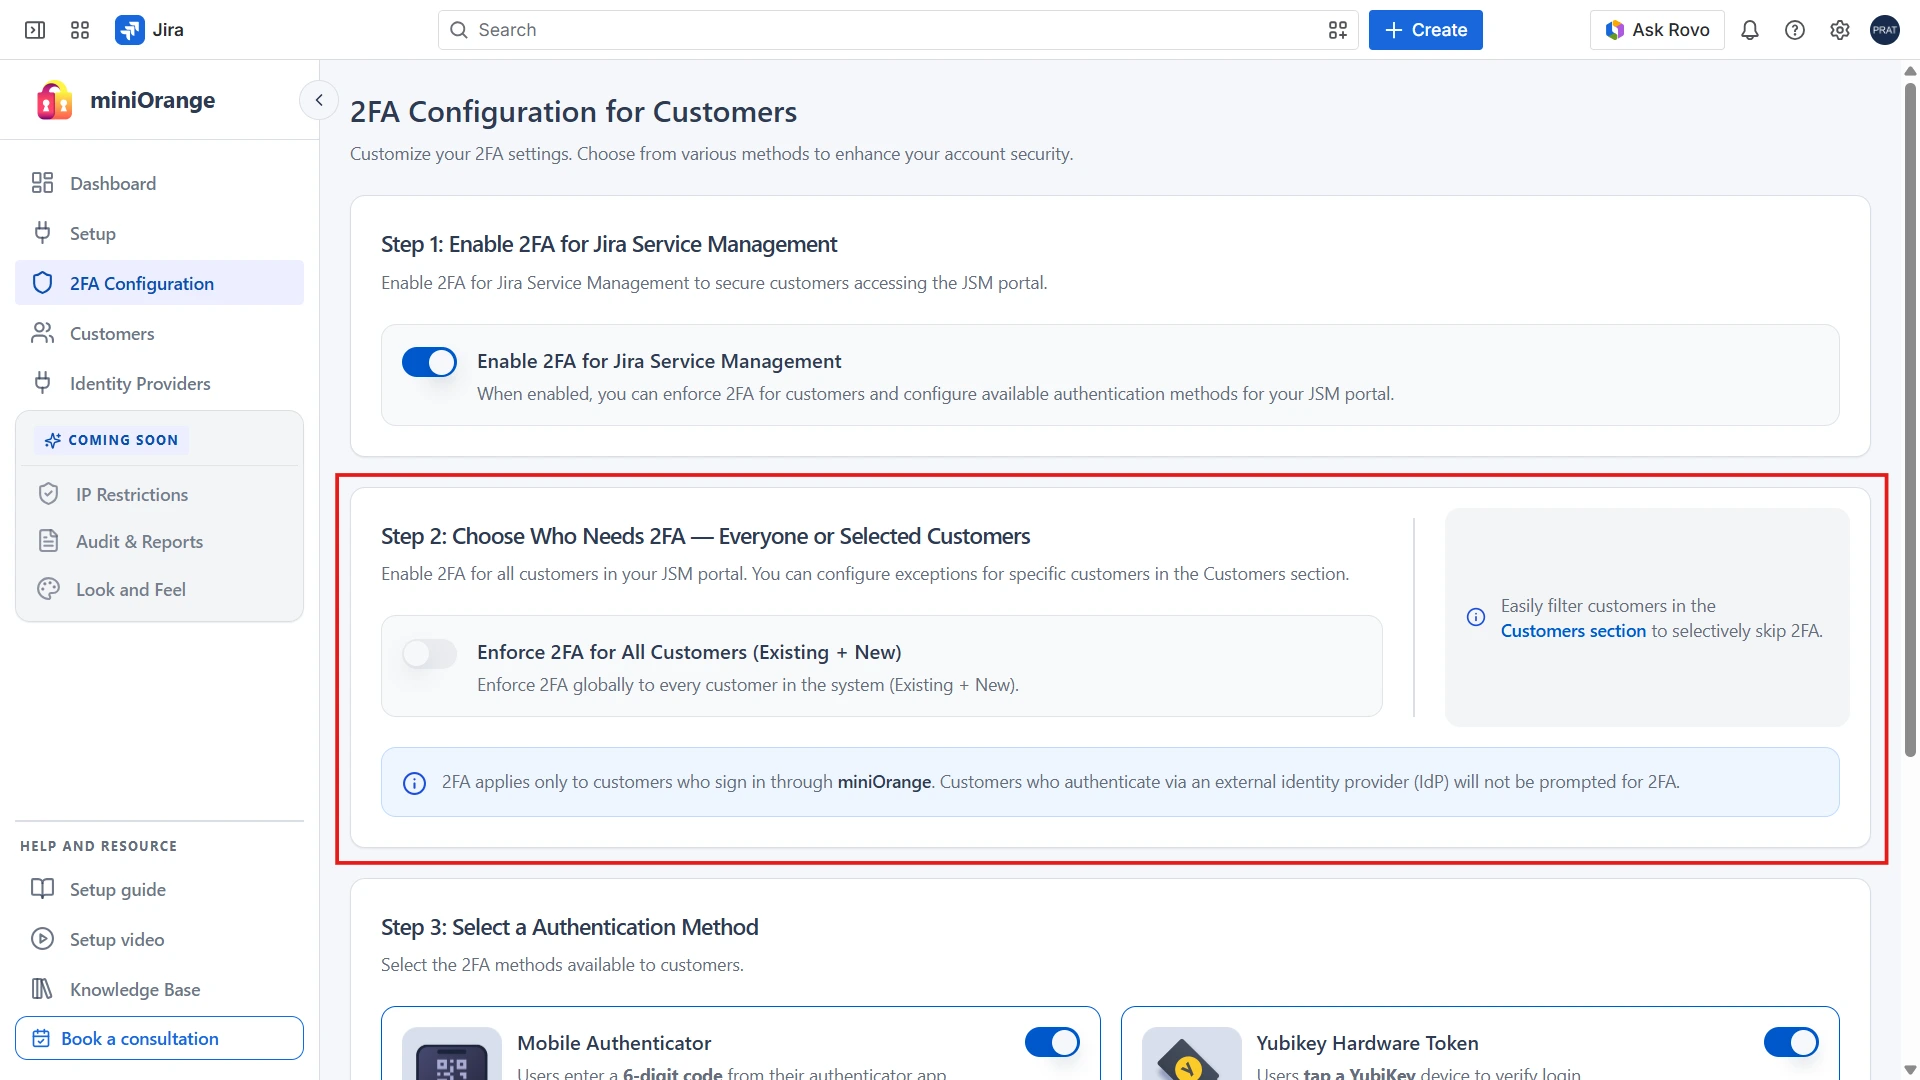
2A. If You Use an External Identity Provider
When an external IdP is configured, the Enforce 2FA for All Users (Existing + New) toggle is disabled. Because 2FA is only prompted for users who sign in through this plugin. Users who sign in through the external Identity Provider are not prompted for 2FA.
Instead, enable 2FA manually for the users who require it from the Users tab, individually or in bulk. See “Enable/Disable 2FA for Individual Users” and “Bulk Actions” below for detailed instructions.
2B. If You Do Not Use an External Identity Provider
If you did not configure an external Identity Provider, you have full control over organization-wide enforcement:
- Enable 2FA for all users in your organization to enhance security across the board. You can create exceptions for specific users or groups from the Users tab.
- Enforce 2FA for all users (existing and newly created) to ensure consistent security coverage across your organization.
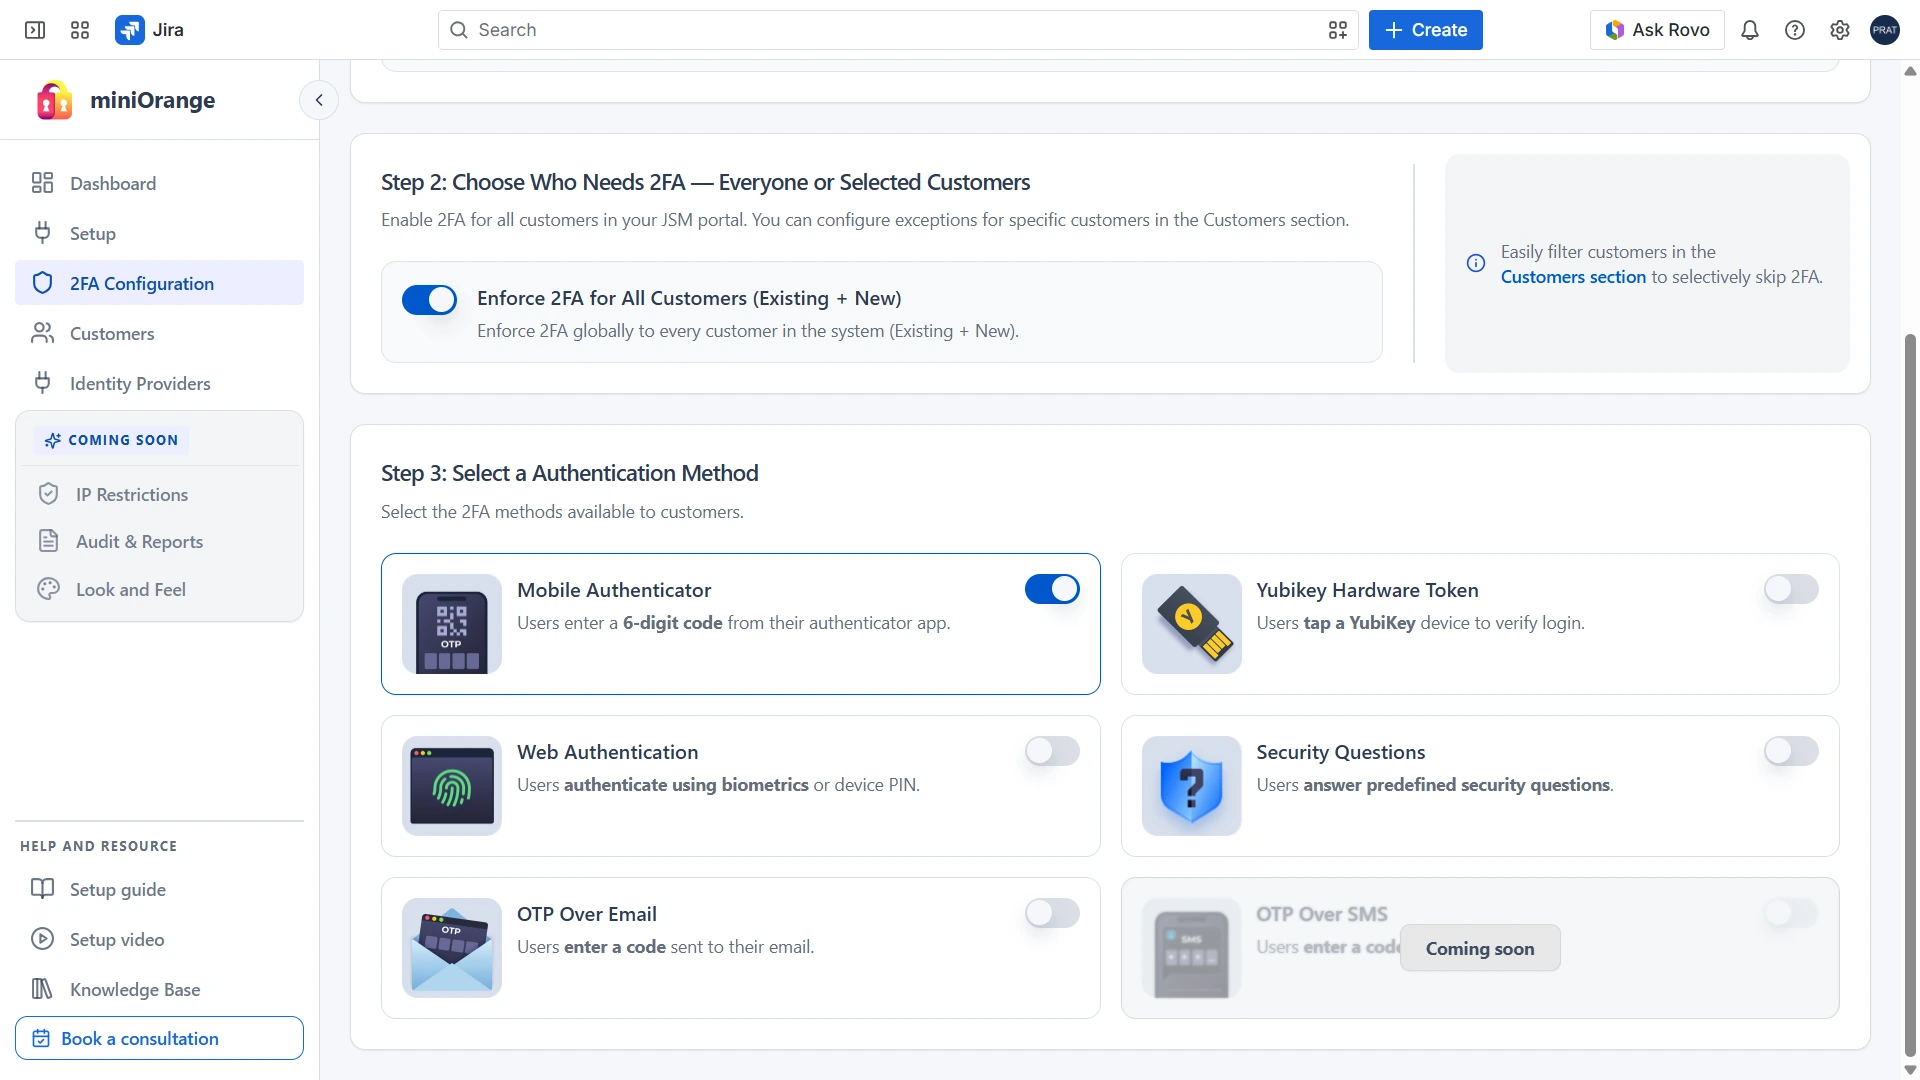
3. Select an Authentication Method
The miniOrange 2FA add-on offers a range of 2FA methods, including Web Authentication, KBA, TOTP, and more. Enable the methods you want from the provided list during configuration, simply select a 2FA method option and toggle it active to make it available to your users.
Users Tab
The Users tab is a centralized interface for managing Jira managed and external users and their 2FA settings, supporting both individual and bulk operations. It is organized into three sub-tabs:
- All Users
- 2FA Enabled Users
- 2FA Disabled Users
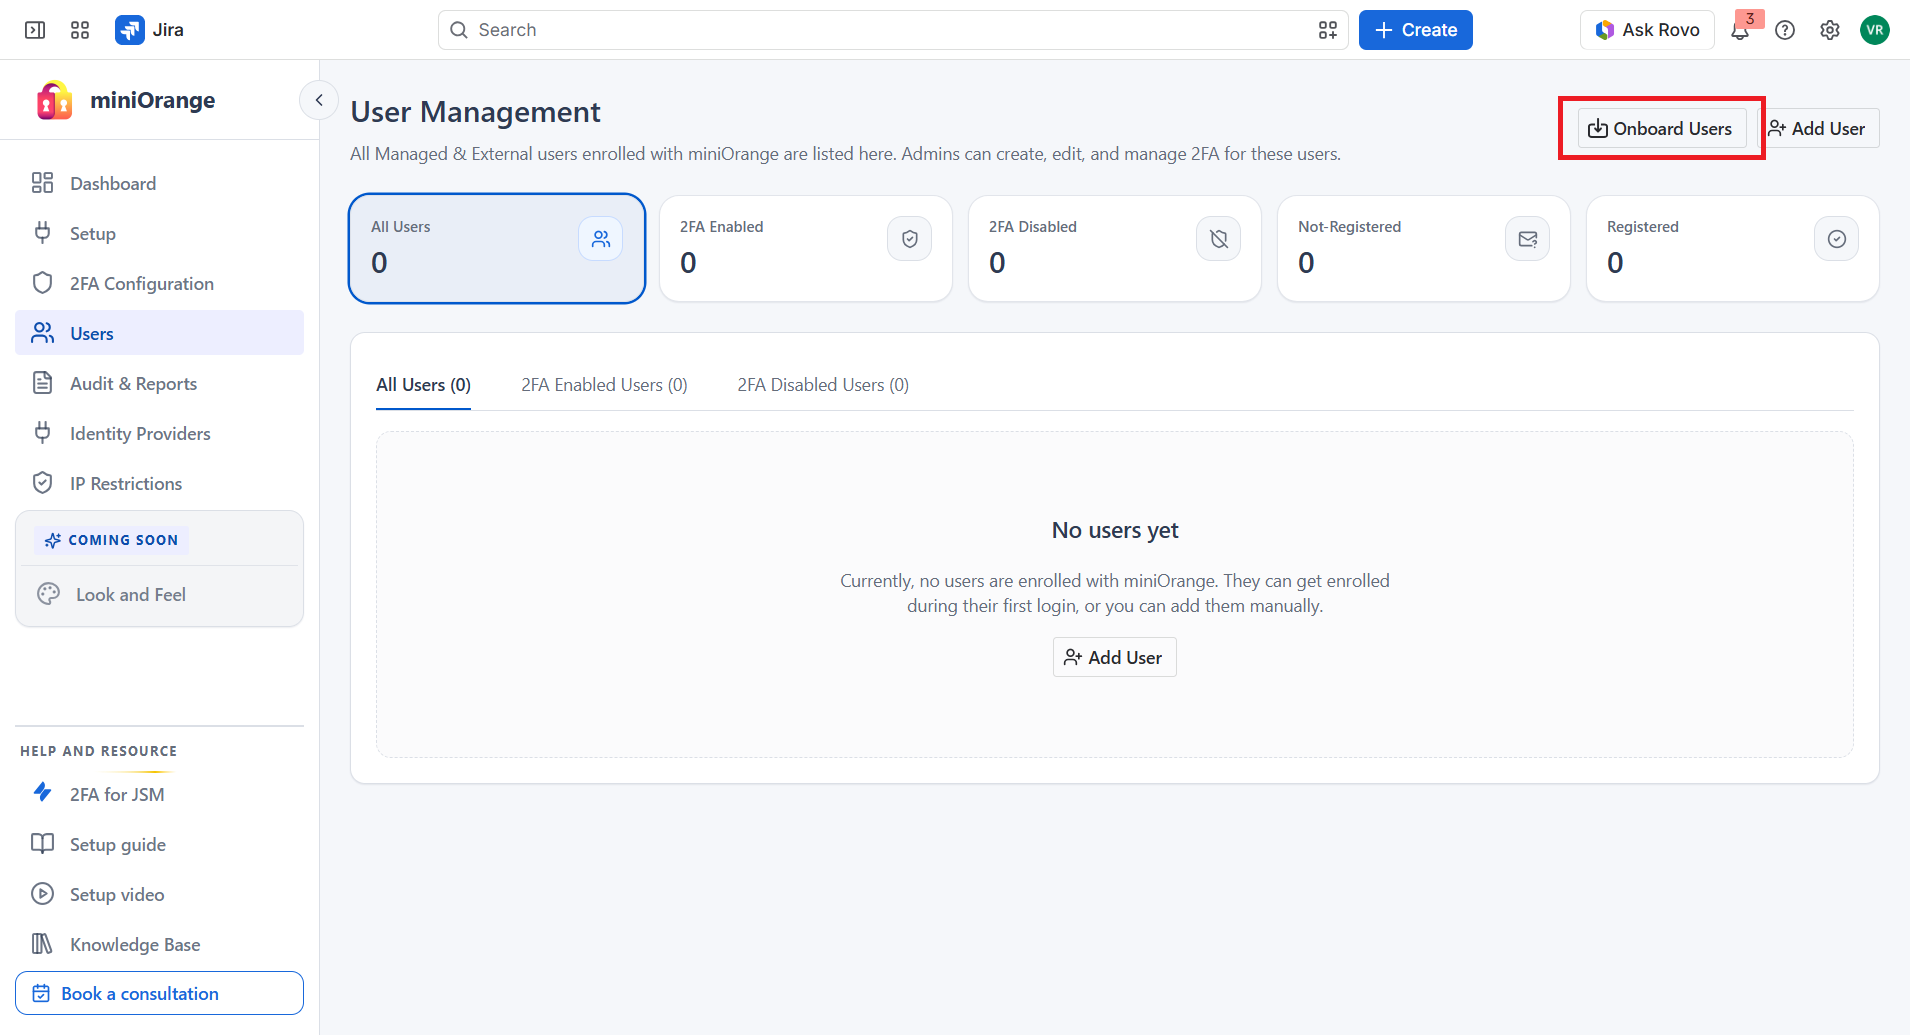
1. Onboard Users
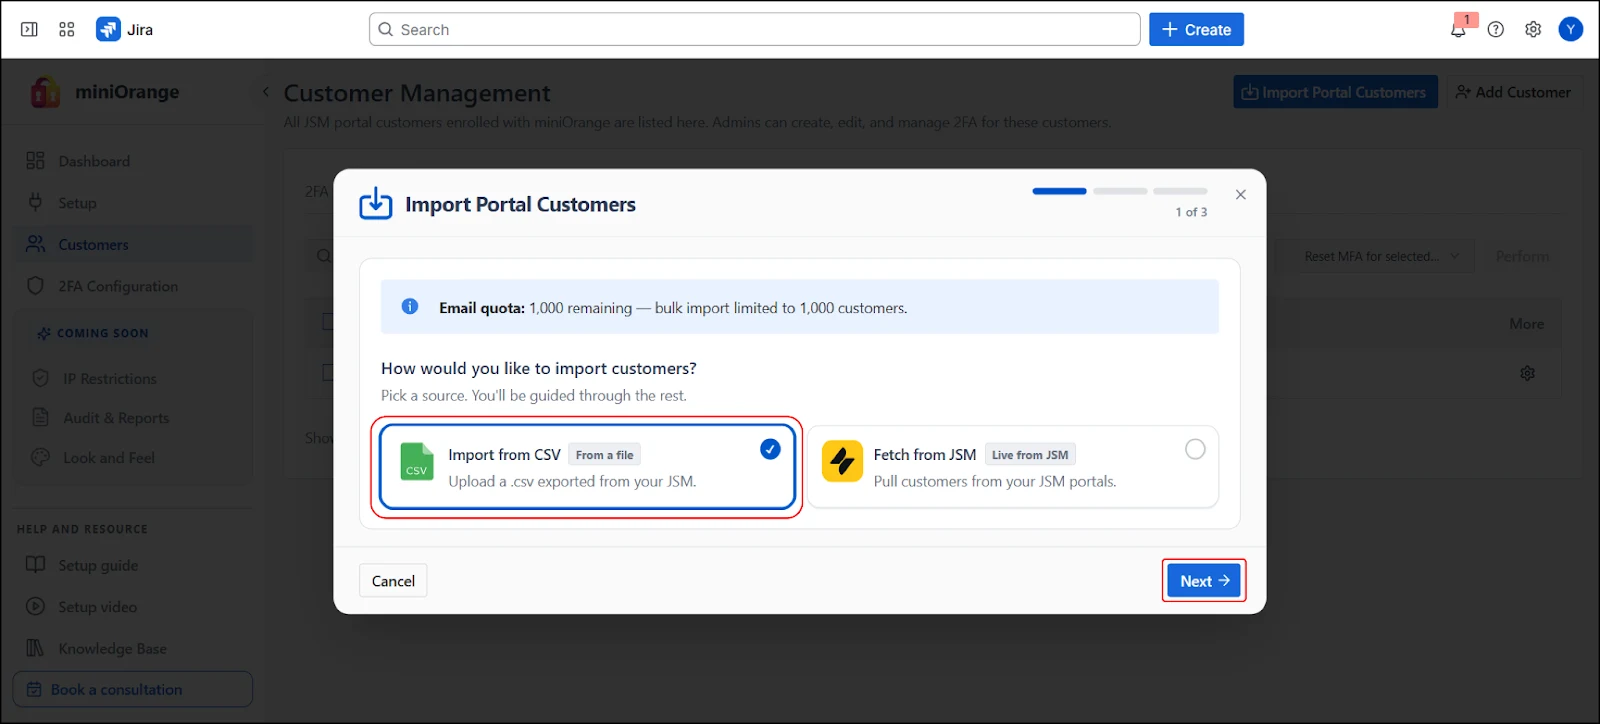
- Click Onboard Users in the Users tab. A step-based modal wizard opens.
- Choose an import method to proceed.
- Select Import from CSV and click Next.
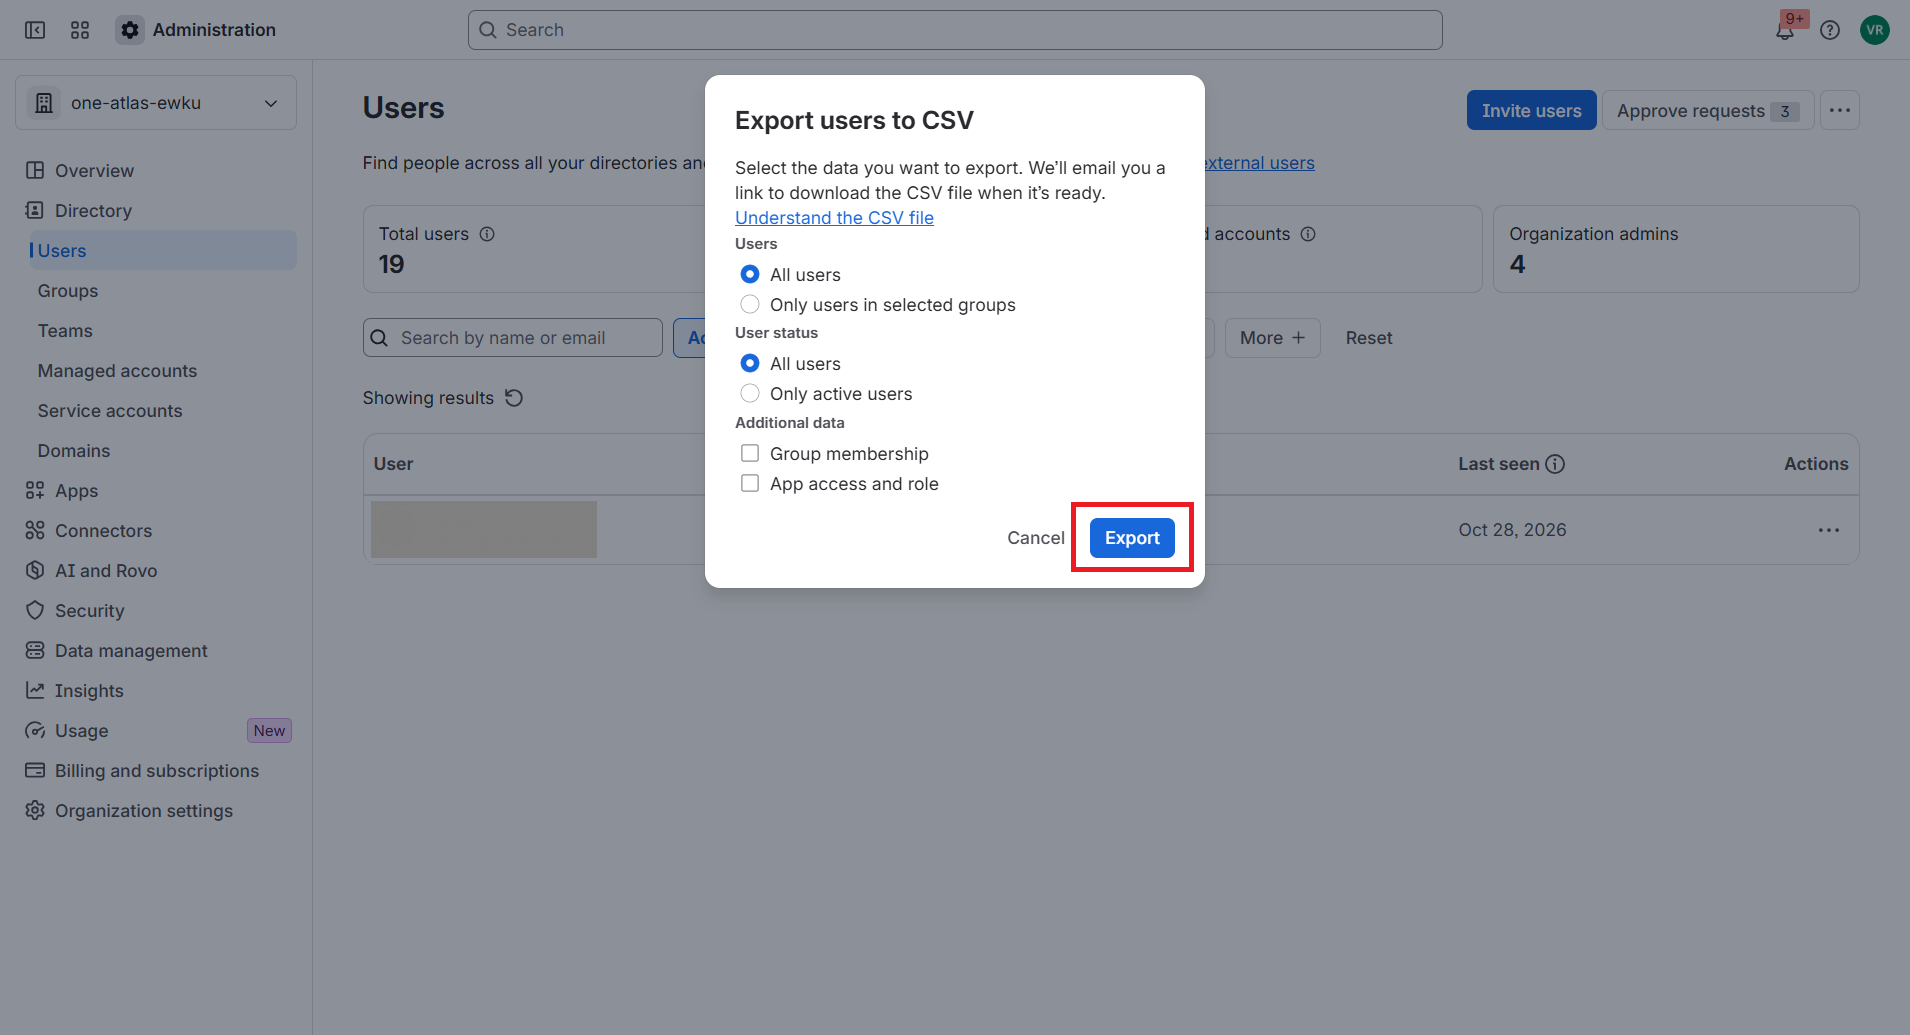
- Export the CSV:
- Open admin.atlassian.com, select your organization, then go to Directory → Users. Only an organization admin can export users.
- Open the ••• menu, select Export users, and export active users only.
- Atlassian emails you a download link. Open it and download the CSV file.
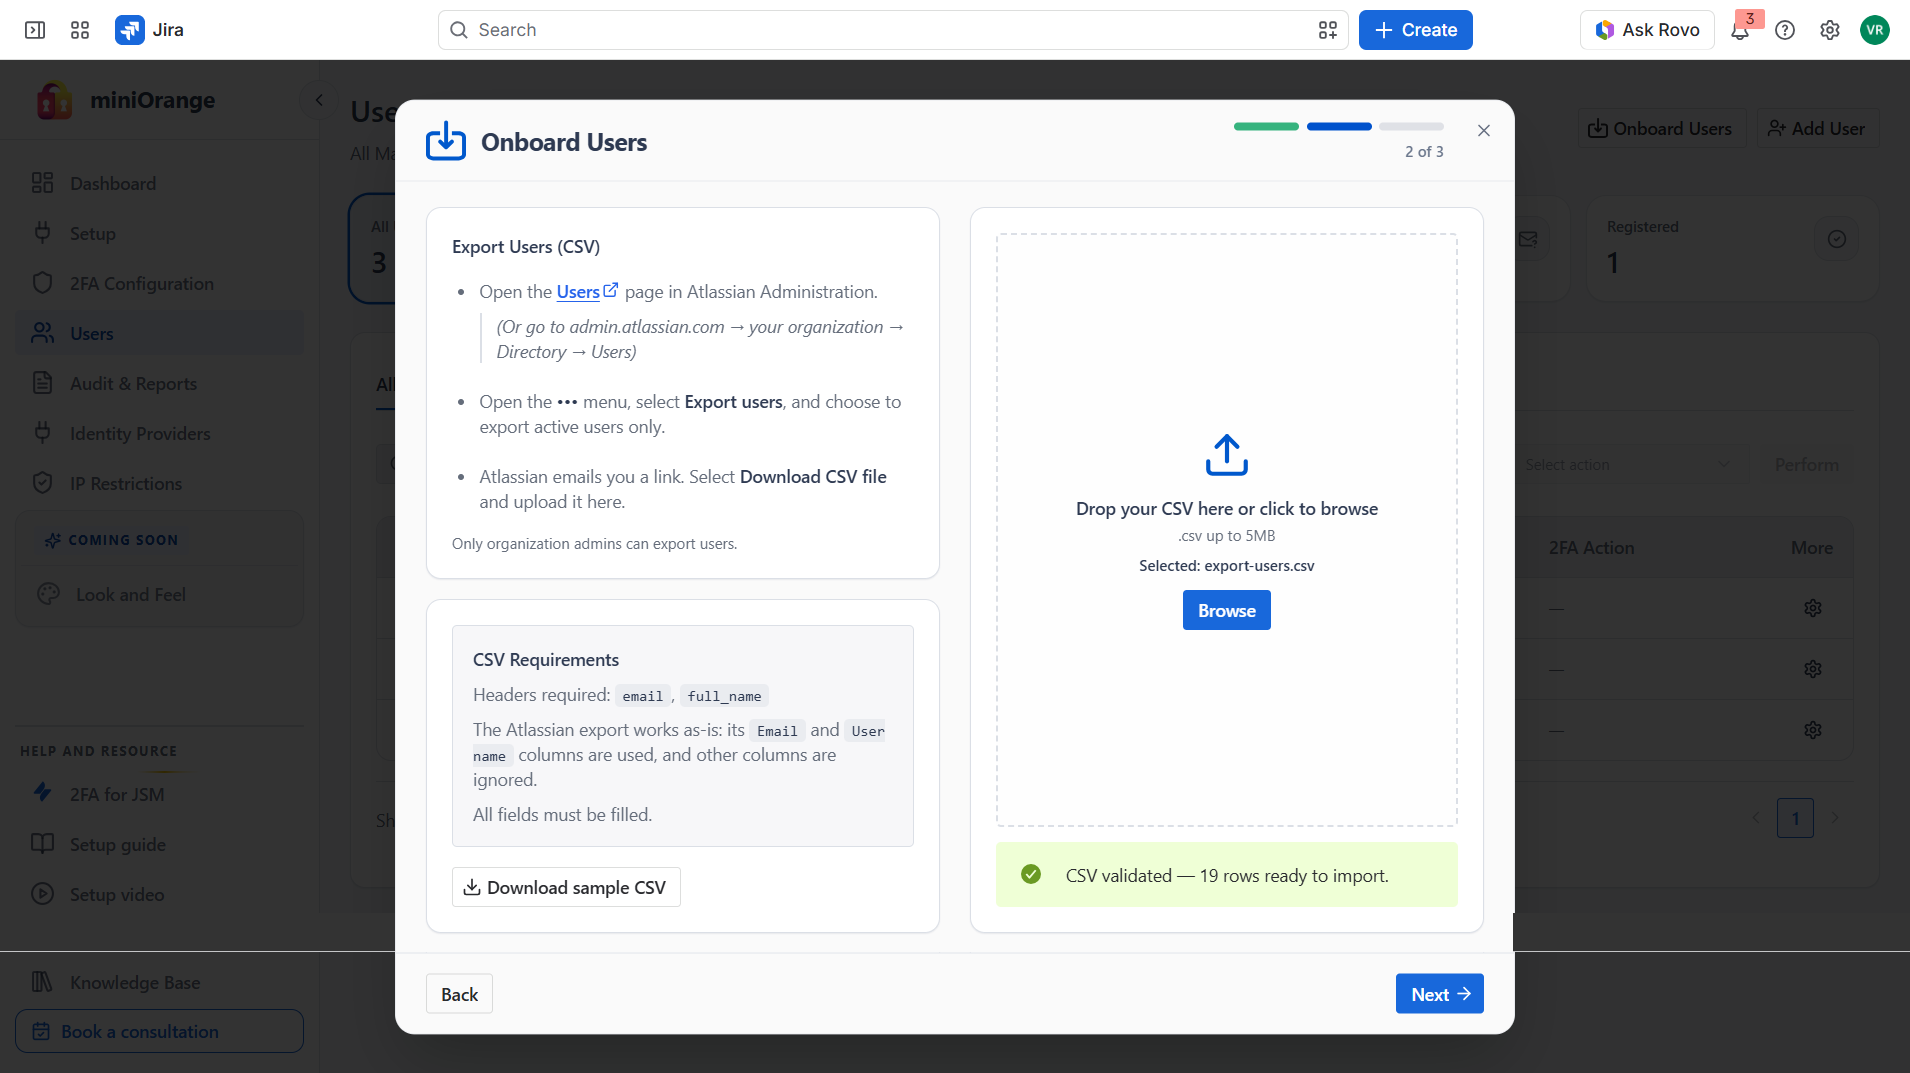
- Upload the CSV using drag-and-drop or the file browser in the Step 2 section, then proceed to the next step.
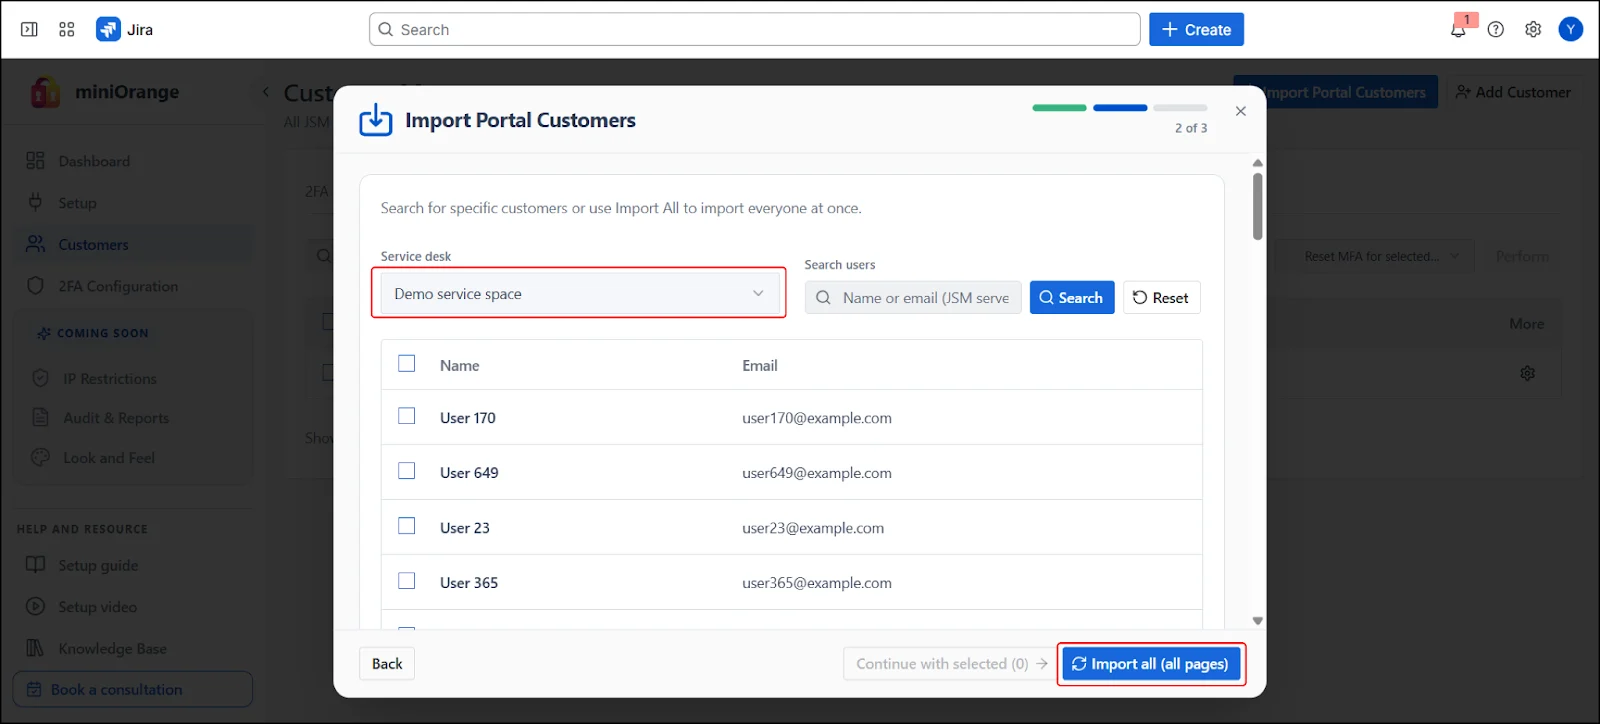
- Select Fetch from Atlassian.
- Leave Group set to All users, or choose a group.
- The user list is displayed in a table.
- Search by name or email when All users is selected. Search is not available after you choose a group.
- Select individual users using checkboxes.
- Select all users on the current page.
- Move between pages with Previous and Next.
-
Note: App accounts, JSM portal-only customers, and deactivated accounts are not listed. A user shown as Email unavailable cannot be selected. Use Import from CSV for that user.
-
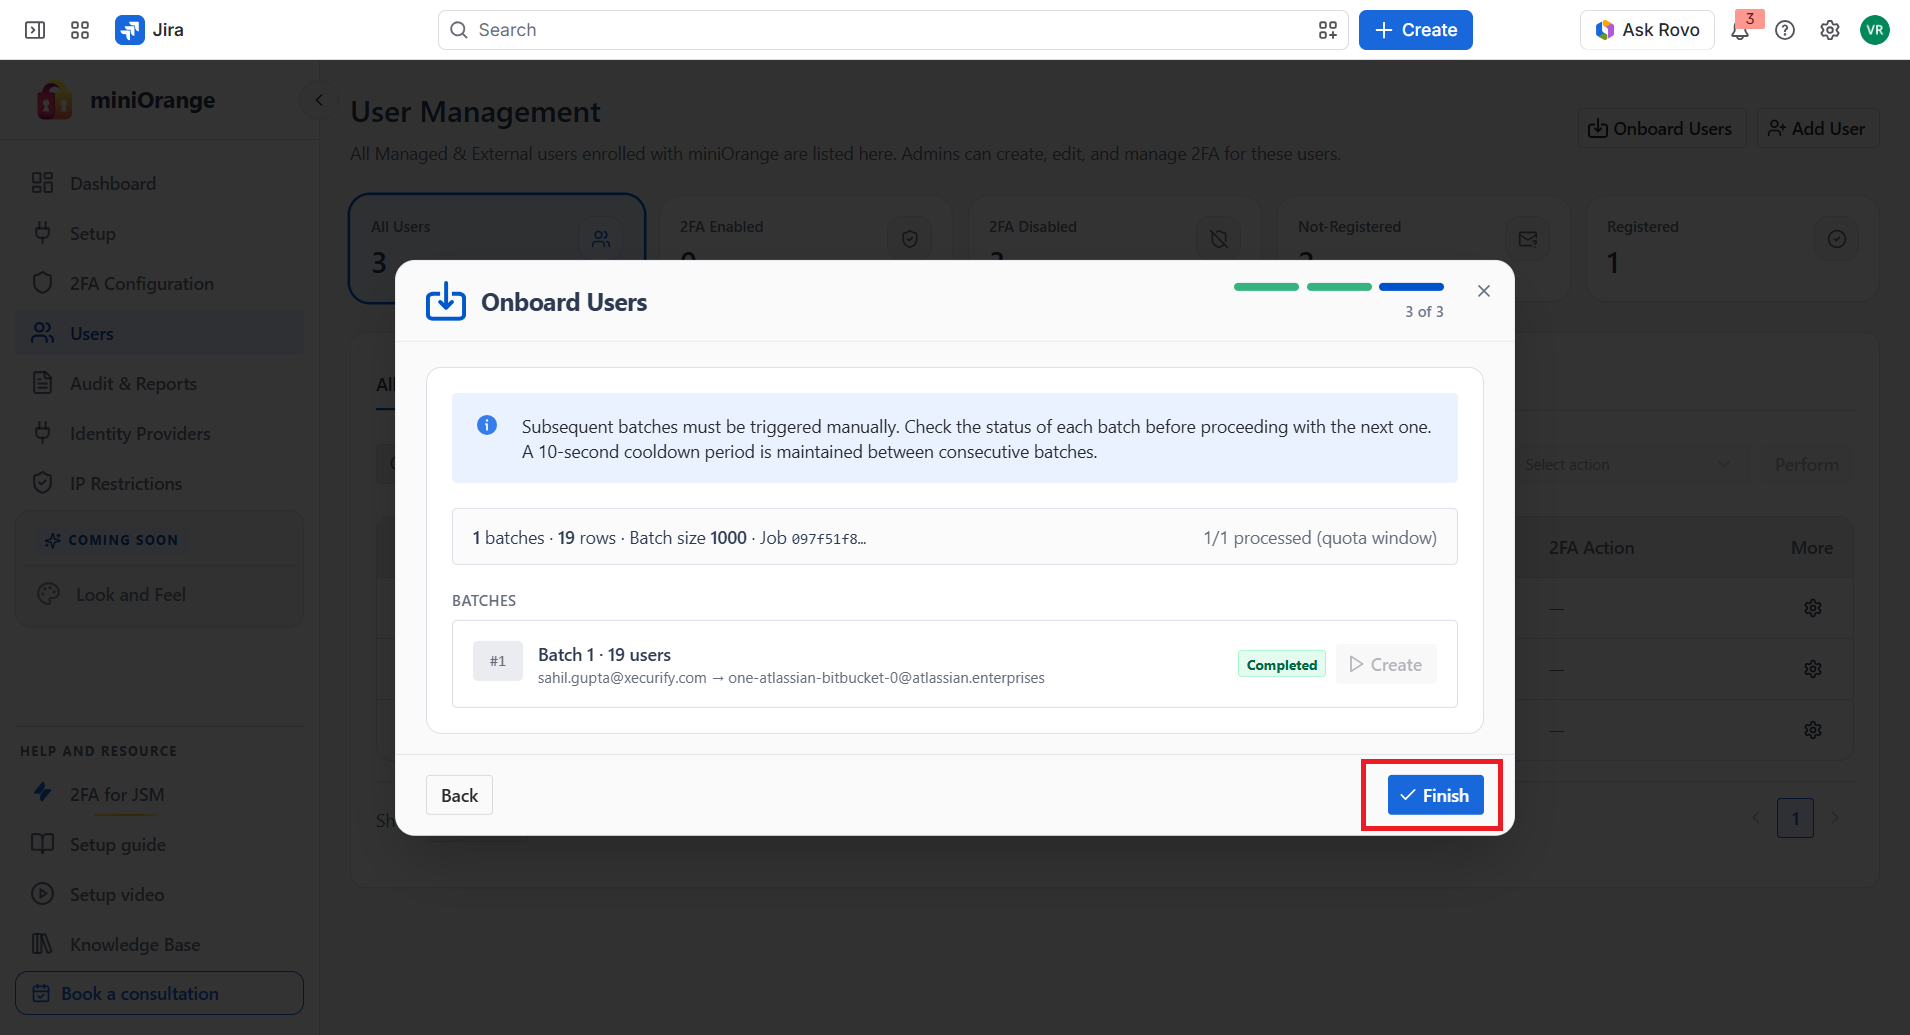
Note: This step is common to both import options.
- Click Create next to each batch and wait for it to finish before starting the next one.
- When every batch has finished, click Finish.
Option 1: Import from CSV
Upload a CSV file exported from Atlassian Administration.
Option 2: Fetch from Atlassian
Use this to pull users directly from your Atlassian instance.
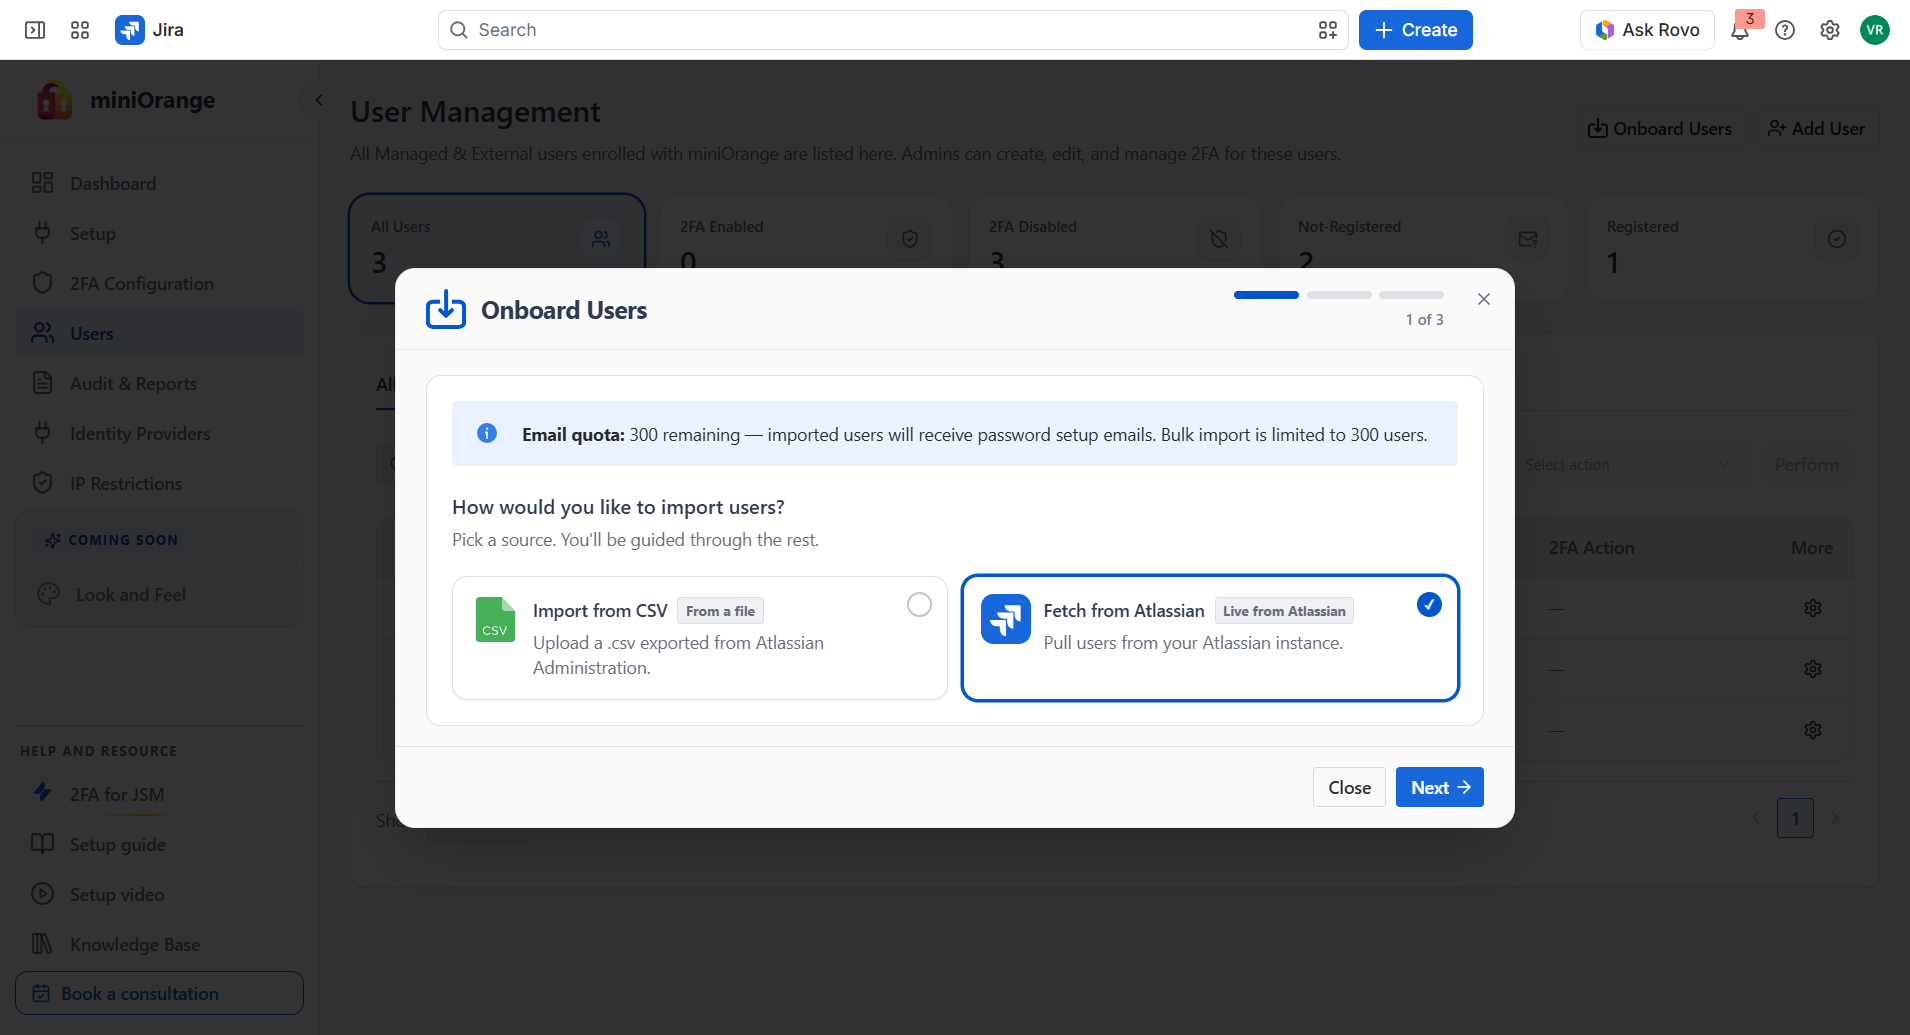
From the fetched list you can:
Click Continue with selected to import the users you checked, or click Import all to import everyone in the current list.
Create the users
2. Add Users Manually
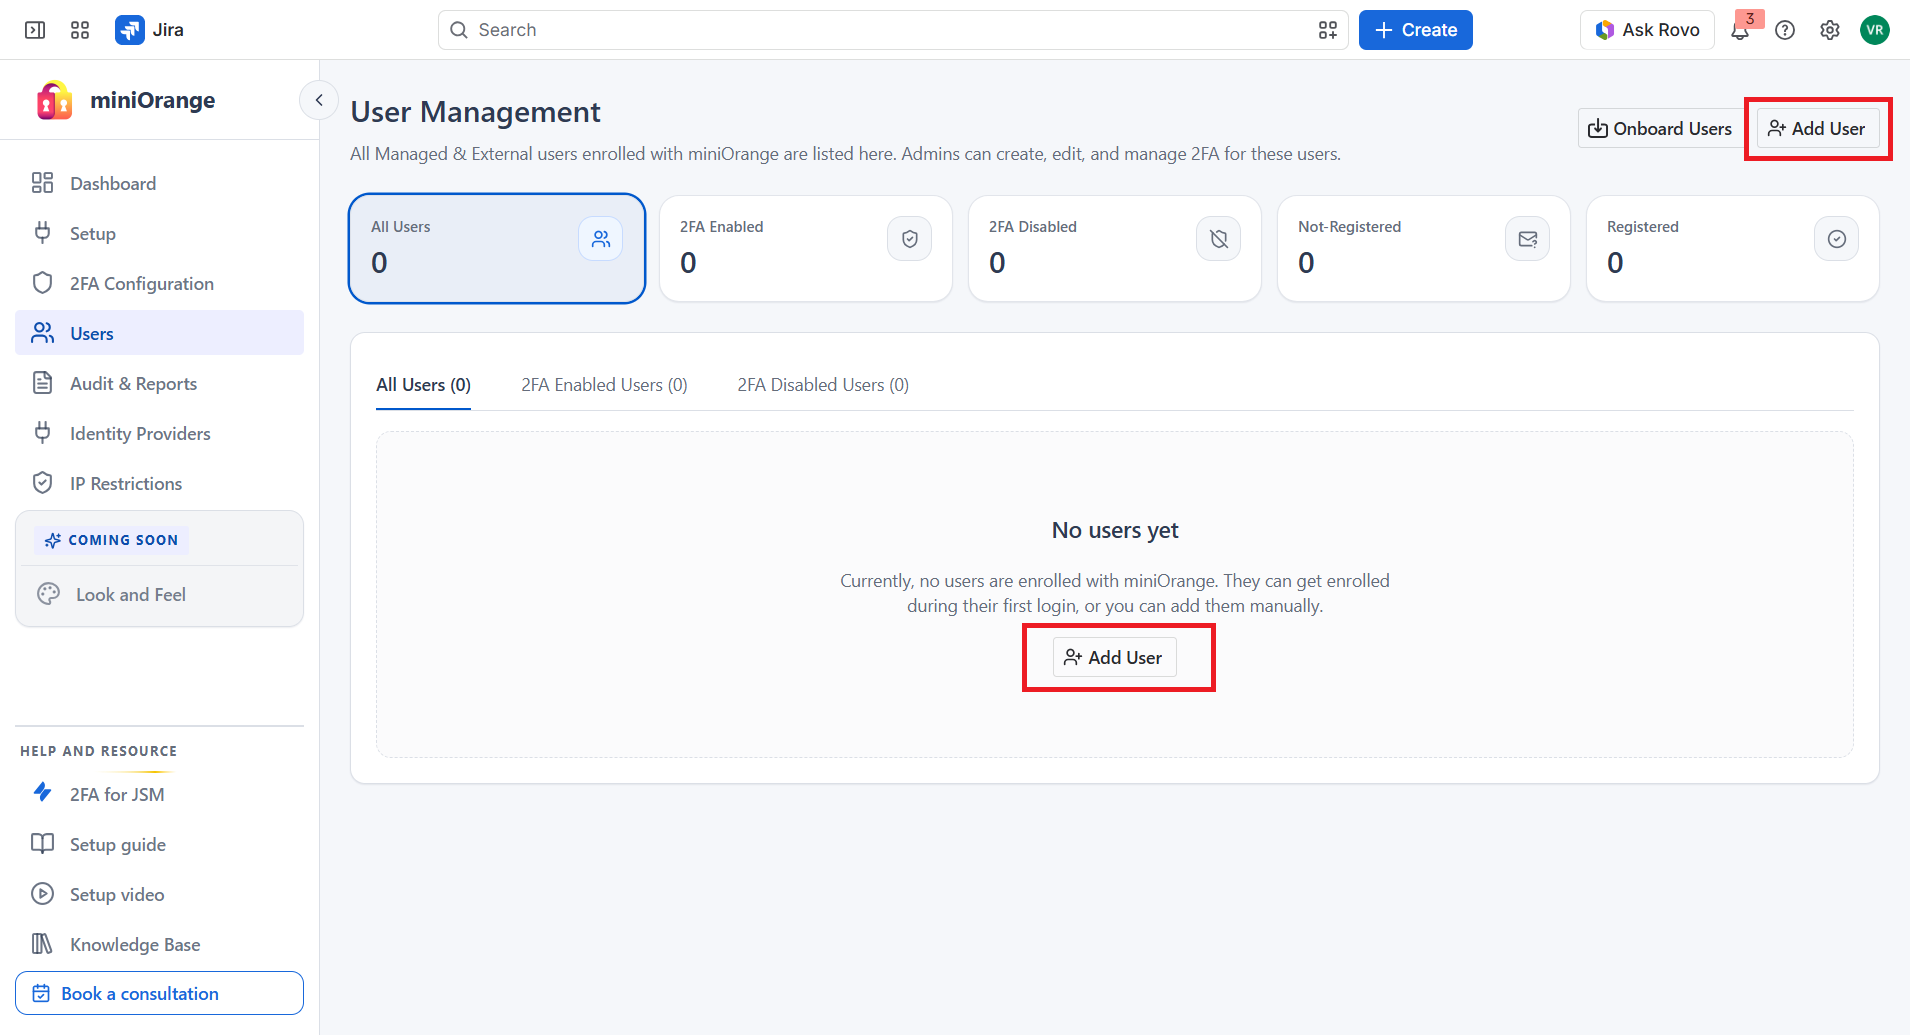
- Click Add User in the Users tab. A modal form appears.
- Fill in the required fields: First Name, Email (used for communication and authentication), Username, and Password (optional).
- Click Create User to complete the form.
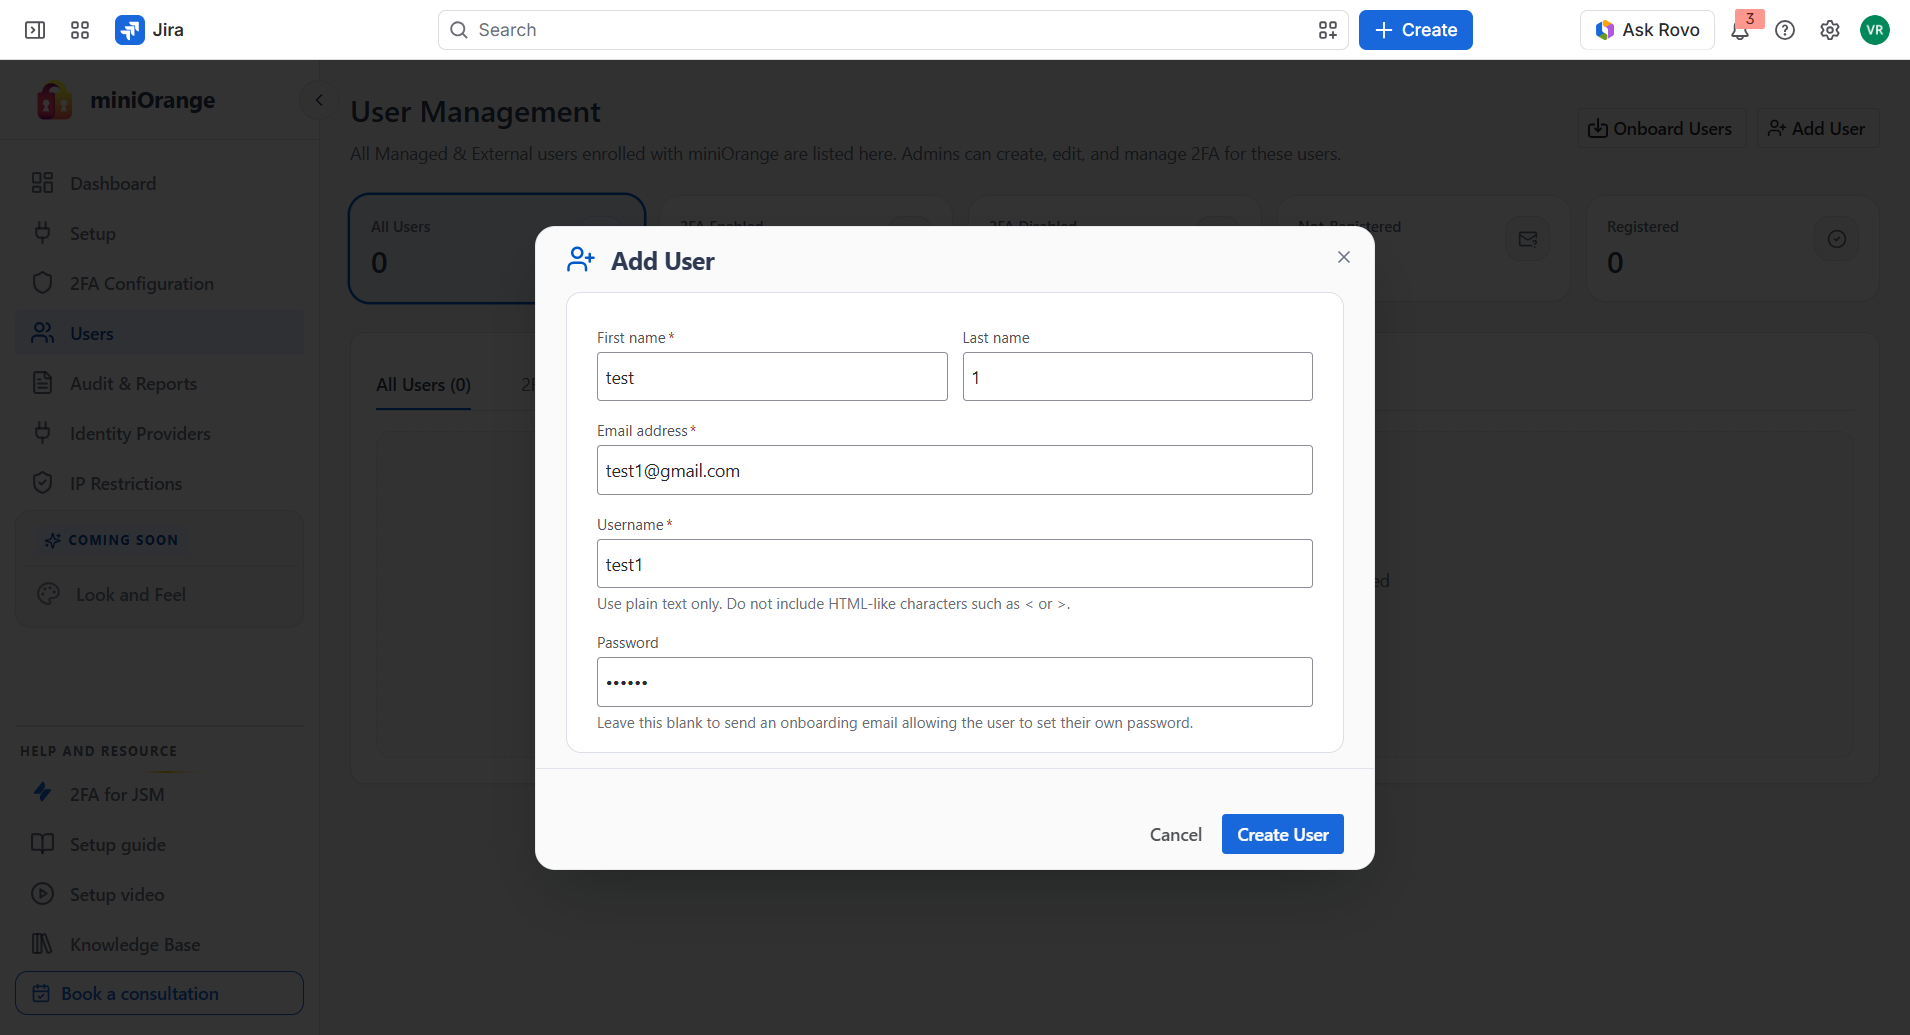
Password behavior:
- If you enter a password, the user is created with that password.
- If the password is left blank, the user receives an onboarding email to set their own password.
After creation, the user appears under All Users , as well as under either 2FA Enabled or 2FA Disabled based on your MFA configuration.
3. View and Filter Users
Users are organized into three sub-tabs:
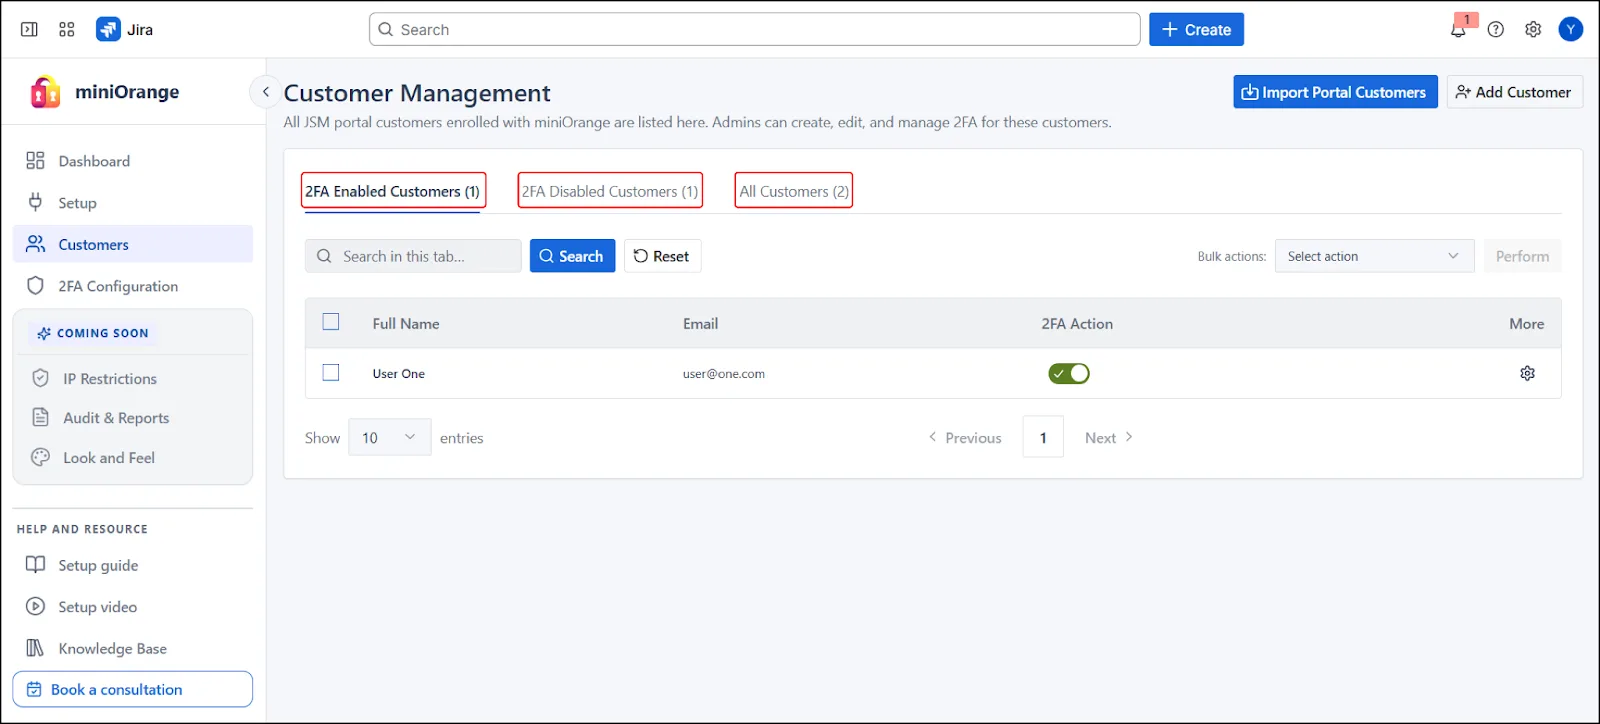
- 2FA Enabled Users , all users who currently have 2FA enabled. Helps monitor secured users and allows disabling 2FA for specific users if required.
- 2FA Disabled Users , all users without 2FA. Useful for identifying unprotected users and enabling 2FA individually or in bulk.
- All users, lists all users regardless of 2FA status, with a Fetch Status option to view each user's current 2FA state.
- On All Users, use Account Status to show All, Registered, or Not-Registered.
- Registered Users: Users who have completed setting up their accounts.
- Not Registered: Users who have been added but have not yet completed registration.
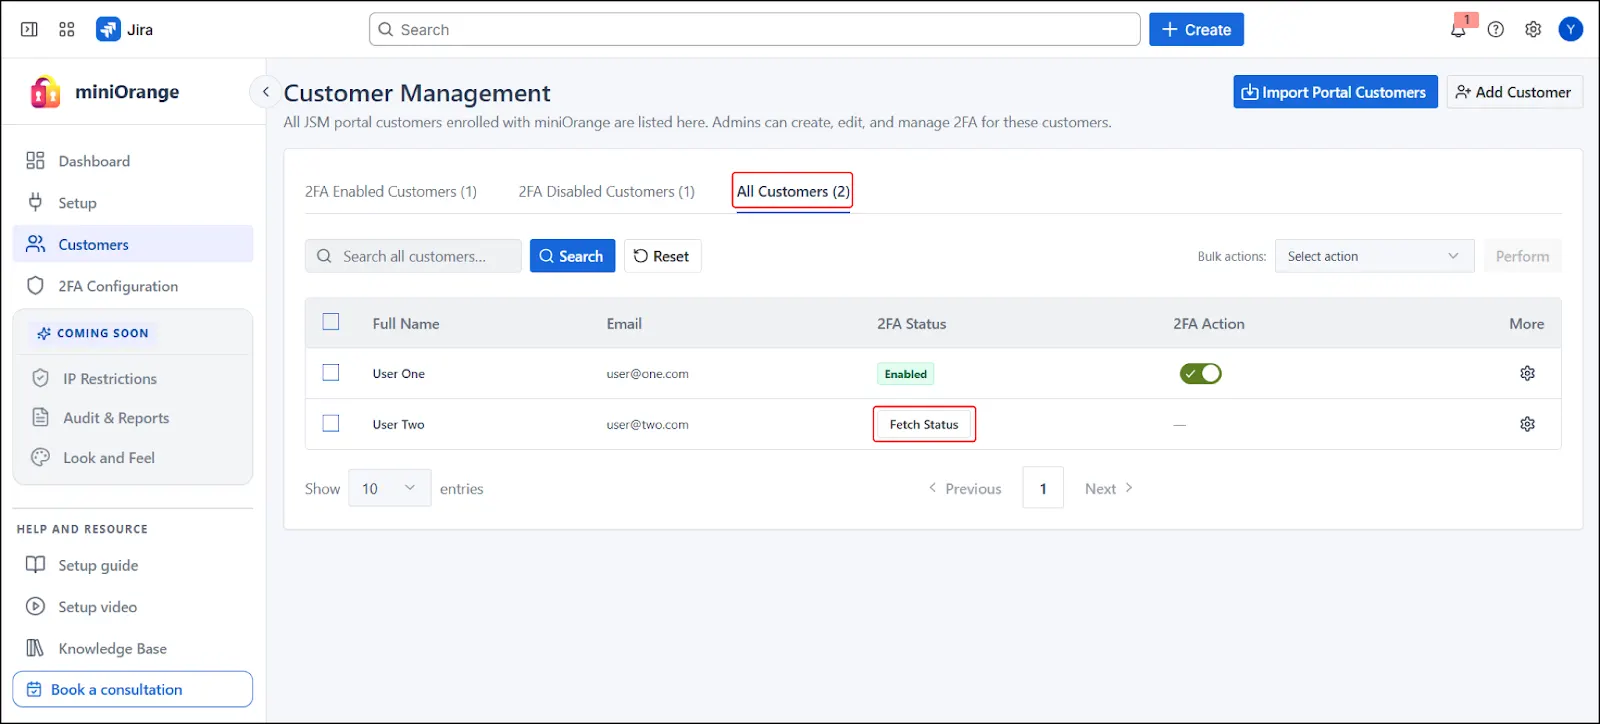
4. Enable or Disable 2FA
2FA management is available from all three sub-tabs; the available actions depend on the selected tab and the user's current state.
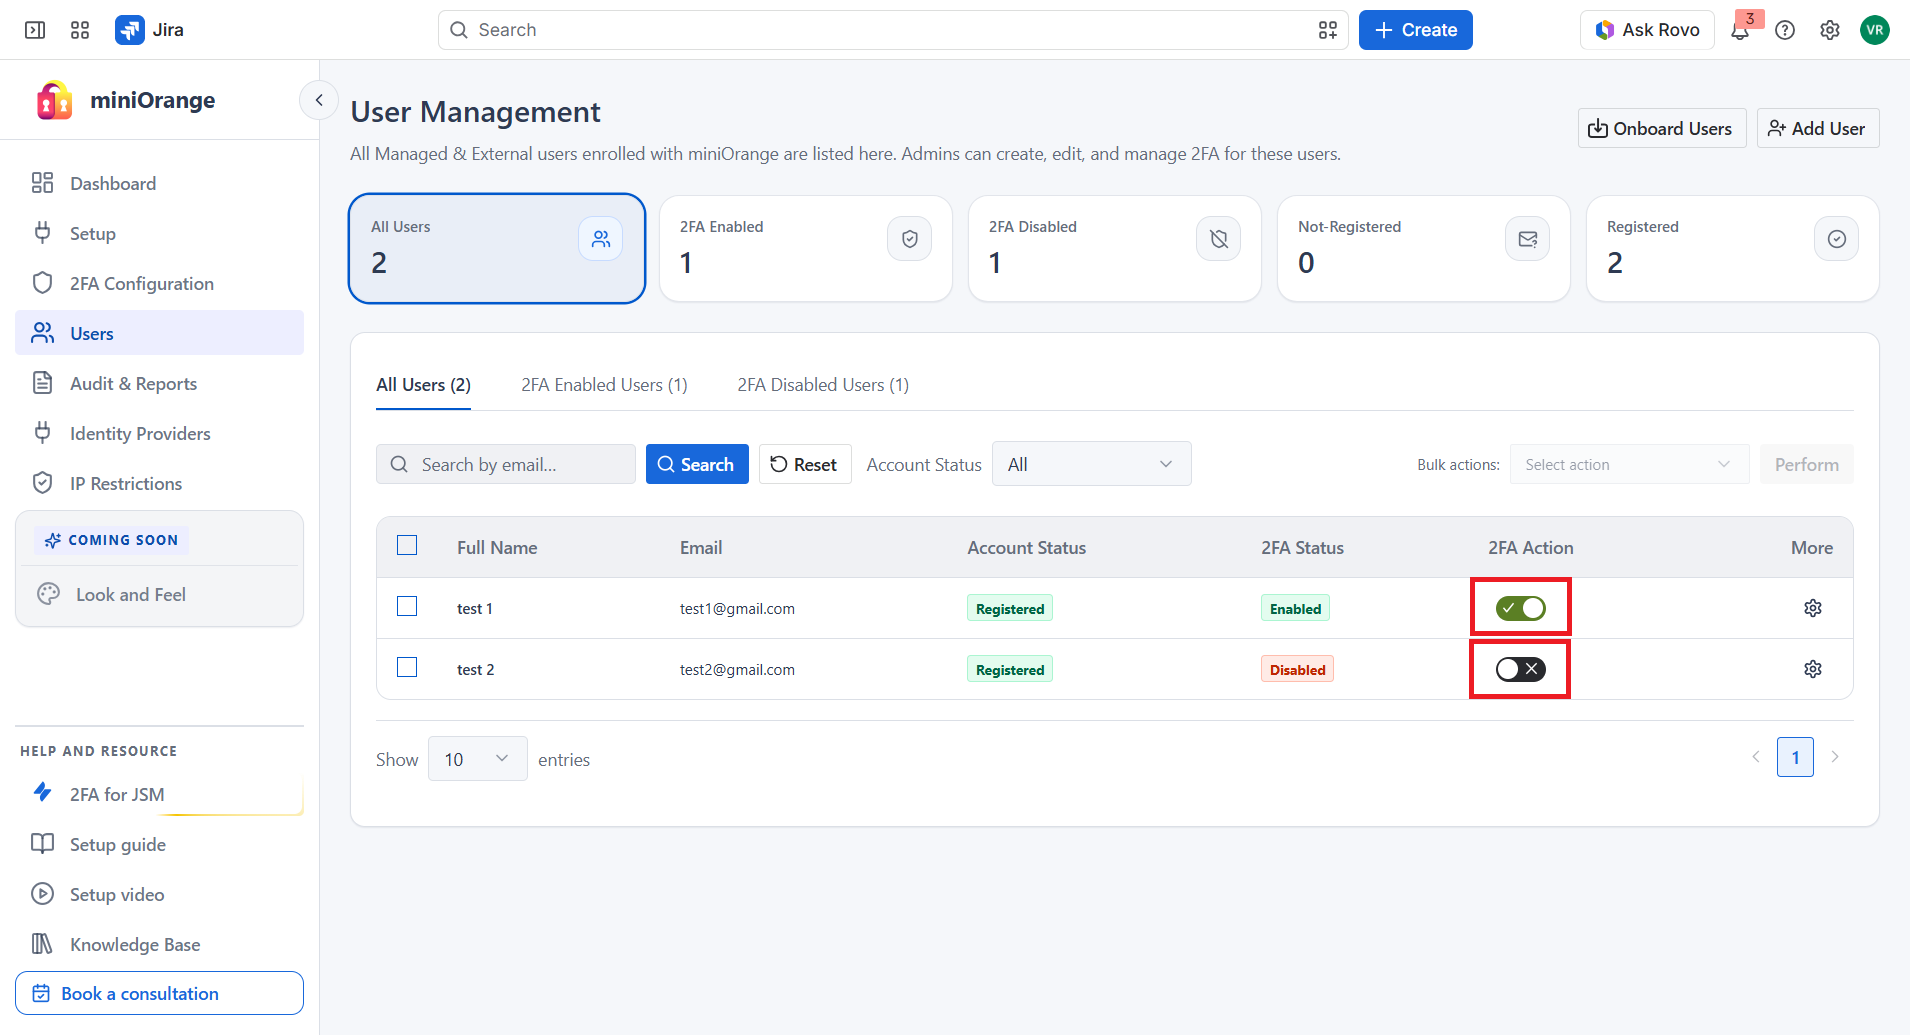
Individual users
Use the toggle switch under the 2FA Action column to control 2FA for each user, toggle ON to enable, OFF to disable.
Multiple users (Bulk Actions)
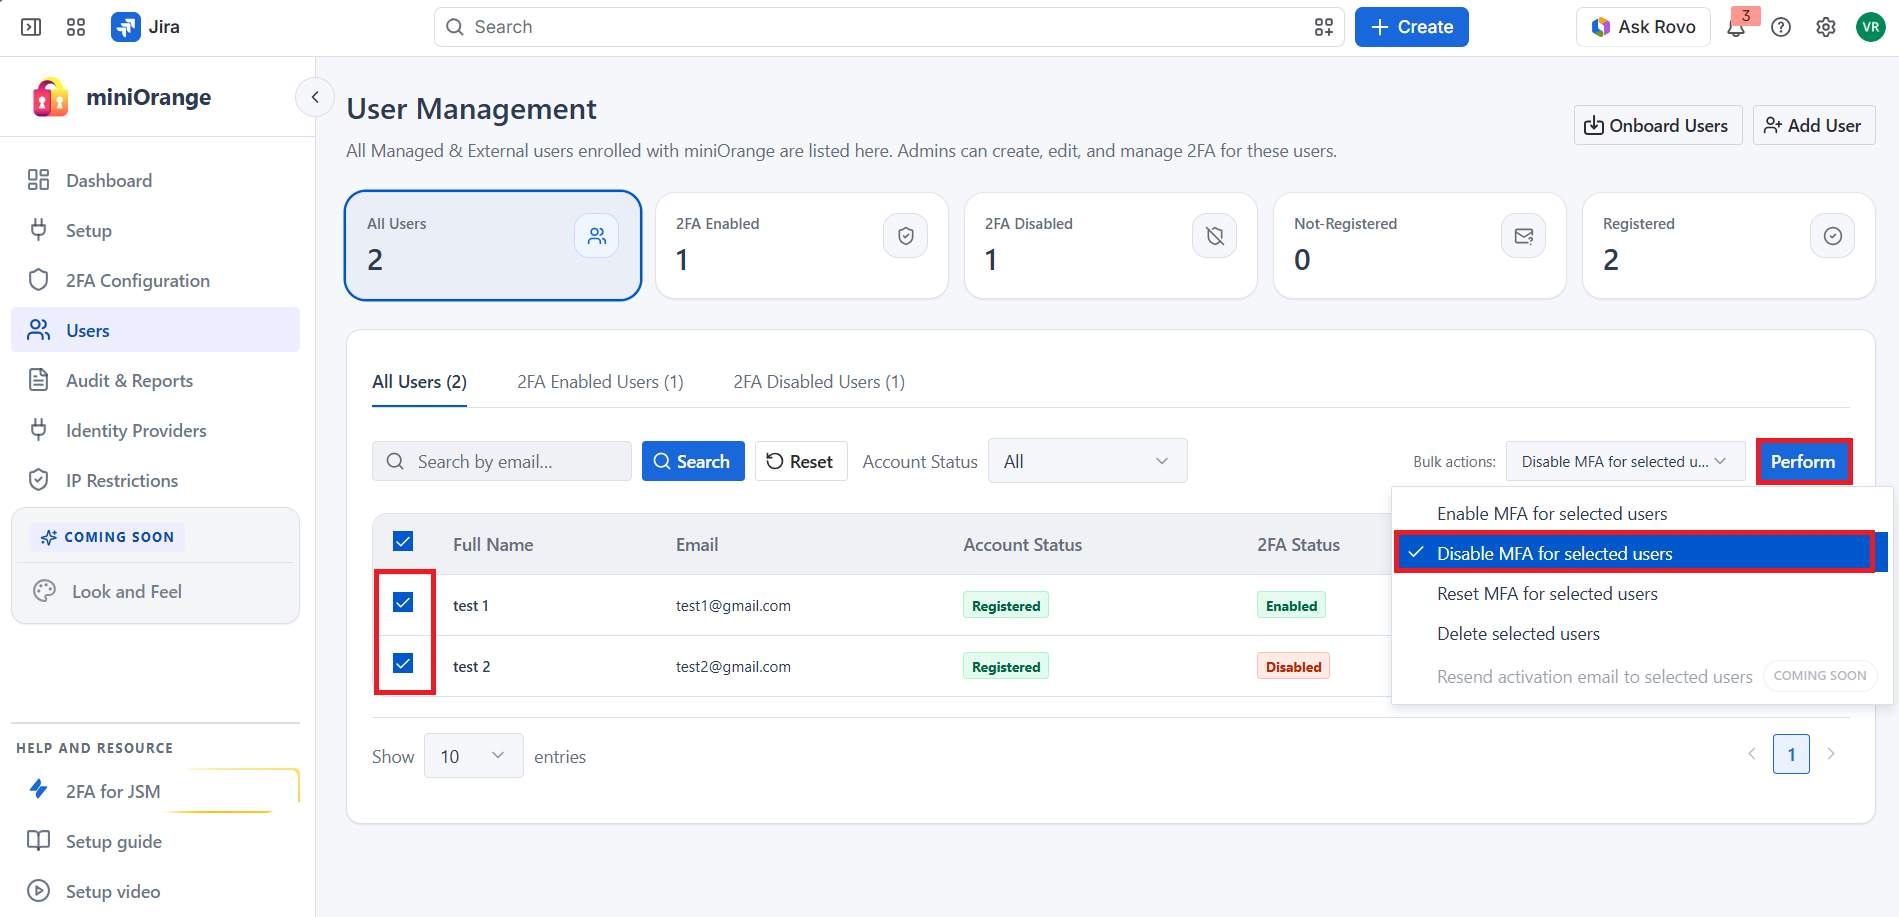
- Select users using the checkboxes.
- Choose an action from the Bulk Actions dropdown.
- Click Perform.
To prevent invalid operations, actions are restricted by tab:
- 2FA Enabled users tab, only Disable 2FA is available.
- 2FA Disabled users tab, only Enable 2FA is available.
- All users tab, both Enable and Disable are available, after fetching 2FA status.
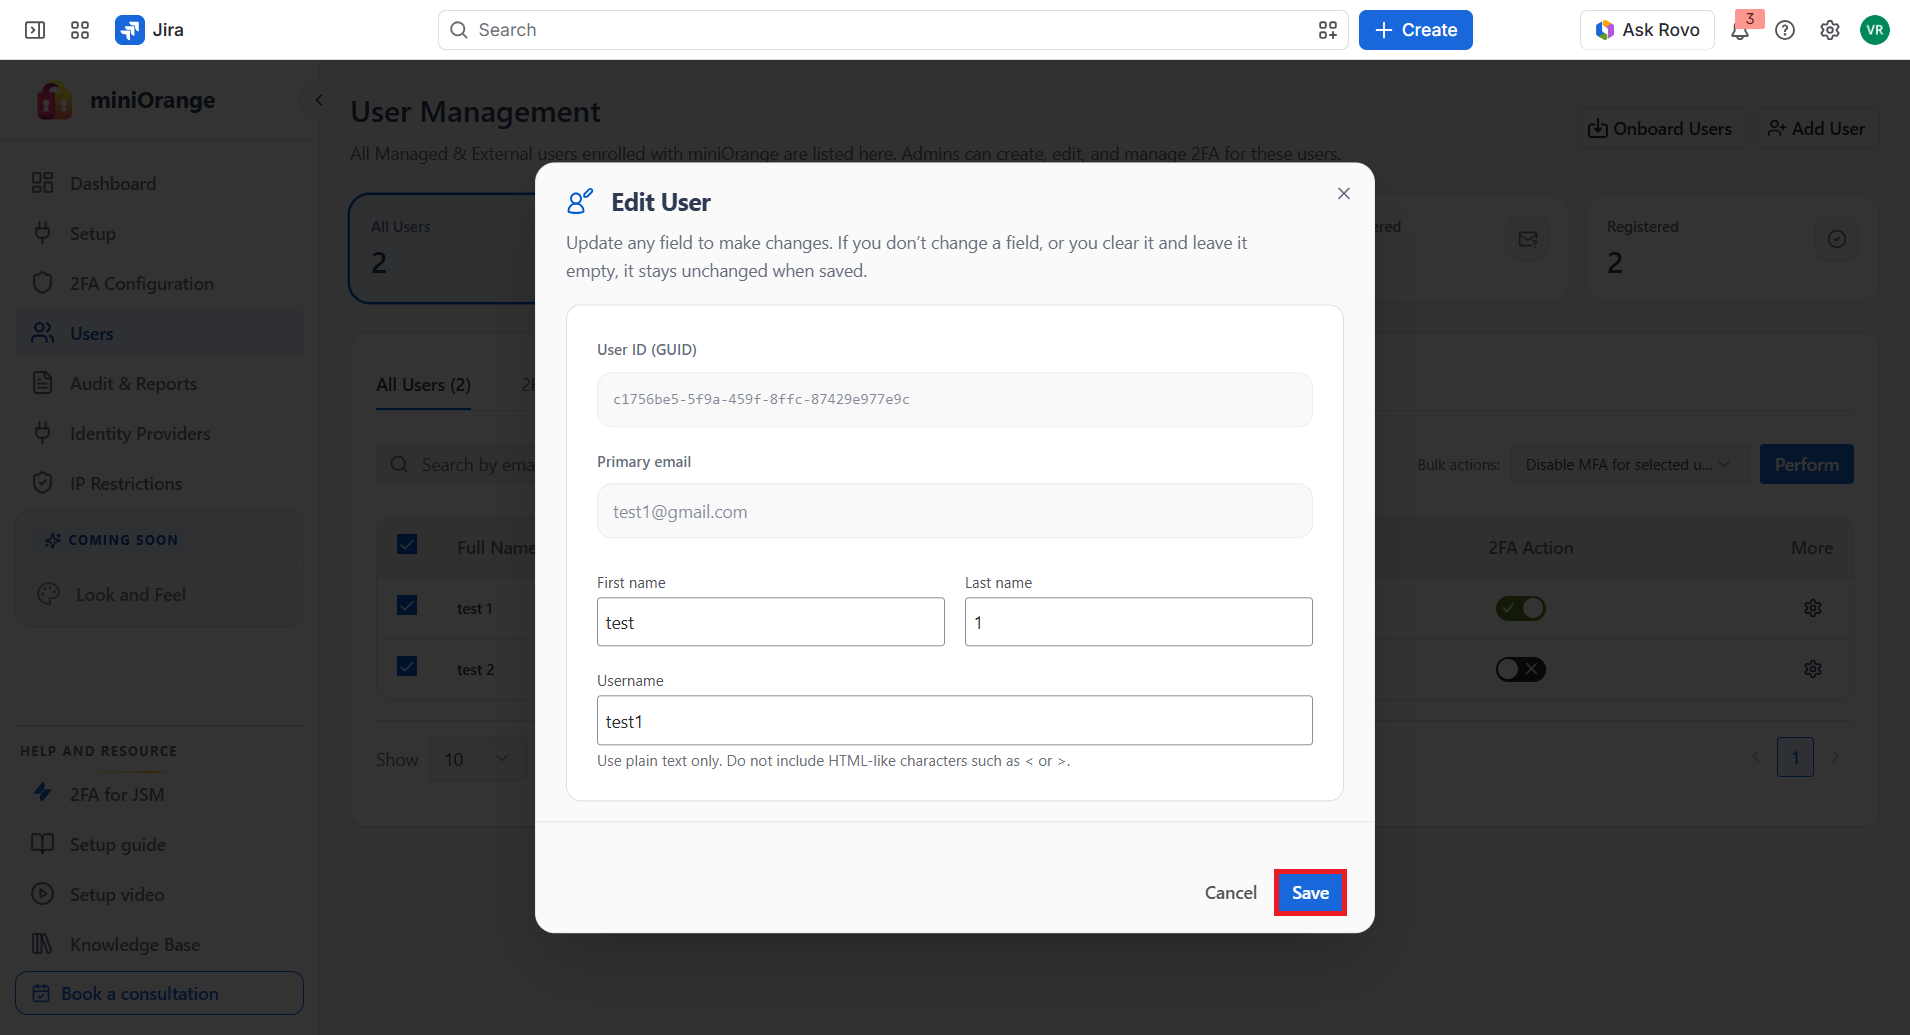
5. Edit user Details
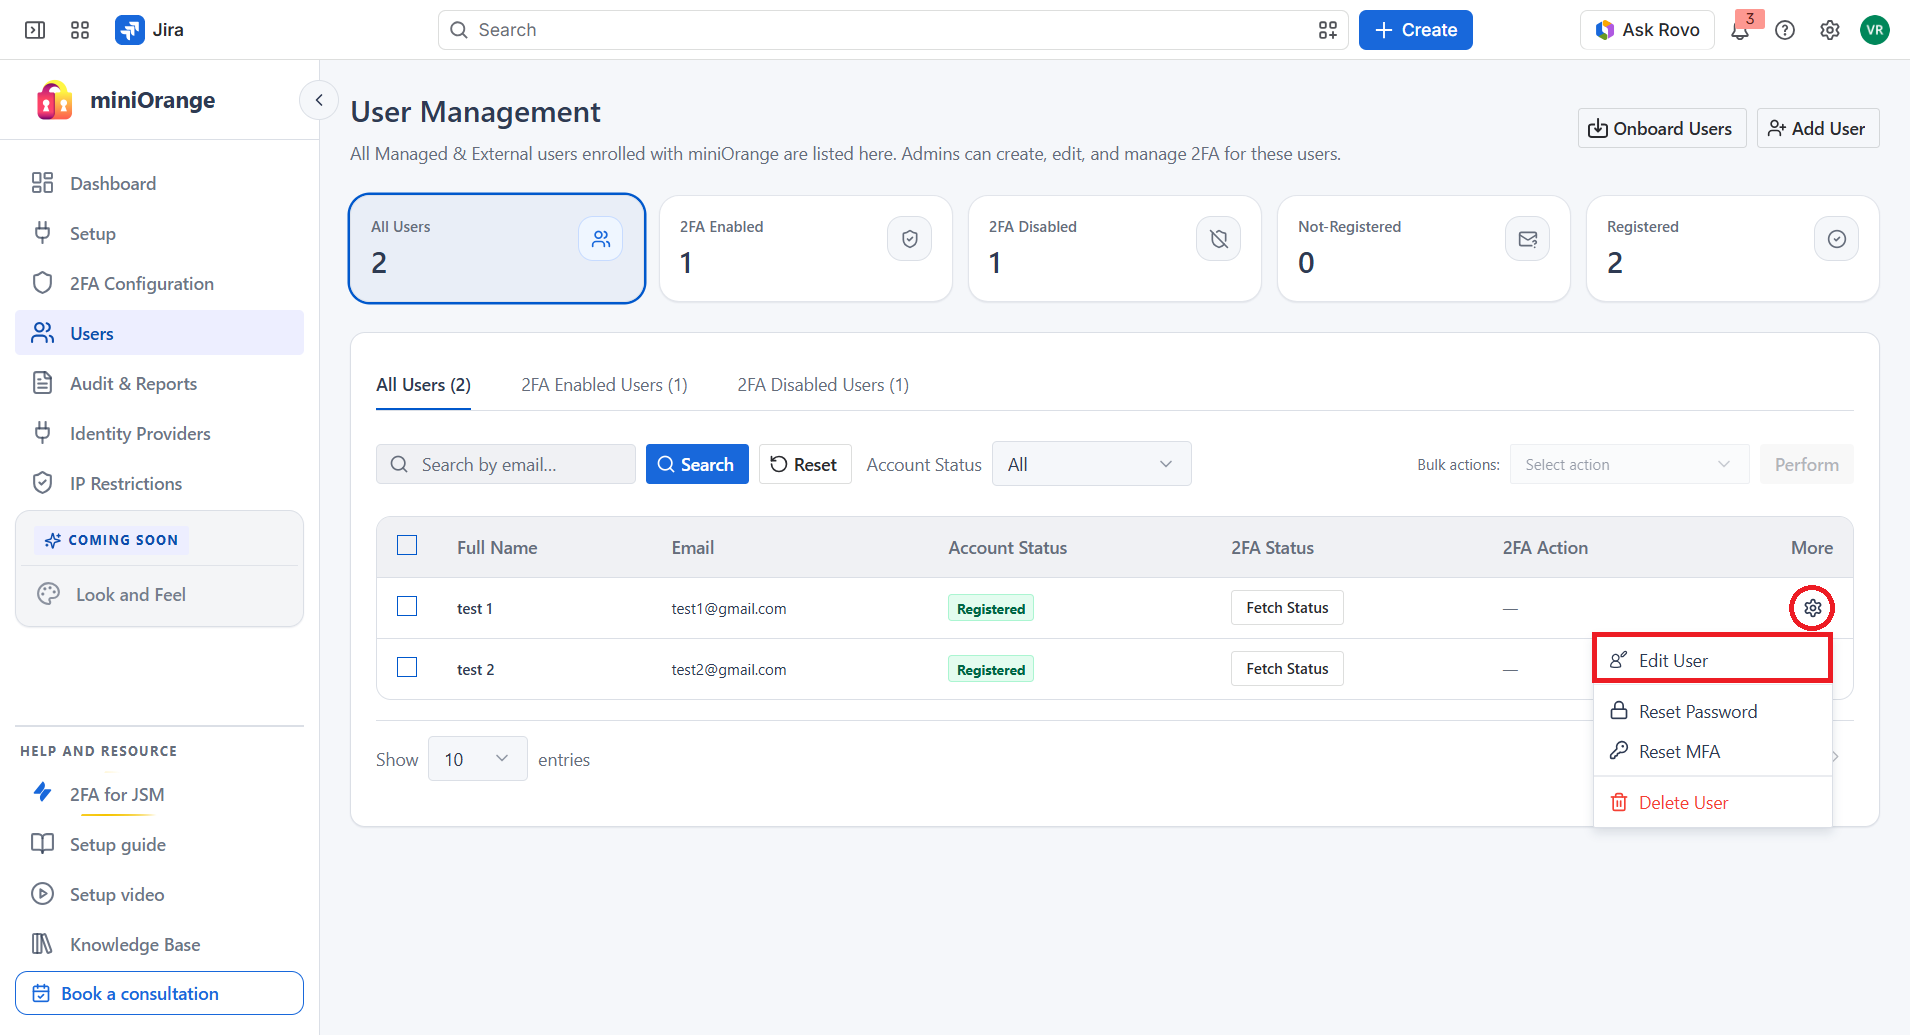
- Select the settings (⚙️) icon next to a user entry.
- Choose Edit user and update the required fields.
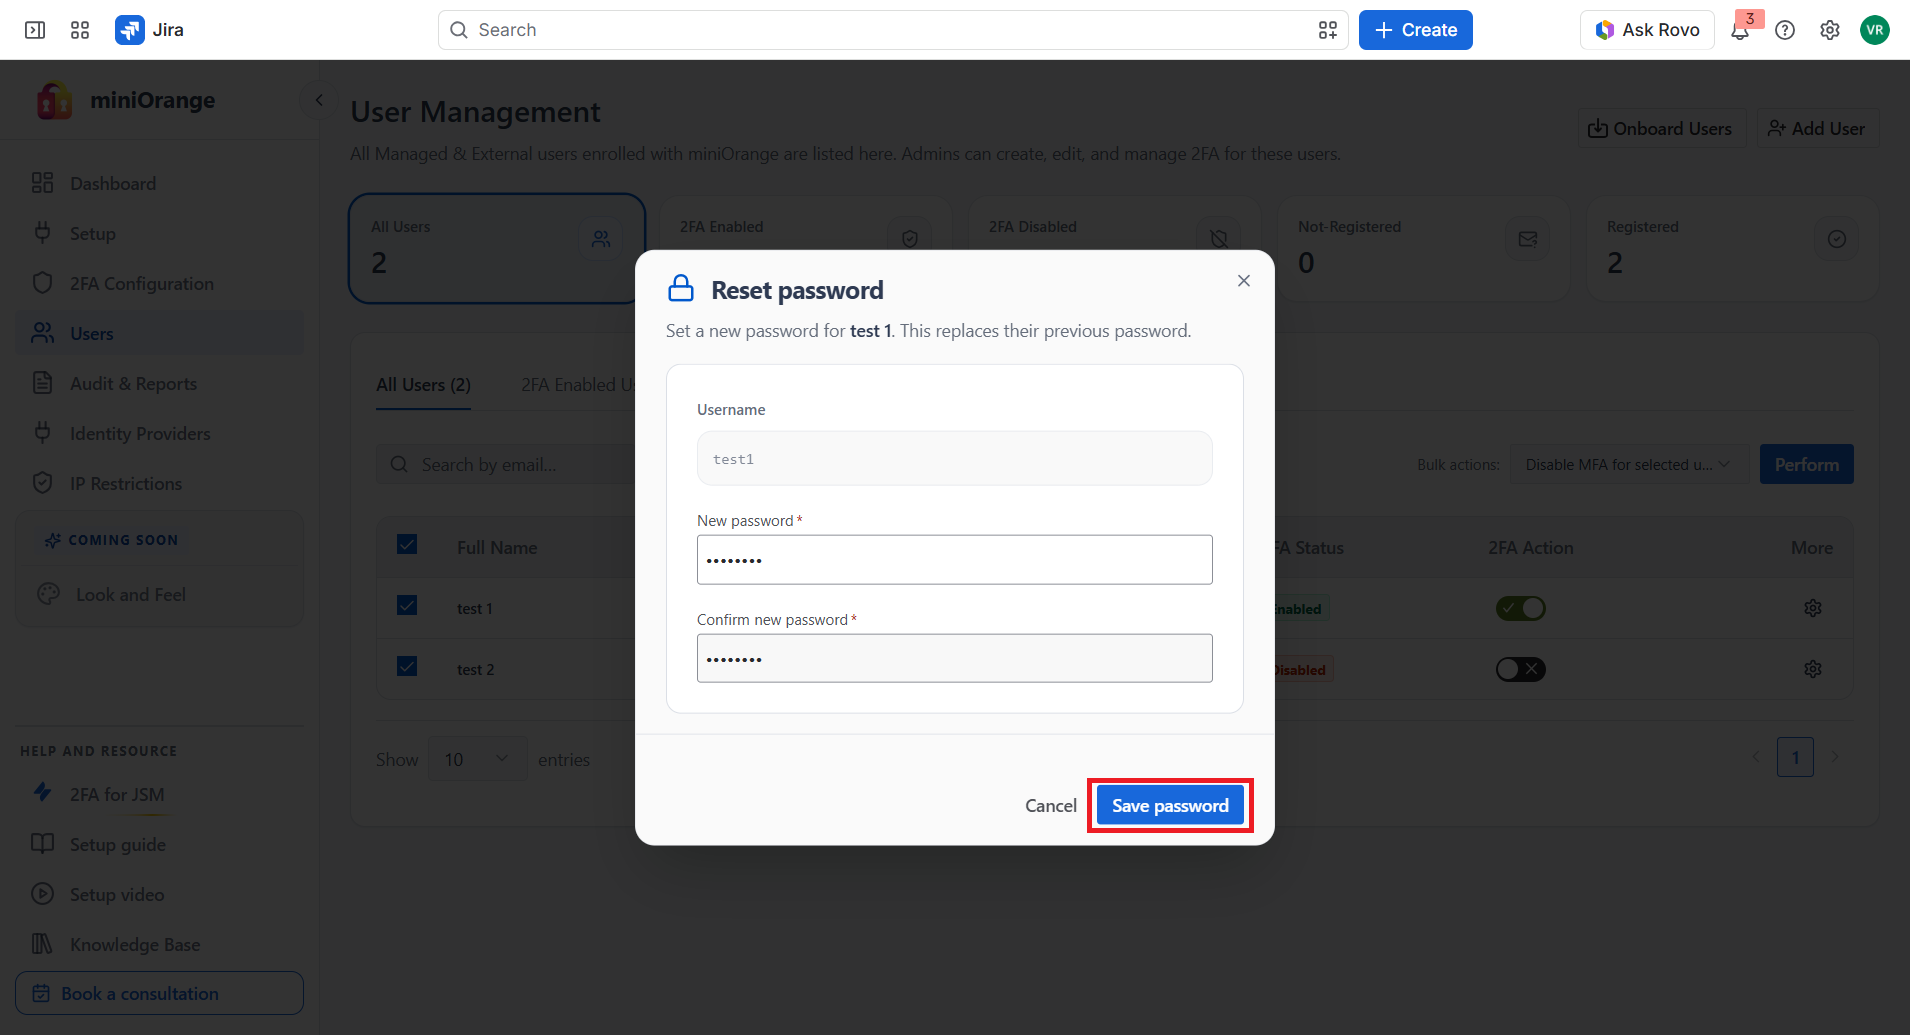
6. Reset user Password
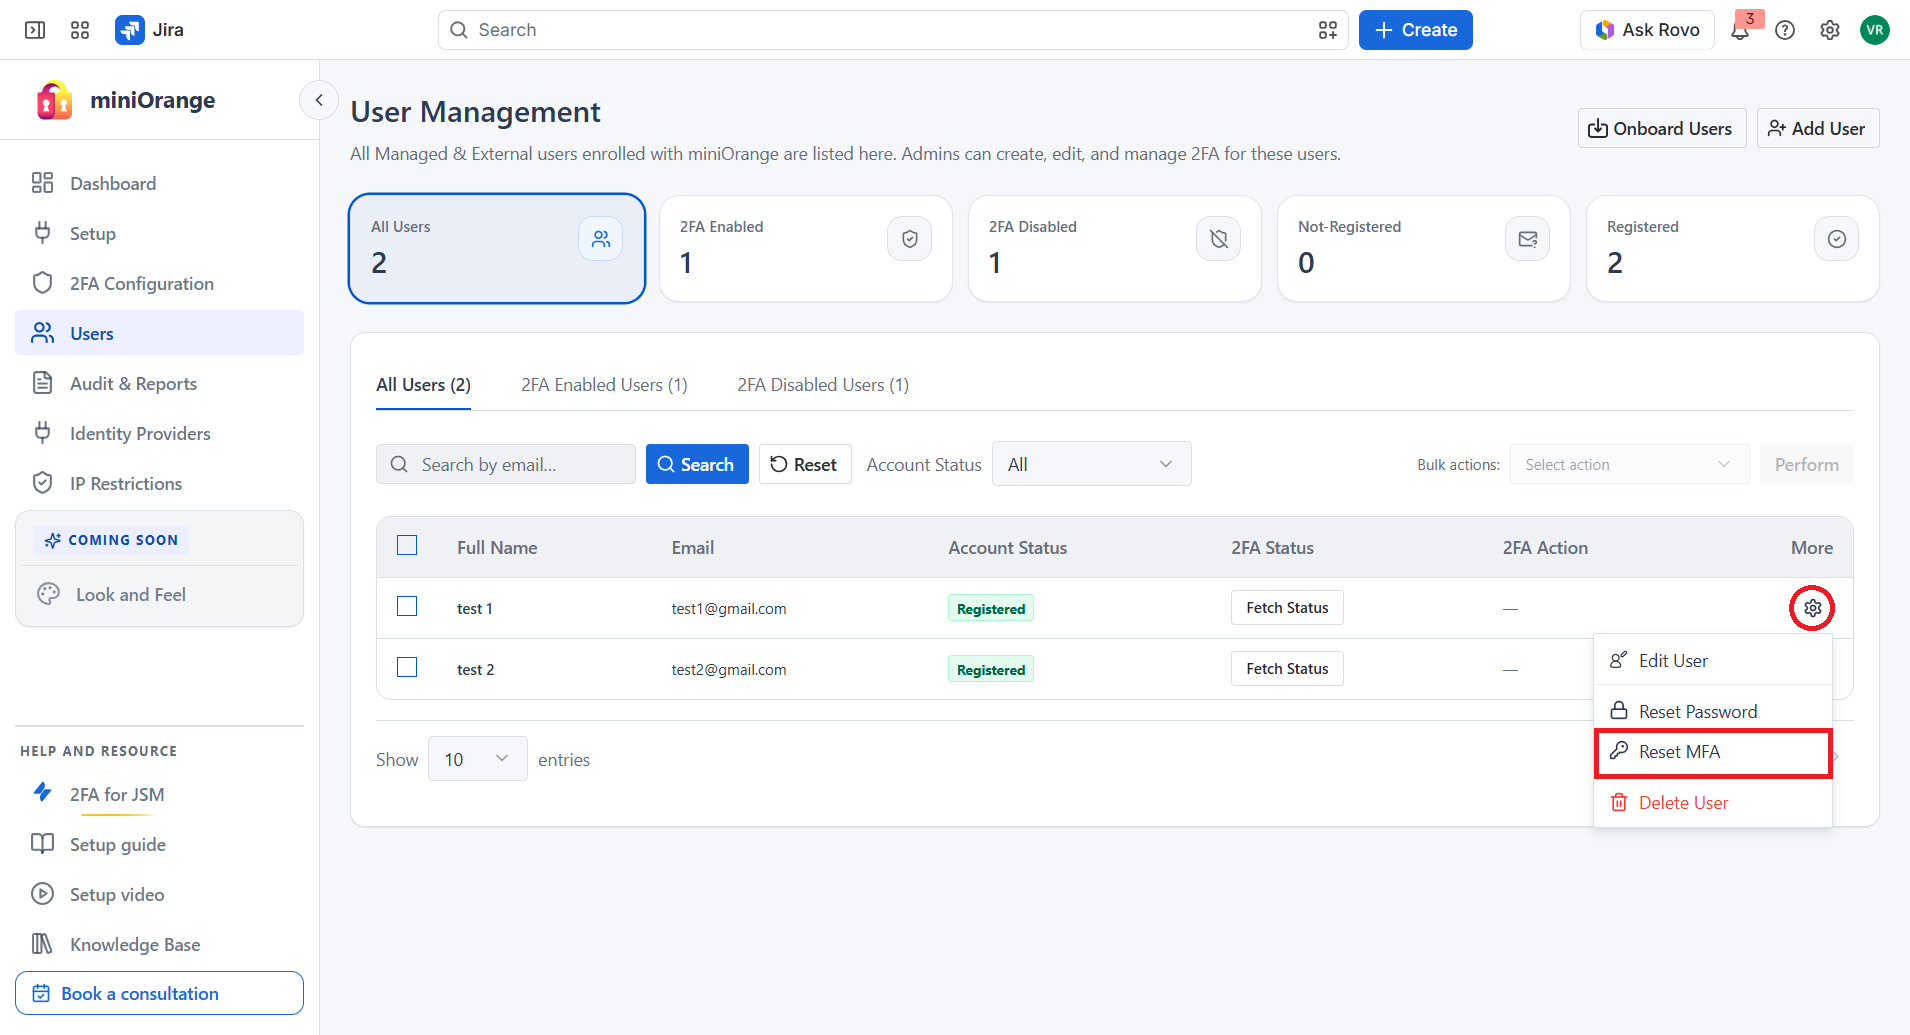
- Select the settings (⚙️) icon next to a user entry.
- Choose Reset Password.
- In the modal dialog, enter and confirm the new password, then click Save Password.
7. Delete user
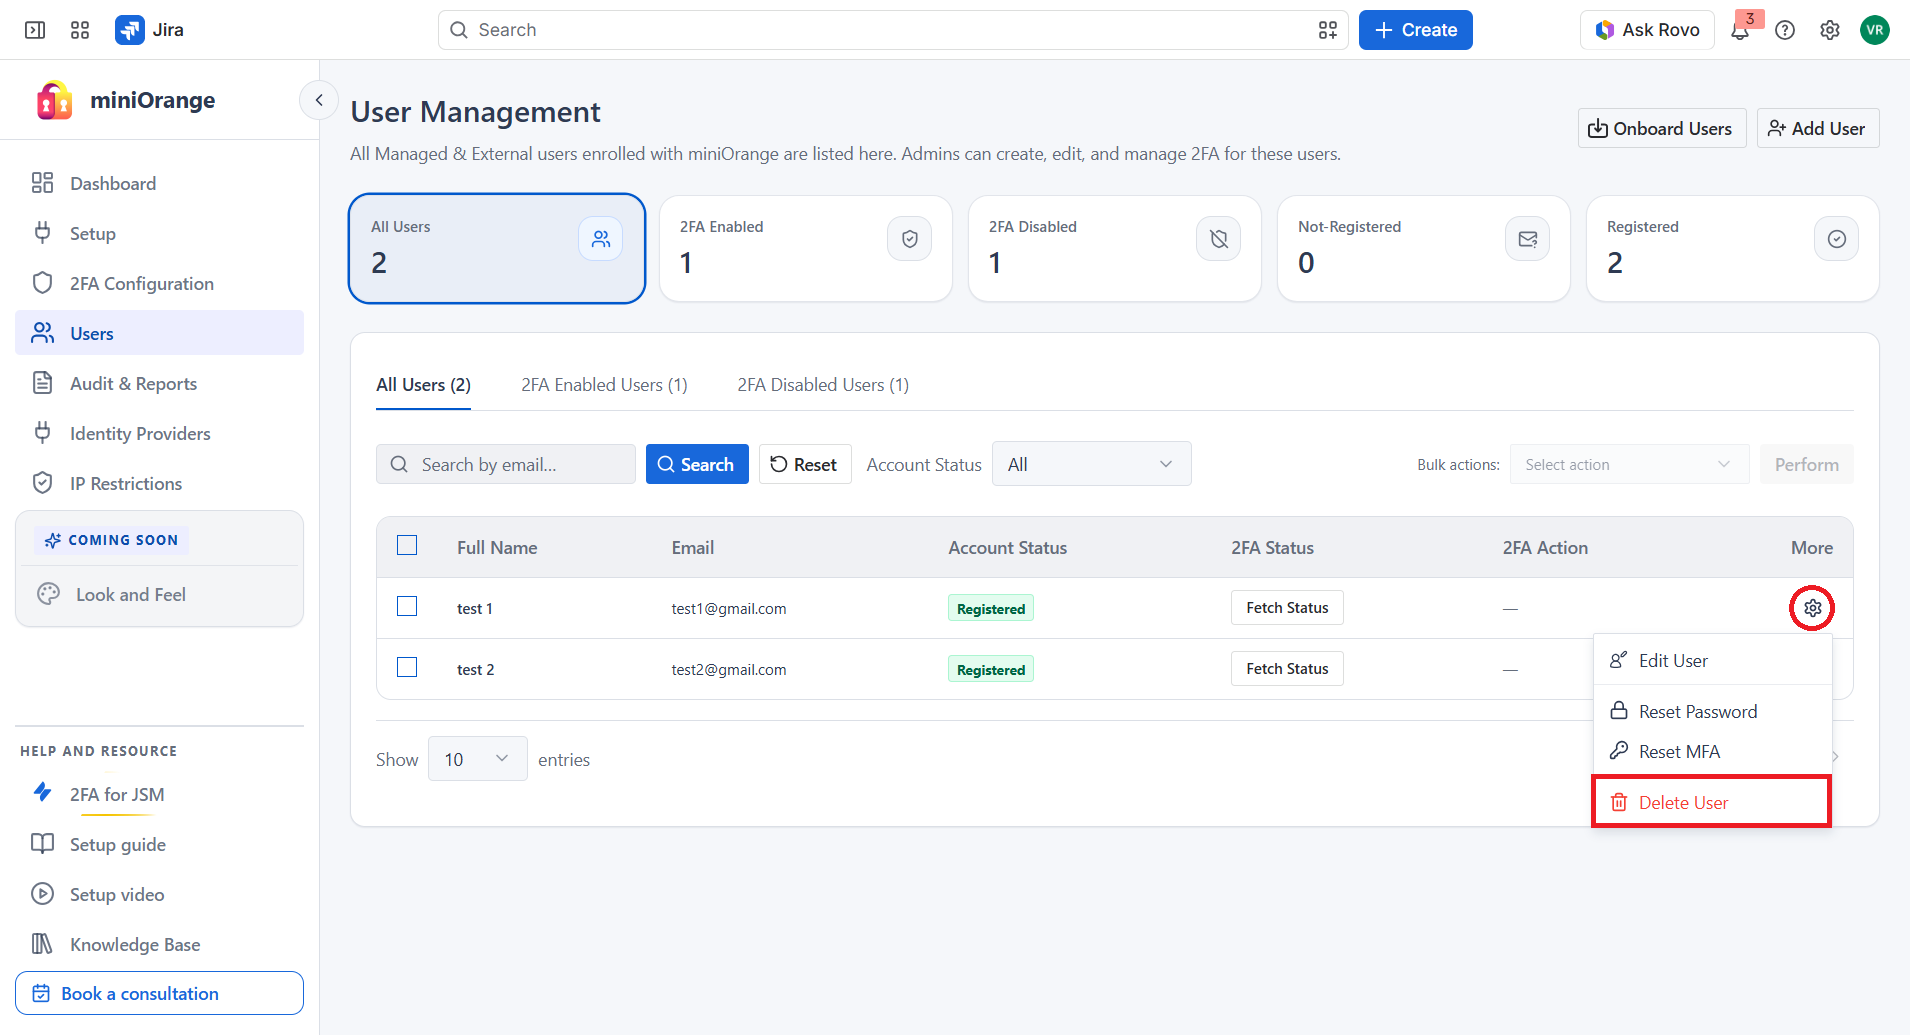
7.1 Individual
- Select the settings (⚙️) icon next to a user entry.
- Choose Delete user and confirm the action.
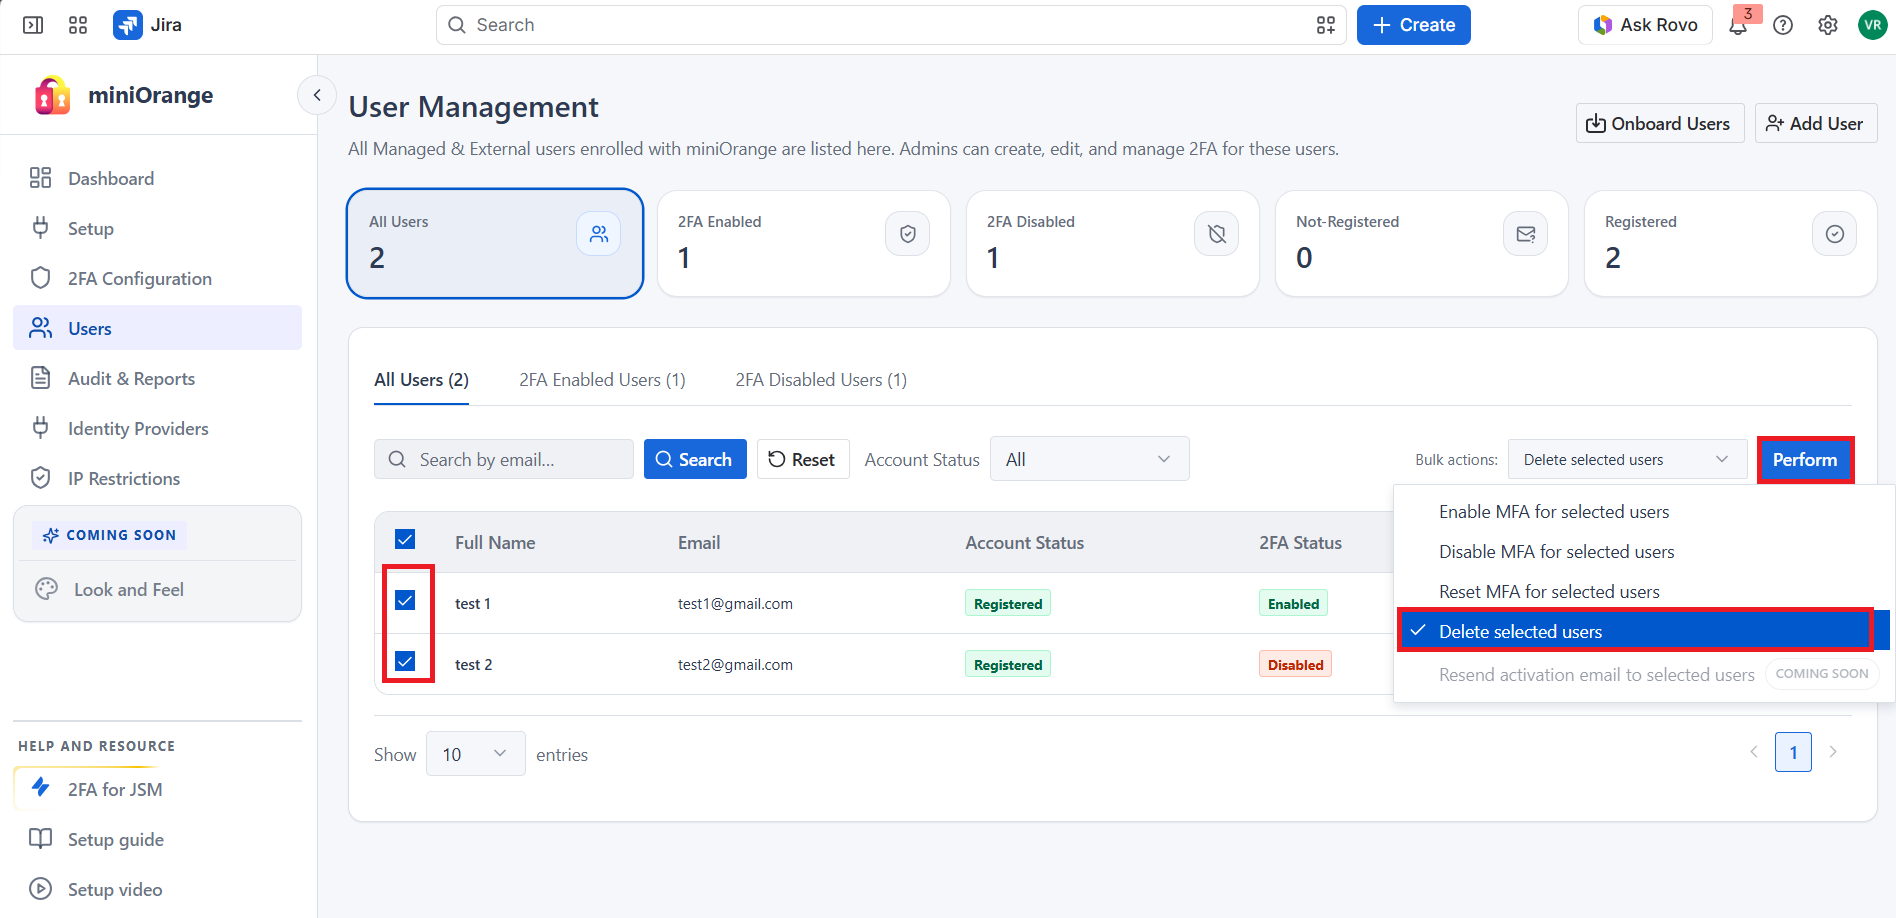
7.2 Bulk
- Select multiple users using the checkboxes.
- Choose Delete Users from Bulk Actions, then execute and confirm.
8. Reset MFA
8.1 Individual
- Select the settings (⚙️) icon next to a user entry.
- Choose Reset MFA and confirm. MFA reconfiguration is required on the user's next login.
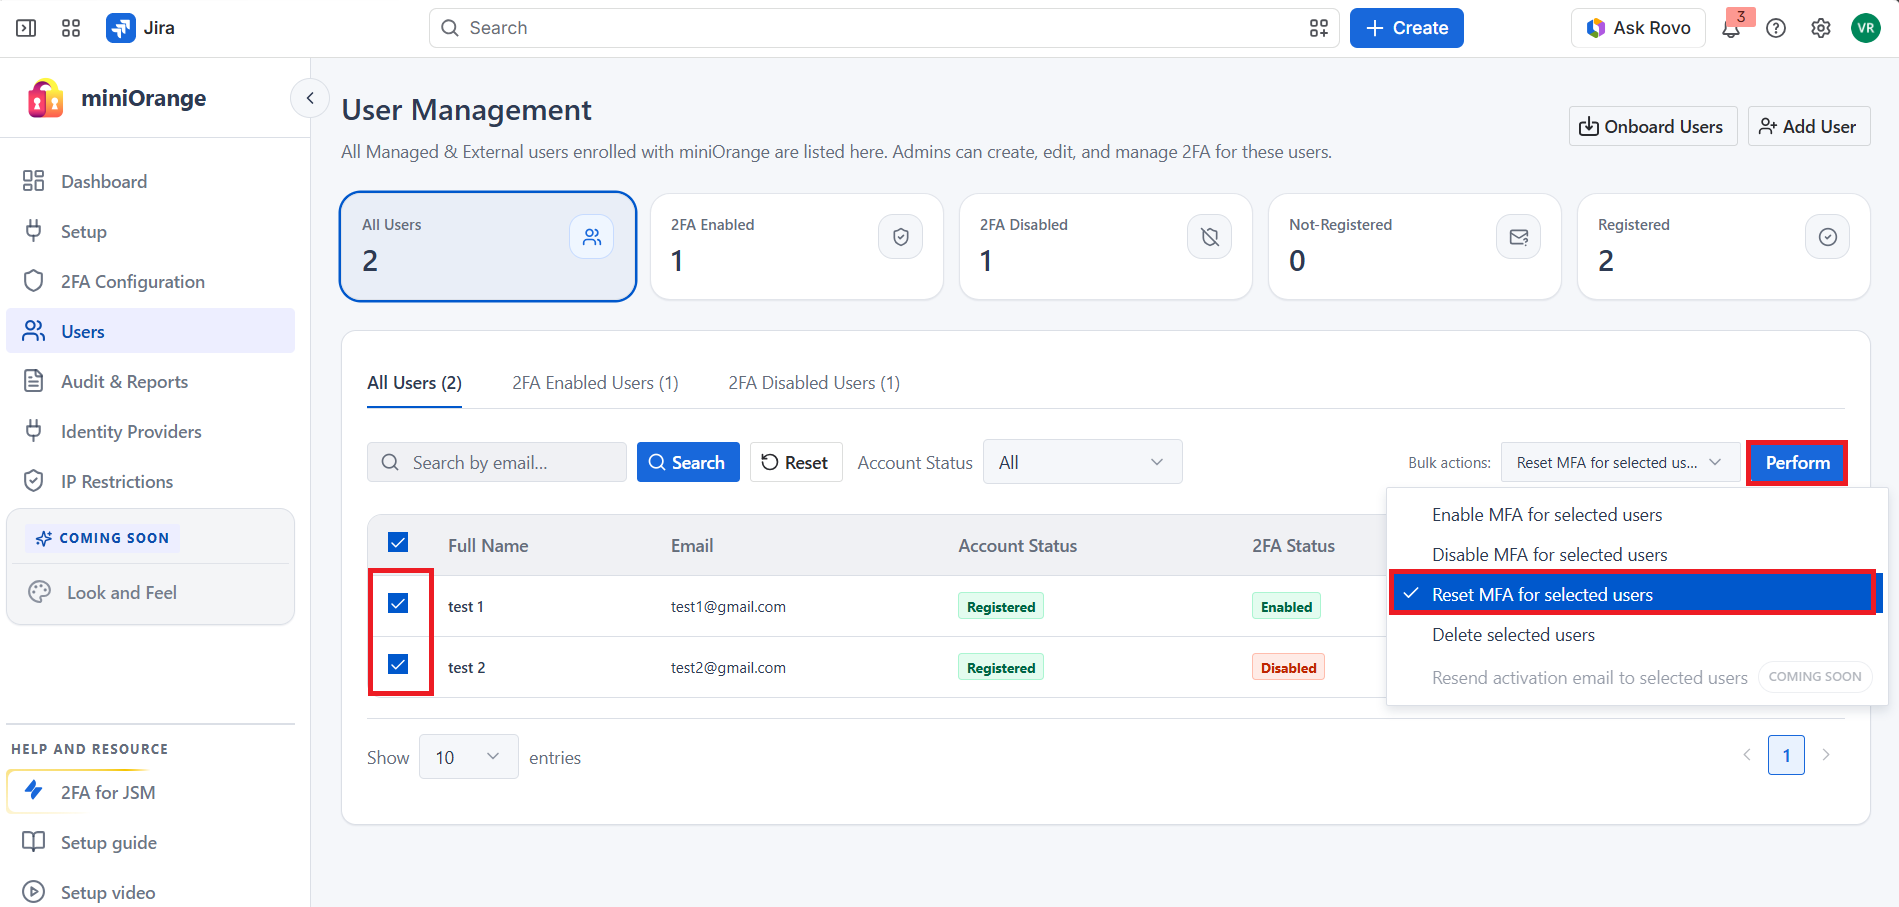
8.2 Bulk
- Select multiple users.
- Choose Reset MFA from Bulk Actions, then execute and confirm.
9. Search users
Use the search bar to locate users by name or email. Search behavior depends on the active tab:
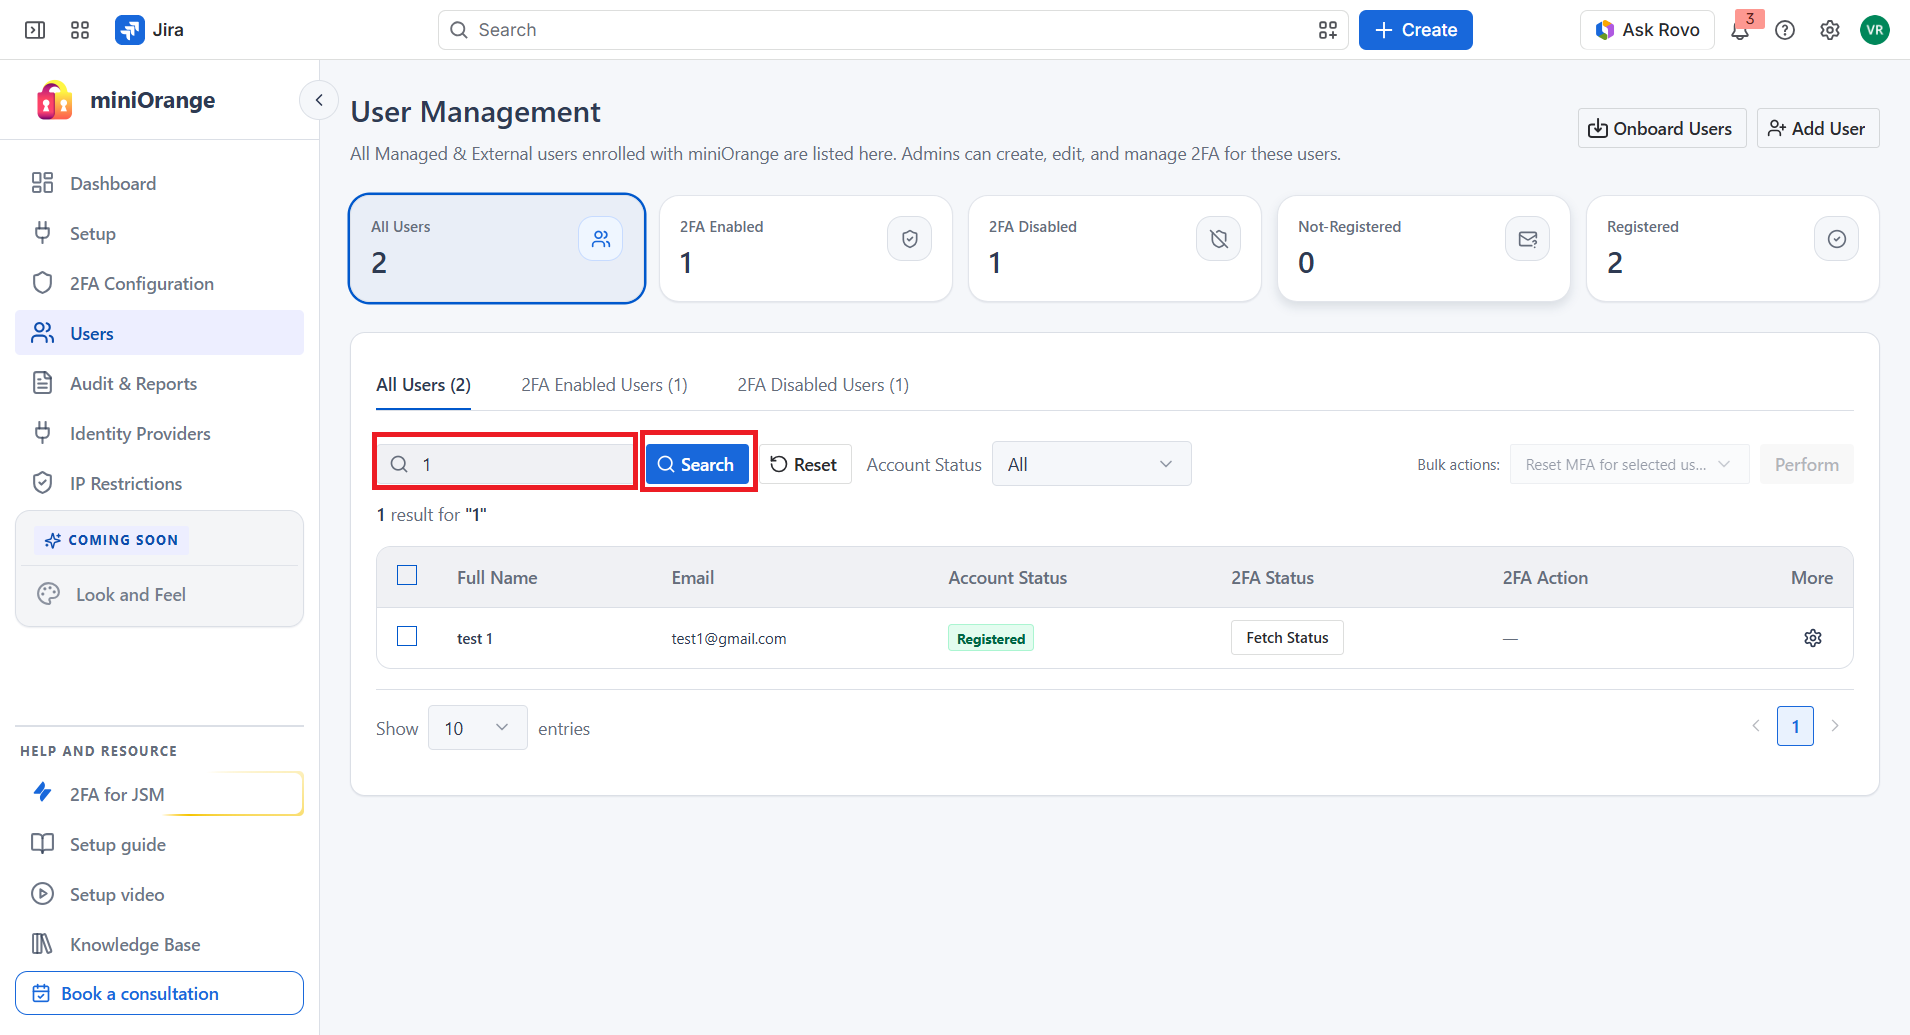
- Enabled / Disabled tabs, results are filtered by 2FA status.
- All users tab, shows all users regardless of 2FA status.
If no results appear in a sub-tab, switching to All users provides complete visibility.
Audit & Reports Tab
Open Audit & Reports from the sidebar to access reports on MFA usage and security activity.
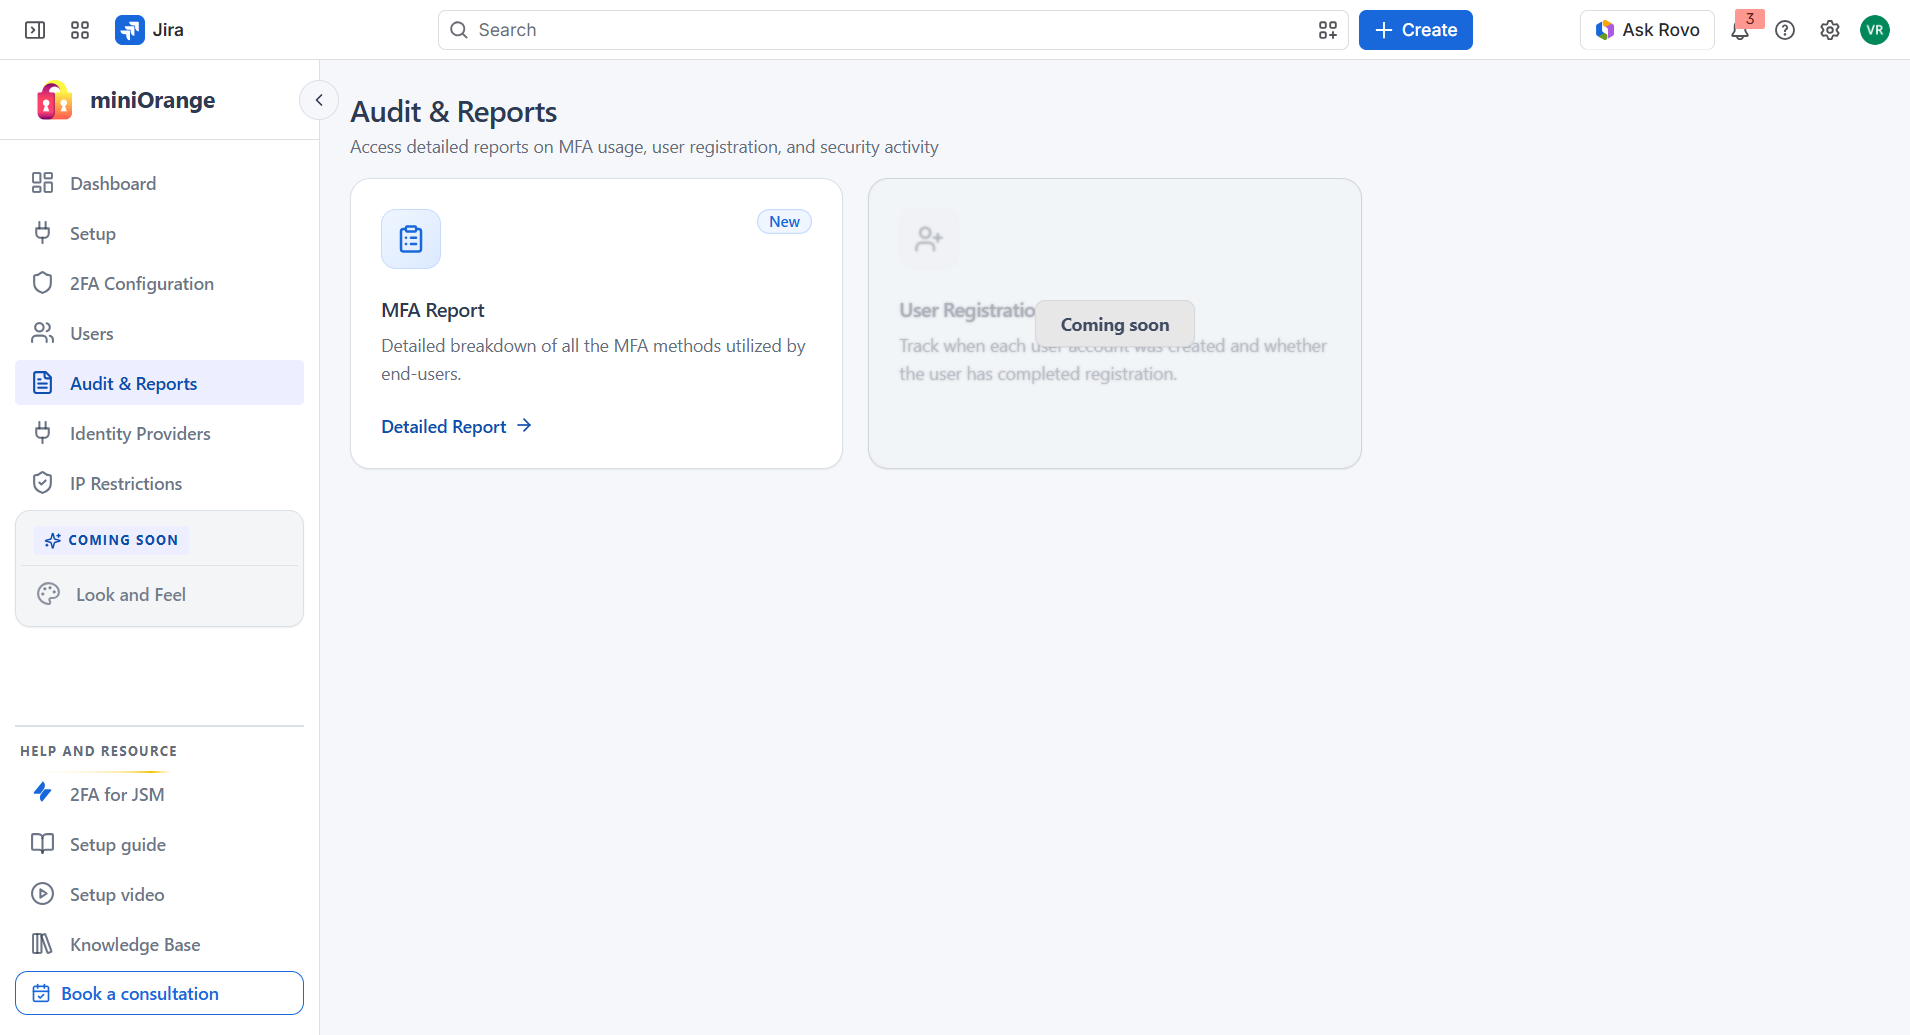
1. MFA Report
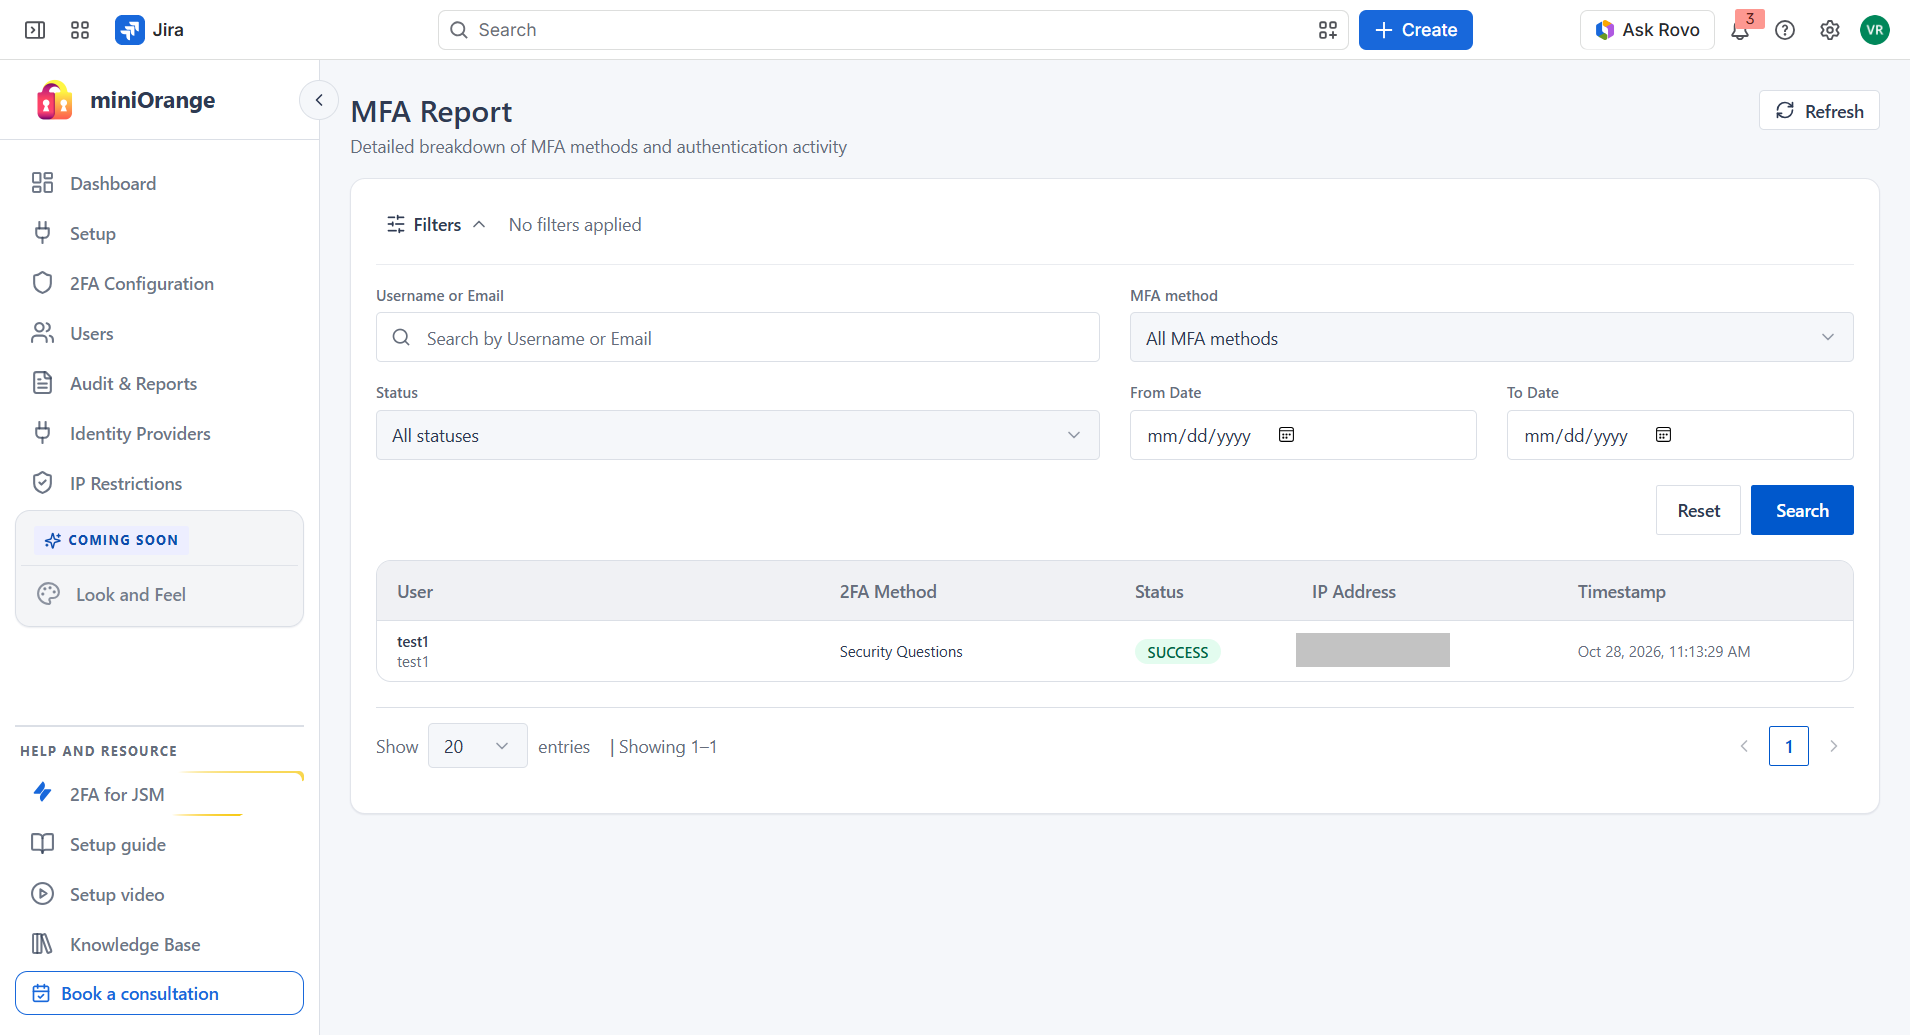
The MFA Report shows a log of every two-factor authentication attempt made by your managed and external users. Each entry includes the user’s identity, 2FA method, authentication status, IP address, and timestamp.
The table lists the following for every attempt:
| Column | Shows |
|---|---|
| User | The name and email or username of the person who authenticated. |
| 2FA Method | The authentication method used, such as Google Authenticator or OTP Over Email. |
| Status | The result of the attempt, for example SUCCESS, FAILED, or DENIED. |
| IP Address | The IP address the user connected from. |
| Timestamp | The date and time of the attempt. |
Click any row to open a side panel with the full detail of that attempt, including the event message and the delivered and responded times.
Filter options
Use the Filters section above the table to narrow the log down. Set the filters you need, then click Search.
| Filter | What it does |
|---|---|
| Username or Email | Finds all attempts for a specific user. Enter a full or partial username or email address. |
| MFA method | Shows only attempts made with the selected method. Leave as All MFA methods to include every method. |
| Status | Shows only attempts with the selected result. Leave as All statuses to include every result. |
| From Date | Includes attempts made on or after this date. |
| To Date | Includes attempts made on or before this date. Must be on or after the From Date. |
Applied filters appear as chips above the table. Remove a single chip to drop that filter, or click Reset to clear all of them and show the complete log again.
2. User Registration Report (Coming soon)
The User Registration Report will track when each user account was created and whether the user has completed their registration, so you can see at a glance who has finished setting up and who still needs to.
Identity Providers Tab
The Identity Providers tab lets you configure external Identity Providers (IdPs). This is useful when your managed and external users are managed in an external IdP such as Okta, Microsoft Entra ID (Azure AD), Google, or any other SAML or OAuth/OIDC-compatible provider. You can configure one or multiple Identity Providers, allowing users to access your Jira site using their existing organizational credentials.
1. Add a New Identity Provider
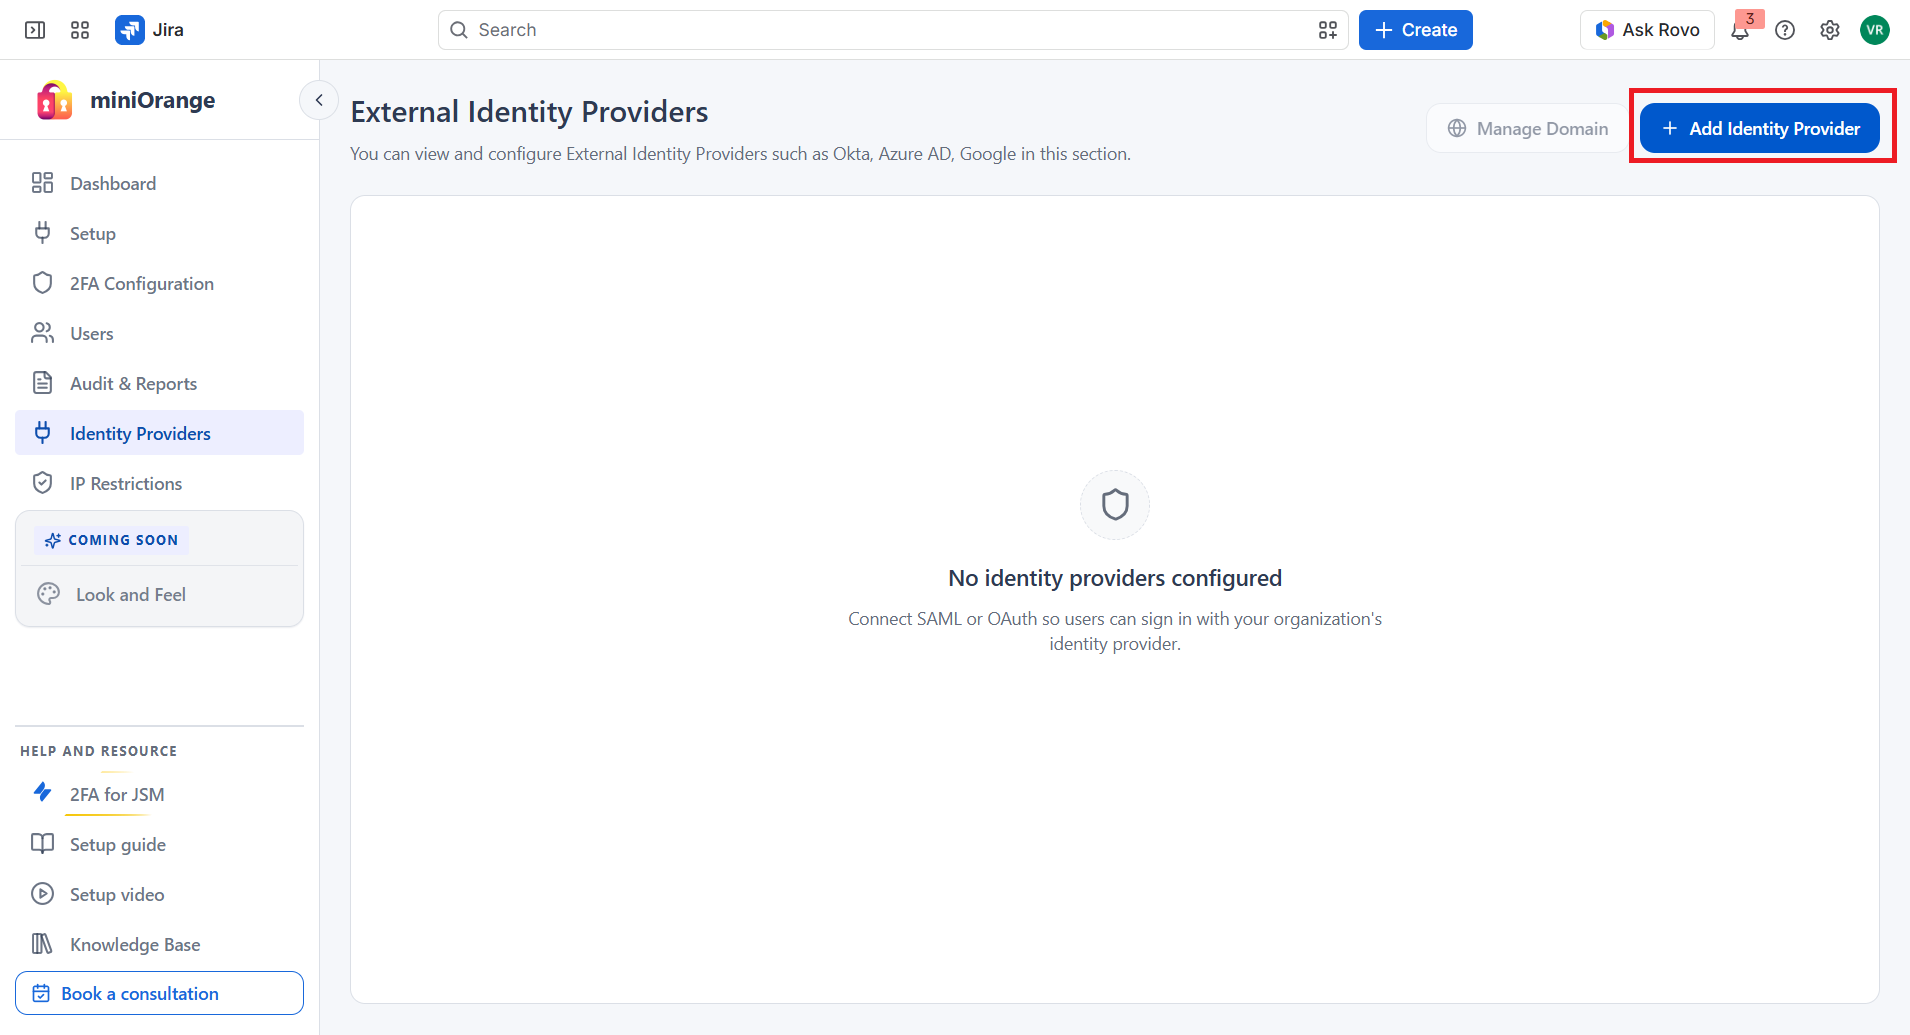
- Open the Identity Providers tab and click Add Identity Provider in the upper-right corner.
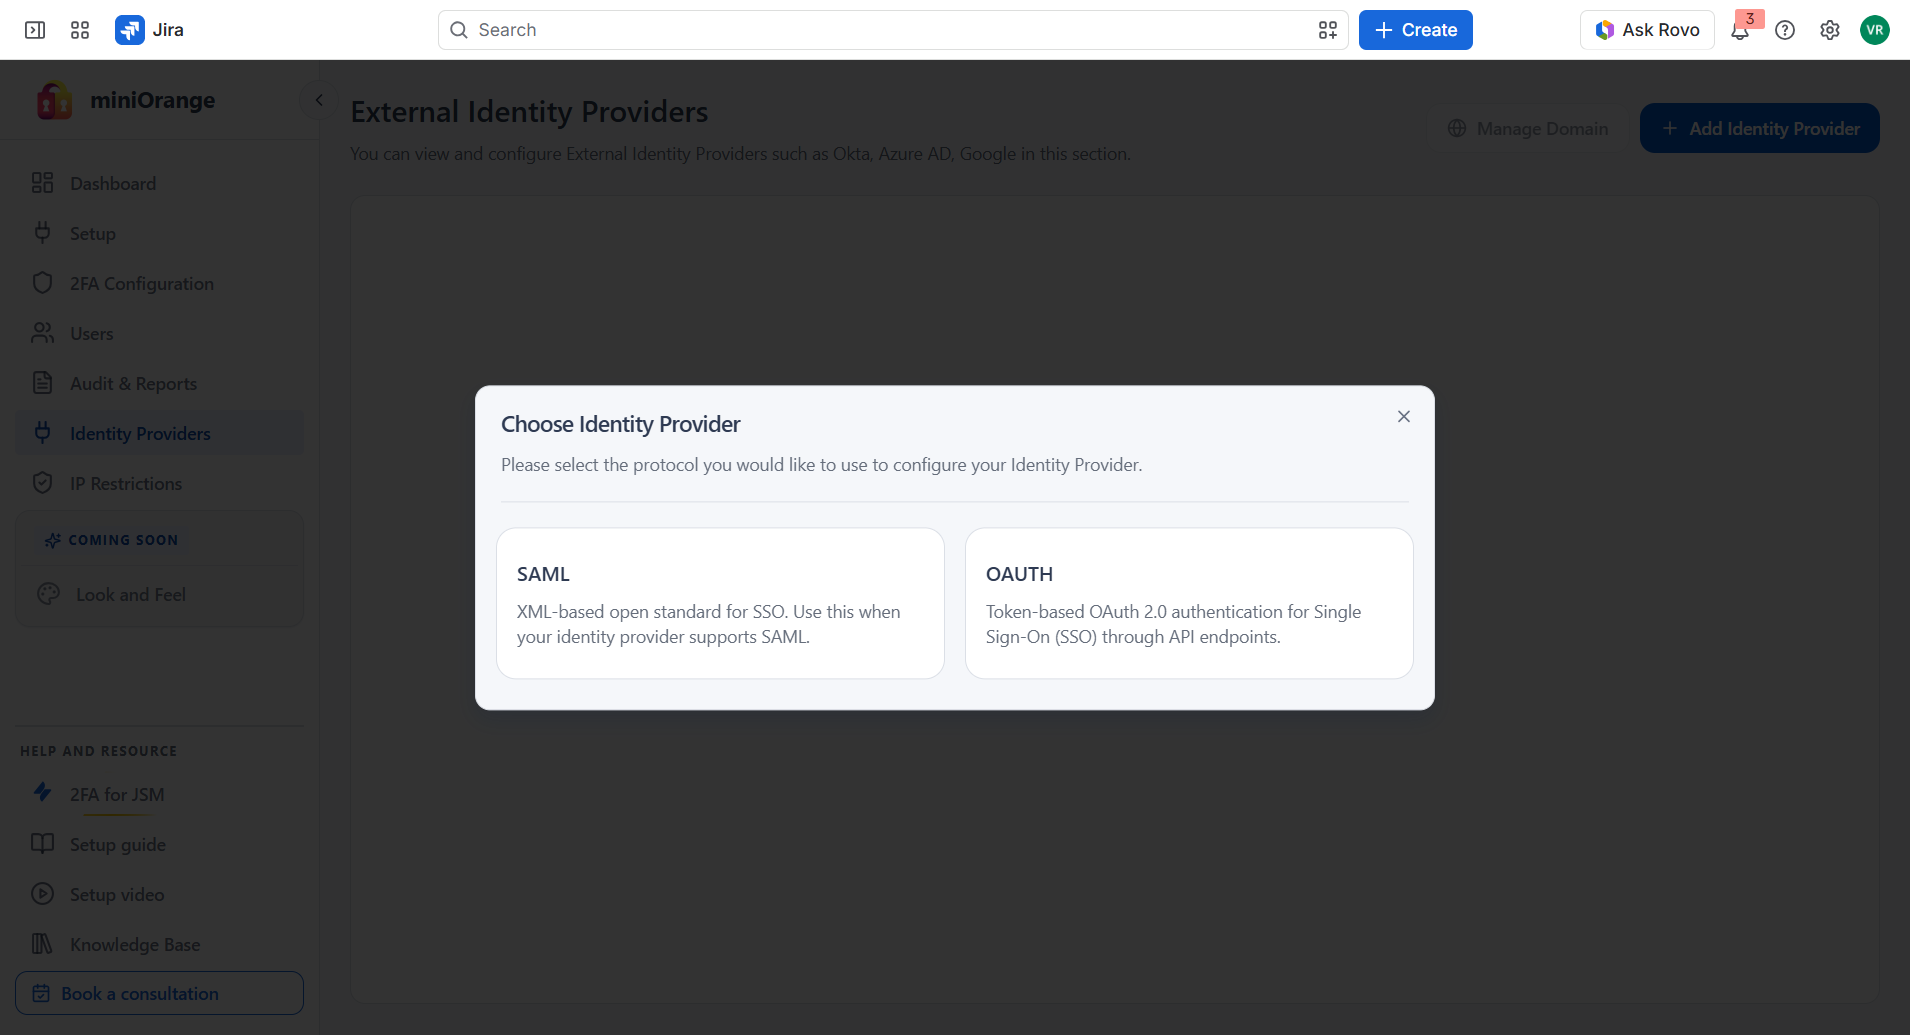
- Select the authentication protocol your IdP supports, SAML or OAuth / OpenID Connect (OIDC).
Configure a SAML Identity Provider
If your Identity Provider supports SAML 2.0, follow the steps below to configure SAML-based Single Sign-On (SSO) for your Jira Site. After selecting SAML as the authentication protocol, complete the following configuration steps.
Step 1: Configure Your Application in the Identity Provider (IdP)
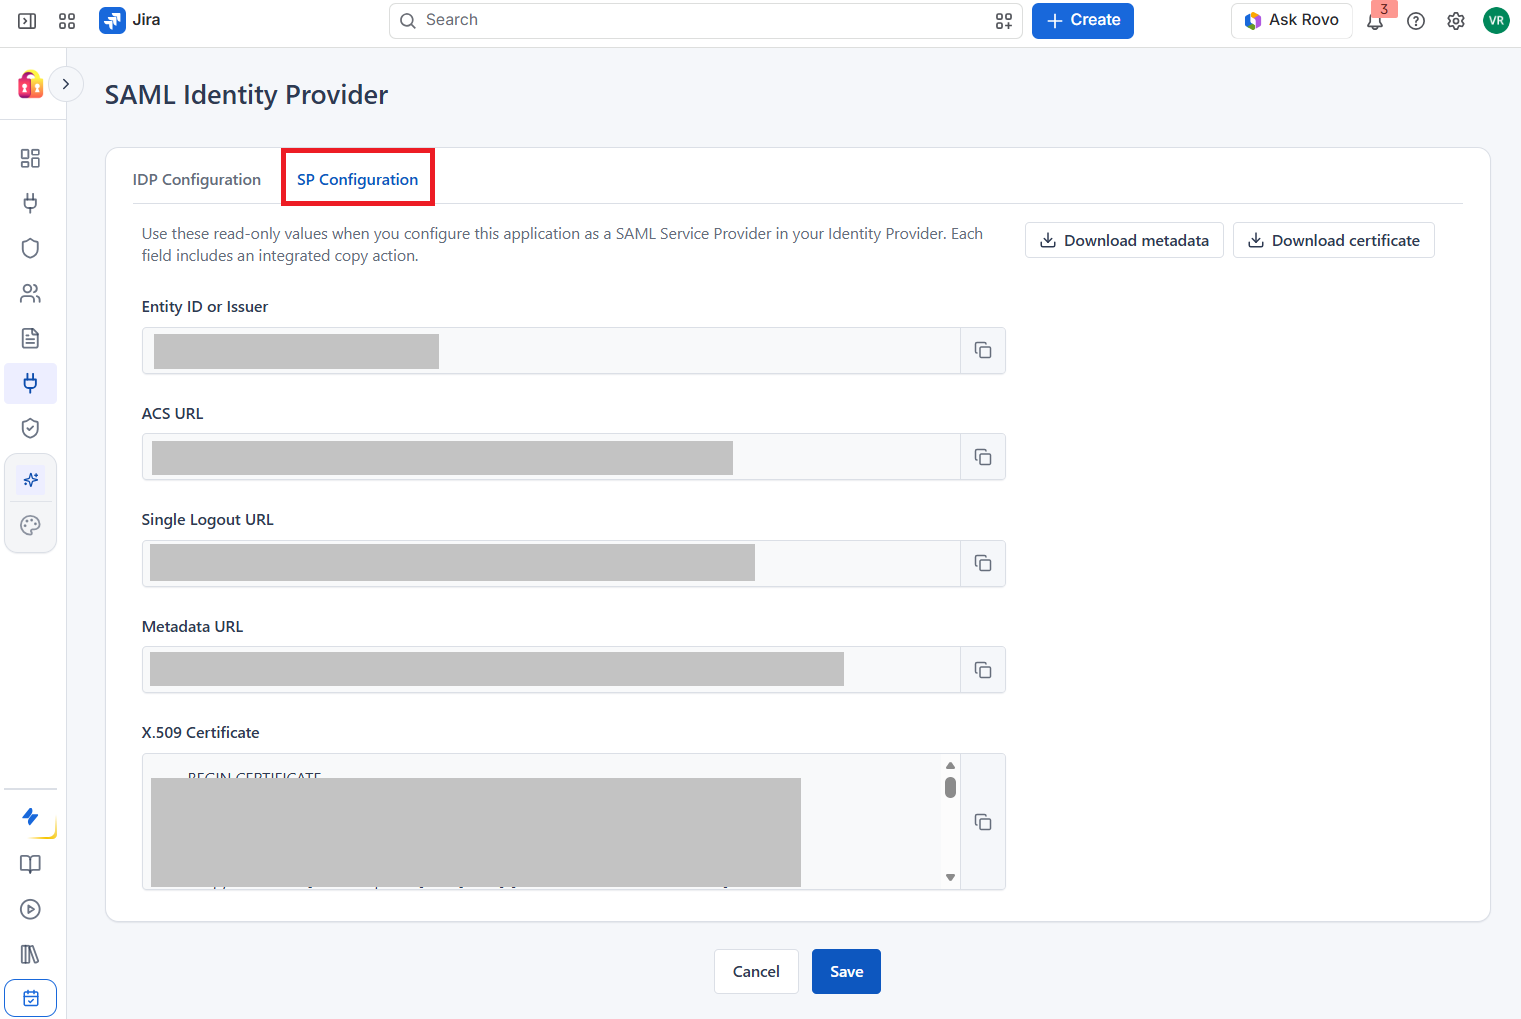
Create a new SAML application in your Identity Provider using the Service Provider (SP) configuration details provided by the plugin.
- Copy the SAML configuration metadata. The plugin displays the required SAML Service Provider (SP) details that must be entered in your IdP.
- Create a new SAML application in your IdP: log in to your IdP's administrator dashboard, navigate to the Applications section, click Create Application (also called Create App Integration, or the equivalent option), and when prompted for a sign-in protocol, choose SAML 2.0 and proceed.
- Configure the application. During setup, your IdP will ask for details such as Application Name, Audience URI (SP Entity ID), Single Sign-On (ACS) URL, and other SAML-related settings. You can find these values on the SAML Identity Provider page, in the SP Configuration tab within the plugin.
- Complete the application setup: copy the required values from the plugin into the corresponding fields in your IdP, review the configuration, and complete the application creation process. Then assign the required users and/or groups to the application so they can access your Atlassian instance via SSO.
- Return to the plugin to configure the Identity Provider details once the SAML application has been created successfully.
Step 2: Configure Identity Provider Details in the Plugin
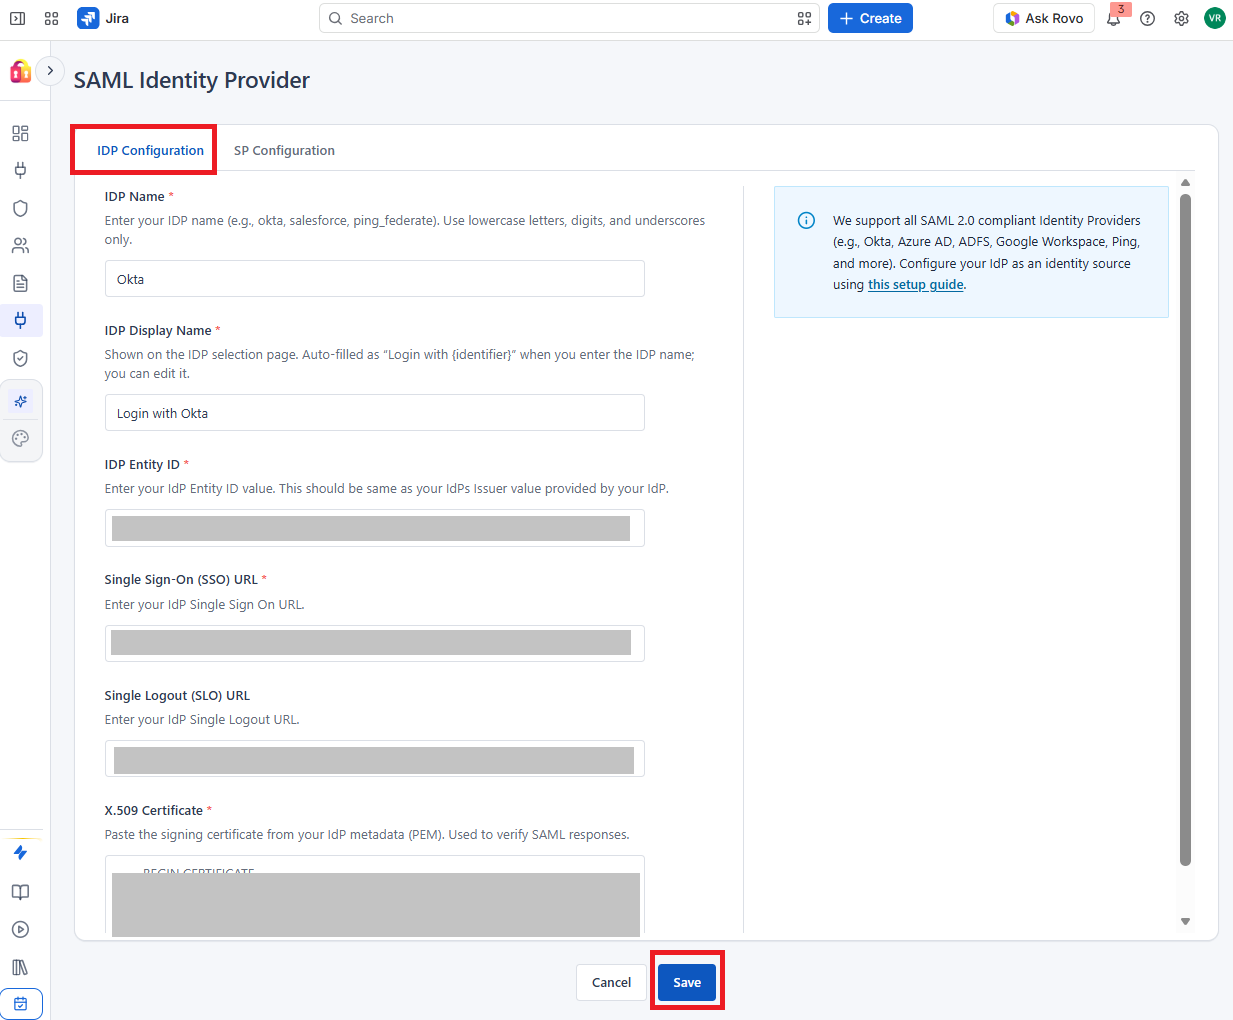
After creating the SAML application, configure the external Identity Provider in the plugin using the SAML metadata provided by your IdP. The following values are required:
- IdP Name
- Idp Display Name
- IdP Entity ID (Issuer)
- Single Sign-On (SSO) URL
- X.509 Certificate
These values can typically be found in the SAML configuration or metadata section of your IdP after the application has been created.
- Copy the IdP metadata: open the SAML application you created in your IdP and locate its SAML configuration or metadata page.
- Configure the plugin: navigate back to the SAML Identity Provider page in the plugin, enter the copied values into their corresponding fields, and click Save to complete the Identity Provider configuration.
Configure an OAuth / OpenID Connect (OIDC) Identity Provider
If your Identity Provider supports OAuth 2.0 or OpenID Connect (OIDC), follow the steps below to configure OAuth/OIDC-based Single Sign-On (SSO) for your Jira Site. After selecting OAuth / OpenID Connect (OIDC) as the authentication protocol, complete the following configuration steps.
Step 1: Configure Your Application in the Identity Provider (IdP)
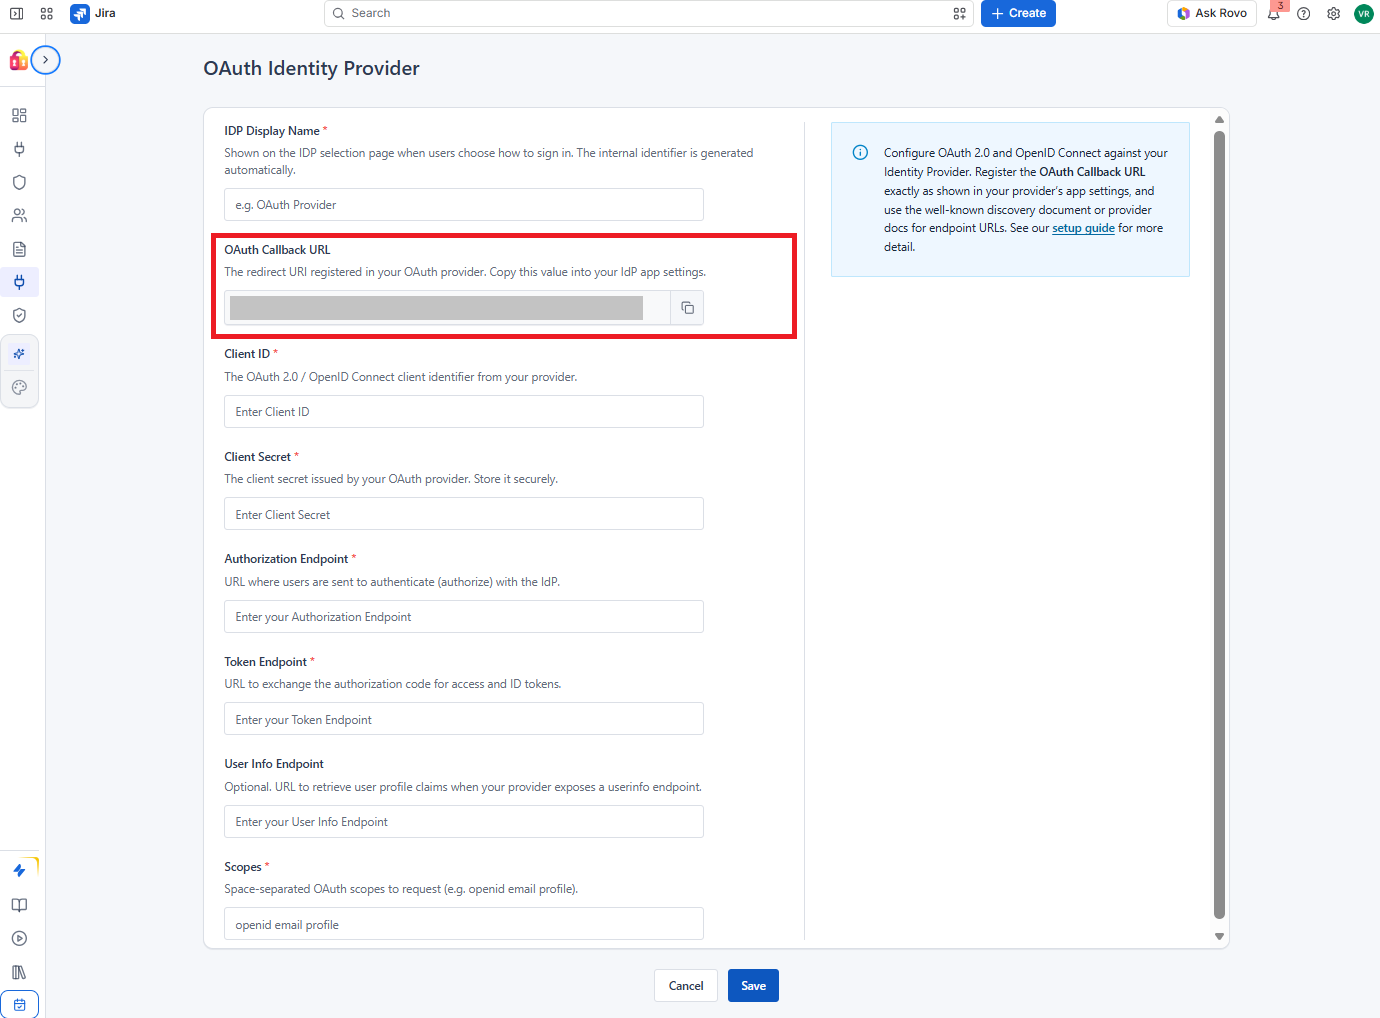
Create a new OAuth/OIDC application in your Identity Provider using the OAuth Callback URL provided by the plugin.
- Create a new OAuth/OIDC application in your IdP: log in to your IdP's administrator dashboard, navigate to the Applications section, and click Create Application (also called Create App Integration, or the equivalent option). When prompted for a sign-in protocol, choose OpenID Connect (OIDC) or OAuth 2.0, depending on your IdP. If asked for an application type, select Web Application and continue.
- Configure the application. During setup, your IdP will ask for details such as Application Name and Sign-in Redirect URL / OAuth Callback URL. Copy the OAuth Callback URL displayed on the OAuth Identity Provider page in the plugin and paste it into the corresponding field in your IdP.
- Complete the application setup: review the configuration, save or create the application, and assign the appropriate users and/or groups so they can authenticate via SSO.
- Return to the plugin to configure the Identity Provider details once the OAuth/OIDC application has been created successfully.
Step 2: Configure Identity Provider Details in the Plugin
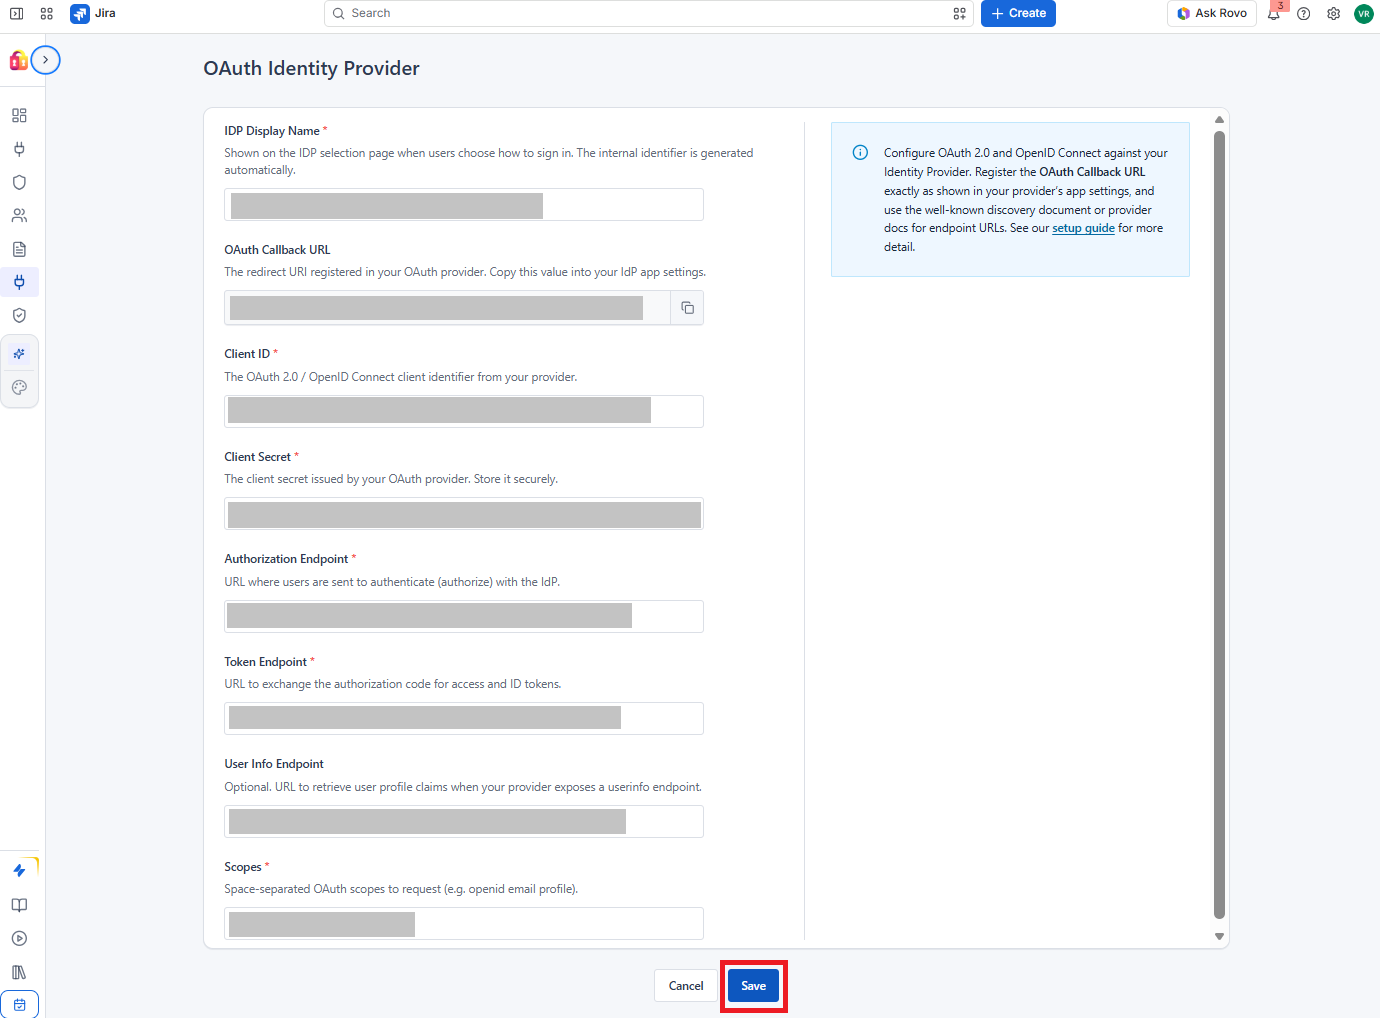
Configure the external Identity Provider in the plugin using the OAuth/OIDC credentials generated by your IdP. The following values are required:
- Idp Display Name
- Client ID
- Client Secret
- Authorization Endpoint
- Token Endpoint
- Scopes (enter at least one scope)
These values are available in the OAuth/OIDC application you created in your Identity Provider.
- Copy the required values from your IdP: locate the OAuth credentials (Client ID, Client Secret) and endpoints in your IdP dashboard.
- Configure the plugin: navigate back to the OAuth Identity Provider page in the plugin and paste the copied values into their corresponding fields. Enter at least one scope, then click Save. For OpenID Connect, include openid and email to complete the Identity Provider configuration.
2. Update the Authentication Source in Atlassian Guard
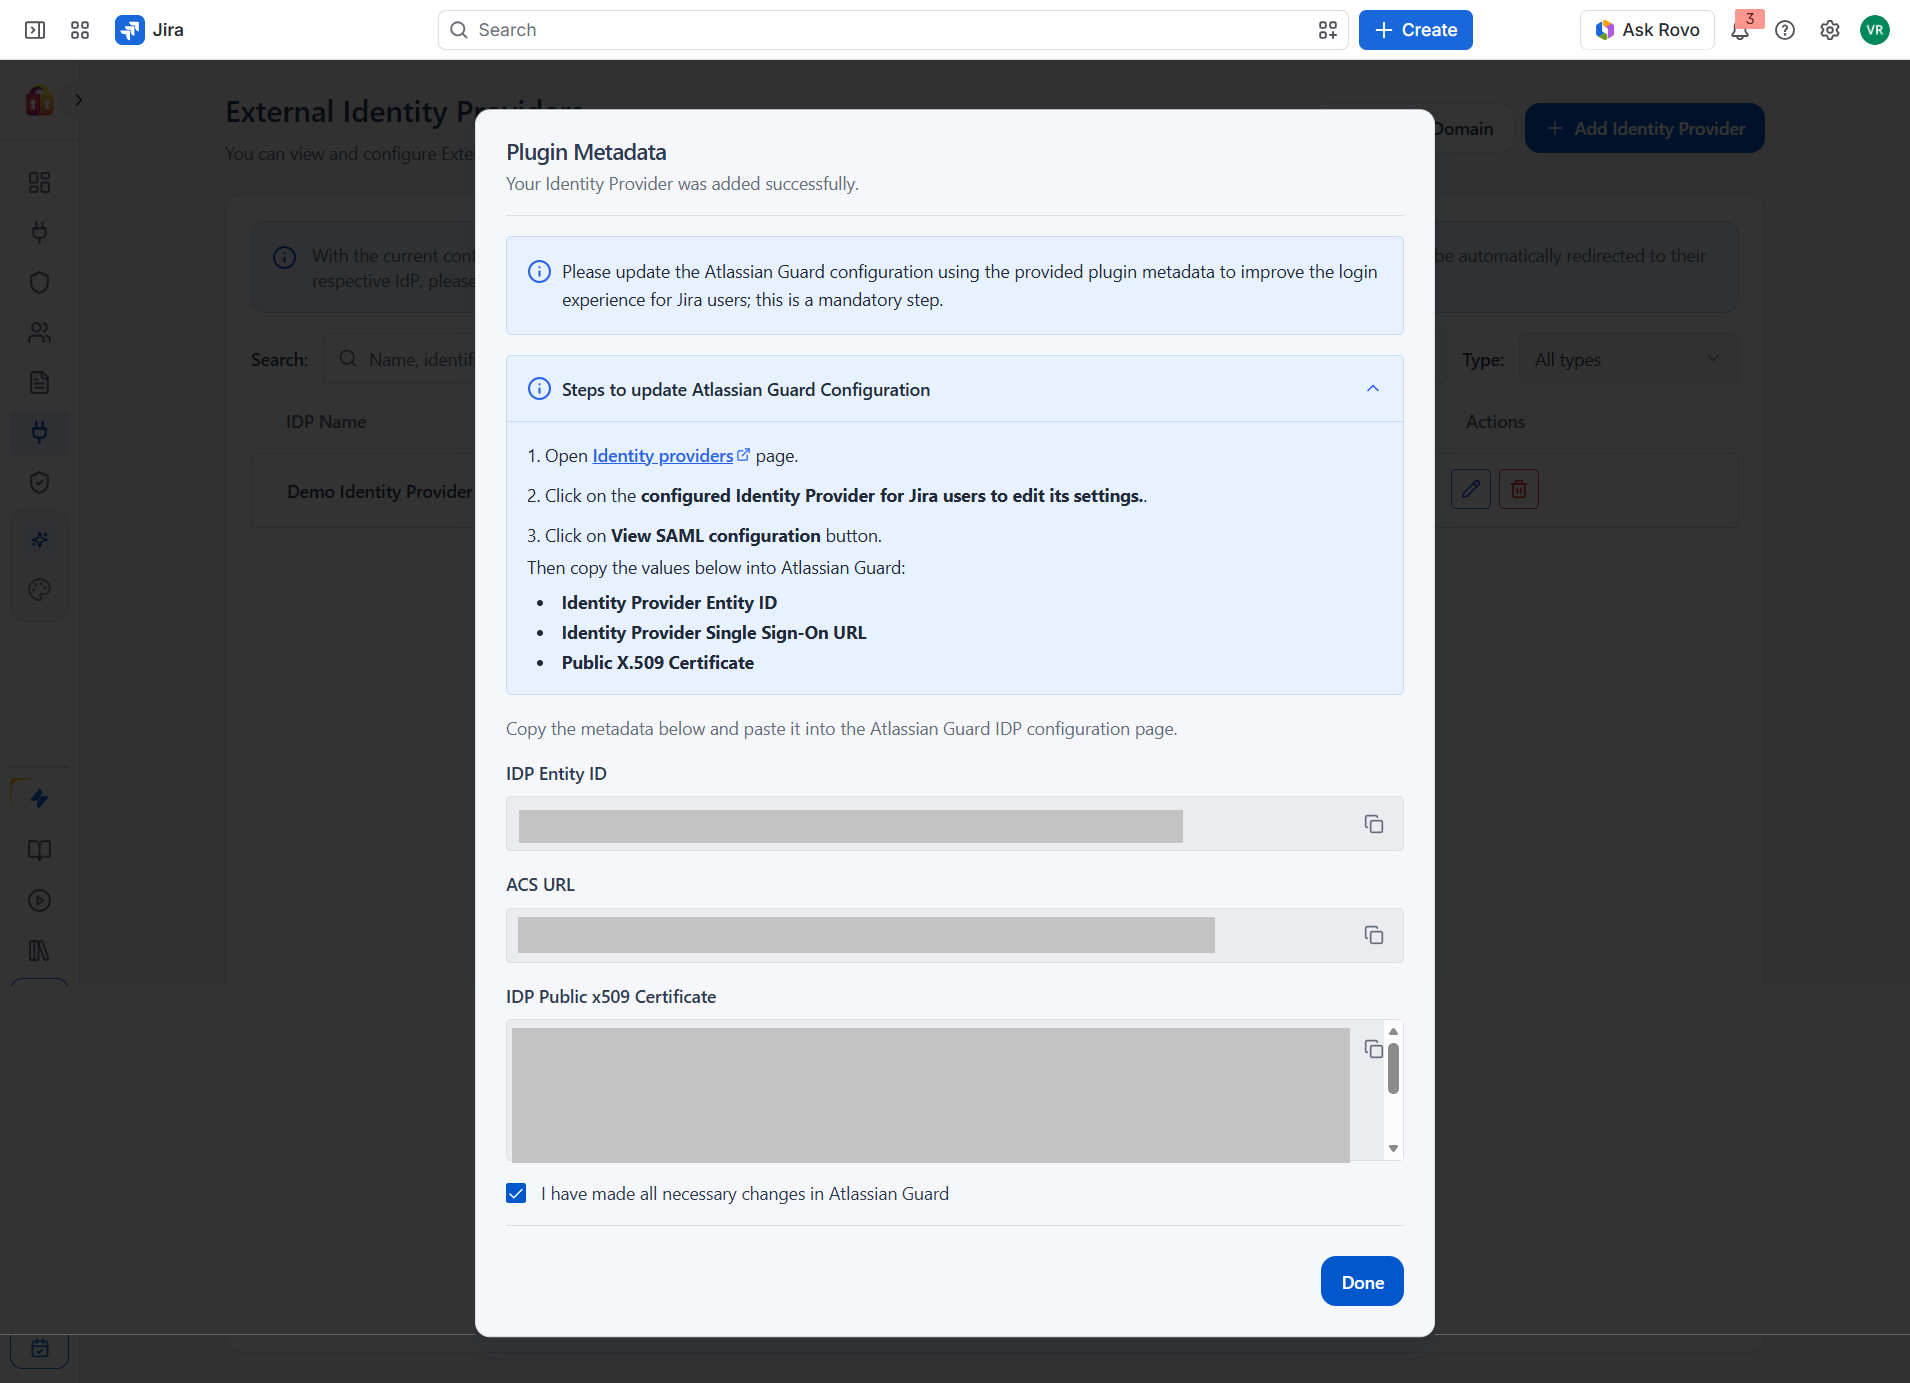
After the Identity Provider has been configured successfully, you are redirected to the Identity Providers landing page, and a confirmation dialog appears with the information required to update your authentication source in Atlassian Guard.
For reference, see: Update authentication source (Step 2)
- On the SAML configuration page in Atlassian Guard, enter the Identity provider entity ID, Identity provider single sign-on URL, and Public X.509 certificate.
- Copy each value from the confirmation dialog displayed in the plugin and paste it into the corresponding field in Atlassian Guard.
- Click Save to update the authentication source.
Complete the Configuration
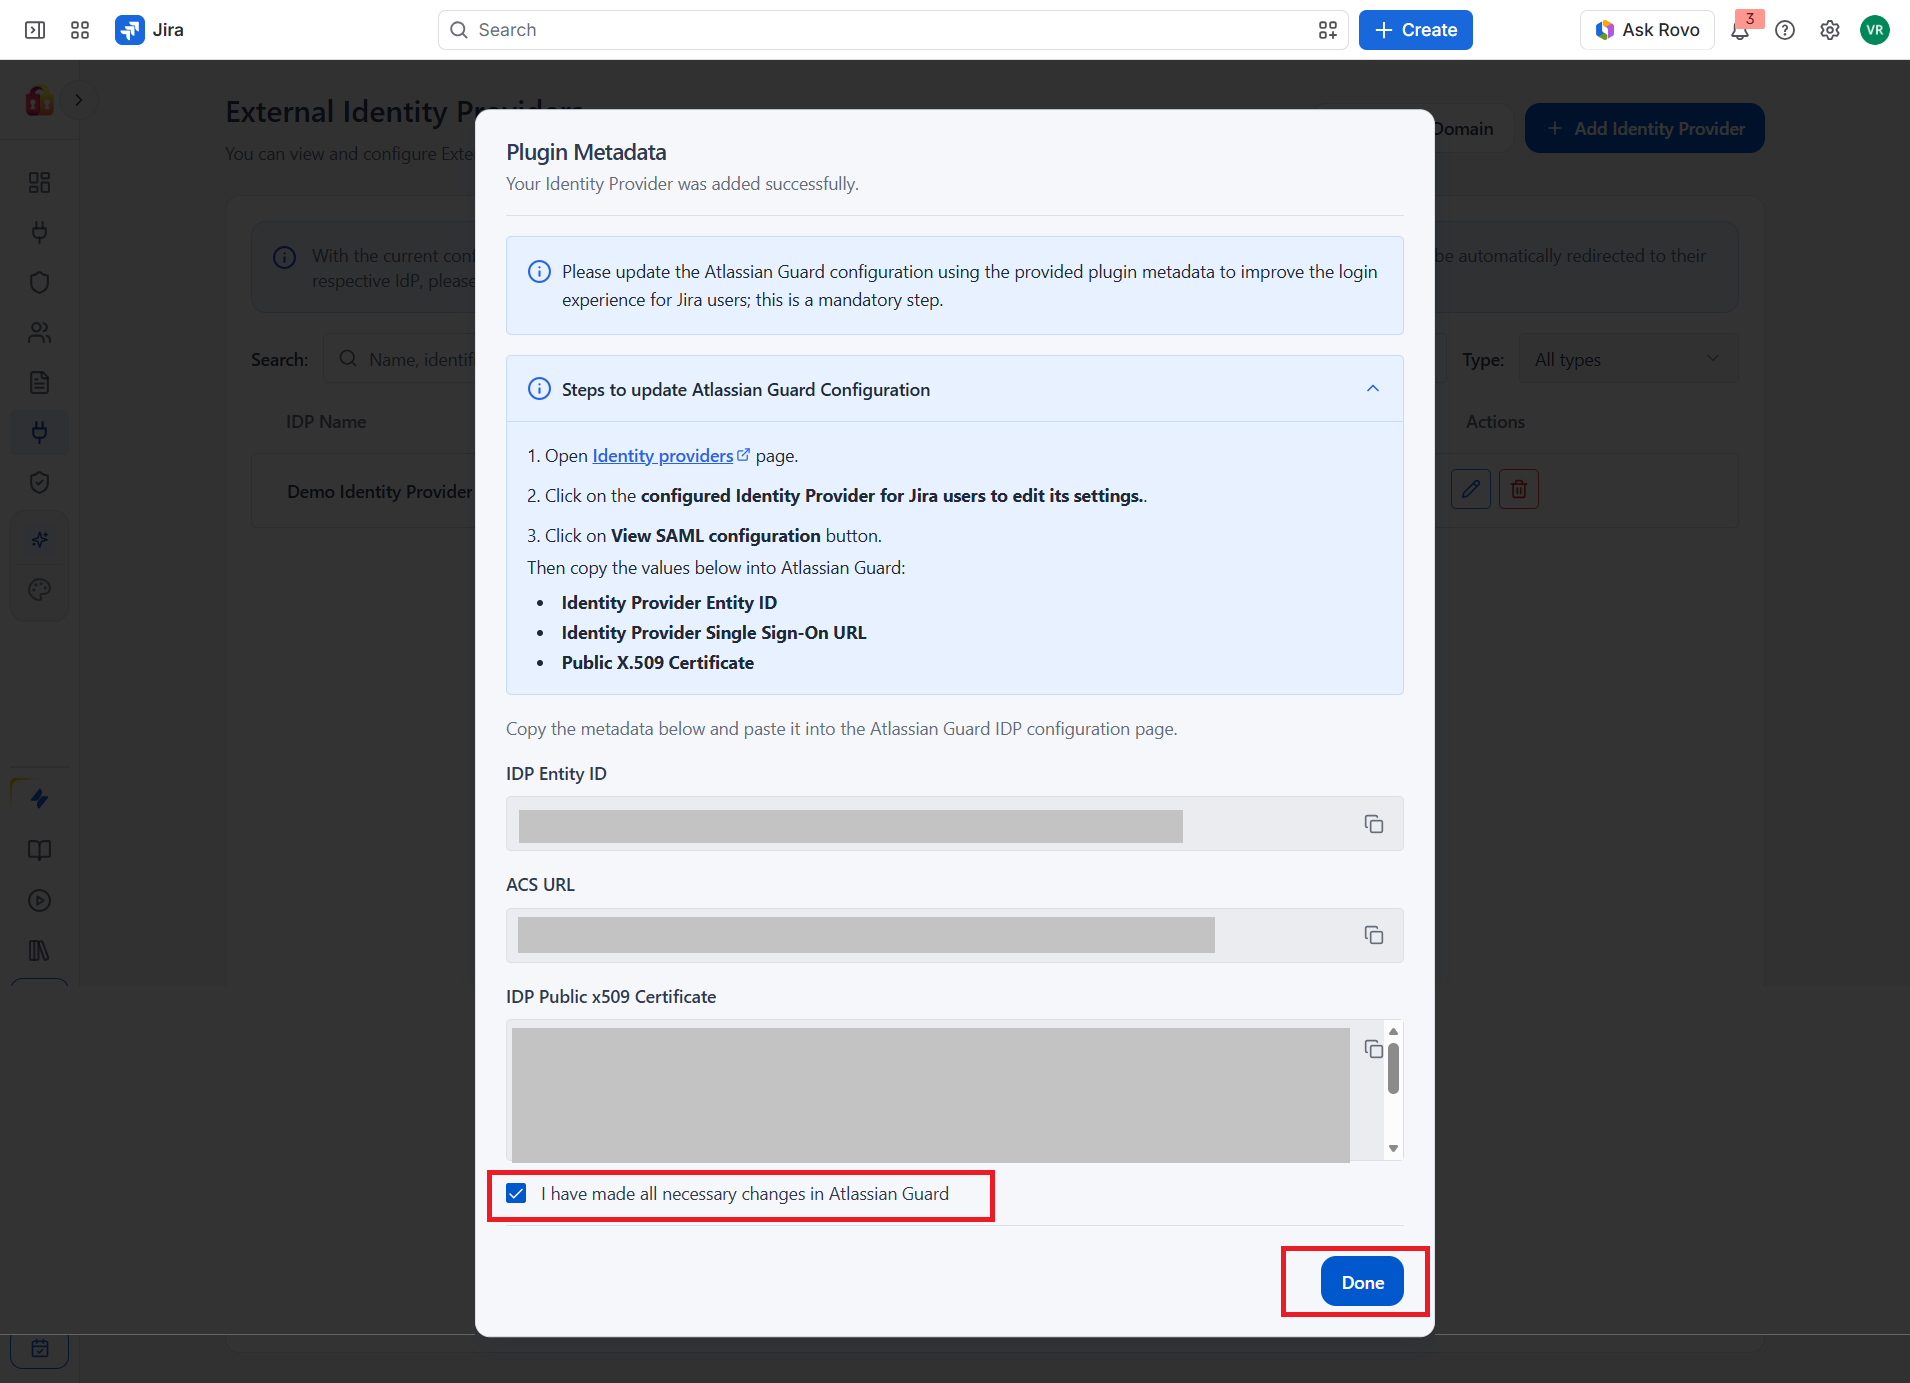
Once the configuration has been saved successfully in Atlassian Guard, return to the plugin. In the confirmation dialog:
- Select the confirmation checkbox indicating that the authentication source has been updated.
- Click Done to complete the Identity Provider setup.
3. Identity Providers Tab Features
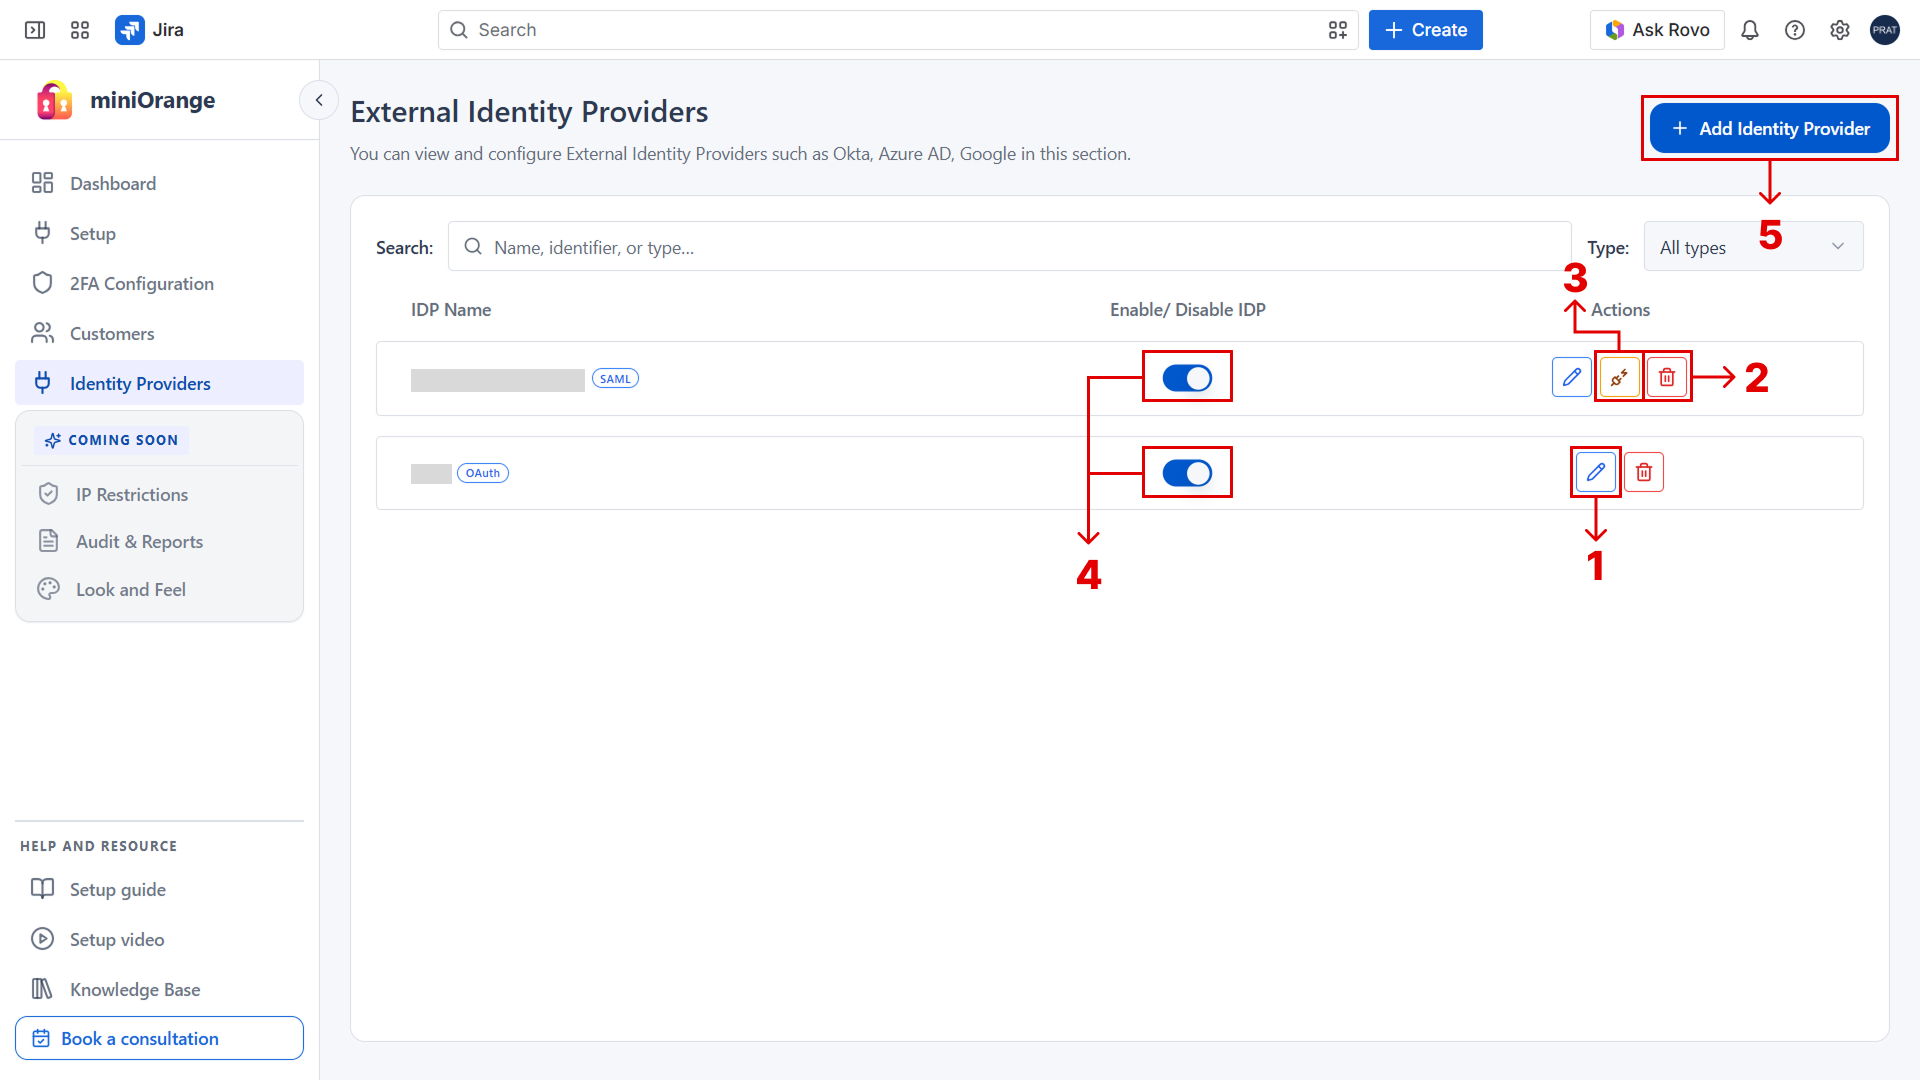
- Edit Identity Provider, modify an existing configuration (for example, updated metadata, certificates, endpoints, or credentials) without creating a new one.
- Delete Identity Provider, permanently remove a configuration. Users authenticating through it can no longer sign in via SSO.
- Test Connection, for SAML, click Test Connection to validate the configuration directly. For OAuth/OIDC, verify by signing in to the Jira Site with a user managed by that IdP.
- Enable / Disable, temporarily control whether an IdP can be used for SSO while retaining its configuration.
- Add Identity Provider, configure an additional Identity Provider.
IP Restrictions Tab
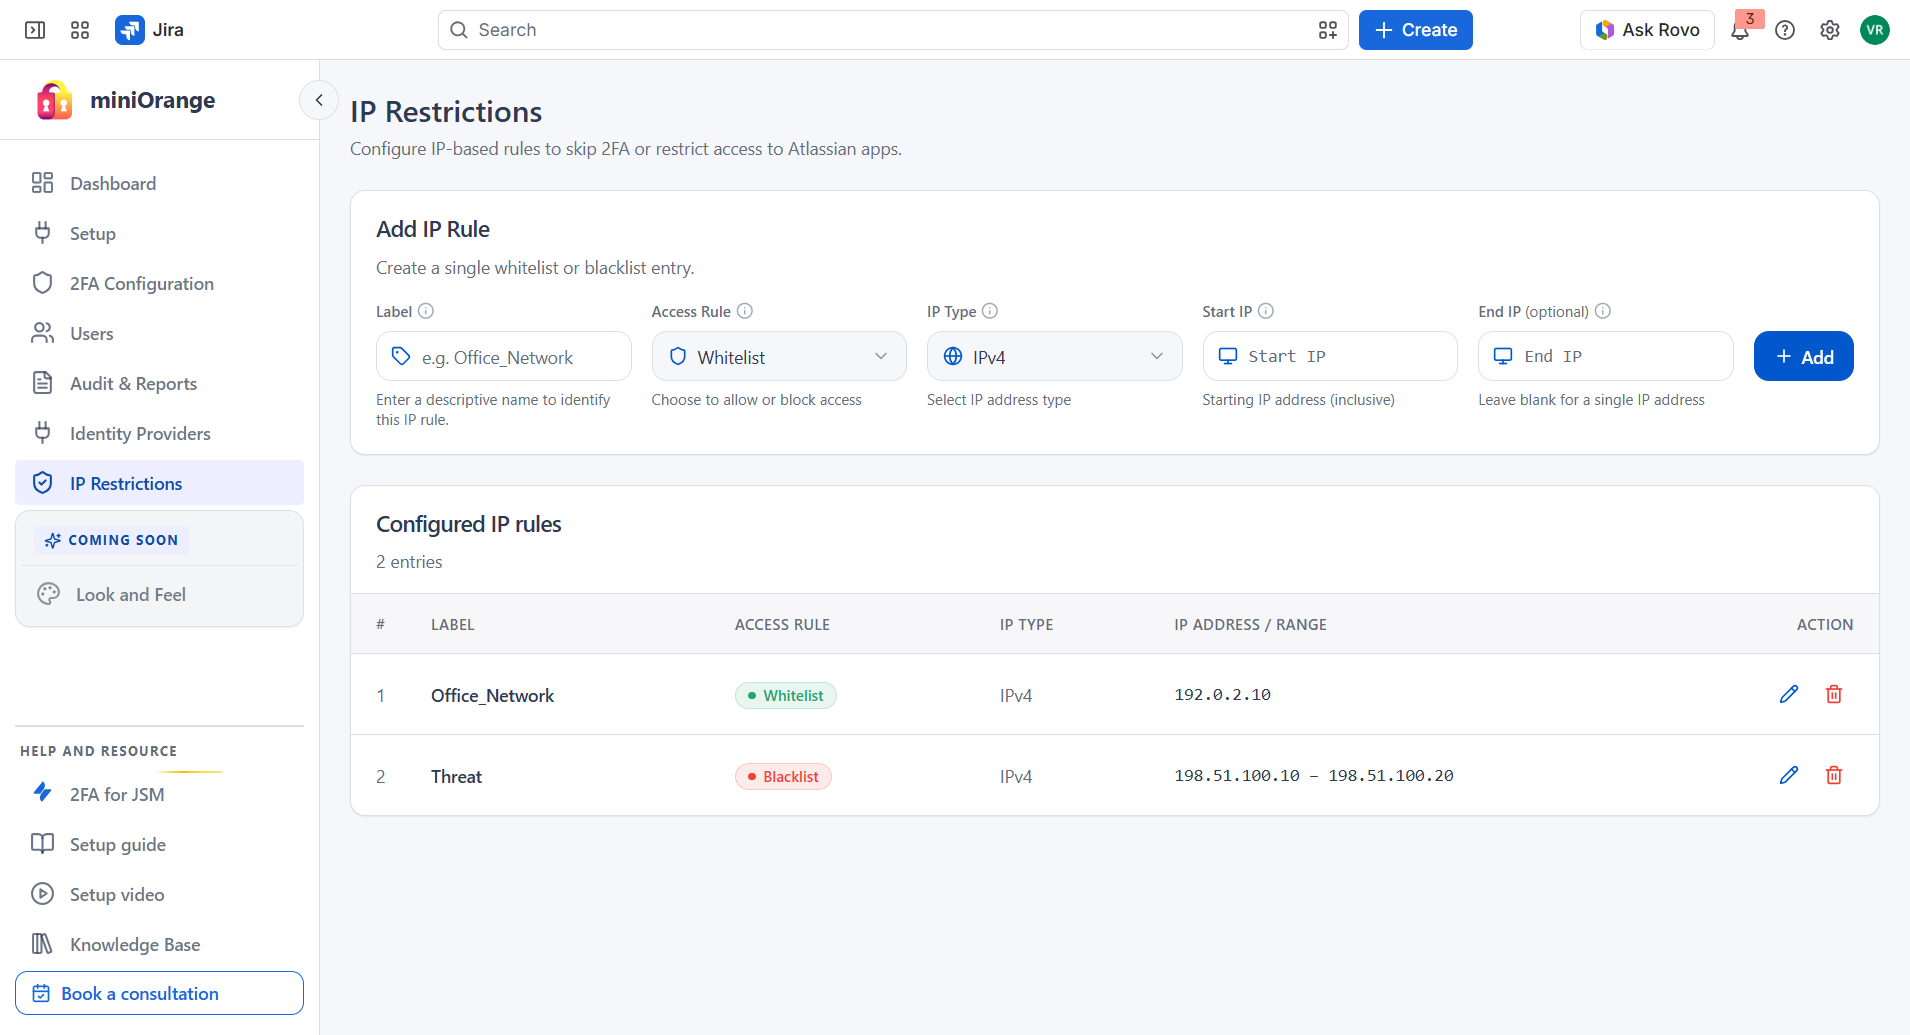
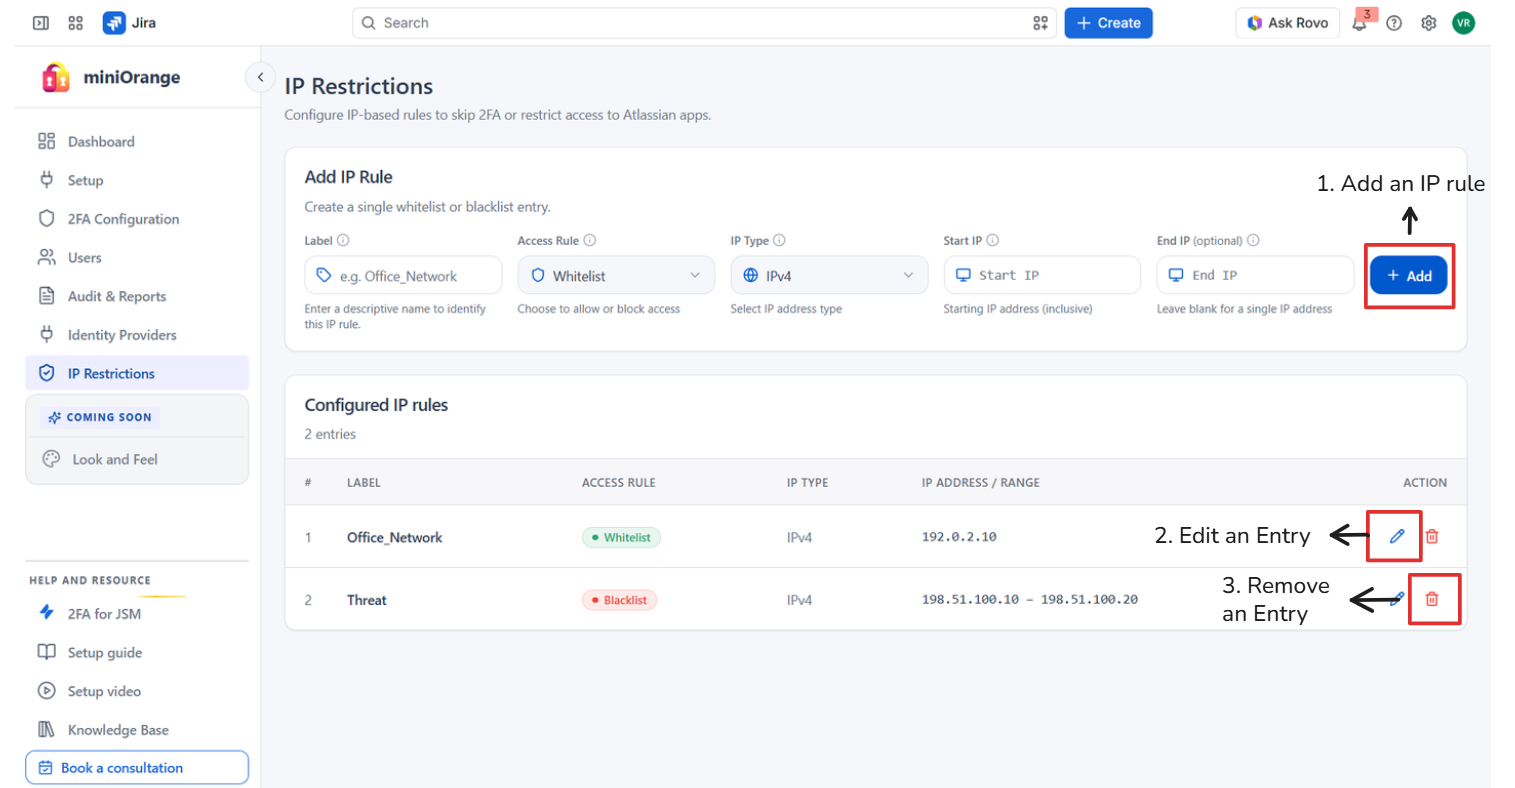
Use the IP Restrictions page to control access to Atlassian apps based on IP address. You can allow trusted IP addresses to bypass 2FA or block access from restricted IP addresses.
1. Add an IP rule
- Step 1: Enter a label. In the Add IP Rule card, type a short name such as Office_Network. The label only helps you identify the entry in the list later. Use letters, numbers, spaces, hyphens and underscores, up to 30 characters and 3 words.
- Step 2: Choose the Access Rule. Select Whitelist to skip two-factor authentication for this IP, or Blacklist to block access from it.
- Step 3: Choose the IP Type. Select IPv4, IPv4 CIDR, or IPv6. The fields to the right change to match.
- Step 4: Enter the address. For IPv4, type the address in Start IP. For a range, type the last address in End IP. Leave End IP blank when the rule is a single address. For IPv4 CIDR or IPv6, type the block in the IP Range (CIDR) field. If the format is wrong, a message appears in red under the field.
- Step 5: Click Add. The entry is saved and appears in the Configured IP rules table below. Use Clear to empty the form and start over.
2. Edit an entry
Click the blue pencil icon in the Action column, type a new name in the Edit label dialog, and click Save.
3. Remove an entry
Click the red bin icon in the Action column, then click Remove in the confirmation dialog. The rule stops applying immediately and cannot be restored, so a removed entry has to be added again.
Additional Resources
Did this page help you?