- Home
- Migration Assistant for Jira and Confluence

DLP Sensitive Data Scanner & Cloud Migration Assistant for Jira and Confluence Data Center
The DLP Sensitive Data Scanner & Cloud Migration Assistant finds personally identifiable information (PII), credentials, financial data, dormant users, duplicate accounts, empty groups and oversized attachments in your Jira and Confluence Data Center instance. You can encrypt, redact or delete sensitive data and clean up users and groups before you migrate to Atlassian Cloud.
This guide walks you through installation, configuration, your first scans and cleanup. The steps are the same for Jira and Confluence.
 Try it for free
1. Overview
Everything in your Data Center instance moves with you to Cloud: inactive accounts, forgotten admin groups, and the credit card number someone pasted into a comment in 2019. The app gives you one place to find these problems, fix them, and prove they were fixed.
The majority of the Migration Readiness Score comes from data violations, the largest single factor.
Atlassian Cloud is billed per user. Dormant and never-logged-in accounts become paid seats if you migrate them.
Atlassian Data Center end of life. After this date, Data Center products and apps get no more support or bug fixes.
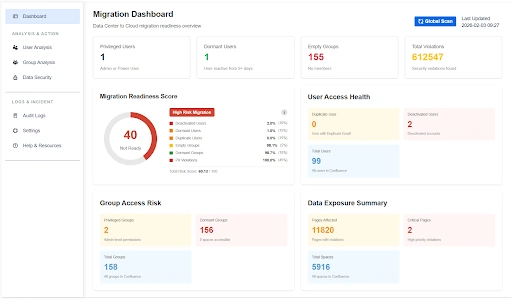
- Migration Dashboard: Readiness score, risk breakdown and a summary of every finding.
- User & Group Analysis: Dormant, duplicate, privileged and never-used accounts. Empty and over-privileged groups.
- Data Security: 40+ built-in regex rules for PII, financial, health and credential data, plus your own.
- Attachment Scanning: Find the largest and unwanted files to reclaim storage before migration.
- Automation: Daily scans, auto-deactivation and auto-encryption on a schedule.
- Audit Logs: Every scan, deletion and encryption recorded with user, target and timestamp.
2. Video Setup Guide
3. Prerequisites
| Requirement | Details | |
|---|---|---|
| Permissions | System Administrator. Needed to install the app, scan across all projects and spaces, and run bulk user actions. | Required |
| Data privacy | Your data stays in your own instance. We do not process any data outside your instance, and nothing is passed to us. | Built in |
| Backup | A recent backup of your instance. Delete actions are permanent. | Recommended |
| Staging instance | A copy of production to try bulk actions and a test migration first. | Recommended |
4. Installation
Install the app for each product you are migrating. The app name on the Marketplace is different for Jira and Confluence:
| Product | App to install |
|---|---|
| Jira | DLP- Sensitive Data (PII, GDPR) Scanner & Cleaner for Jira |
| Confluence | DLP - Sensitive Data (PII, GDPR) Scanner for Confluence |
Install from the Marketplace
- Log in to Jira or Confluence as a System Administrator.
- Go to Administration › Manage apps › Find new apps.
- Search for DLP Sensitive Data and select the miniOrange app for your product.
- Click Free trial and follow the prompts to generate a 30-day license.
- When installation finishes, open the app. It starts on the Migration Dashboard.
Install without internet access
- Download the app .jar from the Marketplace listing.
- Go to Administration › Manage apps › Upload app and upload the file.
- Paste your license key into the app's entry under Manage apps.
Check the installation
Under Manage apps, the app shows as enabled with a valid
license, and opening it shows the Migration Dashboard with the
left-hand menu.
5. Navigating the App
The left-hand menu groups the app into five areas. Jira and Confluence use the same layout. A few labels differ:
| Menu section | Confluence | Jira | Use it to |
|---|---|---|---|
| Migration Assistant | Dashboard | Dashboard | See the readiness score and run a Global Scan |
| Analysis & Action | User Analysis | User Analysis | Find and clean up users |
| Group Analysis | Group Analysis | Find and clean up groups | |
| Data Security | Data Analysis | Scan and remediate sensitive data | |
| Attachment Scanning | Attachment Analysis | Audit attachments by size and type | |
| Logs & Incident | Audit Logs | Audit Logs | Review and export every action |
| Administration | Settings | Settings | Notifications, rules, automation, access |
| Support & Resources | Help & Resources, Getting Started | Help & Resources, Getting Started | Guides and support contacts |
6. Configuration Steps
Configure the app once before your first scan. All settings are under Administration › Settings, which has four tabs: Admin Settings, Regex Rules, Automation and Access (called User Access in Jira).
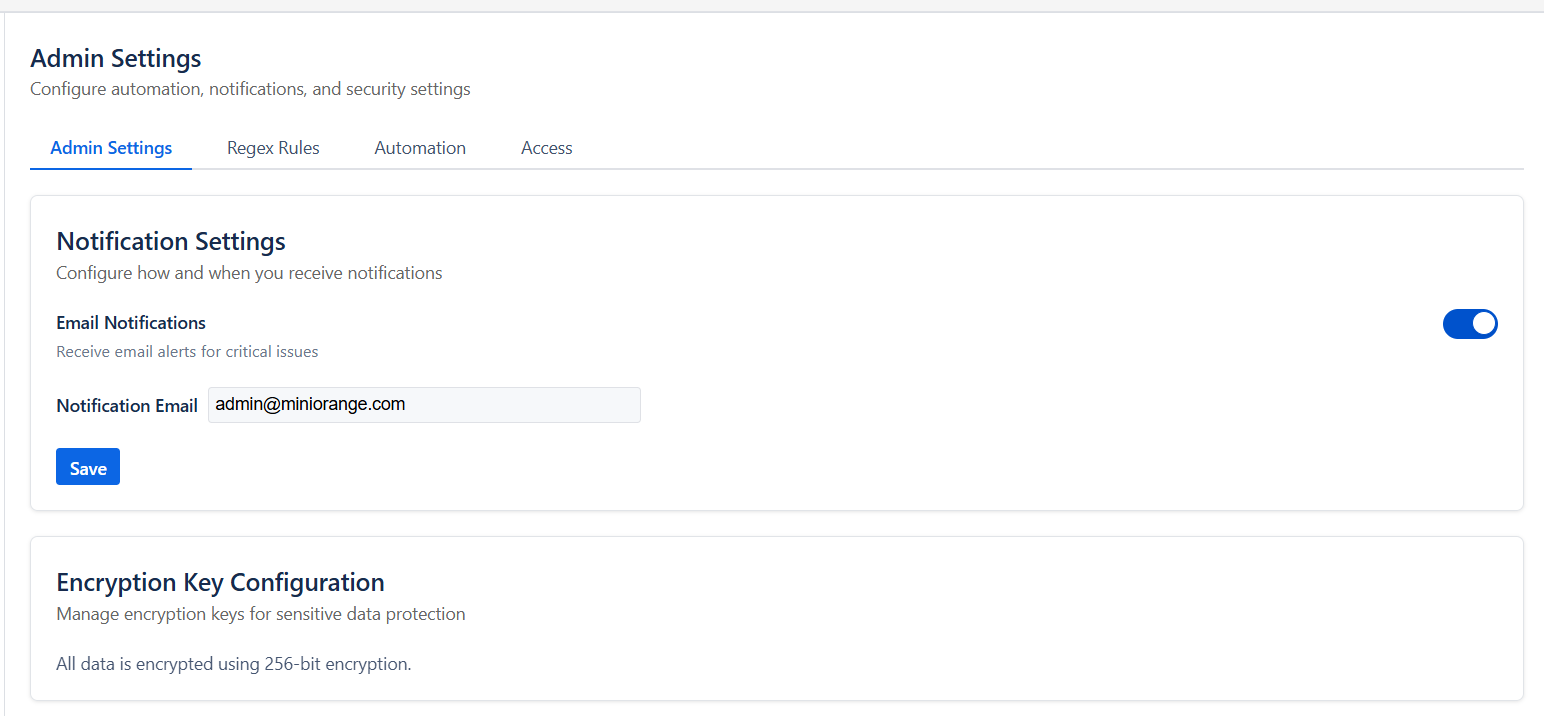
6.1 Admin Settings: email alerts
- Open Settings › Admin Settings
- Under Notification Settings, turn on Email Notifications to receive email alerts for critical issues.
- In Notification Email, enter the address that should receive alerts. A shared team mailbox works best.
6.2 Regex Rules: choose what counts as sensitive
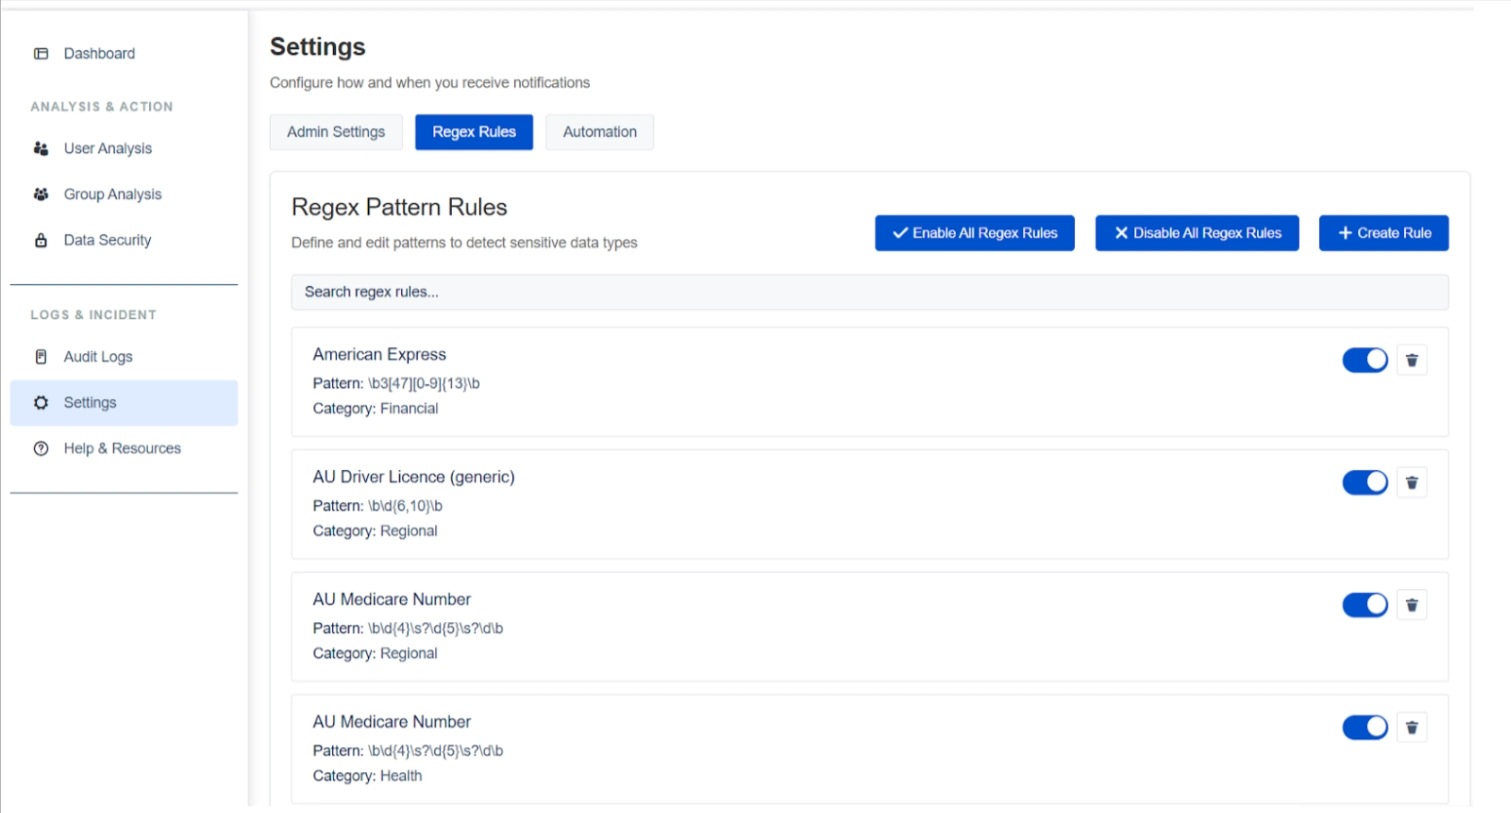
The app ships with 40+ built-in rules grouped into categories such as FINANCIAL, REGIONAL, HEALTH and personal or compliance data. Each rule has a status toggle, so you control exactly what is scanned.
- Open Settings › Regex Rules
- Use Search regex rules to find a rule, or browse the Regex Pattern Rules table.
- Turn off rules for data types your organization never stores. To change everything at once, use Enable All Regex Rules or Disable All Regex Rules.
- To add your own pattern, click + Create Rule and fill in the rule details.
- Click Test on a rule to check it against sample text before you scan.
https://api.prod.example.com, that people have pasted
into pages and issues.
-
Click + Create Rule and add a rule with the pattern
https?://[\w.-]*prod[\w.-]*\.example\.com\S*. Replaceexample.comwith your domain. - Click Test and paste a sample URL to confirm it matches.
- Run a scan from Data Security and search the results for your new rule to see every page or issue that contains a production URL.
6.3 Automation & Cleanup Thresholds
Automation keeps your instance clean between now and cutover. Review each option before you save.
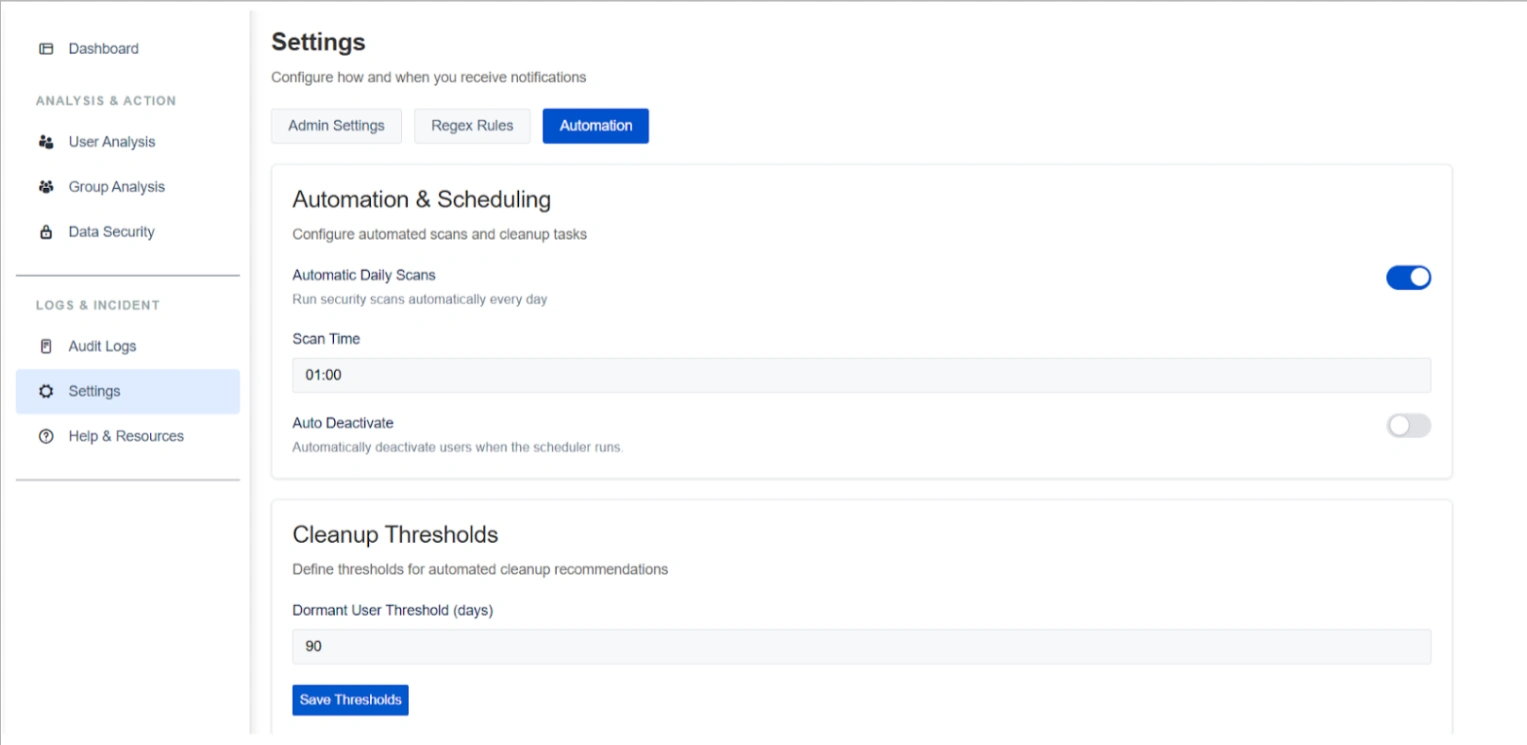
- Open Settings › Automation
- Turn on Automatic Daily Scans and set a Scan Time outside business hours.
- Optional: Turn on Auto Deactivate to deactivate dormant users when the scheduler runs. Use Select Groups to also deactivate members of specific groups.
- Optional: Turn on Auto Encryption, set the Auto Encryption Time, and choose the rules under Select Regex Rules. Auto encryption uses only these selected rules.
- Click Save.
- Under Cleanup Thresholds, set the Dormant User Threshold (days), then click Save Thresholds.
Run cleanup manually first
Auto Deactivate acts on every user that matches. Run User Analysis by
hand at least once and review the list before you turn it on. A
threshold of 30 days suits most teams; use 90 days if contractors or
seasonal staff log in rarely.
6.4 Realtime Scanning
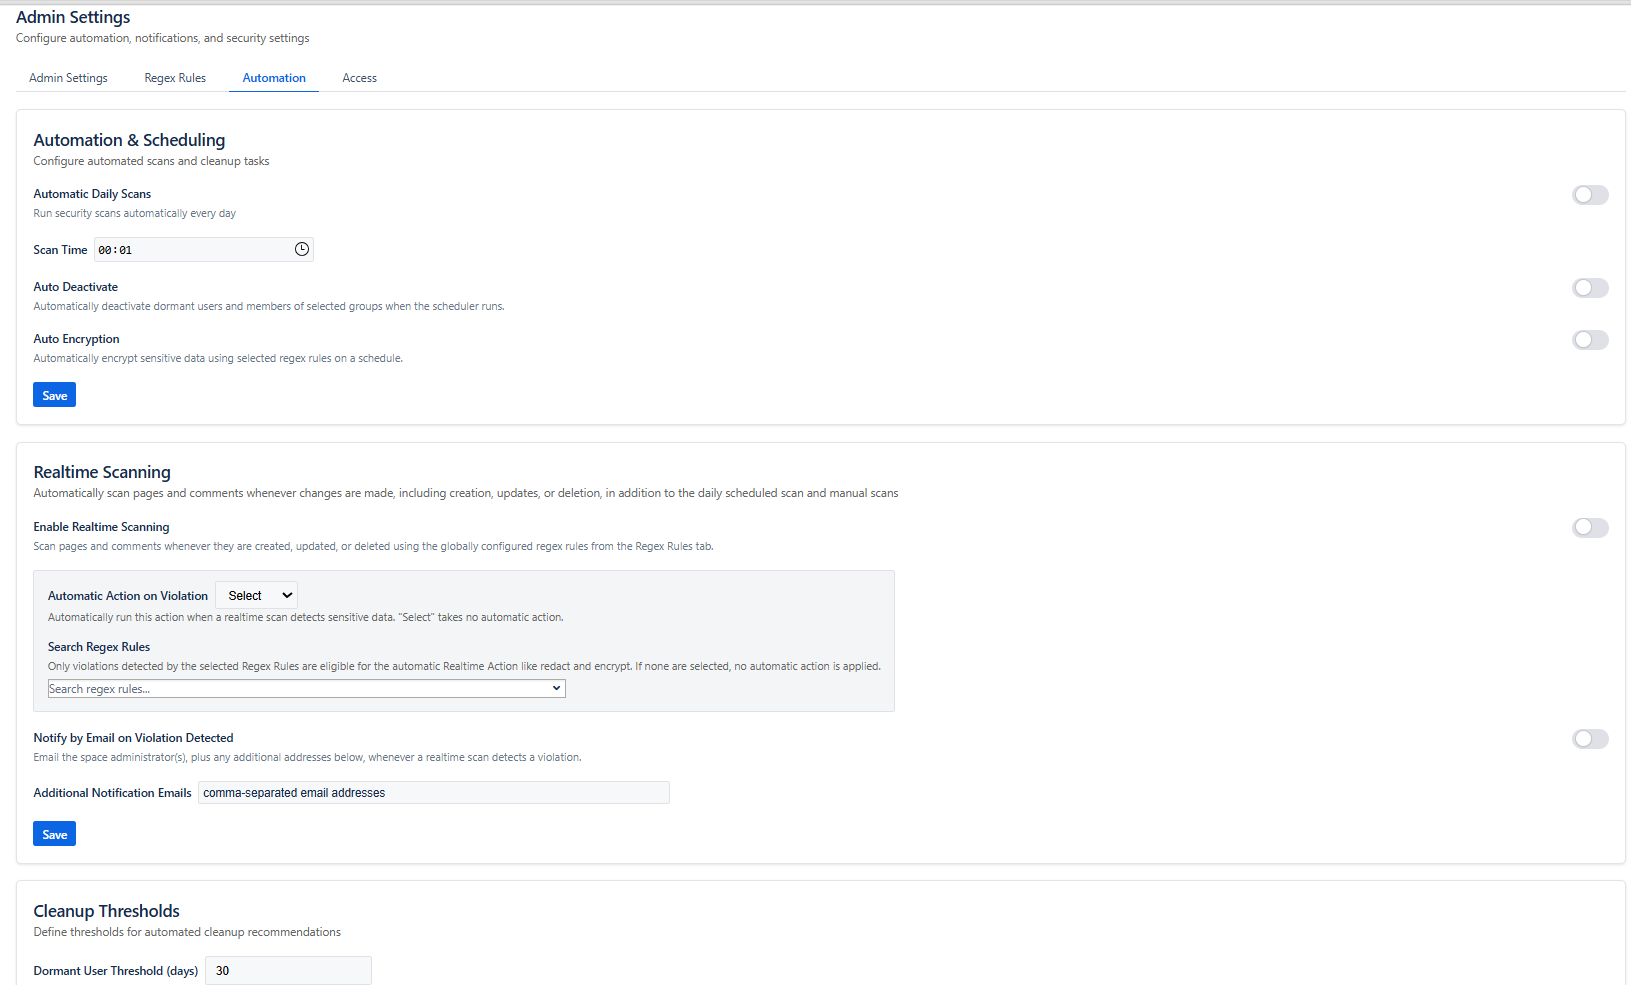
Realtime Scanning checks pages and comments the moment they are created, updated or deleted, in addition to the daily scheduled scan and manual scans. New sensitive data is caught as soon as someone adds it, not the next day.
- Turn on Enable Realtime Scanning. Changes are checked against the rules turned on in the Regex Rules tab.
- Optional: In Automatic Action on Violation, choose Encrypt or Redact. Leave it on Select to detect violations without changing any content.
- If you chose an action, use Search Regex Rules to pick the rules that trigger it. Only violations found by these rules are encrypted or redacted. If you select no rules, no automatic action is applied.
- Optional: Turn on Notify by Email on Violation Detected. The space administrators get an email for every violation found. Add more recipients in Additional Notification Emails, separated by commas.
6.5 User Access (optional)
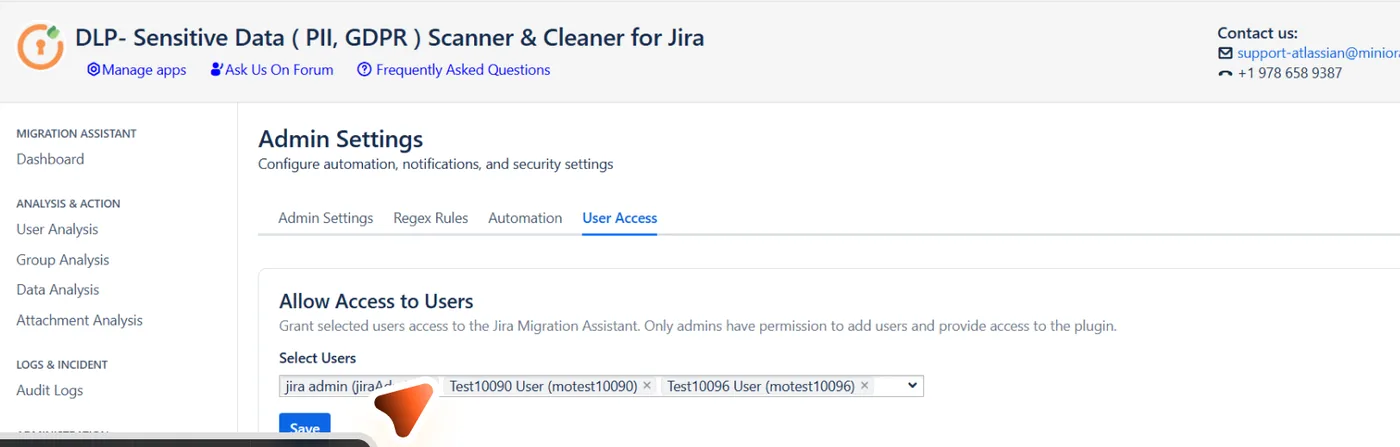
Let team members who are not system administrators run scans and cleanup.
- Open Settings › Access (User Access in Jira).
- Under Allow Access to Users, add people in Select Users.
- Click Save. Only admins can grant access to the app.
7. Running Scans
Scans only read your data. Nothing changes until you choose an action. Run them in this order: identity problems first, because Atlassian's Cloud Migration Assistant blocks migration until every user has a unique email address.
7.1 Global Scan and the Migration Readiness Score
- Open Migration Assistant › Dashboard
- Click Global Scan. When it finishes, Last Updated shows the scan time.
- Note your Migration Readiness Score. This is your baseline. A status such as Fix Issues Before Migrating means there is work to do.
The score is weighted. Fix the heaviest factors first for the biggest improvement:
| Risk factor | Weight | Fix it in |
|---|---|---|
| Data Violations | 45% | Data Security / Data Analysis |
| Dormant Users | 15% | User Analysis |
| Duplicate Users | 15% | User Analysis |
| Deactivated Users | 10% | User Analysis |
| Dormant Groups | 10% | Group Analysis |
| Empty Groups | 5% | Group Analysis |
7.2 User Analysis
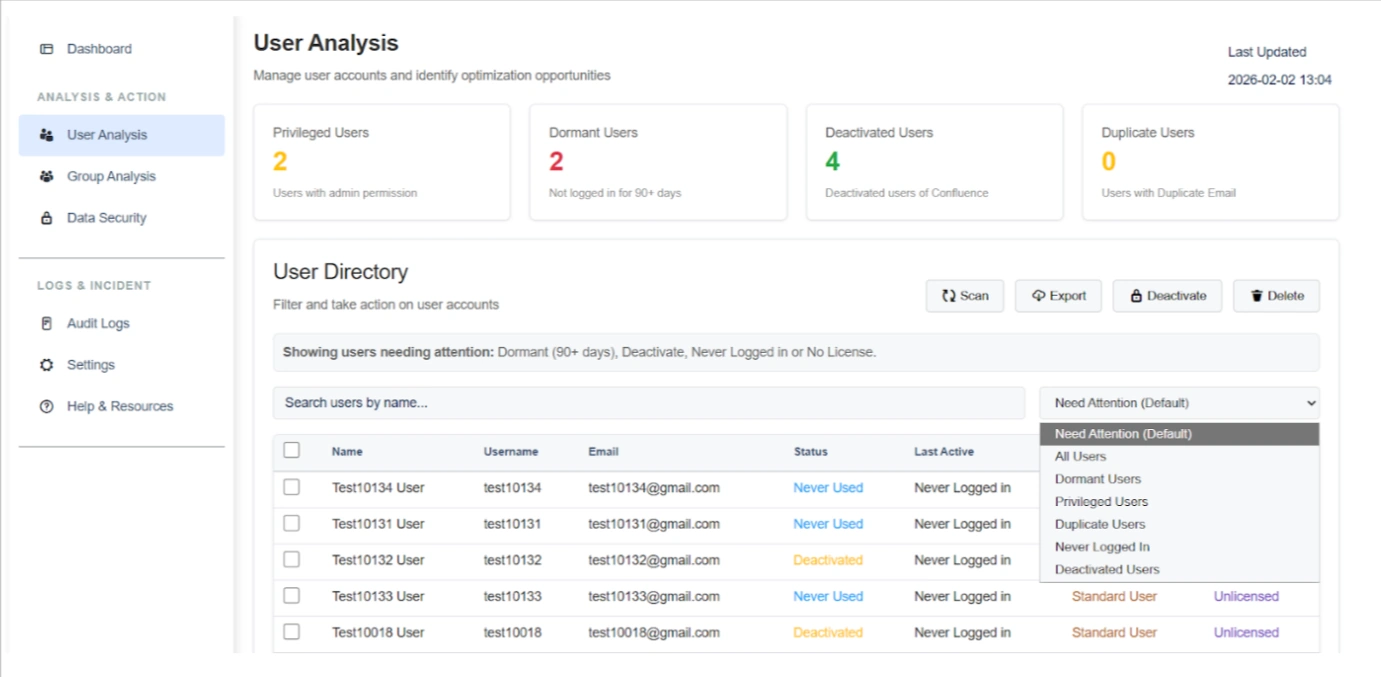
- Open Analysis & Action › User Analysis and click Scan.
- Review the summary cards: Total Users, Privileged Users, Dormant Users, Deactivated Users and Duplicate Users.
- In the User Directory, the filter opens on Need Attention (Default). Switch it to see dormant, privileged, deactivated, never logged-in, duplicate or all users.
- Check the Status, Last Active, Permission and License columns, then select users and click Export, Deactivate or Delete.
Start with duplicates
Fix Duplicate Users first. Then deactivate dormant and
never-logged-in users, and export the list for your license planning.
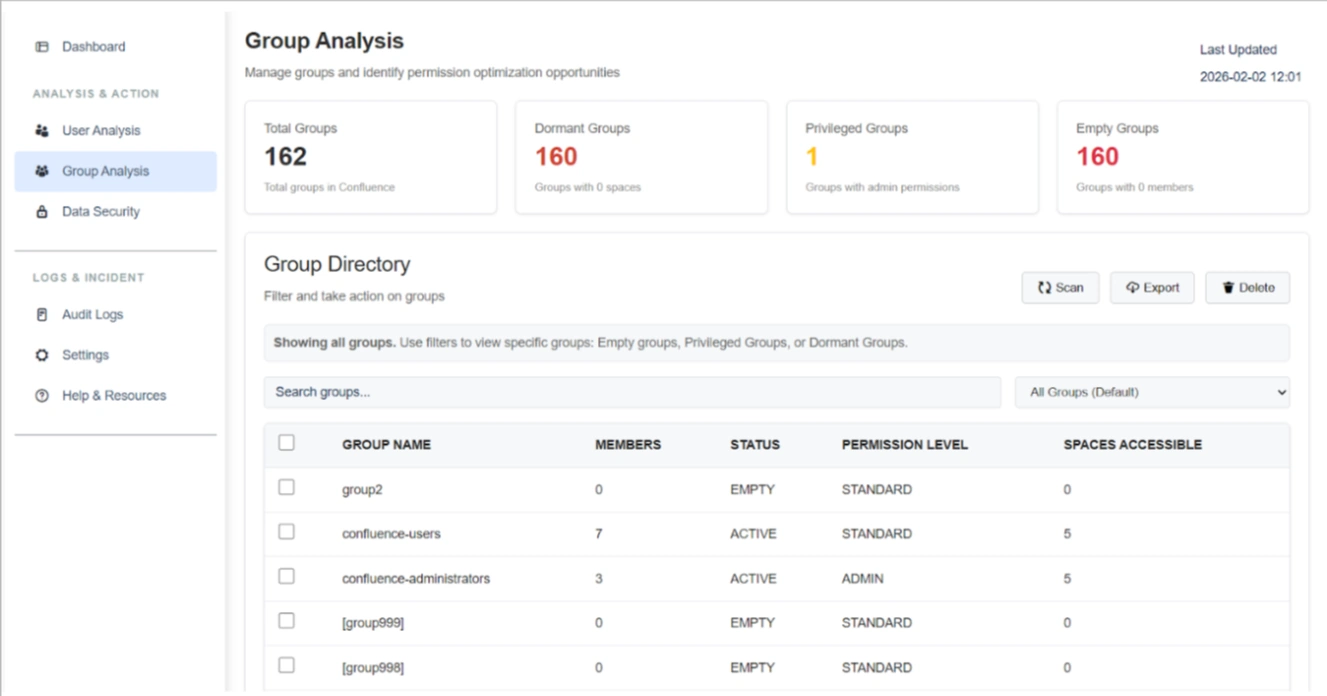
7.3 Group Analysis
- Open Analysis & Action › Group Analysis and click Scan.
- Review Privileged Groups, Dormant Groups (groups with no space access), Empty Groups and Total Groups.
- Change the All Groups (Default) filter to show empty, privileged or dormant groups.
- Click Export to keep a record, then select redundant groups and click Delete.
7.4 Data Security and Managing Violations
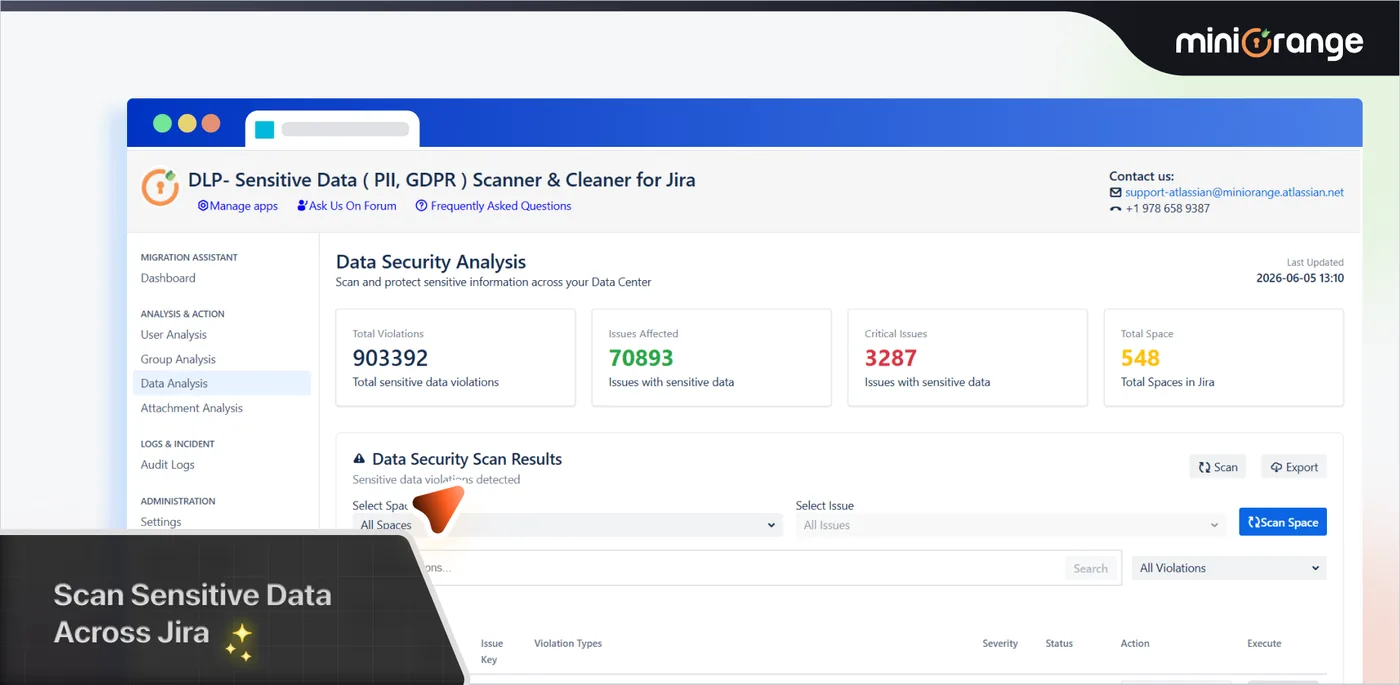
- Open Analysis & Action › Data Security.
- Click Scan to scan everything, or pick a space in Select Space and a page in Select Page (Select Issue in Jira), then click Scan Space.
- Review Total Violations, pages or issues affected, critical items and Total Space.
- In Scan Results, filter with All Violations or search, and check the Pattern matches, Severity and Status columns.
- Click Manage Violations on a row to see each match in context and fix it, as described below.
Manage violations
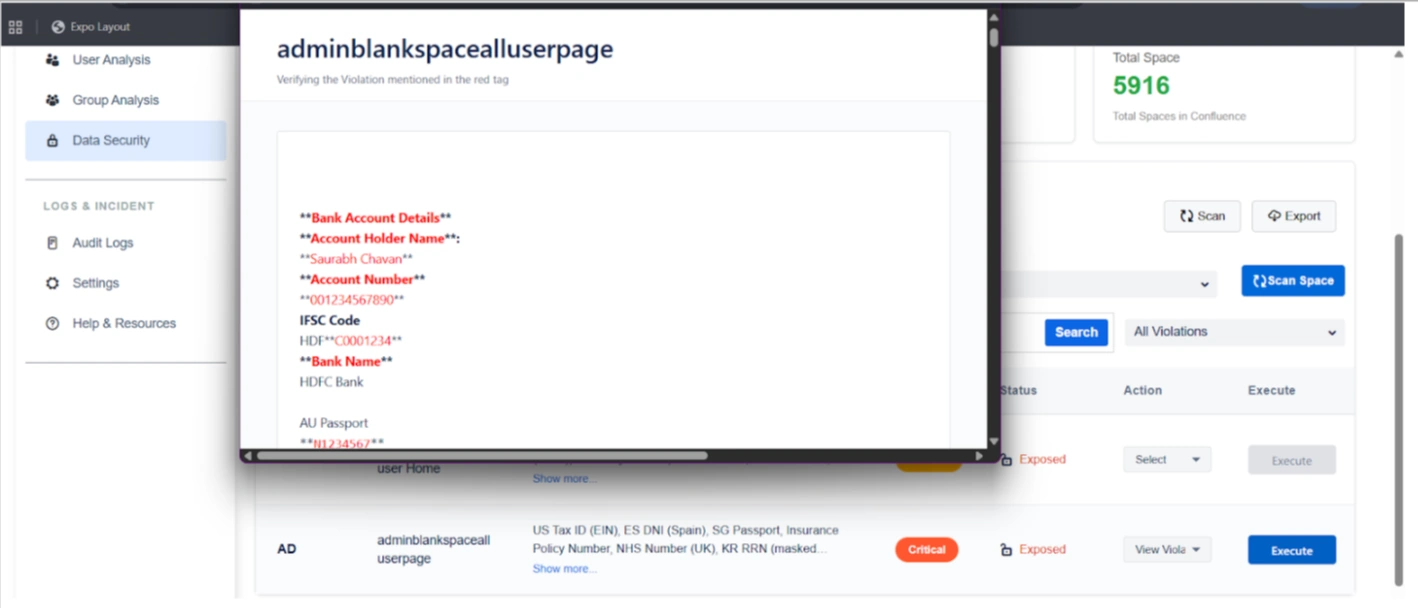
Open Manage Violations on any result. Matches are highlighted in the content. Tick the matches you want to fix, then choose an action in the Remediation Actions panel. For many items at once, select rows in Scan Results and use the Encrypt, Decrypt, Redact or Delete buttons.
What each action does
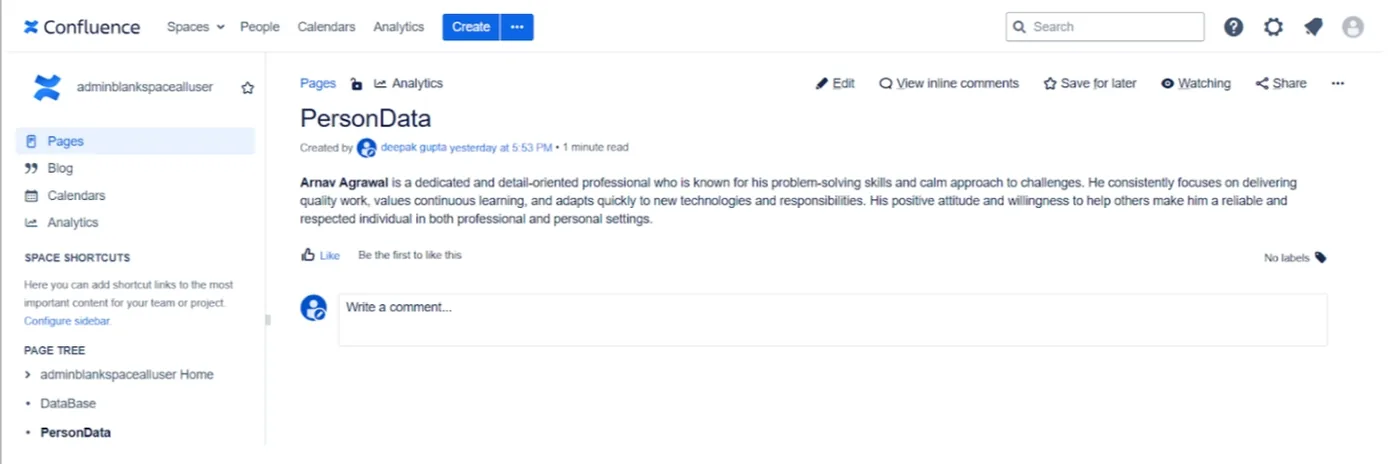
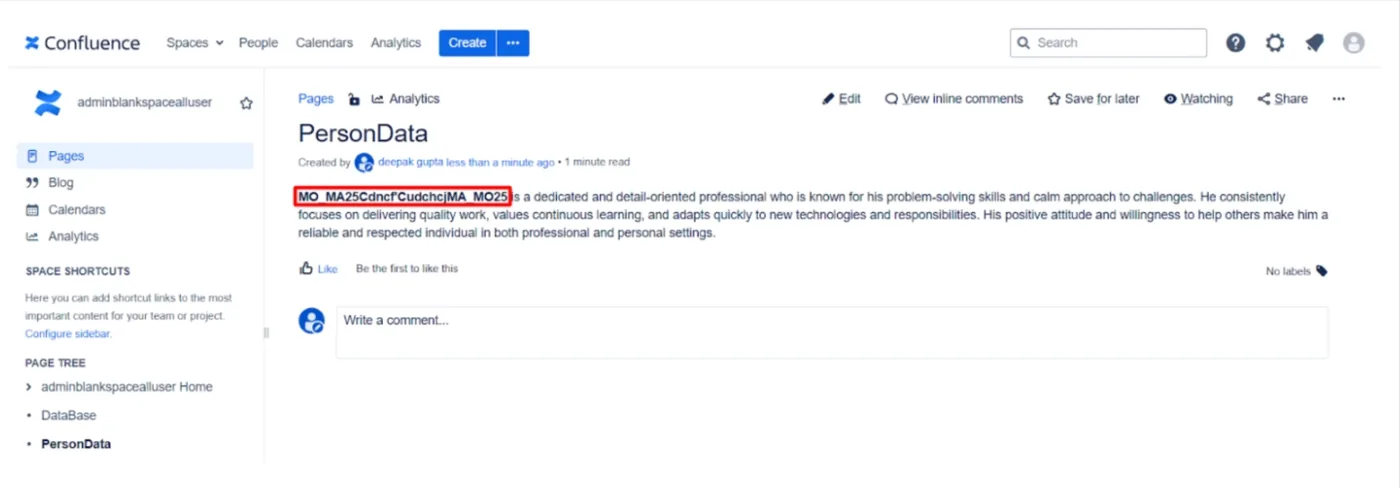
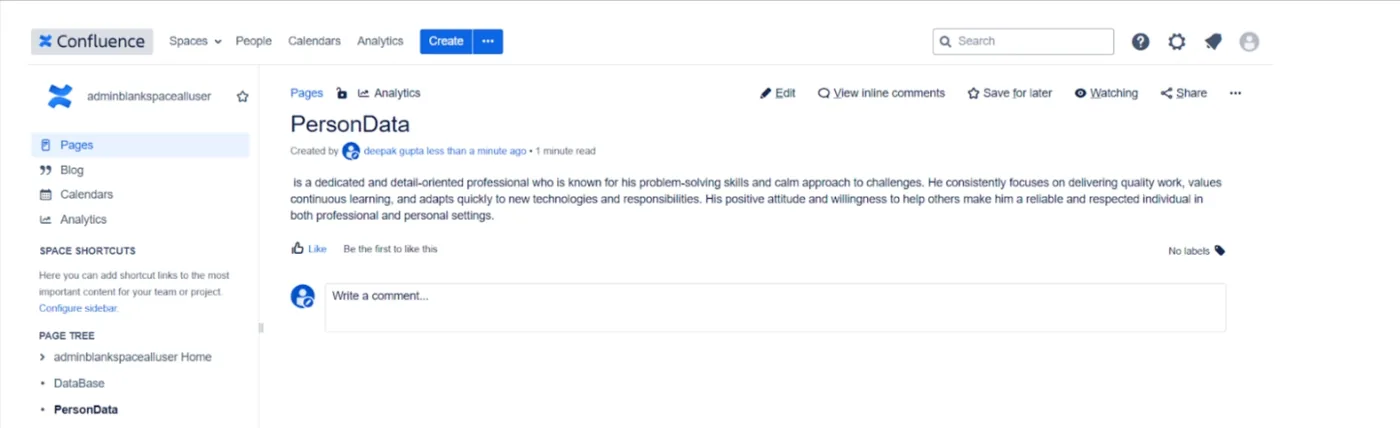
- Before: The original content with a person's name.
- Encrypt: The value becomes an encrypted token. Reversible with Decrypt or in Cloud.
- Delete: The value is removed from the content. Not reversible.
Choose the right action
| Finding | Recommended action | Reversible |
|---|---|---|
| Sensitive data you still need after migration | Encrypt, then decrypt in Cloud with the miniOrange Cloud add-on | Yes |
| Data that should stay hidden on the page | Redact | Check first |
| Data nobody needs, such as old passwords or tokens | Delete, which also removes older versions in Confluence and Jira | No |
| Large or unwanted attachments | Review the export with owners, then remove | No |
Delete is permanent
Deleting sensitive data removes the matched text permanently. In
Confluence/Jira it is also removed from older page versions. Always
check matches with Manage Violations, try on staging first, and
keep a backup.
Working with a migration partner?
Encrypt critical pages and issues before you share access. Partners
can move the data without reading it, and you decrypt it in Cloud
afterwards.
7.5 Attachment Scanning
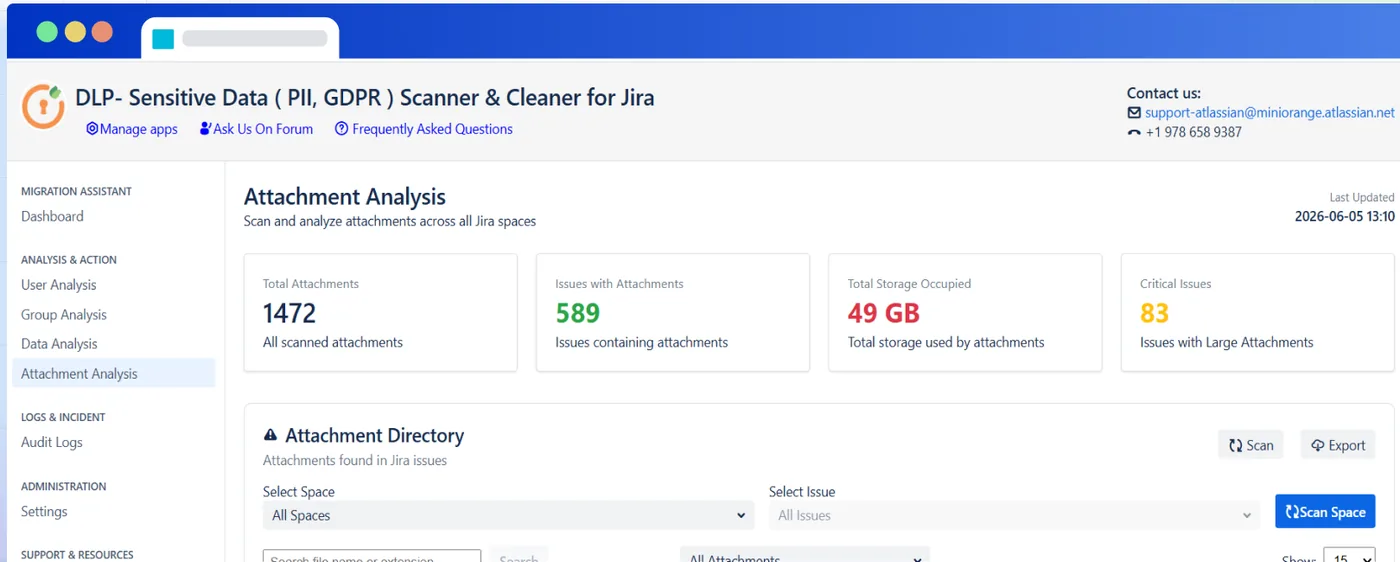
- Open Analysis & Action › Attachment Scanning (Attachment Analysis in Jira).
- Choose a space and page or issue, or keep All Spaces, then click Scan Space.
- Review Total Attachments, Total Storage Occupied and items with large attachments.
- Search by file name or extension, filter the Attachment Directory, and click Export for a report.
8. Audit & Migrate
The Audit Logs page records every scan and cleanup action, whether run by an admin or by the Scheduler. Export it as evidence for your compliance team before you migrate.
- Open Logs & Incident › Audit Logs
- Search Recent Activity by action, user or target. Each row shows Action, Performed By, Target Entity, Timestamp, IP address and Status.
- Click Export to download the audit trail.

9. Pre-migration checklist
Tick each item as you go. Your progress is saved in this browser.
10. Additional Resources