Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×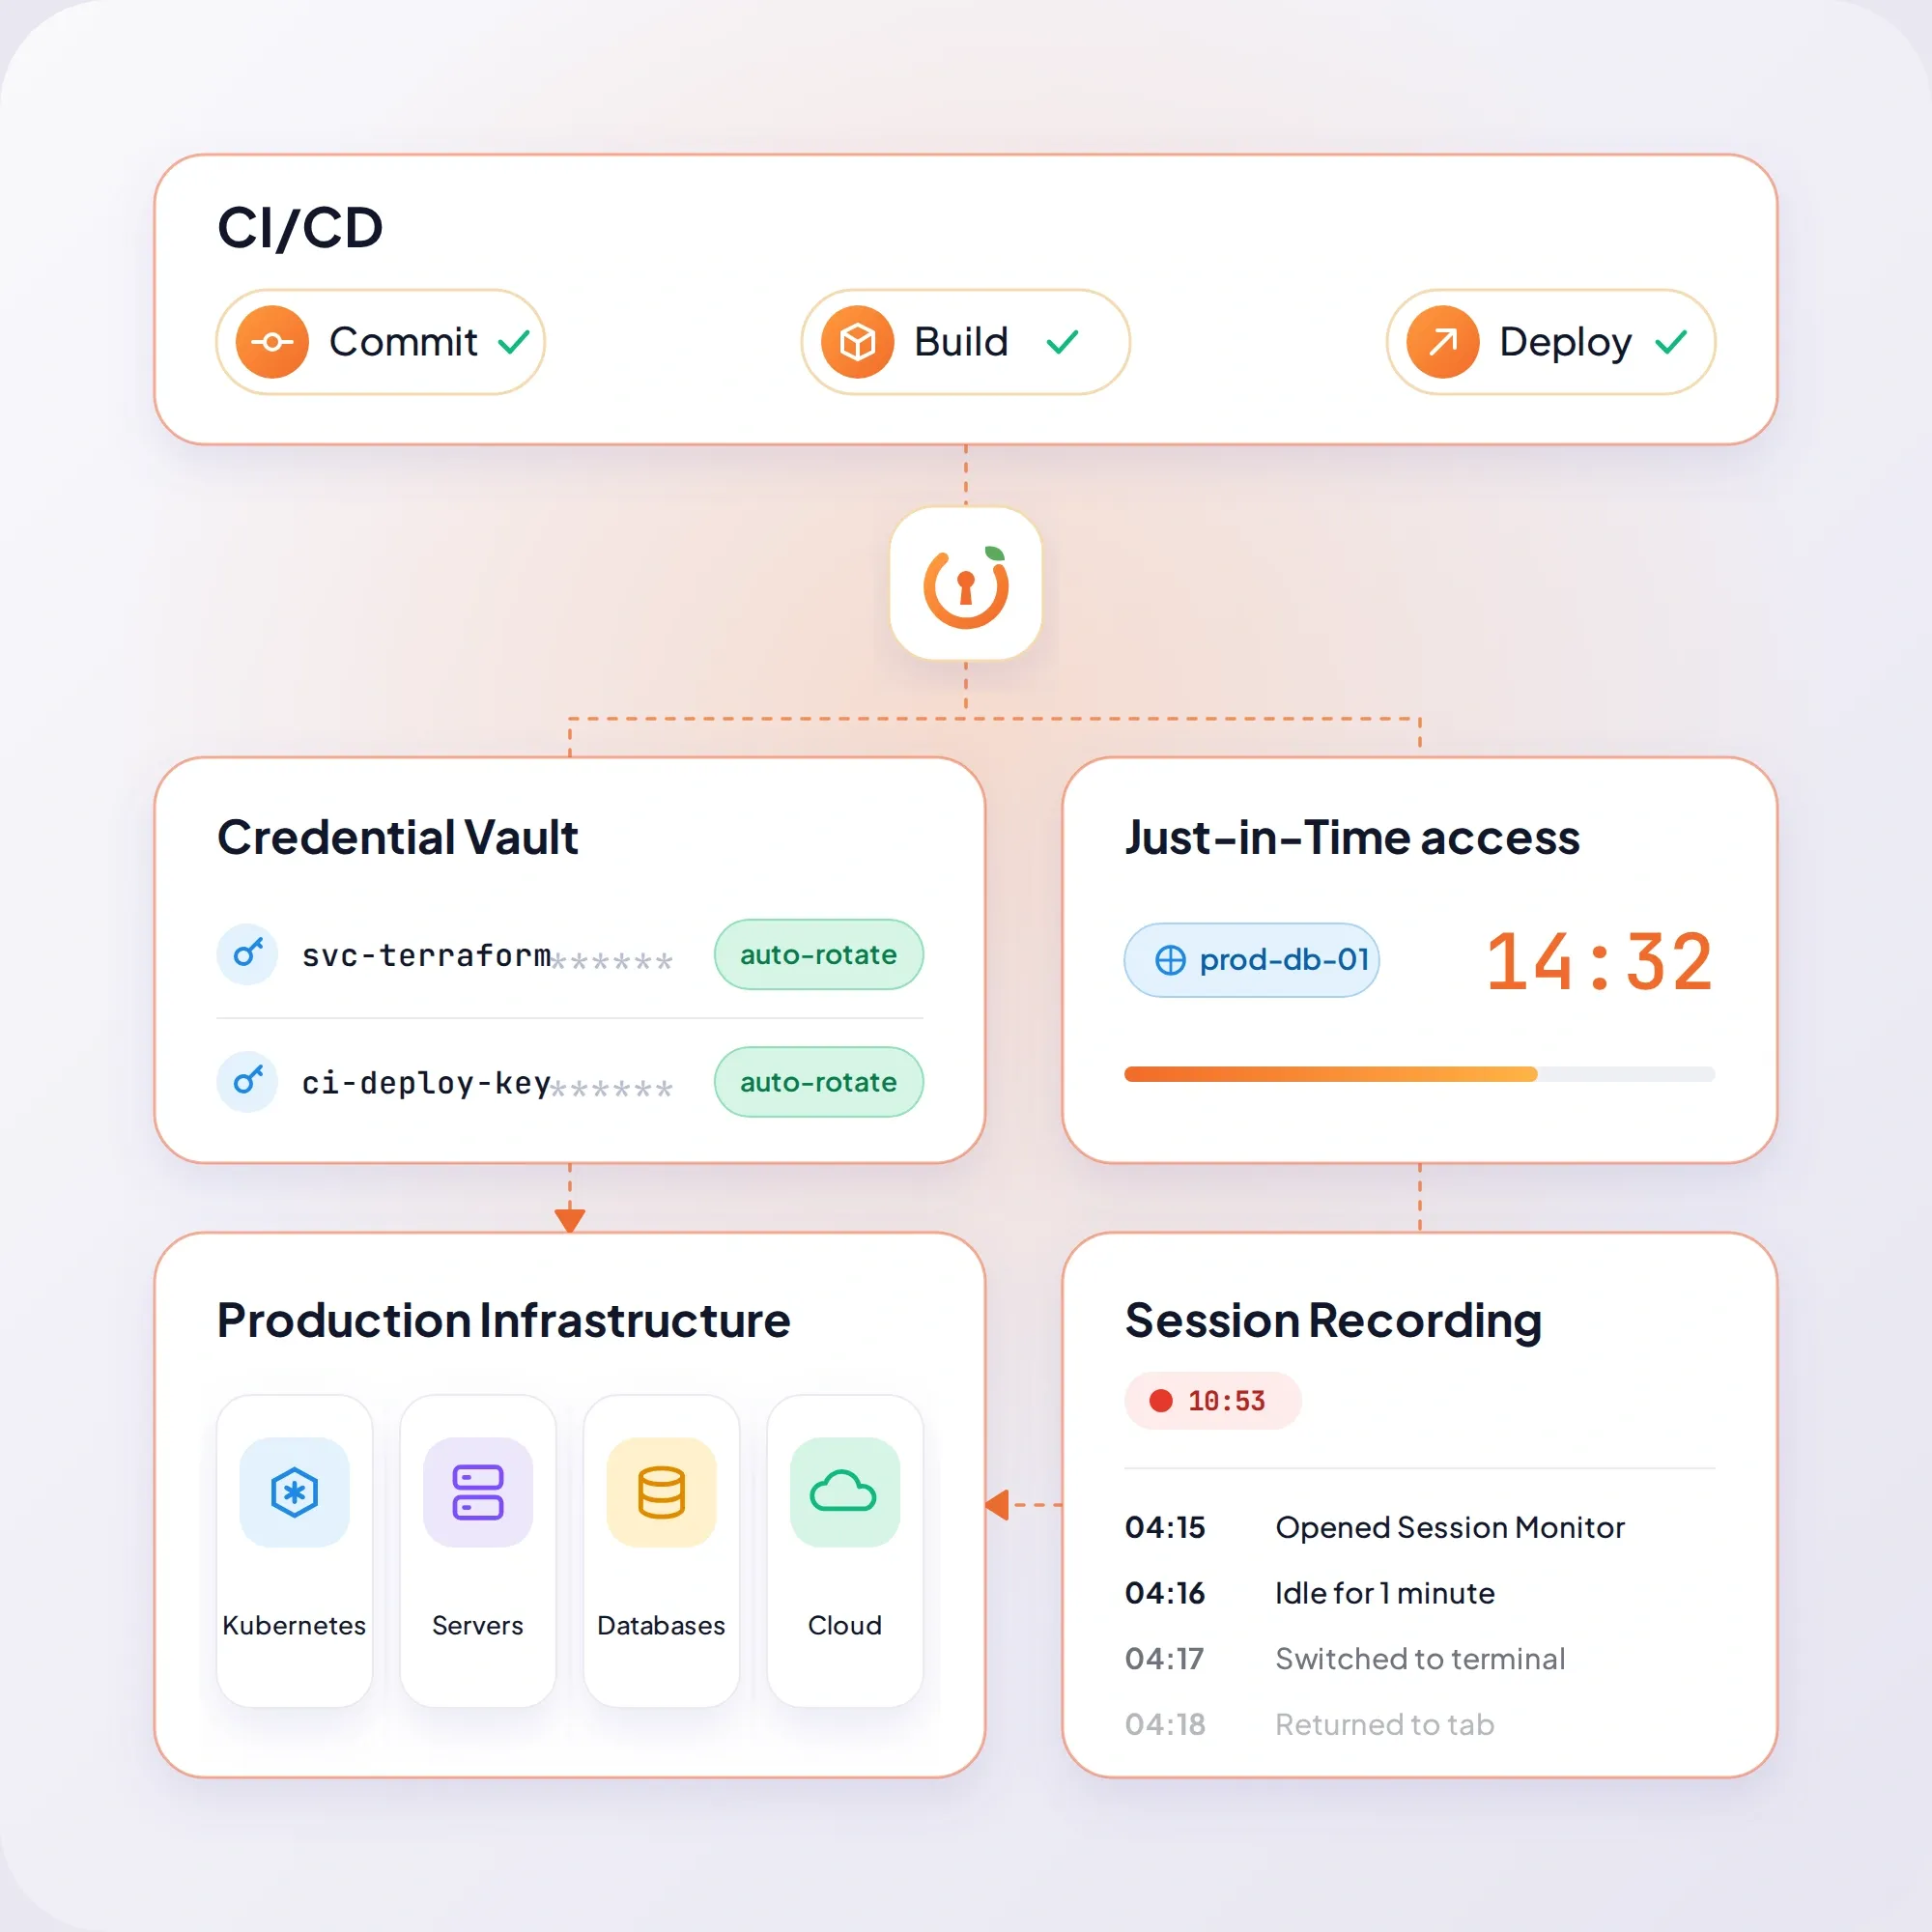
DevOps teams need privileged access to build systems, deployment environments, production servers, and cloud infrastructure. But it becomes risky when access exceeds or outlasts the task, teams use shared credentials, and there is no transparency into privileged activity.
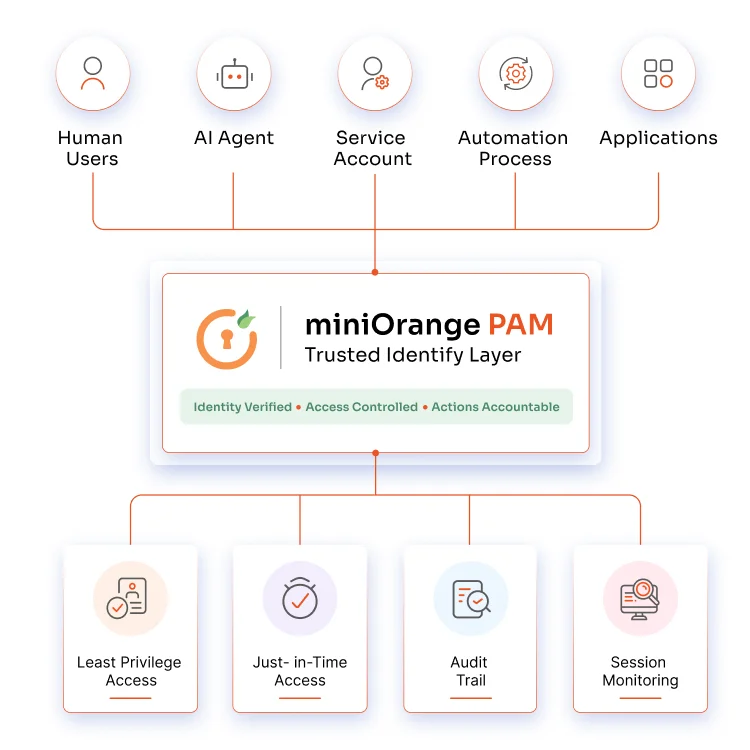
The miniOrange PAM solution addresses these risks by automating credential management and enforcing least privilege. It gives you a centralized dashboard to manage credentials and access controls, enforce restrictions, and monitor privileged sessions in real time.
Explore comprehensive PAM features, integration methods, compliance benefits, and everything you need in one place.
Your download should start now. If not, please email us at idpsupport@xecurify.com.
Please enter a valid email-id
Securing a fast-moving DevOps environment comes with unique roadblocks. We solve them.

Developers often embed API keys, tokens, and passwords directly into code or scripts. If a repository is breached, your entire infrastructure can be compromised.

Developers are often given full root or excessive permissions. In most cases, they do not need it. The potential damage is much greater if one of their accounts is compromised.

When several engineers use the same administrator password or SSH key, accountability becomes difficult. Revoking access for one person can also require changing credentials used by others.

Always-on access pathways to critical databases and servers create a permanent attack surface for attackers to exploit. A stolen credential may remain useful after the original task is complete.

When multiple engineers share root accounts, you cannot trace actions back to a specific user. This also creates challenges during audits and when fulfilling compliance requirements.

A typical DevOps environment may span cloud platforms, on-premises servers, databases, containers, source control systems, and infrastructure automation tools. Securing it all is a challenge.
Protect your pipeline from end to end. We provide the controls you need to lock down your DevOps workflows.
Centralize privileged credential vaulting and rotation. Automatically inject secrets into your pipelines precisely when they are needed. Reduce direct credential exposure.
Give developers and operations teams temporary, time-bound access to production systems that automatically expires when the job is done. Reduce the number of standing privileges.
Enforce the principle of least privilege. Restrict access to privileged accounts and infrastructure across development, staging, and production environments based on the user’s role.
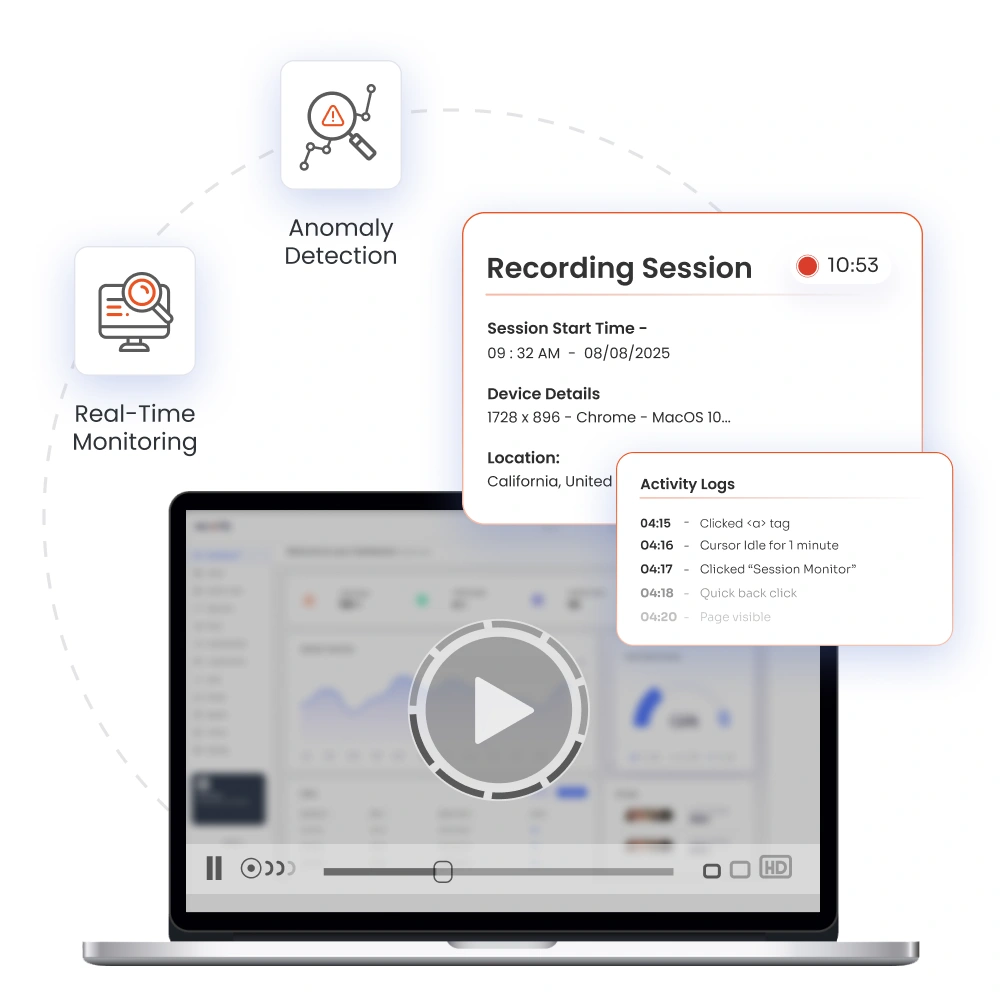
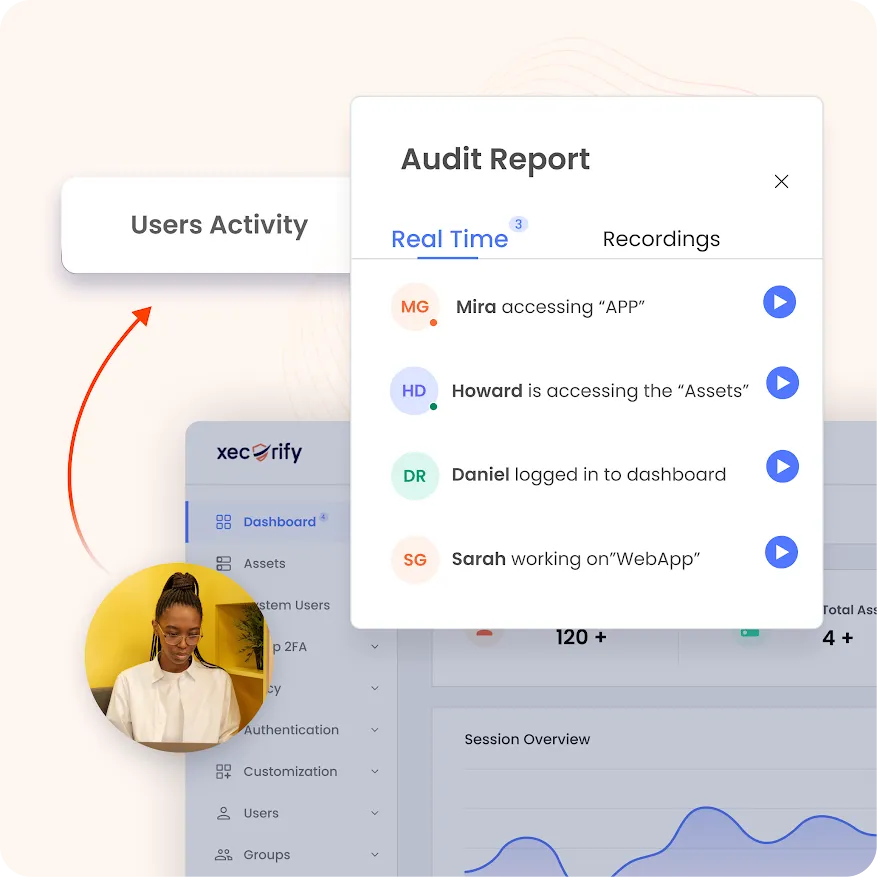
Know exactly what happens during a privileged session. Monitor and record privileged activity to ensure accountability and terminate a privileged session if you notice anything suspicious.
Control privileged remote access to servers and administrative environments. Provide secure, audited pathways without relying on the unmanaged sharing of privileged credentials or exposed SSH keys.
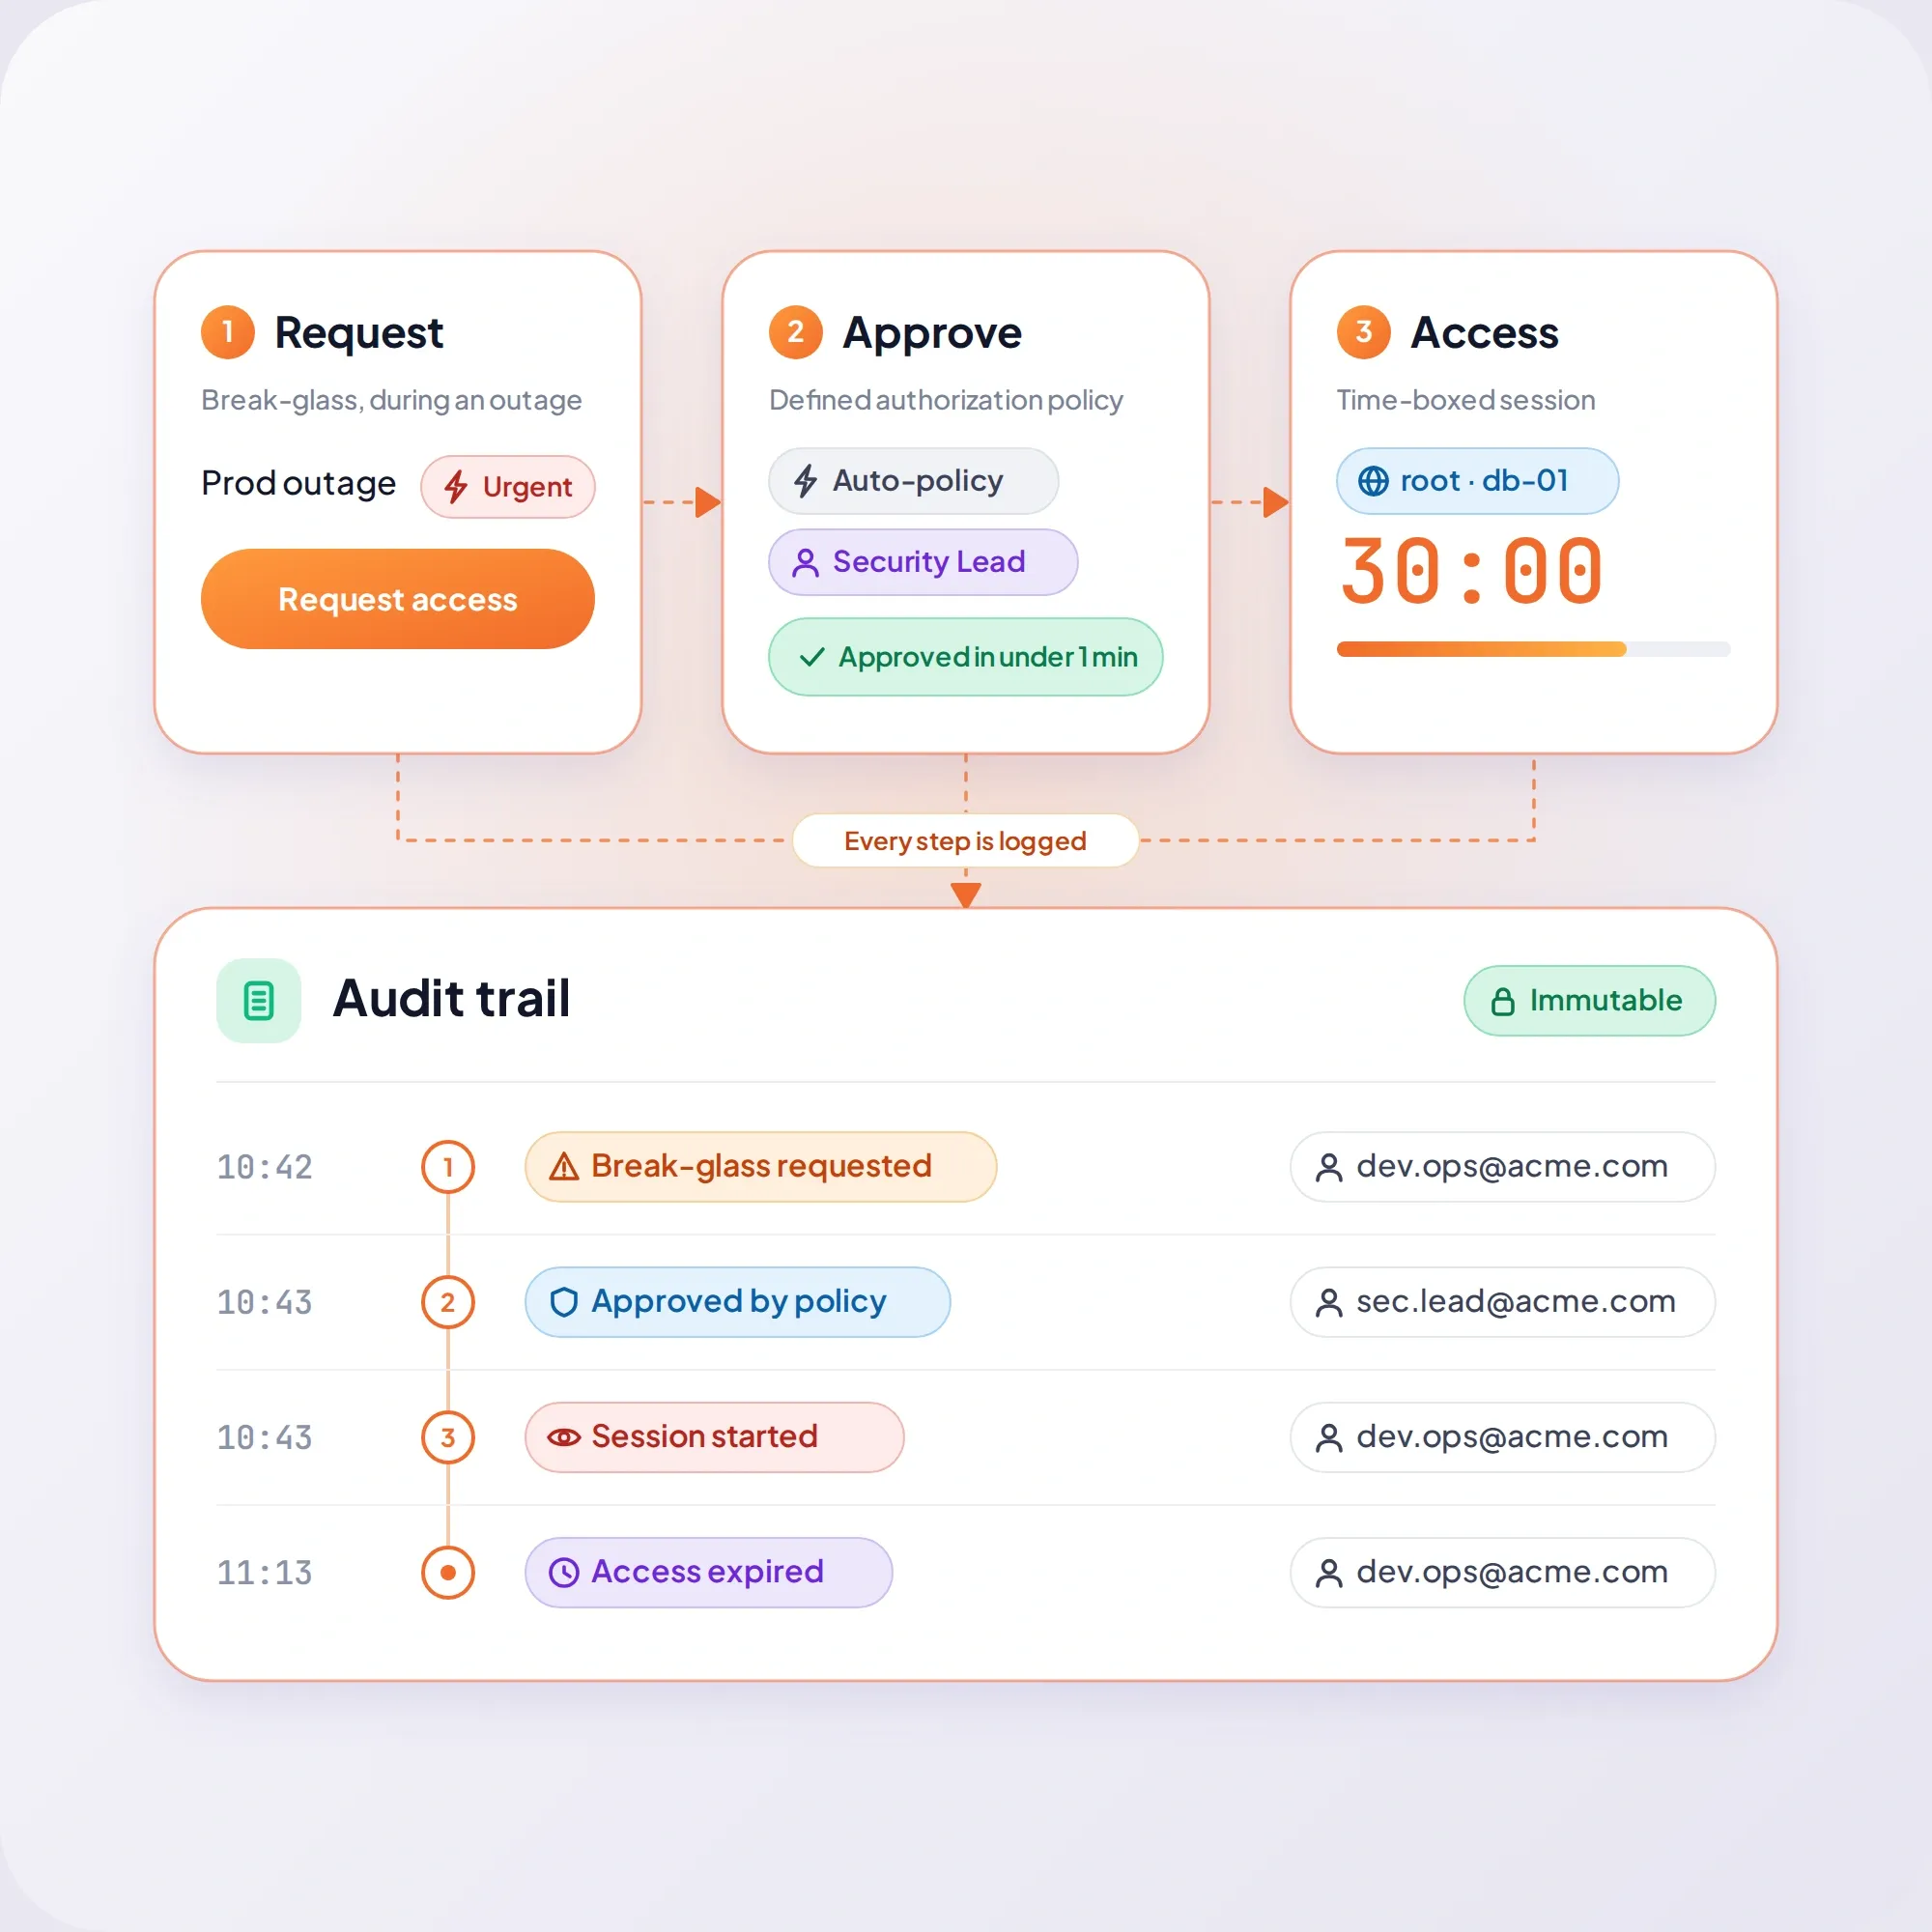
Control exceptional administrative access during outages or security incidents. Use defined authorization policies and maintain strict audit trails for all emergency access.
Maintain audit records and support privileged session recording and reporting. Conduct security reviews and prepare evidence for compliance requirements.
Address the risks associated with AI agents, service accounts, automation accounts, and other non-human identities that require privileged access to function.
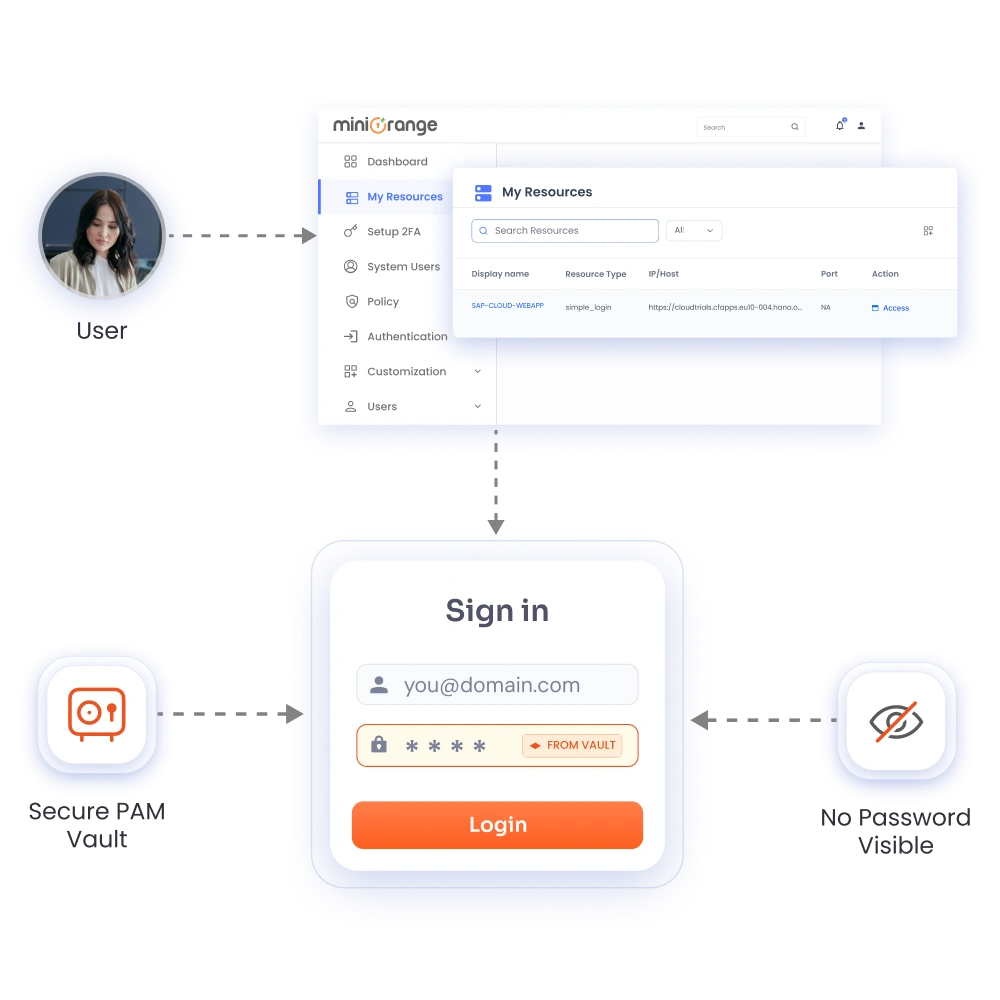

You need a PAM solution for Terraform AWS DevOps workflows and everything in between. miniOrange integrates smoothly with your existing stack.




Manage privileged access across supported cloud, on-premises, and hybrid environments from a centralized platform. Apply credential protection, JIT access, granular permissions, and session oversight to supported resources.
Get round-the-clock technical support for deployment, integration, troubleshooting, and other PAM requirements. Work with the support team to address your environment and implementation needs.
Secure supported servers, databases, and other resources without installing agents on every target system. The agentless access model reduces endpoint maintenance and simplifies access management across distributed infrastructure.
Choose a licensing option that fits your organization's requirements. Discuss your users, assets, required capabilities, and deployment model with miniOrange to identify a suitable plan.
Start a free trial with us - the next step is all yours
PAM for DevOps is the practice of securing privileged accounts, credentials, and access to critical systems used throughout software development and deployment. It helps teams enforce least privilege, limit standing access, protect privileged credentials, and monitor sensitive activities. miniOrange PAM provides these controls for supported resources across cloud, on-premises, and hybrid environments.
miniOrange PAM supports privileged access management across supported AWS and hybrid environments. However, access to AWS resources does not automatically establish a native integration with every Terraform or CI/CD workflow. If you need a PAM solution for Terraform AWS DevOps, confirm your required API calls, credential exchange, automation path, and resource scope with miniOrange before implementation.
PAM helps protect service accounts and other non-human identities by centralizing supported privileged credentials, controlling access to critical resources, and maintaining audit records. miniOrange PAM supports privileged access controls for service accounts, applications, scripts, and APIs, helping security teams reduce reliance on unmanaged credentials and persistent privileges.
Yes. miniOrange PAM supports privileged access management across cloud, on-premises, and hybrid environments, including supported AWS, Microsoft Azure, and Google Cloud resources. Its agentless access model also helps reduce the need to deploy software on every target system. Specific resource, protocol, and integration requirements should be validated for your environment.