Step 1: Set Up ADFS as OAuth Provider
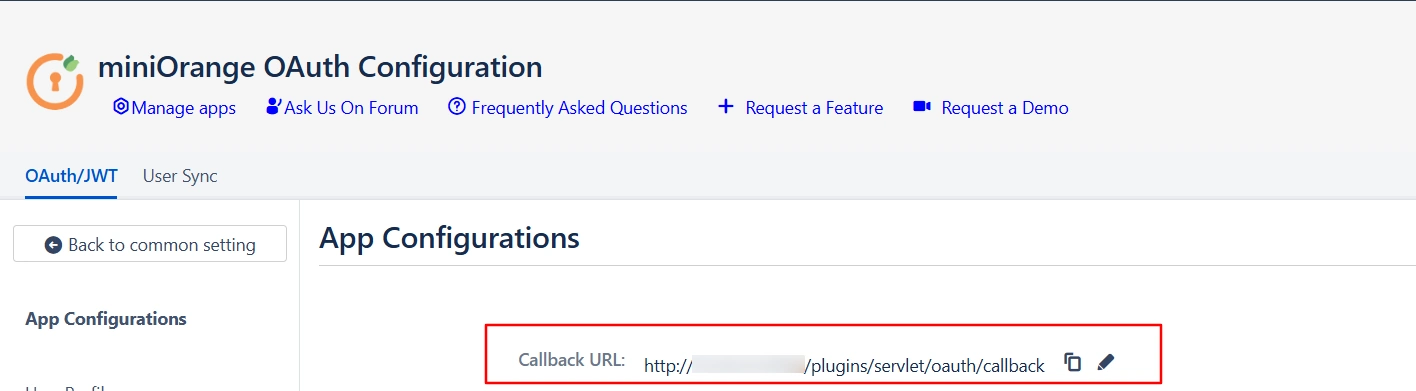
- Navigate to the plugin configuration page, click the "Add New Provider" button (located either in the middle or top-right corner), select ADFS as the application, and copy the callback URL from the plugin and keep it handy, as you'll need it to configure ADFS as the OAuth provider.
- To perform SSO with ADFS as Provider, your application must be https enabled.
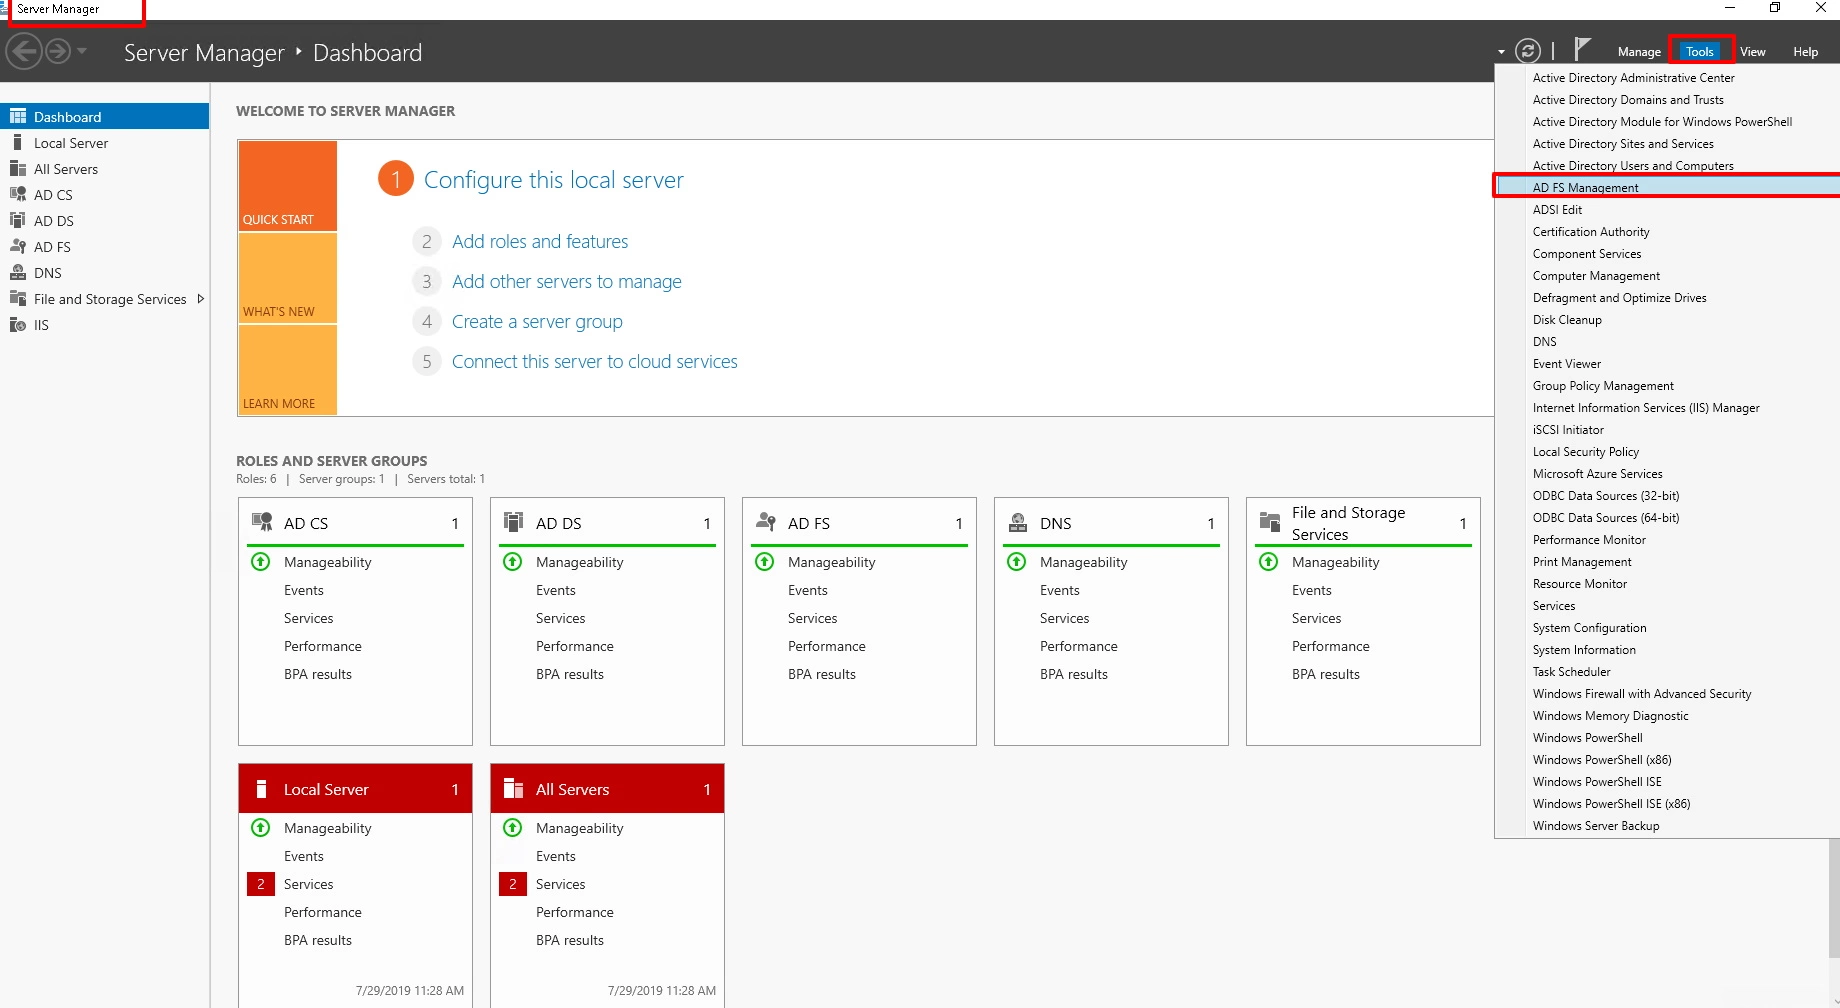
- Navigate to Server Manager Dashboard->Tools->ADFS Management.
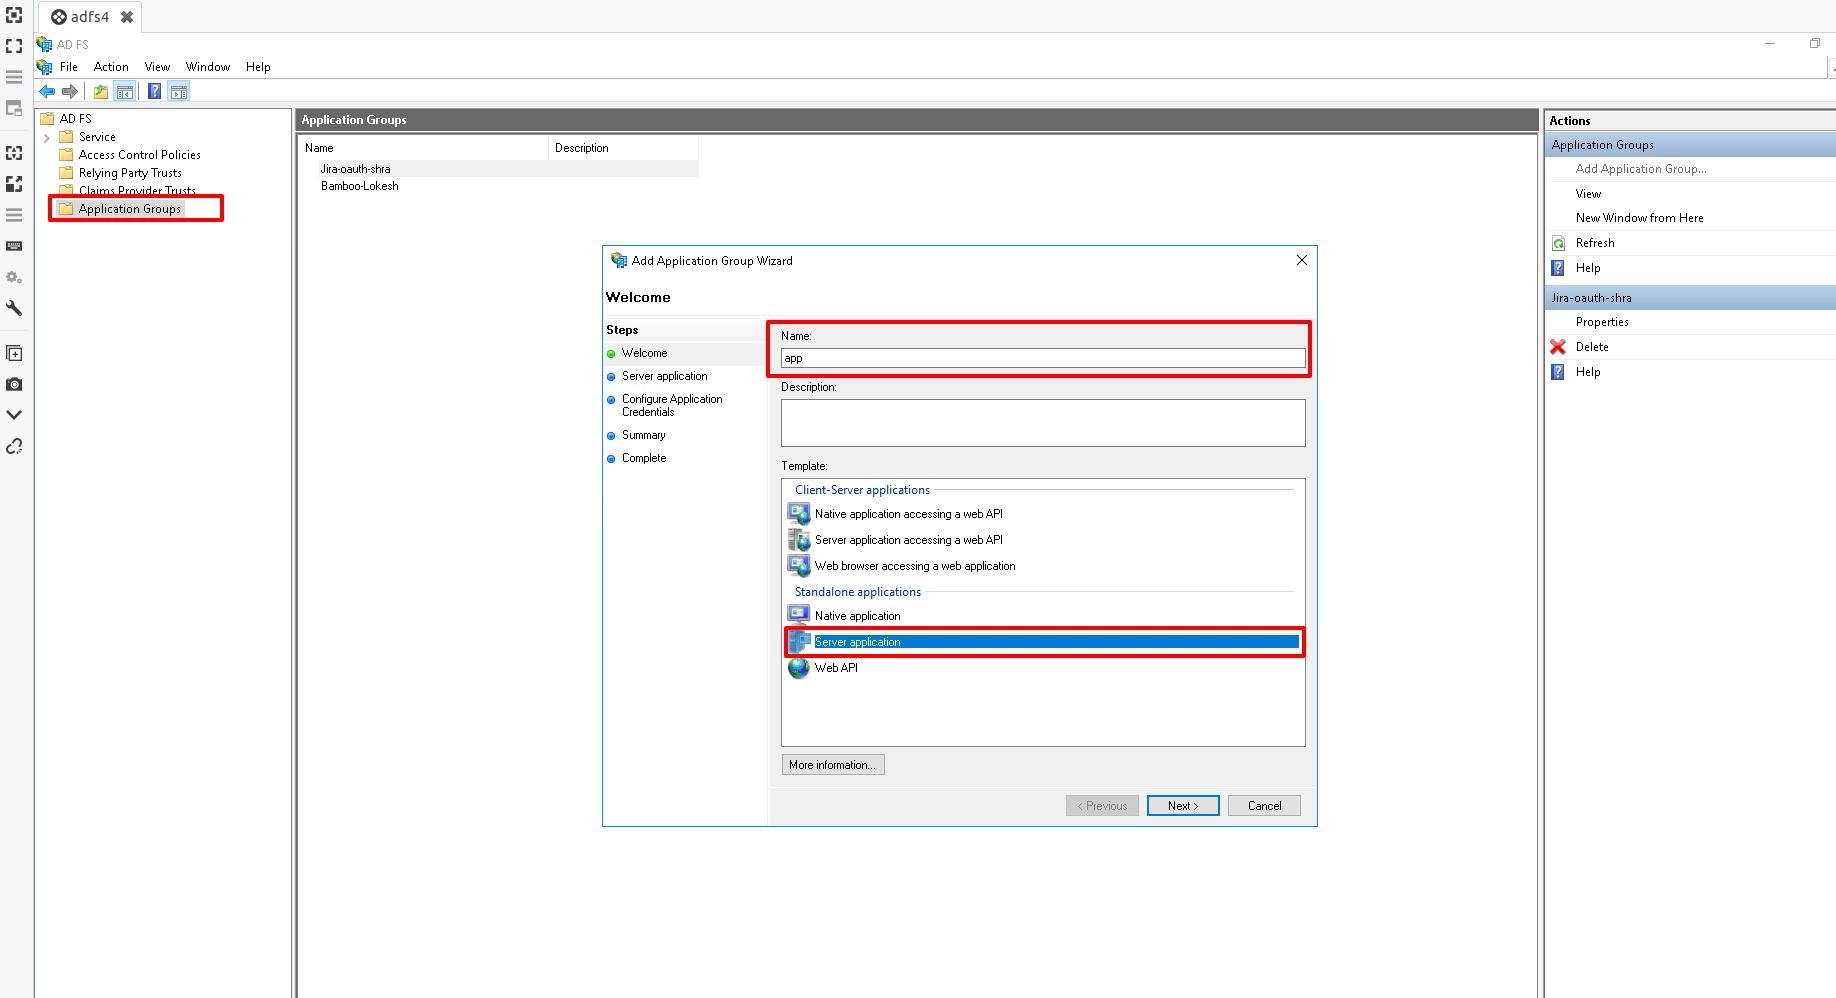
- Navigate to ADFS->Application Groups. Right click on Application Groups & click on Add Application group then enter Application Name. Select Server Application & click on next.
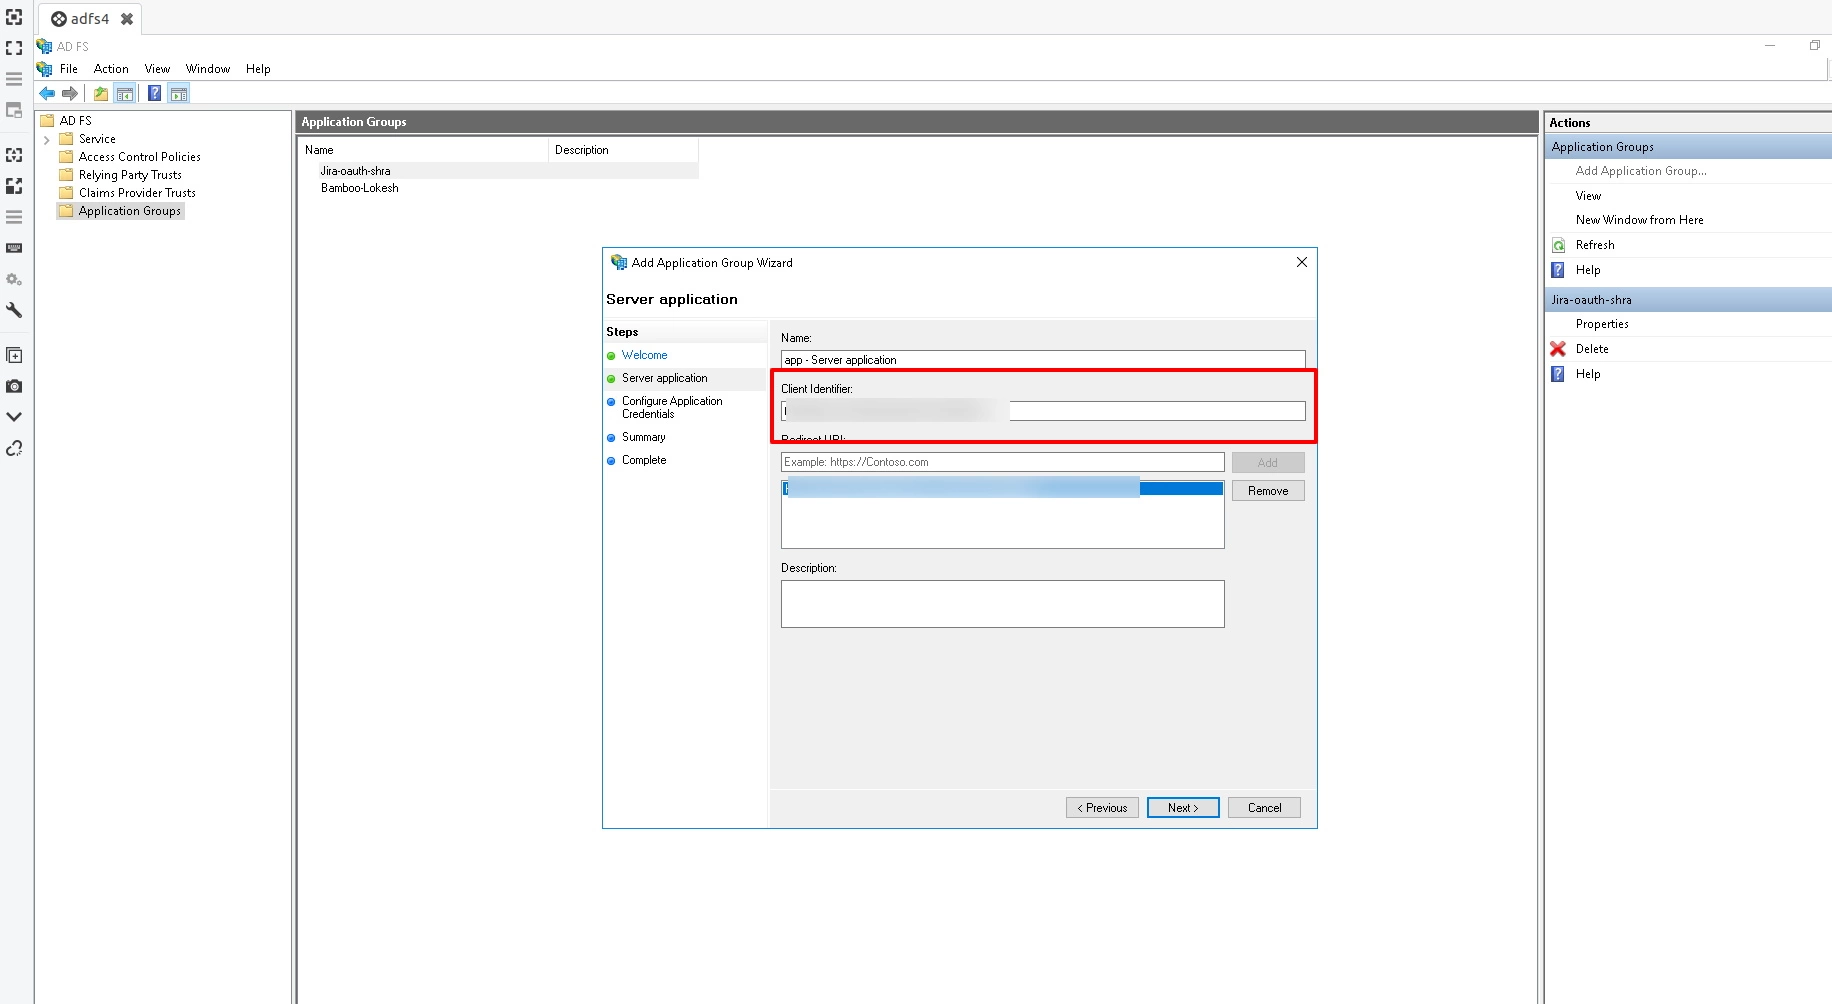
- Copy Client Identifier. This is your Client ID. Add Callback URL in Redirect URL. You can get this callback URL from plugin. Click on next.
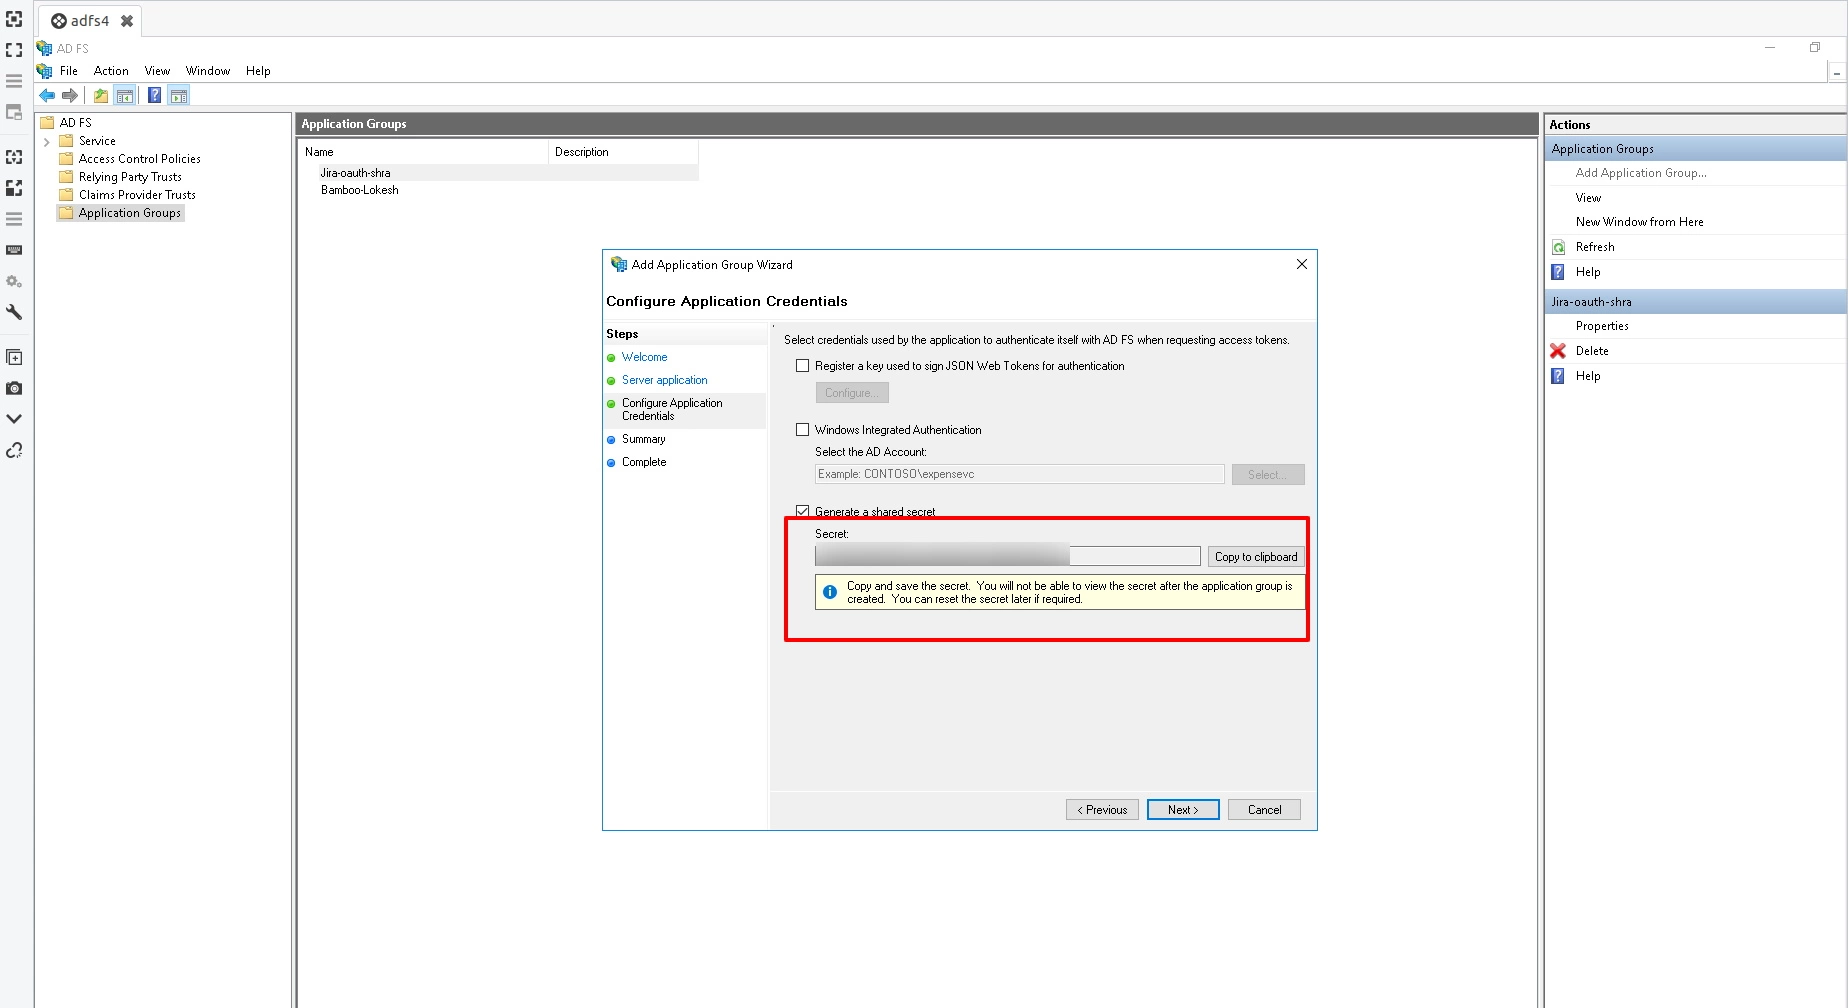
- Click on Generate shared secret. Copy the Secret value. This is your Client Secret. Click on Next.
- On the Summary screen, click Next. On the Complete screen, click Close.
- Now, right-click on the newly added Application Group and select Properties.
- Click on Add application from App Properties.
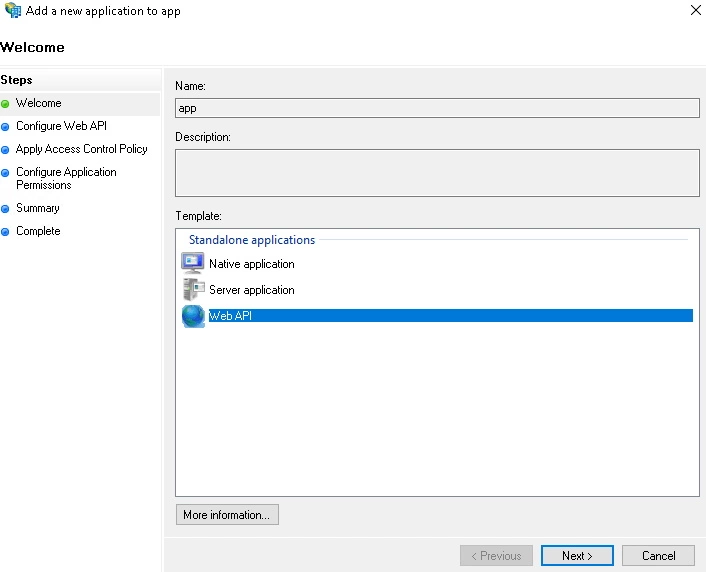
- Click on the Add application. Then select Web API and click Next.
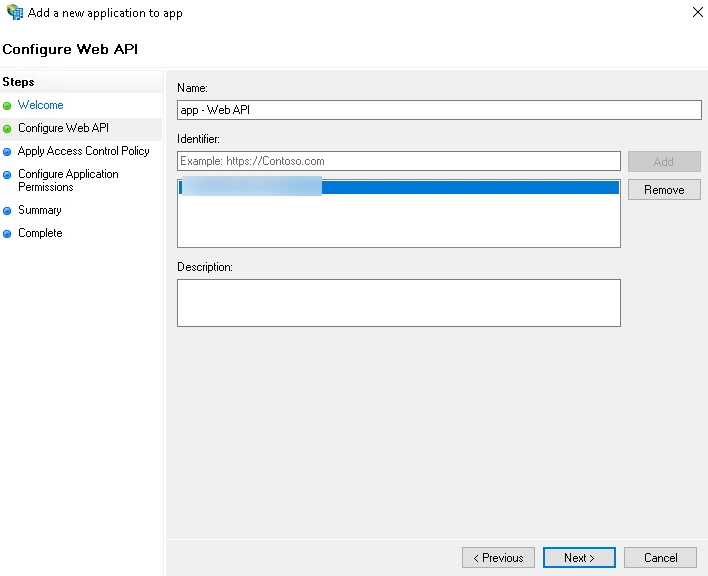
- On the Configure Web API screen, enter the domain name address into the Identifier section. Click Add. Click Next.
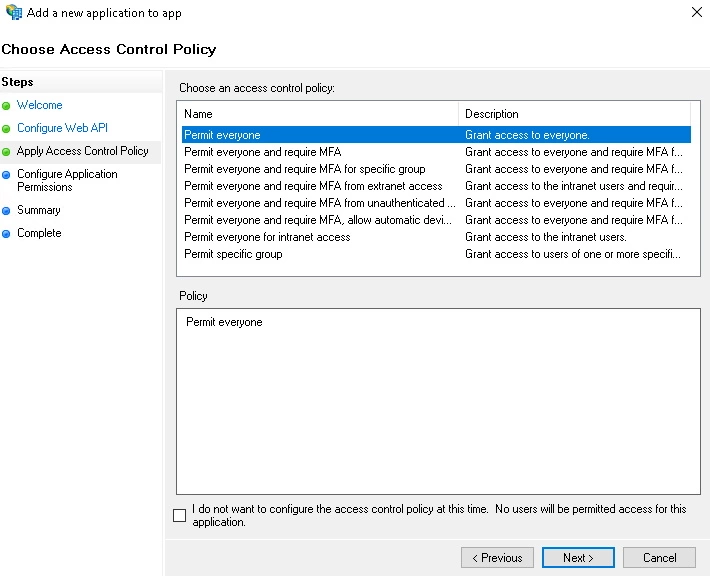
- On the Choose Access Control Policy screen, select Permit everyone and click Next.
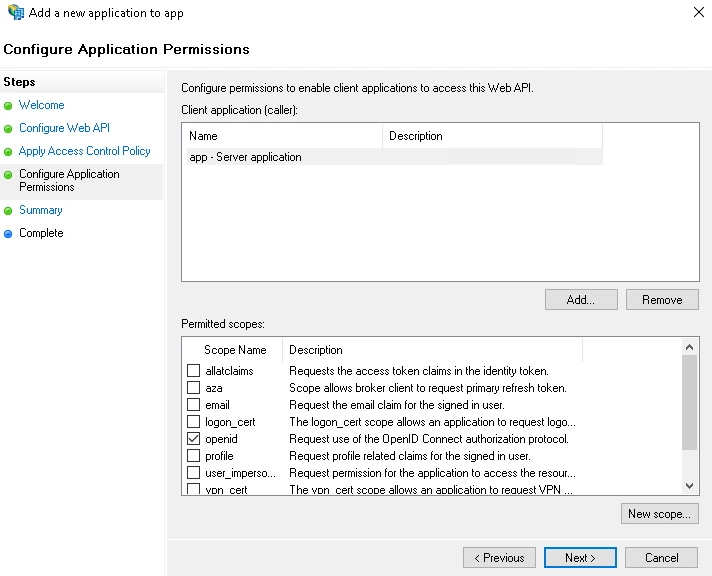
- On the Configure Application Permission, by default openid is selected as a scope & click on next.
- On the Summary screen, click Next. On the Complete screen, click Close.
- On the Sample Application Properties click OK.