Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×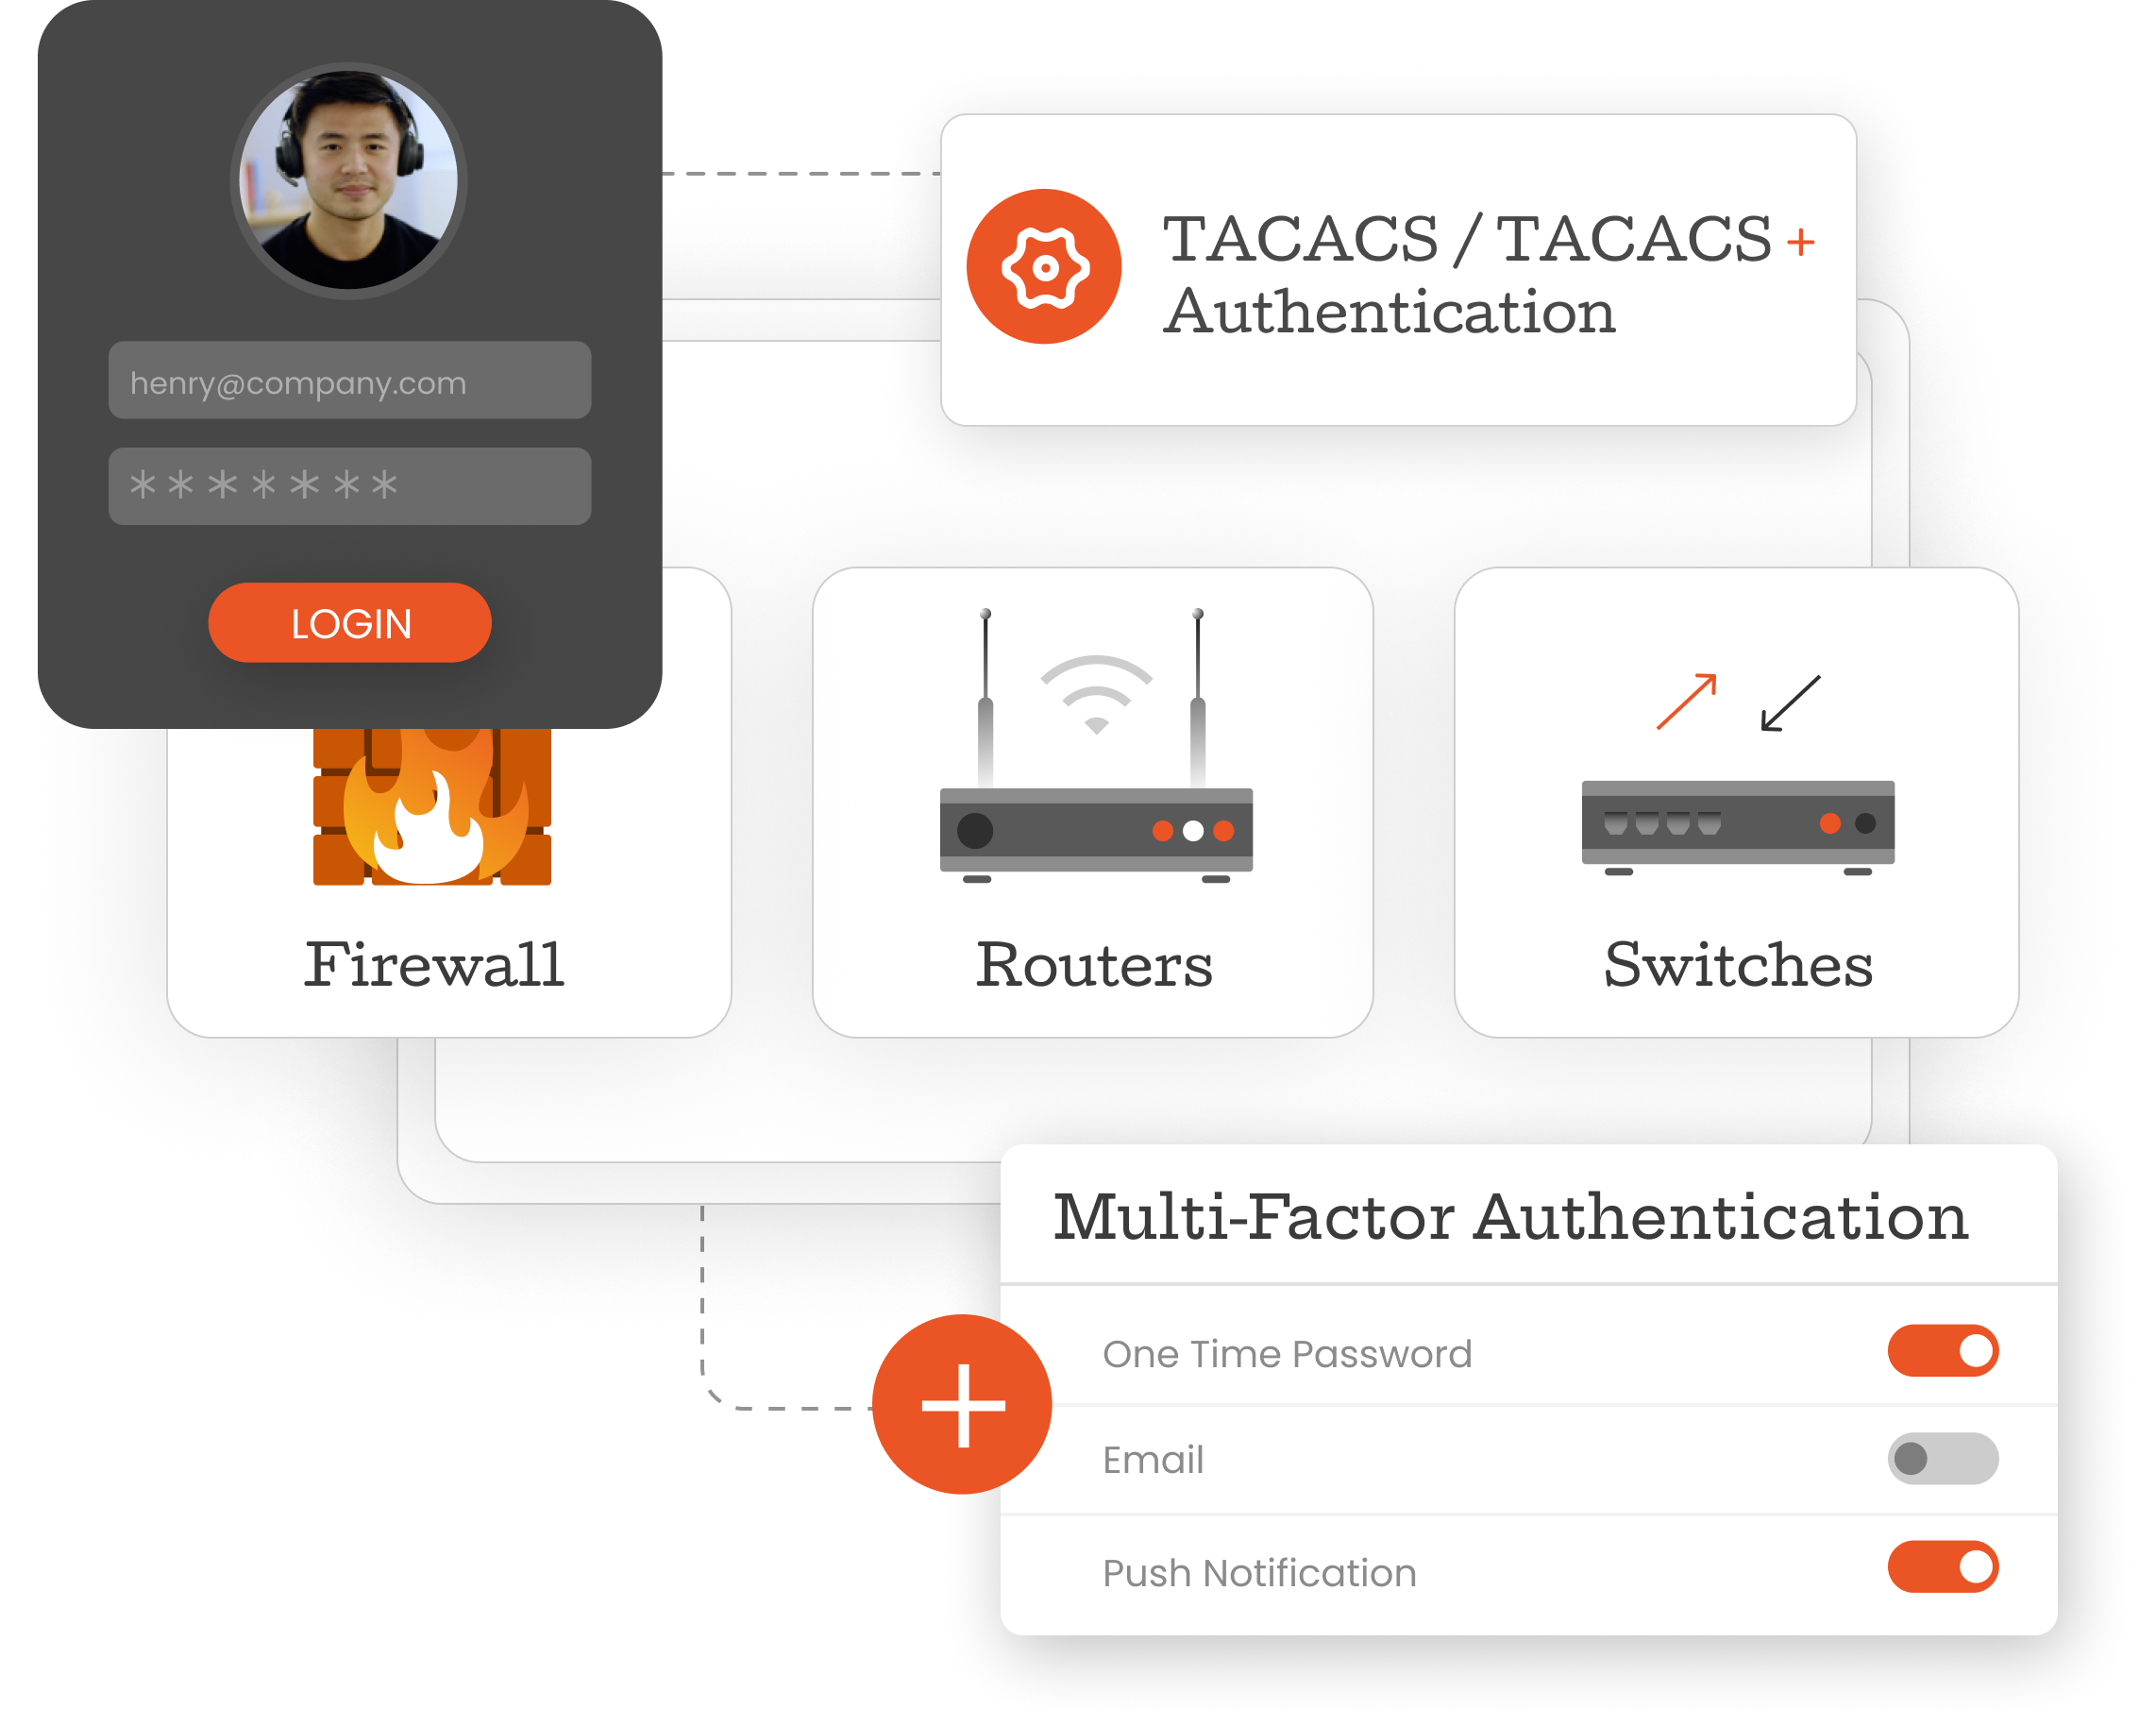
TACACS, which stands for Terminal Access Controller Access-Control System, is a network protocol that was developed by Cisco. TACACS+ is an improved version of the original TACACS protocol, which is now popularly used in the industry for Authentication, Authorization, and Accounting (AAA) in network security.
TACACS/TACACS+ Authentication controls user access to devices like routers, NAS, and switches, separating authentication and allowing fine-grained access control. With encryption and support for command authorization, it significantly improves the security of enterprise networks.
TACACS+ AAA separates authentication, authorization, and accounting, giving you centralized control over network administrator access and activity.
Verify administrator identities before granting access to routers, switches, and other network devices through supported TACACS+ authentication methods.
Control what authenticated administrators can access and execute using privilege levels, AV pairs, and granular command-level authorization policies.
Record administrator sessions and commands with detailed TACACS+ accounting data for auditing, monitoring, investigation, and security operations.
Bring administrator authentication, access policies, MFA, and network activity controls together across your infrastructure.
Authenticate administrators consistently across routers, switches, firewalls, and other network devices through a dedicated TACACS+ server.
Define privilege levels, AV pairs, and command permissions to determine exactly what each administrator can view or execute.
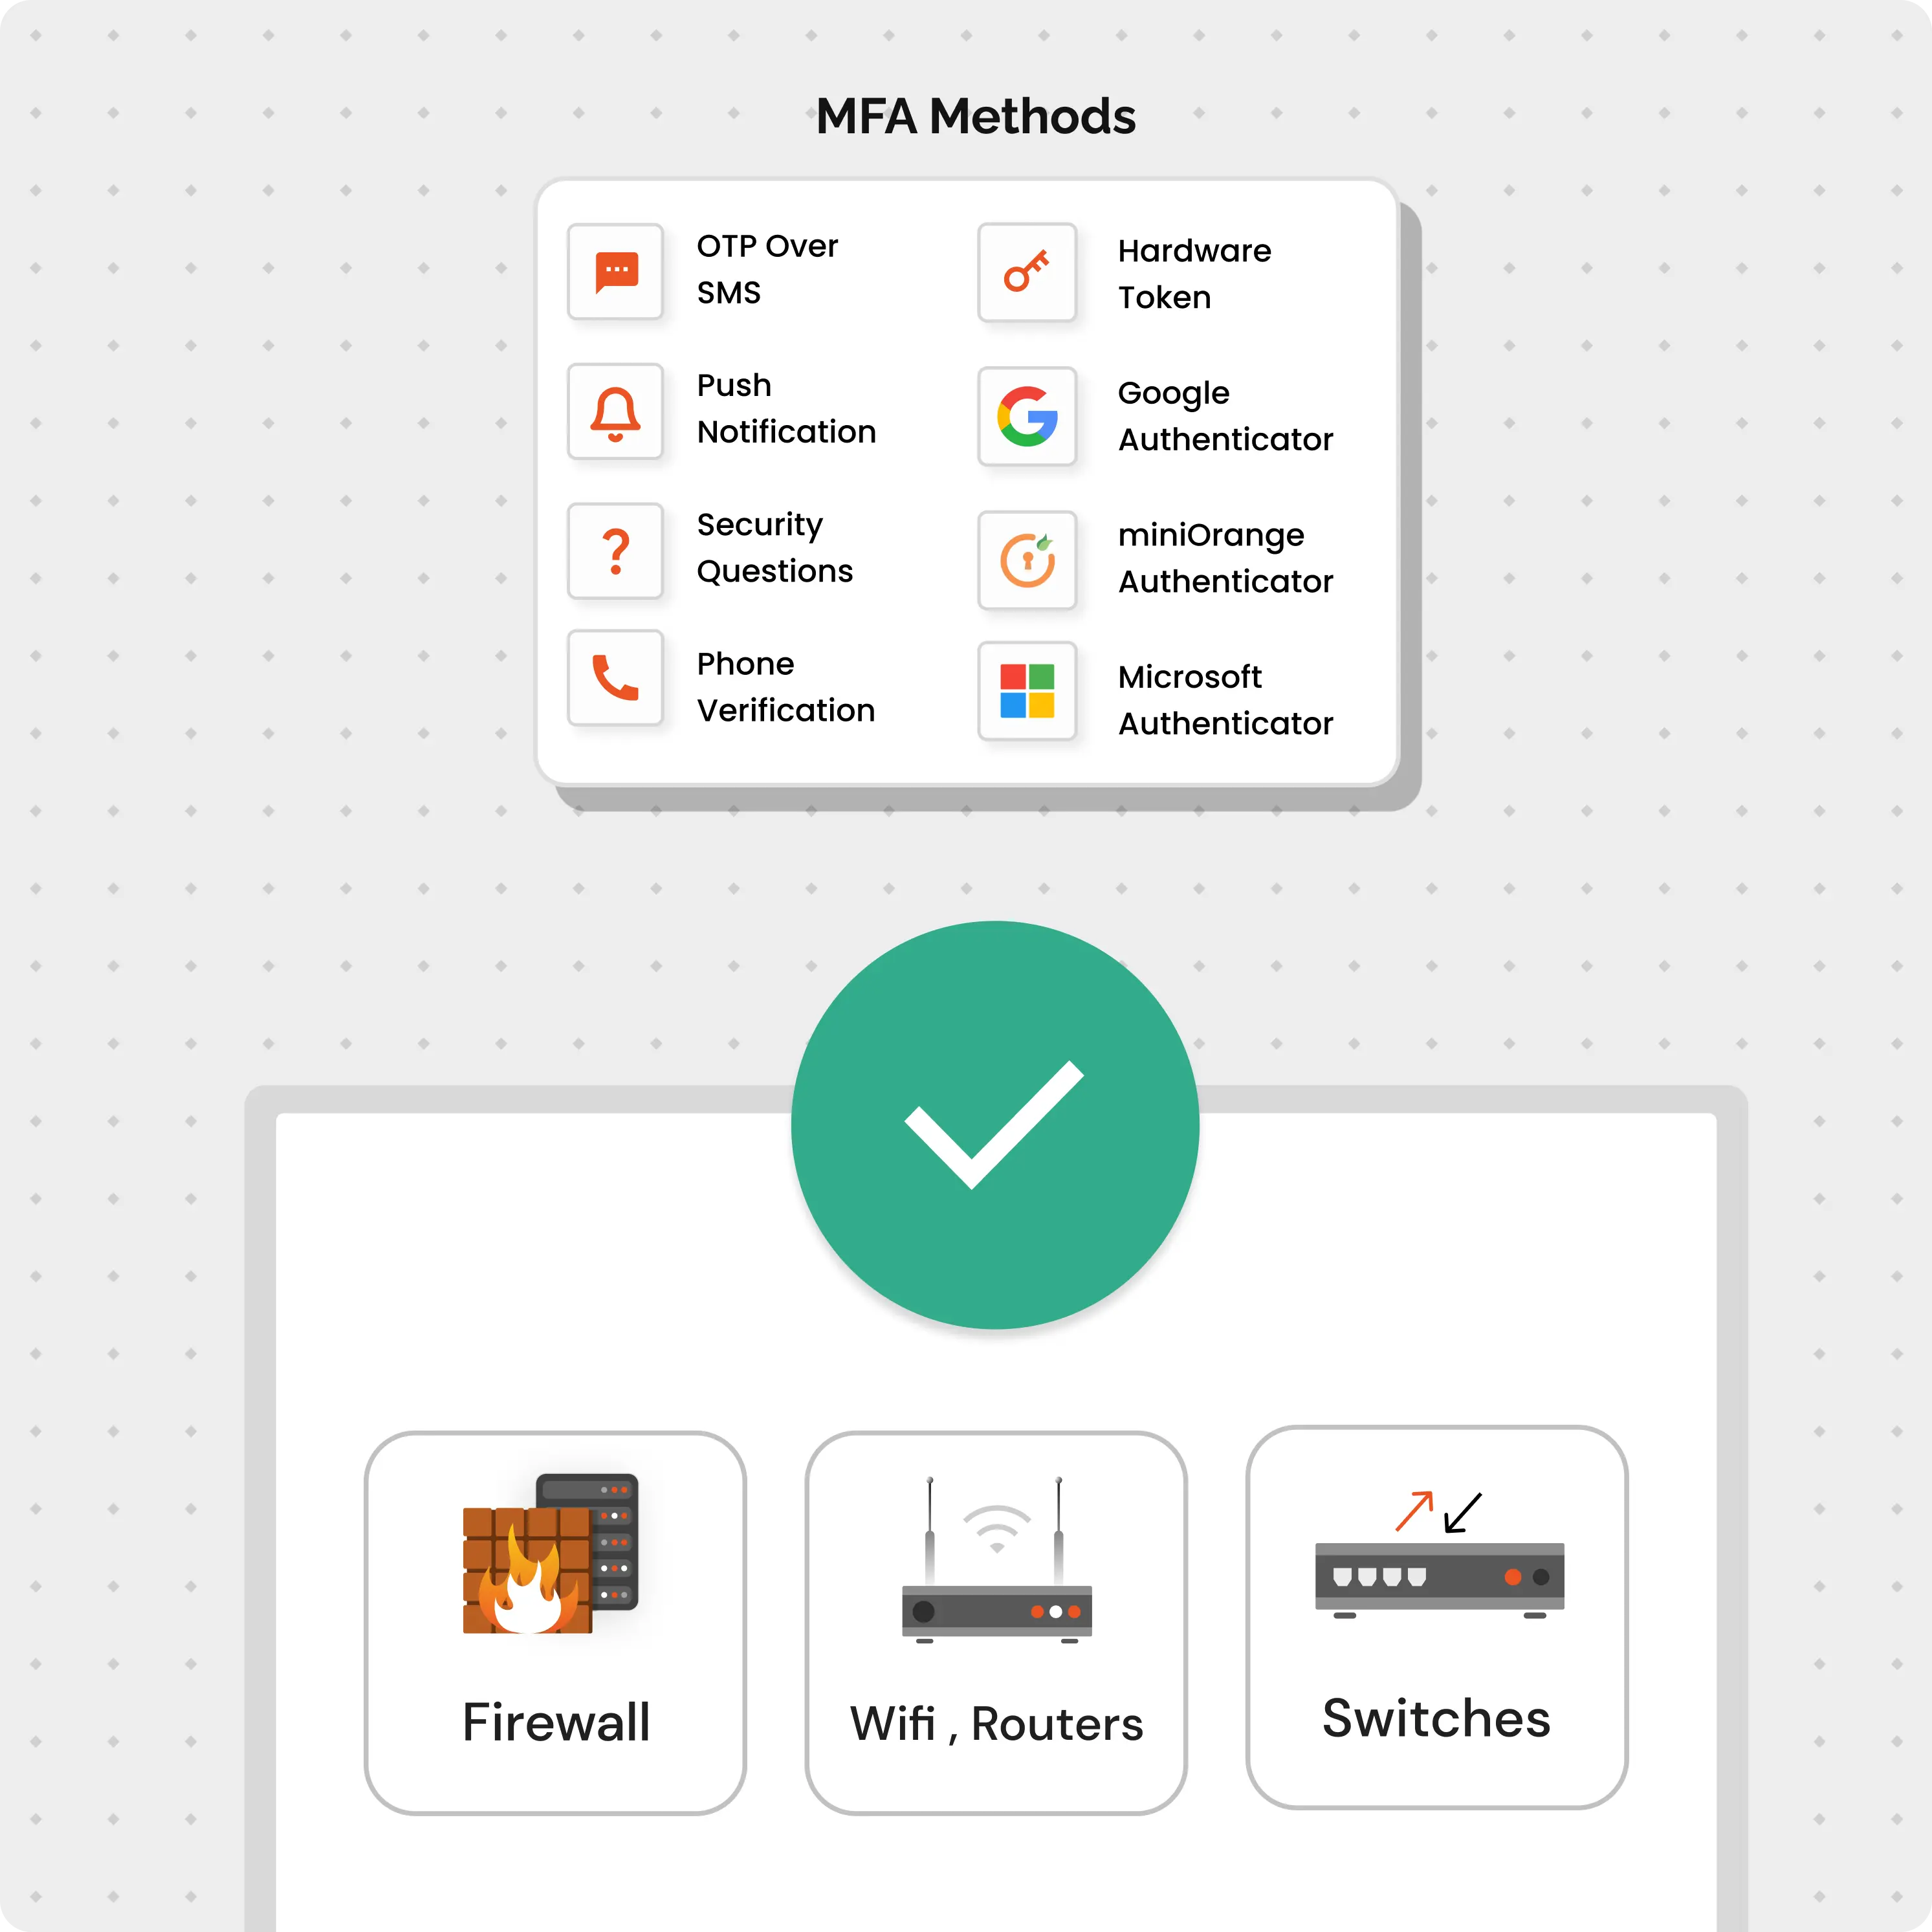
Strengthen TACACS+ authentication with an additional verification step using TOTP, push, or out-of-band authentication methods.
Use Active Directory and LDAP identities and groups to authenticate administrators without creating a separate identity store.
Apply TACACS+ authentication across Cisco, Juniper, Huawei, Nokia, Fortinet, and other supported network devices.
Expose authorization-related events through supported APIs for monitoring, reporting, security workflows, and integration with external systems.
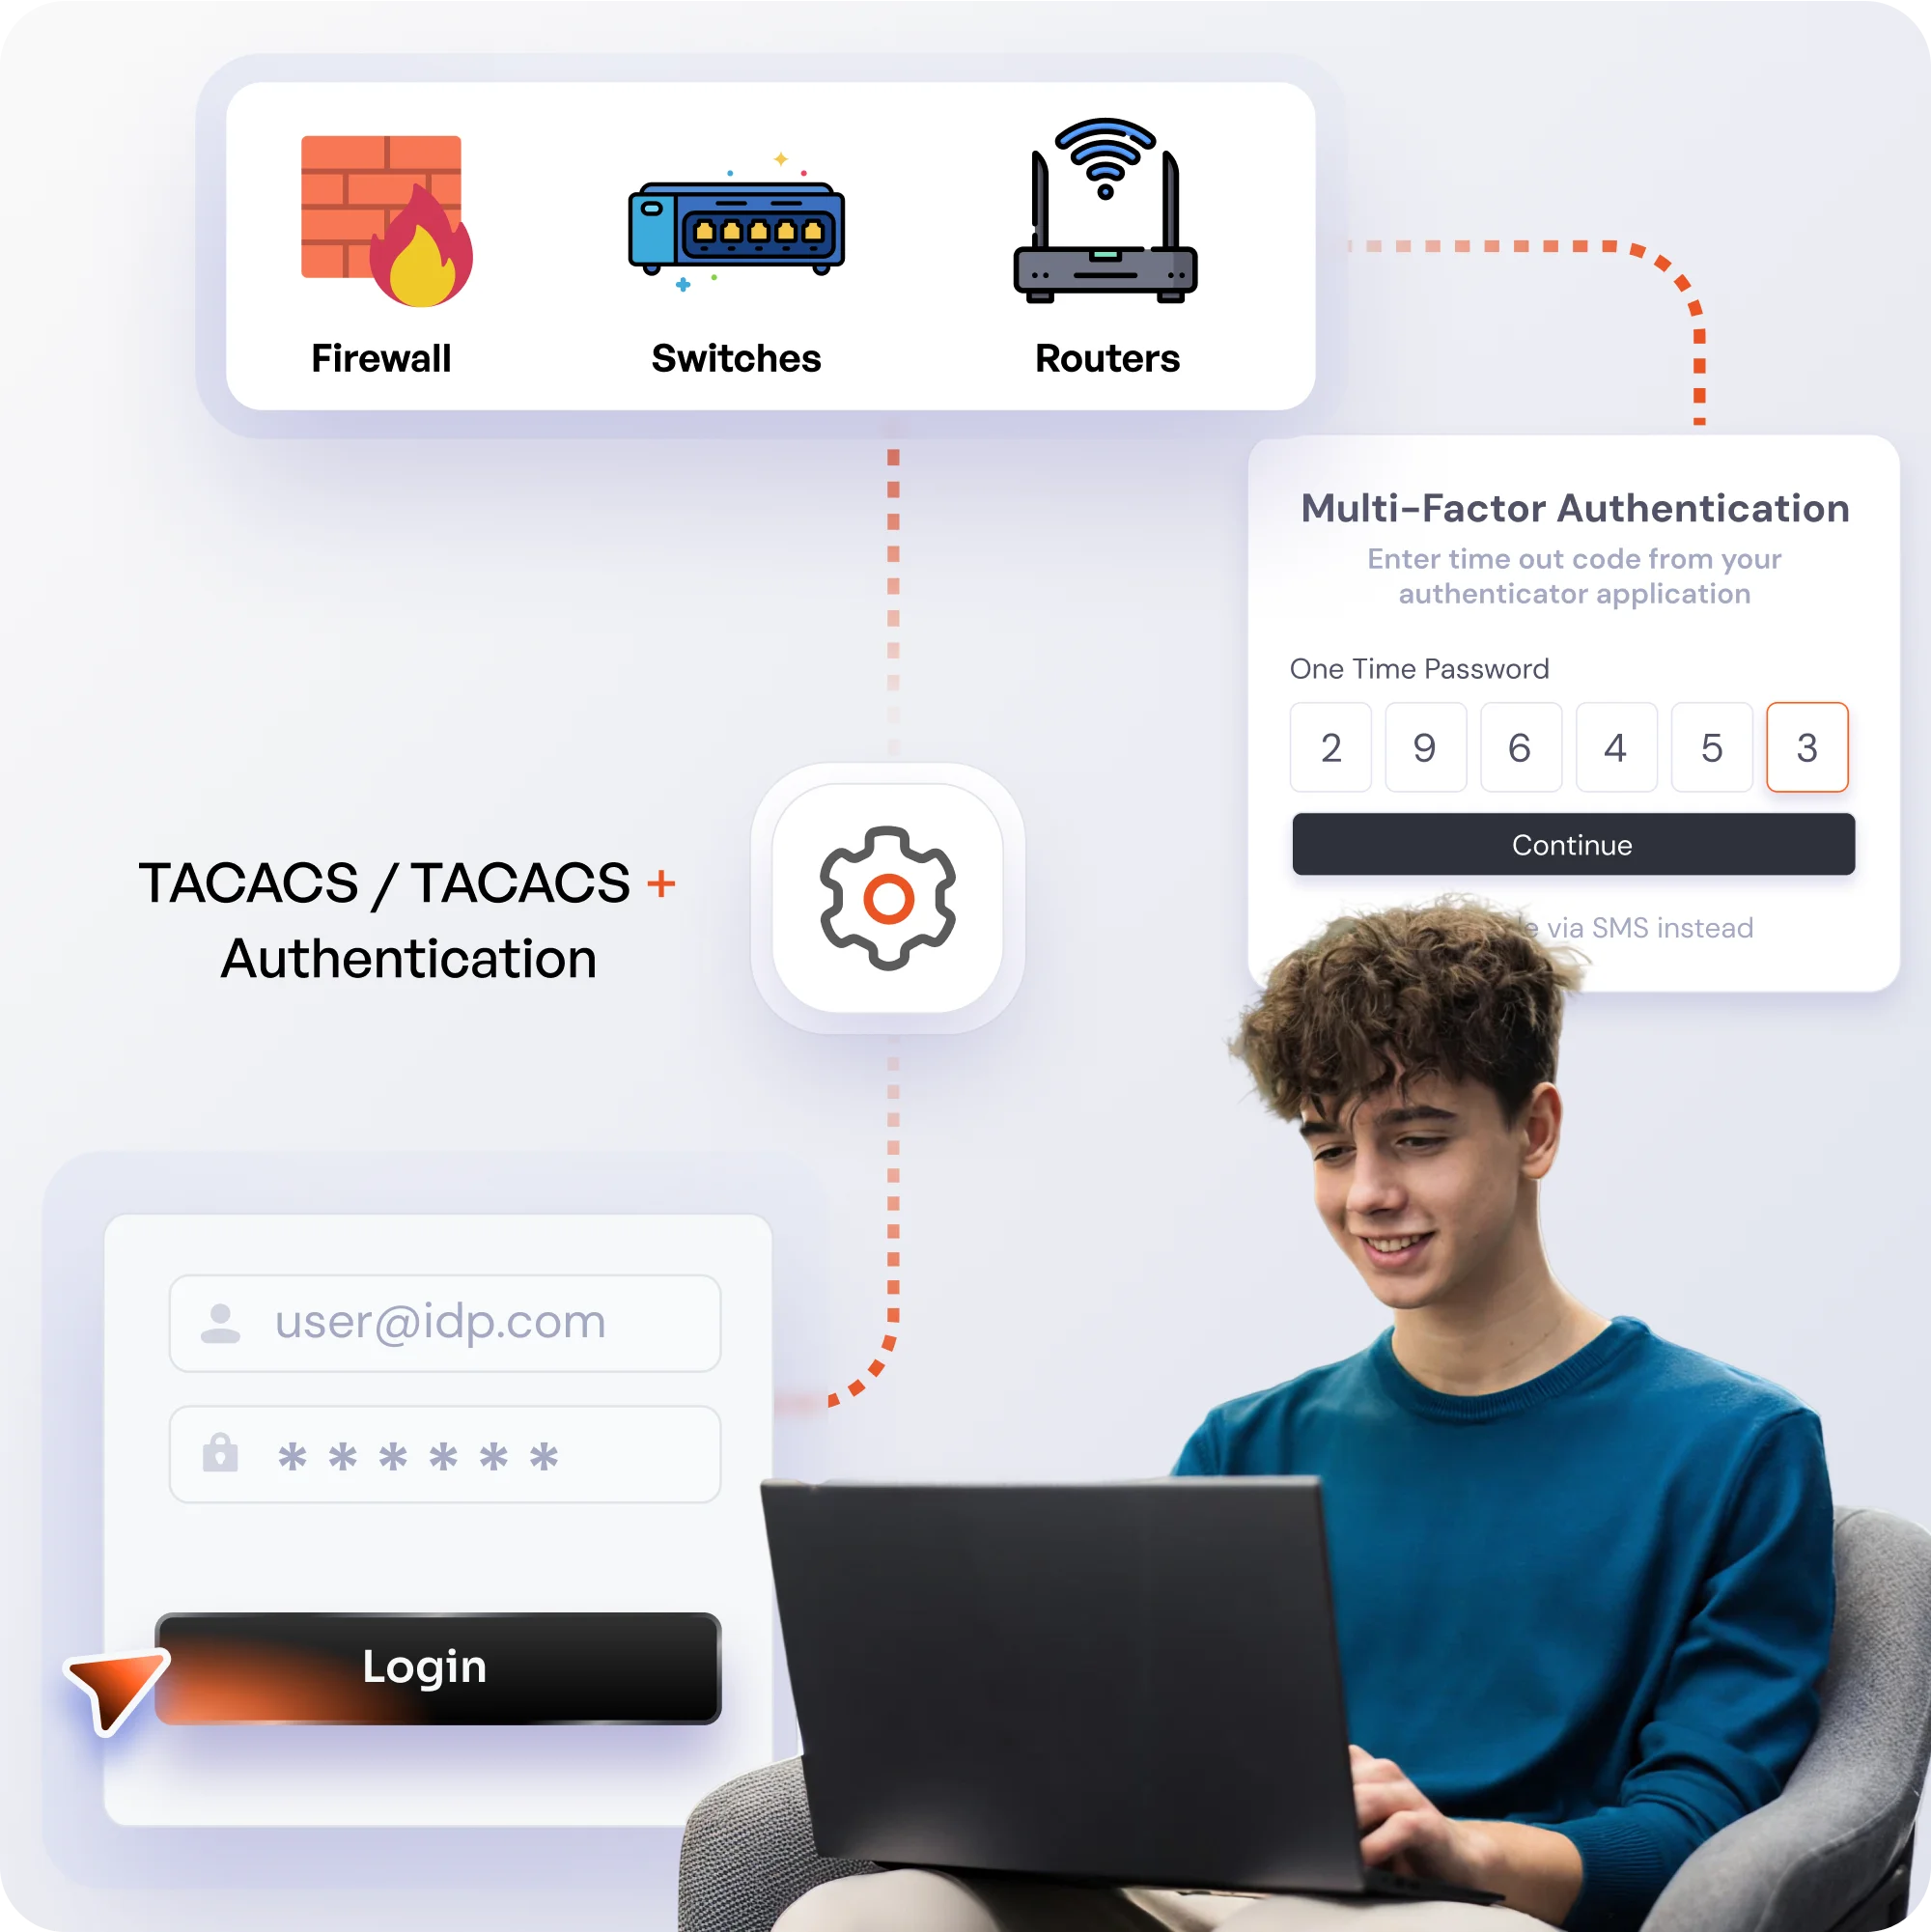
See how identity, privilege, and administrator activity can work together across your network infrastructure.
Add an independent verification layer to TACACS+ authentication for stronger protection of network administrator access.
Set up TACACS+ across your network infrastructure with flexible configuration for different devices, environments, and administrator access requirements.
Our TACACS+ Authentication solution supports Network Devices from Multiple Vendors:






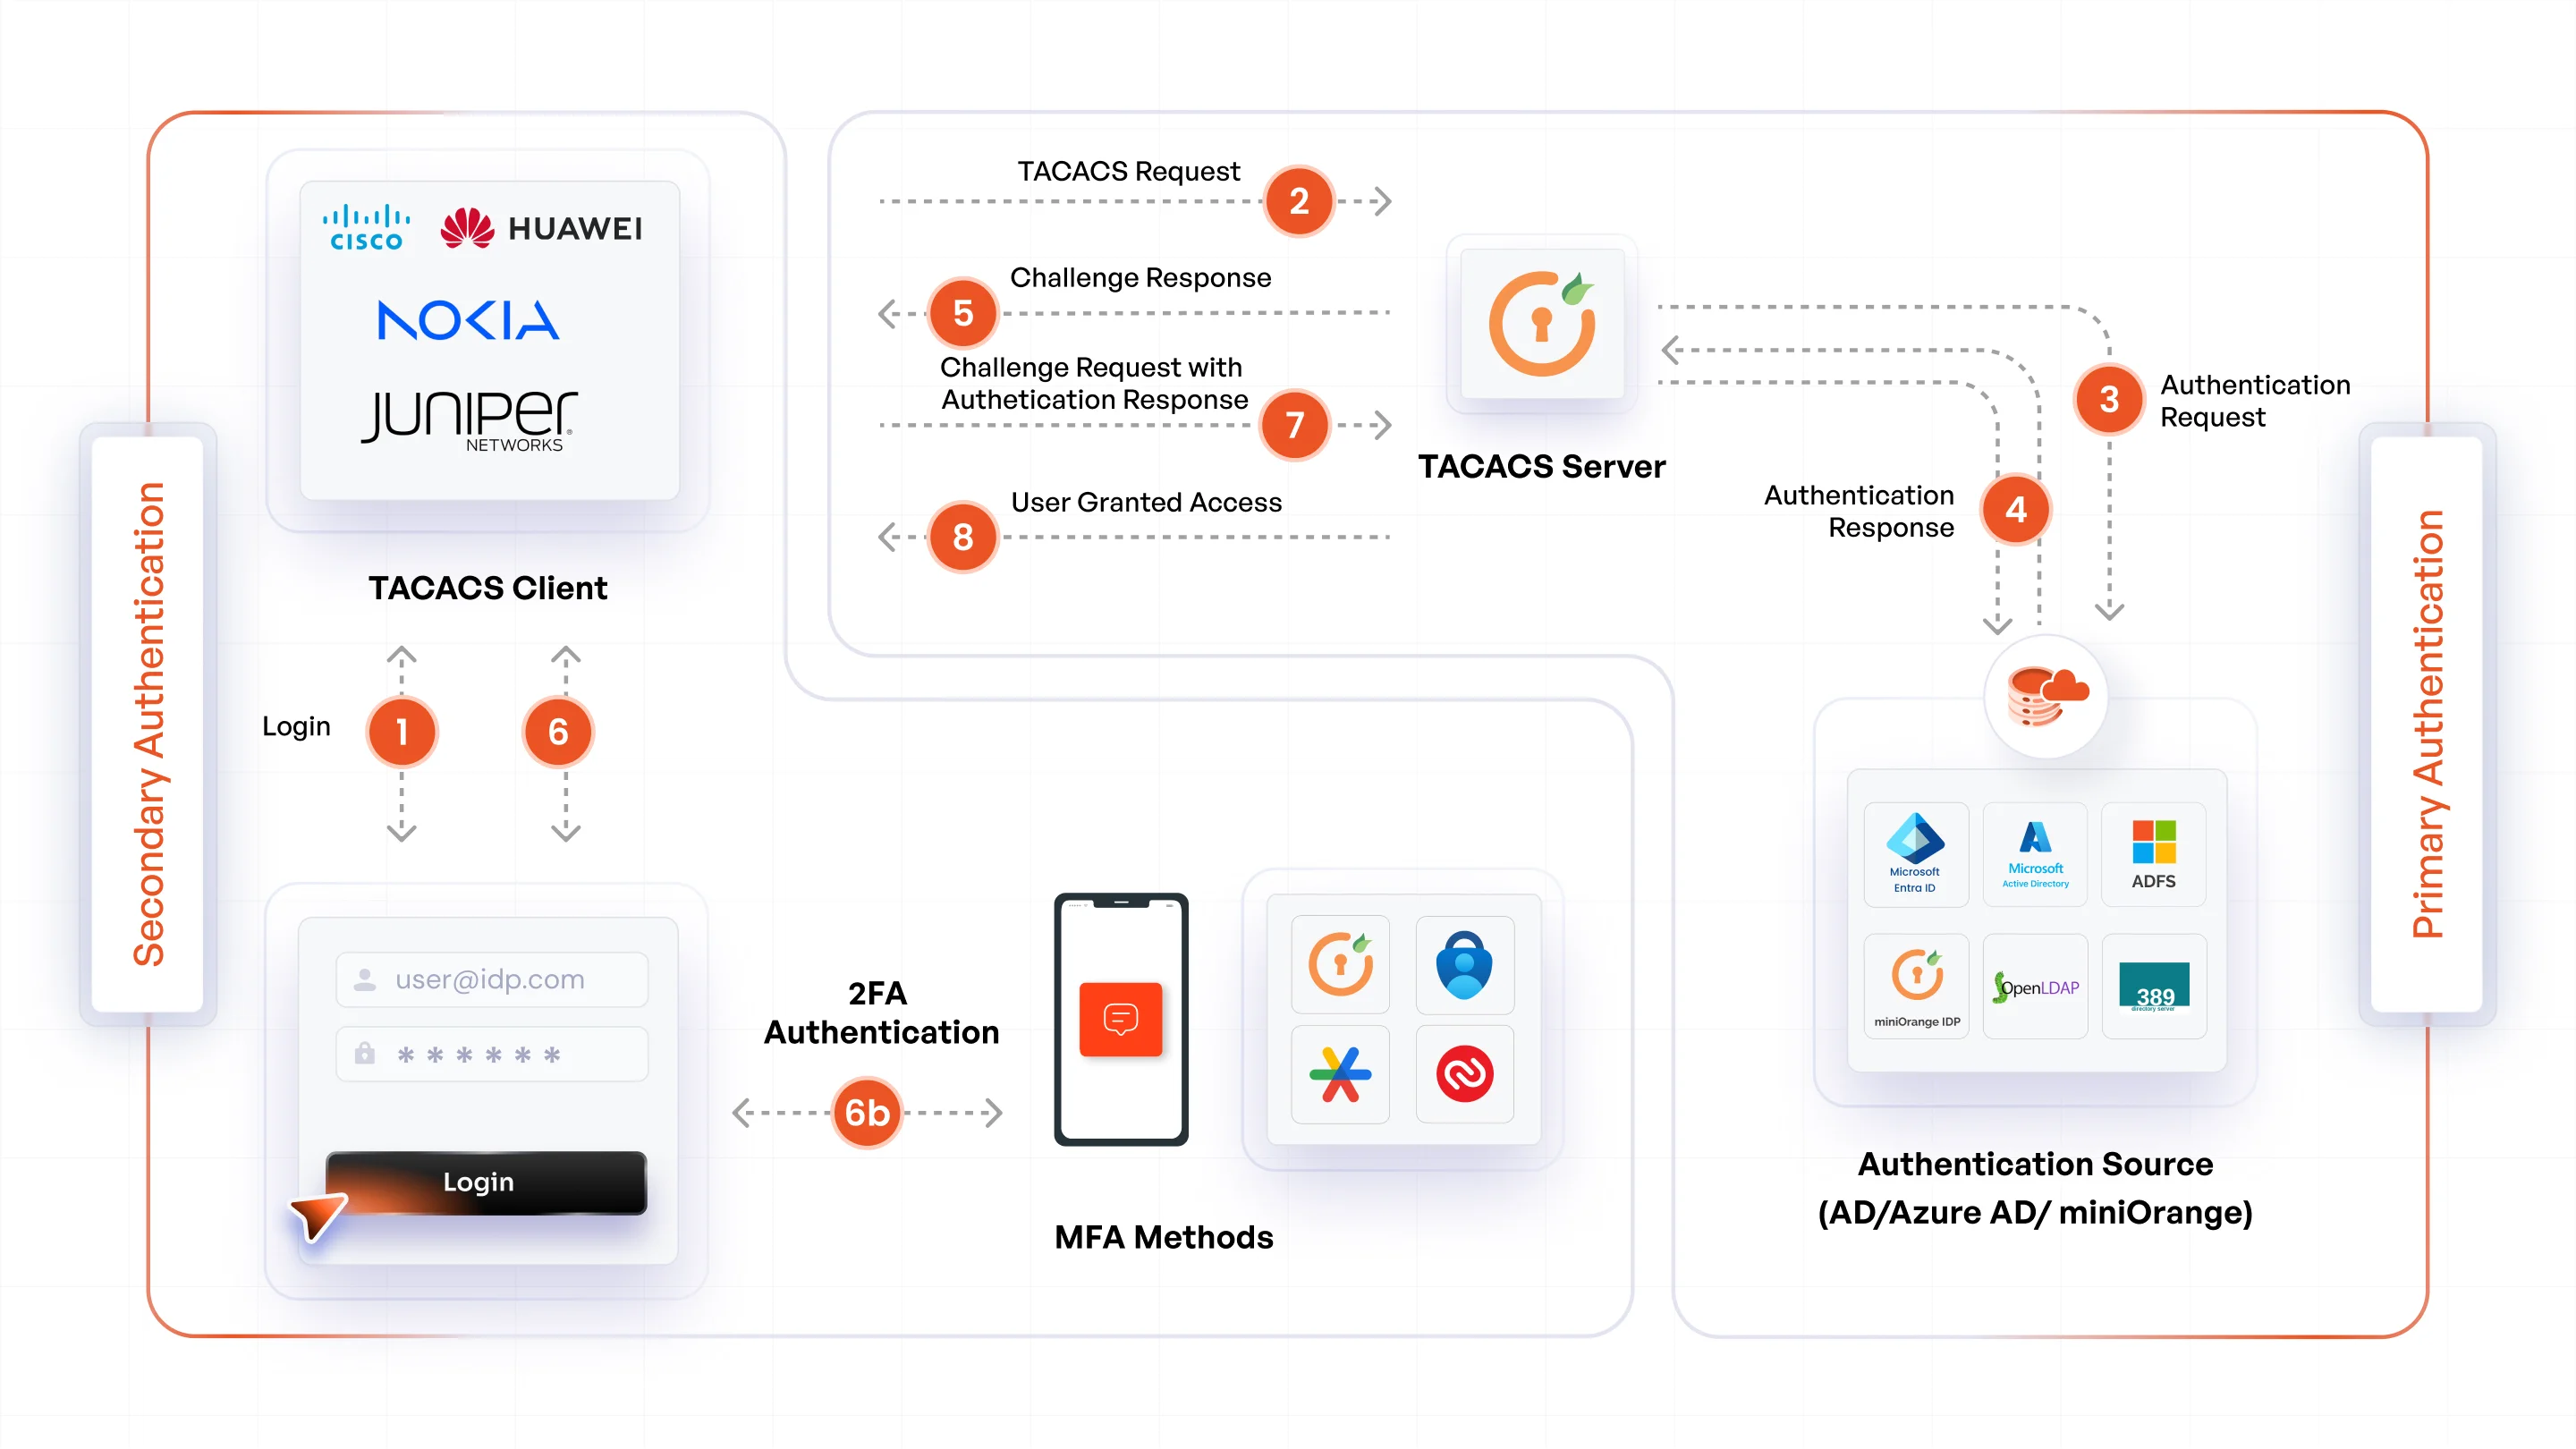
miniOrange connects your network devices, identity sources, MFA, and access policies into one administrator authentication flow.
An administrator enters their credentials on a Cisco, Juniper, Nokia, or other supported network device to start a session.
The network device sends the TACACS+ request to miniOrange, which verifies the administrator against Active Directory, LDAP, or a configured database.
When MFA is enabled, miniOrange triggers an additional verification step using TOTP, push, or out-of-band authentication before access is authorized.
The TACACS+ server determines the administrator's privilege level, AV pairs, and permitted commands based on configured roles and authorization policies.
miniOrange returns the authorization response to the network device, which grants the permitted access, while TACACS+ accounting records sessions and commands.
Get an enterprise-ready TACACS+ solution designed to simplify network access management while fitting the operational realities of modern IT environments.
Manage TACACS+ access through a centralized administrative experience instead of maintaining authentication configurations across individual network devices.
Move away from outdated TACACS+ infrastructure while retaining the network devices and identity environment your teams already depend on.
Extend TACACS+ access data into broader security operations to support monitoring, investigation, and response workflows.
Update access policies as teams, responsibilities, devices, and network environments change without rebuilding the underlying authentication architecture.
Replace fragmented administrator access with a deliberate approach to authentication, privilege, and accountability.
TACACS+ separates Authentication, Authorization, and Accounting into three distinct operations and encrypts the full packet. RADIUS only encrypts the password and bundles all three operations together. TACACS+ also uses TCP for reliable connections; RADIUS uses UDP. If you need command-level control over network devices, TACACS+ is the right choice.
miniOrange TACACS+ is available as Cloud (IDaaS), On-Premise (including air-gapped environments), and Hybrid. You choose the deployment that fits your infrastructure — no forced cloud migration.
TACACS+ records what each user does, including all commands they run. This detailed logging helps with investigations, audit trails, and meeting compliance rules.
Yes. miniOrange streams all TACACS+ authentication and authorization events to your SIEM in real time via a unified auditing framework. Supported platforms include Splunk, Microsoft Sentinel, IBM QRadar, and any syslog-compatible SIEM.
Yes. The TACACS+ authorization event API lets you pull privilege grant and deny records into your own dashboards, SOAR tools, or compliance reporting workflows programmatically — no manual log exports needed.
Yes. You can define which commands each user or group is allowed to run on each device. This gives you granular control beyond basic login access — critical for compliance with PCI-DSS and HIPAA network security requirements.