Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×Connected energy environments create more identities and access points to secure, making strong identity controls critical to operational resilience.
Experienced ransomware attacks
Face higher OT vulnerability
OT security is weaker than IT
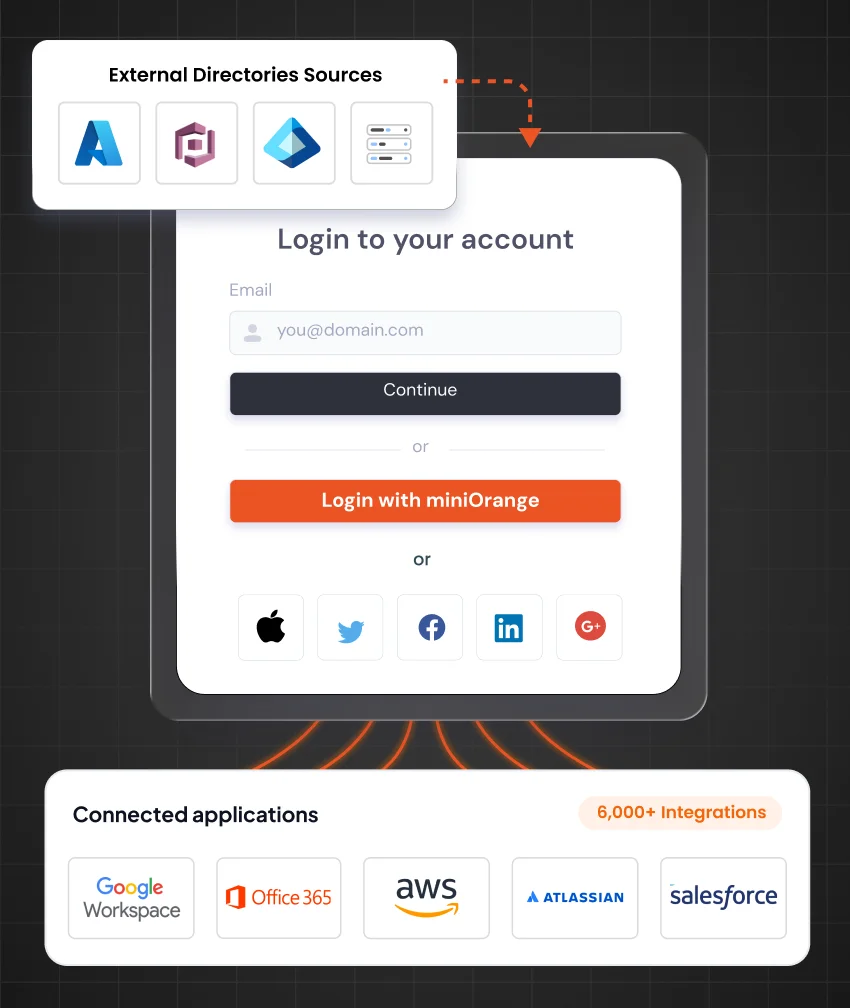
Give operators, engineers, and corporate teams one secure login across plant applications, utility portals, cloud services, and legacy systems, reducing credential sprawl.
Know More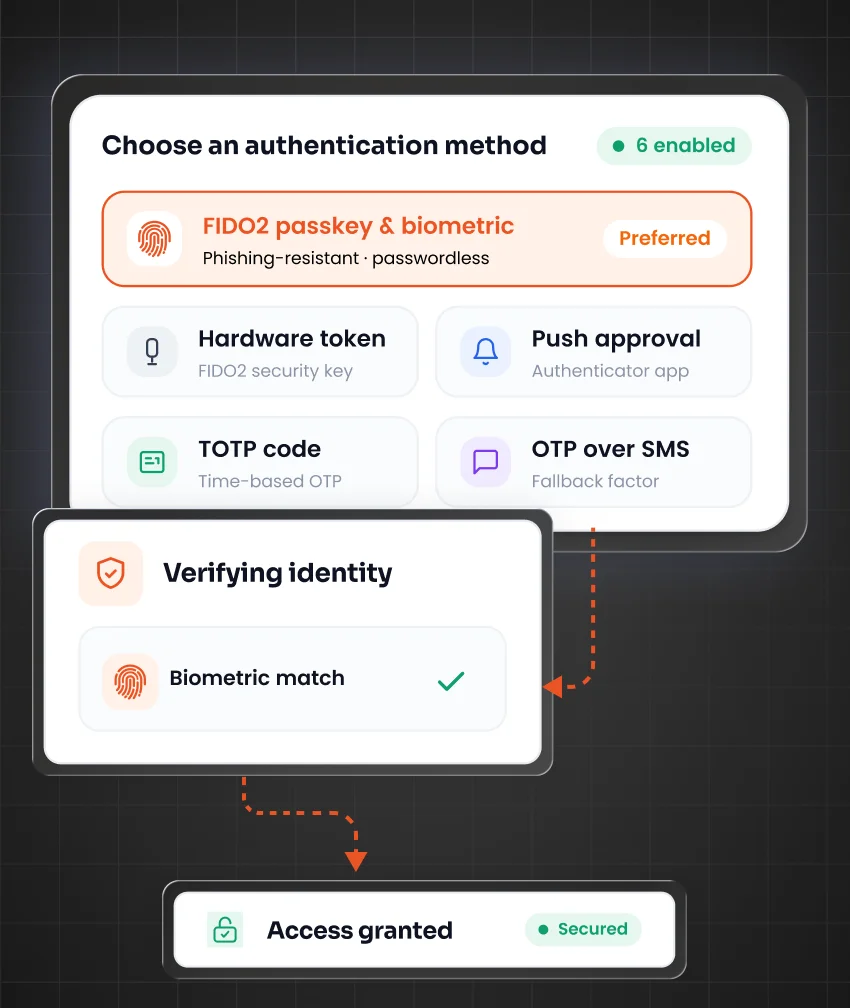
Strengthen authentication for VPNs, remote access, and sensitive applications used by personnel working across plants, substations, field locations, and corporate environments.
Know More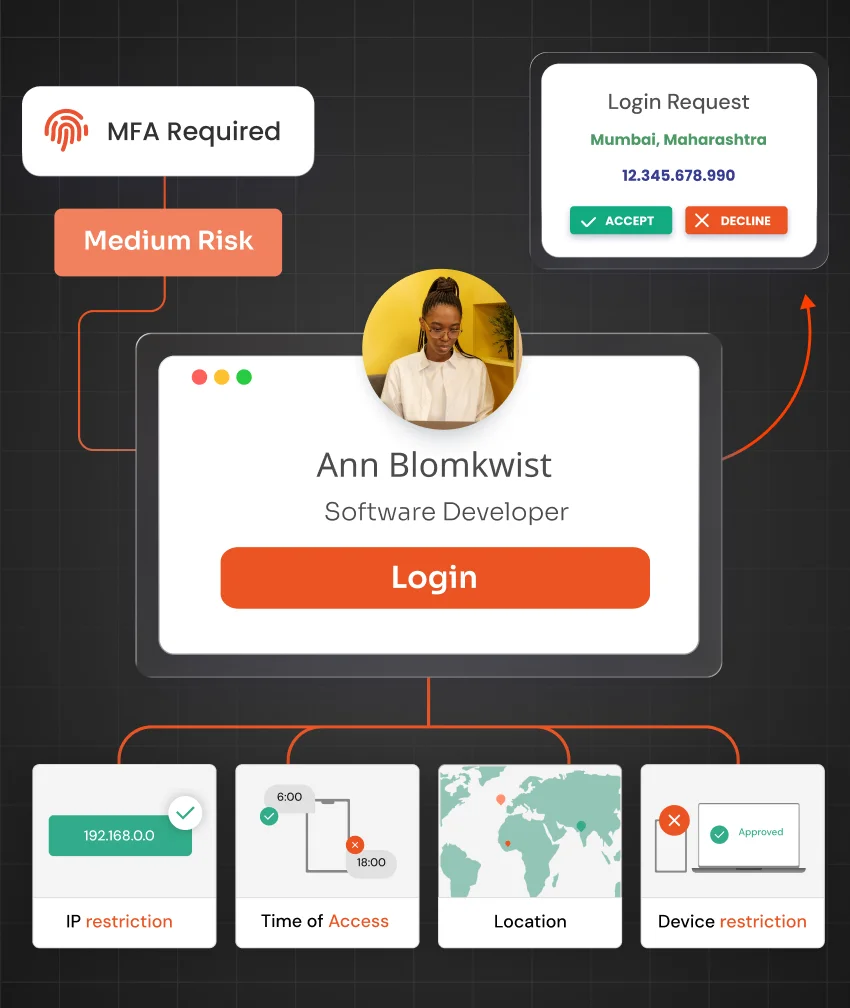
Apply access decisions based on user, device, location, network, and risk context before granting access to sensitive applications and operational resources.
Know More
Automate access changes as employees, technicians, contractors, and vendors join, change responsibilities, move locations, or leave, helping prevent outdated permissions from persisting.
Know More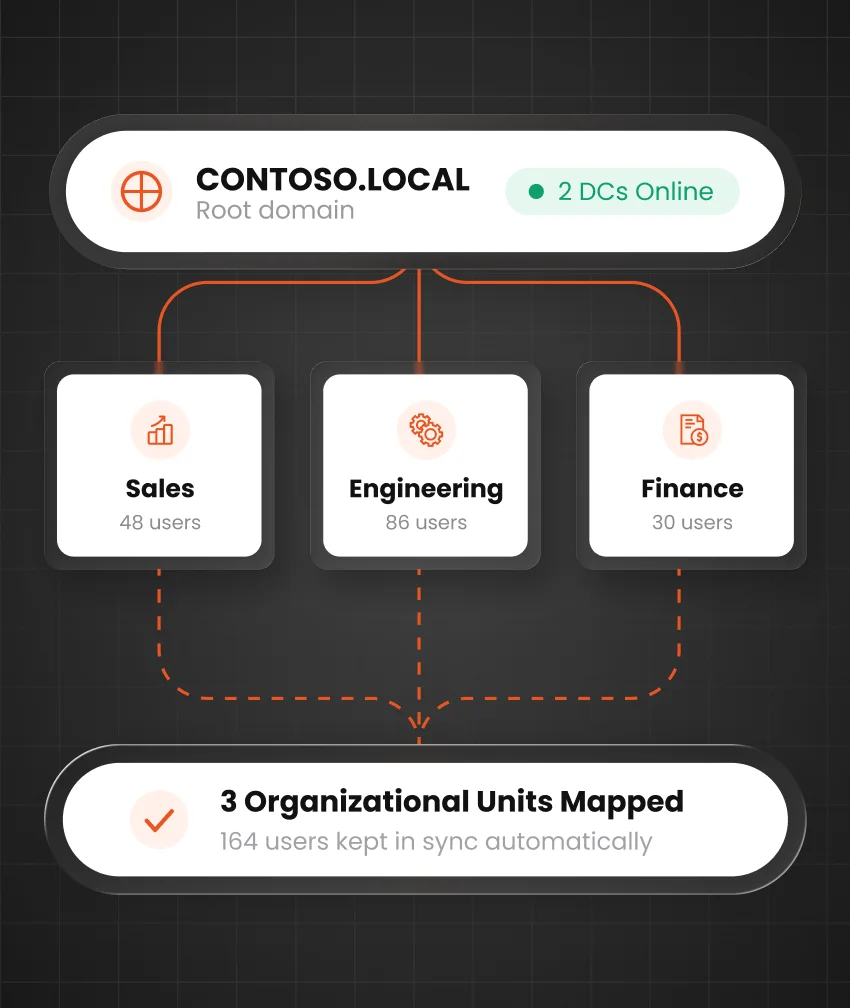
Connect Active Directory, LDAP, Microsoft Entra ID, and other identity sources to reduce fragmented identity records across corporate offices, plants, substations, and field operations.
Know More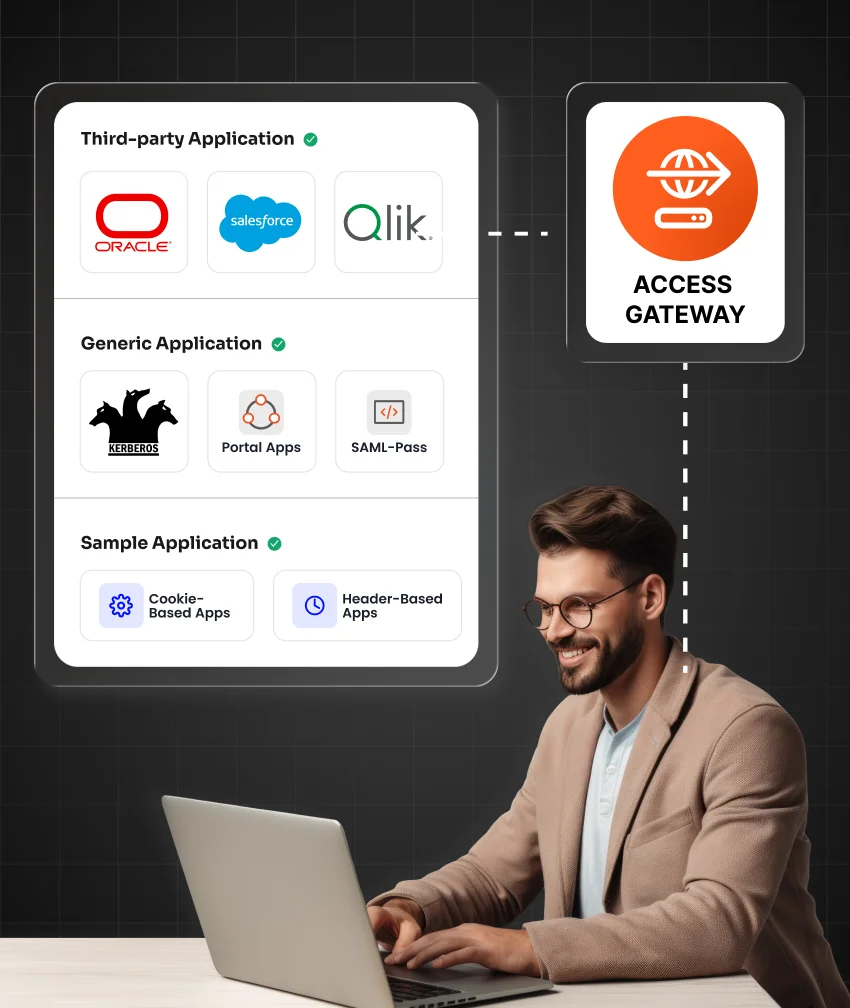
Bring modern authentication to legacy and custom applications, VPNs, and on-premises systems without forcing changes to established applications or operational workflows.
Know MoreSecure workforce identities, control privileged access, and connect modern authentication with the legacy and OT environments your teams already rely on.

“CPCL faced the challenge of securing workforce and privileged identities across servers and databases, addressed through miniOrange’s unified IAM and PAM suite with SSO and MFA.”
“Complex applications like Oracle E-Business Suite and custom .NET integrations made secure access difficult; miniOrange’s IWA and SCIM simplified access and user management.”
Read their story
“Managing identities across seven Entra ID tenants created access complexity for Petredec’s Singapore workforce; miniOrange unified SSO across applications and HRMS.”
“Valley Pacific needed stronger authentication for Meraki VPN access without adding friction; miniOrange’s RADIUS integration, LDAP Gateway, and push MFA secured remote access.”
“Aegis Logistics faced fragmented access across SAP, SAML/OIDC applications, AD, and O365; miniOrange unified authentication with SSO and MFA.”
Extend identity controls across the applications, directories, operational systems, and access infrastructure already used across energy environments.




miniOrange IAM addresses unique vulnerabilities of the energy sector with robust MFA to prevent unauthorized access to sensitive systems, granular PAM to control high-risk accounts, and more.
miniOrange offers a modular platform that allows energy businesses to implement the security features & optimize security investments, avoiding the costs associated with disparate systems, with a scalable solution.
We boast an intuitive interface for both administrators and end-users, and simplify the implementation and ongoing management of security policies, reducing the learning curve for IT teams.
We recognize the diverse and often complex nature of the energy industry and offer highly customizable IAM solutions for various user groups, adapting to your specific requirements.
From generation and grids to renewables and oil & gas, adapt identity and access controls to the people, systems, and environments unique to each segment.
Control access for plant operators, engineers, maintenance teams, and contractors across generation facilities and the systems supporting them.
Manage identities across substations, control centers, field teams, and connected systems while maintaining appropriate access across geographically distributed infrastructure.
Centralize workforce access across utility applications, corporate systems, field locations, and critical resources without creating separate identity silos.
Secure remote technicians, engineers, contractors, and other users accessing systems across distributed solar, wind, and energy-storage facilities.
Manage employee, contractor, vendor, and privileged access across upstream, midstream, downstream, refining, and supporting enterprise environments.
Apply stronger identity controls to connected grid applications, devices, and users as distributed technologies expand the number of access points.
Energy IAM has to account for fragmented IT and OT environments, changing workforce roles, third-party access, legacy systems, and geographically distributed resources.

Connect identity sources and access controls across IT and OT environments, improving visibility and applying consistent policies to critical energy resources enterprise-wide.

Automate provisioning, approvals, role changes, and deprovisioning so employee, technician, contractor, and vendor access consistently reflects their current responsibilities and site assignments.

Govern external identities with defined roles, stronger authentication, approval workflows, and controlled permissions aligned with each contractor's or vendor's specific responsibilities securely.

Extend modern authentication to legacy applications through Access Gateway without replacing established systems or forcing extensive redevelopment across critical operational environments today.

Apply centralized authentication, MFA, and adaptive access policies across plants, substations, remote facilities, and corporate resources used by distributed field teams consistently.

Enforce role-based, least-privilege access while strengthening authentication and visibility for engineers, administrators, operators, and other users with elevated system permissions consistently everywhere.
Choose cloud, on-premises, or hybrid deployment to align with your infrastructure, security requirements, and established energy environments.


Apply identity and access controls across legacy applications, SCADA-connected environments, cloud services, and modern applications without disruptive infrastructure changes.
Address workforce identity, privileged access, identity governance, and endpoint security through complementary miniOrange solutions designed to work across your security environment.
Get 24/7 technical support from security experts for deployment, integrations, troubleshooting, configuration, and ongoing identity security requirements.
From contractors and field teams to legacy applications and IT/OT environments, give every identity the right access at the right time.
Find the right IAM capabilities to secure workforce, contractor, and critical energy access.
Download NowResources
Explore resources to help energy organizations strengthen identity security and access across their environments.
IAM controls access to critical applications, IT and OT resources, and facilities while enforcing consistent authentication and access policies across energy environments.
Yes. IAM assigns access based on roles, responsibilities, locations, and assignments, helping contractors and technicians access only the systems and resources they need.
Yes. IAM can connect identity and access controls across IT and OT while maintaining the distinct infrastructure and security requirements of each environment.
Yes. IAM can add modern authentication and access controls around legacy applications without requiring organizations to replace established systems or disrupt existing workflows.
IAM automates provisioning, approvals, role changes, and deprovisioning, helping ensure employee, contractor, and vendor permissions reflect current assignments and access requirements.
IAM can support authentication, access management, account lifecycle, and least-privilege controls relevant to NERC CIP programs, but does not independently make an organization compliant.
x
Your download should start now. If not, please email us at idpsupport@xecurify.com or contact us.