- Home
- DLP
- Guide for configuring Executable App policy
Configure miniOrange DLP solution for Executable Application Blocking and Data Protection
This guide explains how to configure the miniOrange DLP solution for application blocking to prevent data breaches. The Applications tab enables restricting access to approved desktop applications, reducing exposure to unauthorized or risky software. Admins can set up policies to block the sharing or uploading of sensitive data through certain apps, minimizing breach risks. These policies can be tailored by application type or data category, ensuring they meet security standards while allowing operational flexibility. This approach strengthens data protection and compliance through controlled application usage and sensitive data management.
Prerequisites
Configuration Steps
Step 1: Steps to configure Application Inventory
- Sign in to your DLP dashboard.
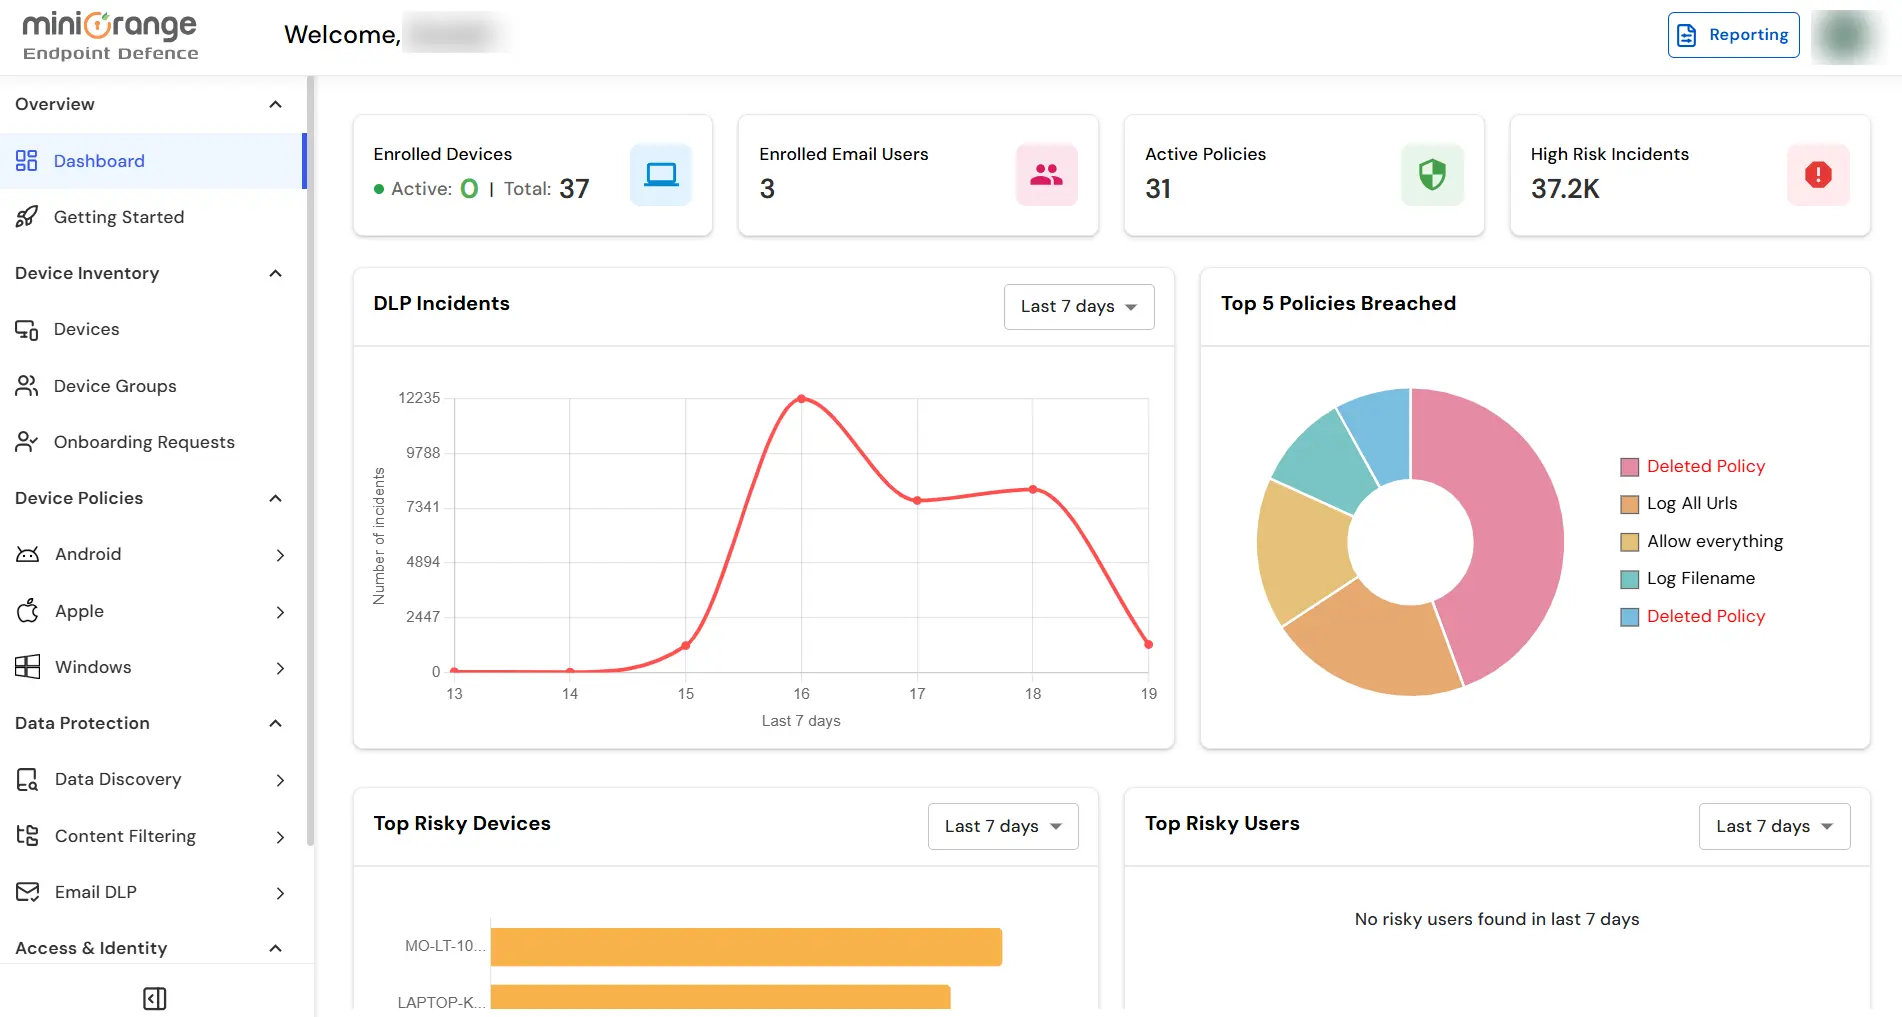
- On the dashboard, navigate to the left menu panel and then click on Endpoint Tab → Executable tab.

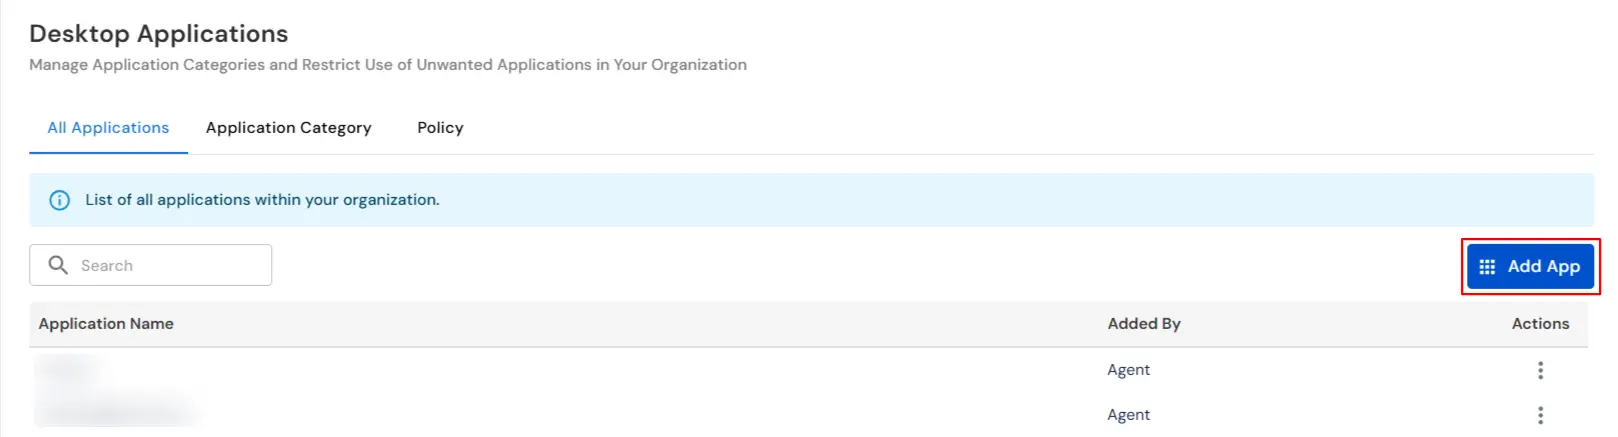
- Under the All Applications tab, click on the Add App button to add an application by providing its name.
- After adding the Application name, navigate to the Application Category tab and click on the Add App Category button.
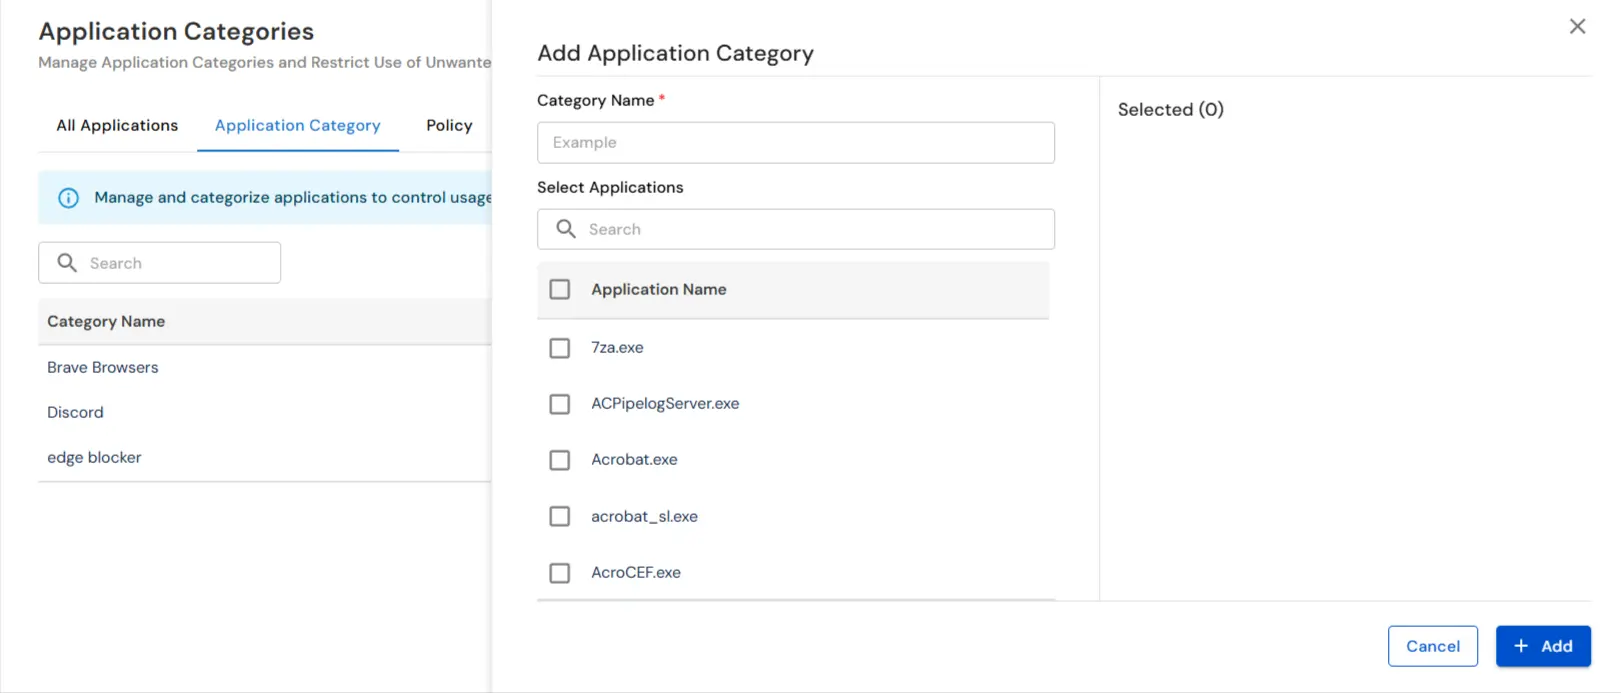
- Enter the desired Category Name and select the applications you want to include under this category and click on the Add button.
Step 2: Steps to Restrict Executables
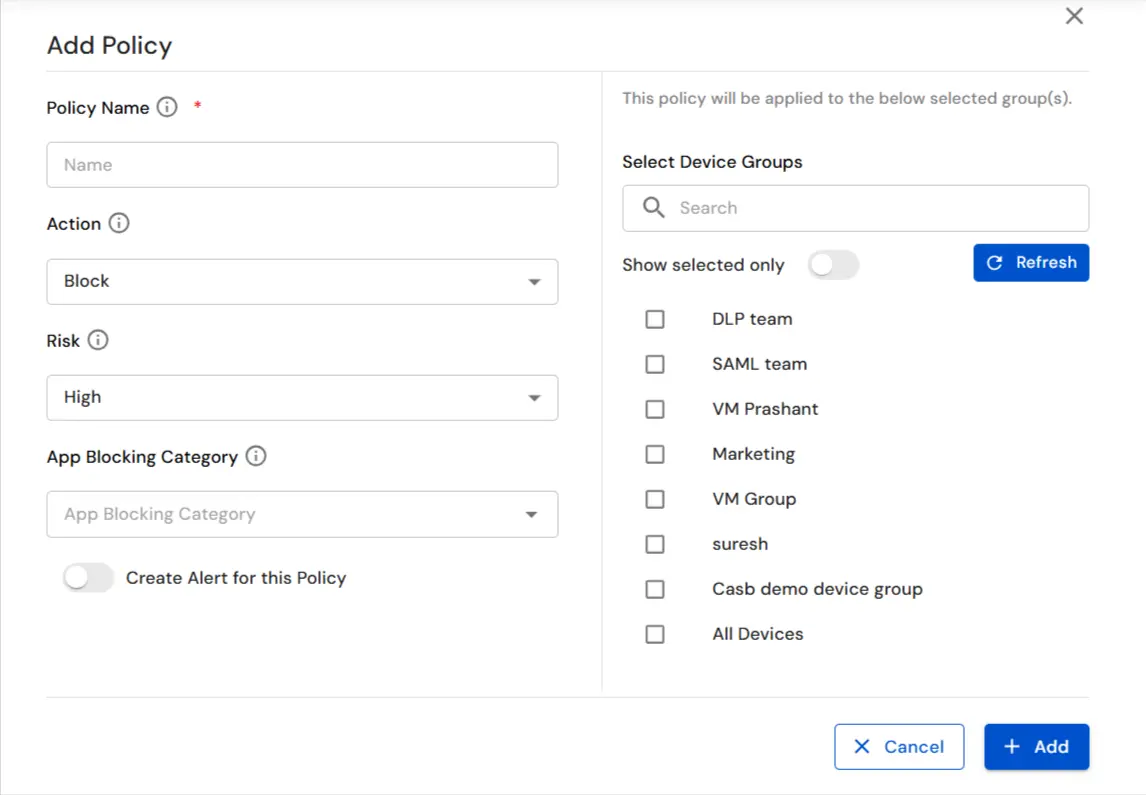
- Now, go to Endpoint Tab → Restrict Executables tab and click on the Add Policy button.

- In the Policy form provide the required policy name.
- Define the Action to be taken when a policy breach occurs. You can choose one of the following options:
- Block: This action blocks all blacklisted applications. A report will be generated listing the blocked applications.
- Log: This action generates a report containing details such as the incident time, blocked application, file hash, and other relevant information.
- Select the Risk Level from the dropdown based on the severity of the policy.
- Choose the App Blocking Category you wish to blacklist.
- You can also enable the Notification Alert toggle to send email alerts upon a policy breach. Enter the email address where notifications should be sent.
Step 3: Reporting
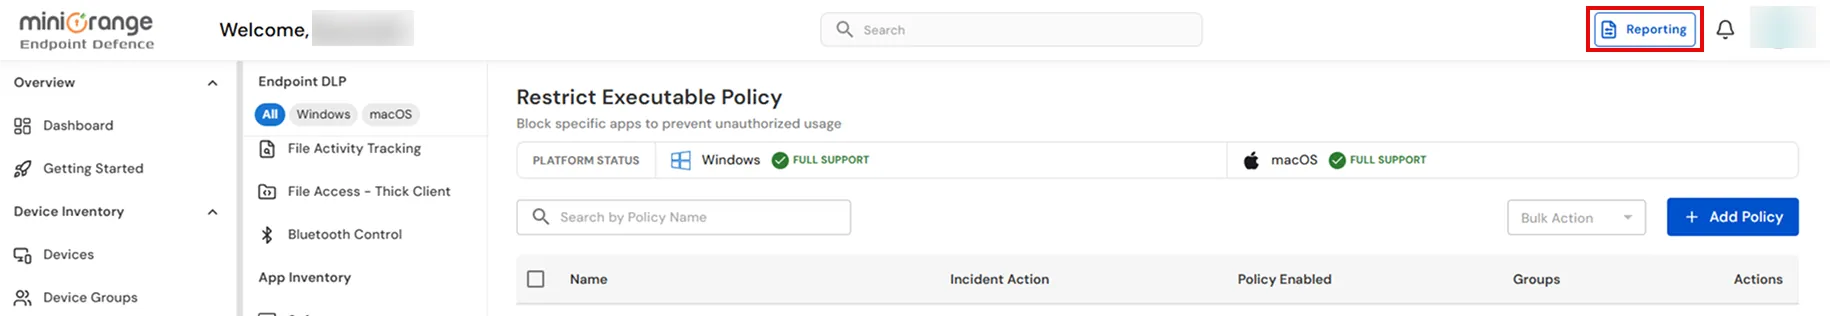
- Click the Reporting button in the top-right corner of the miniOrange DLP dashboard to view policy activity and reports.
- From the left navigation panel, select Executable to view executable-related policy events across managed devices.
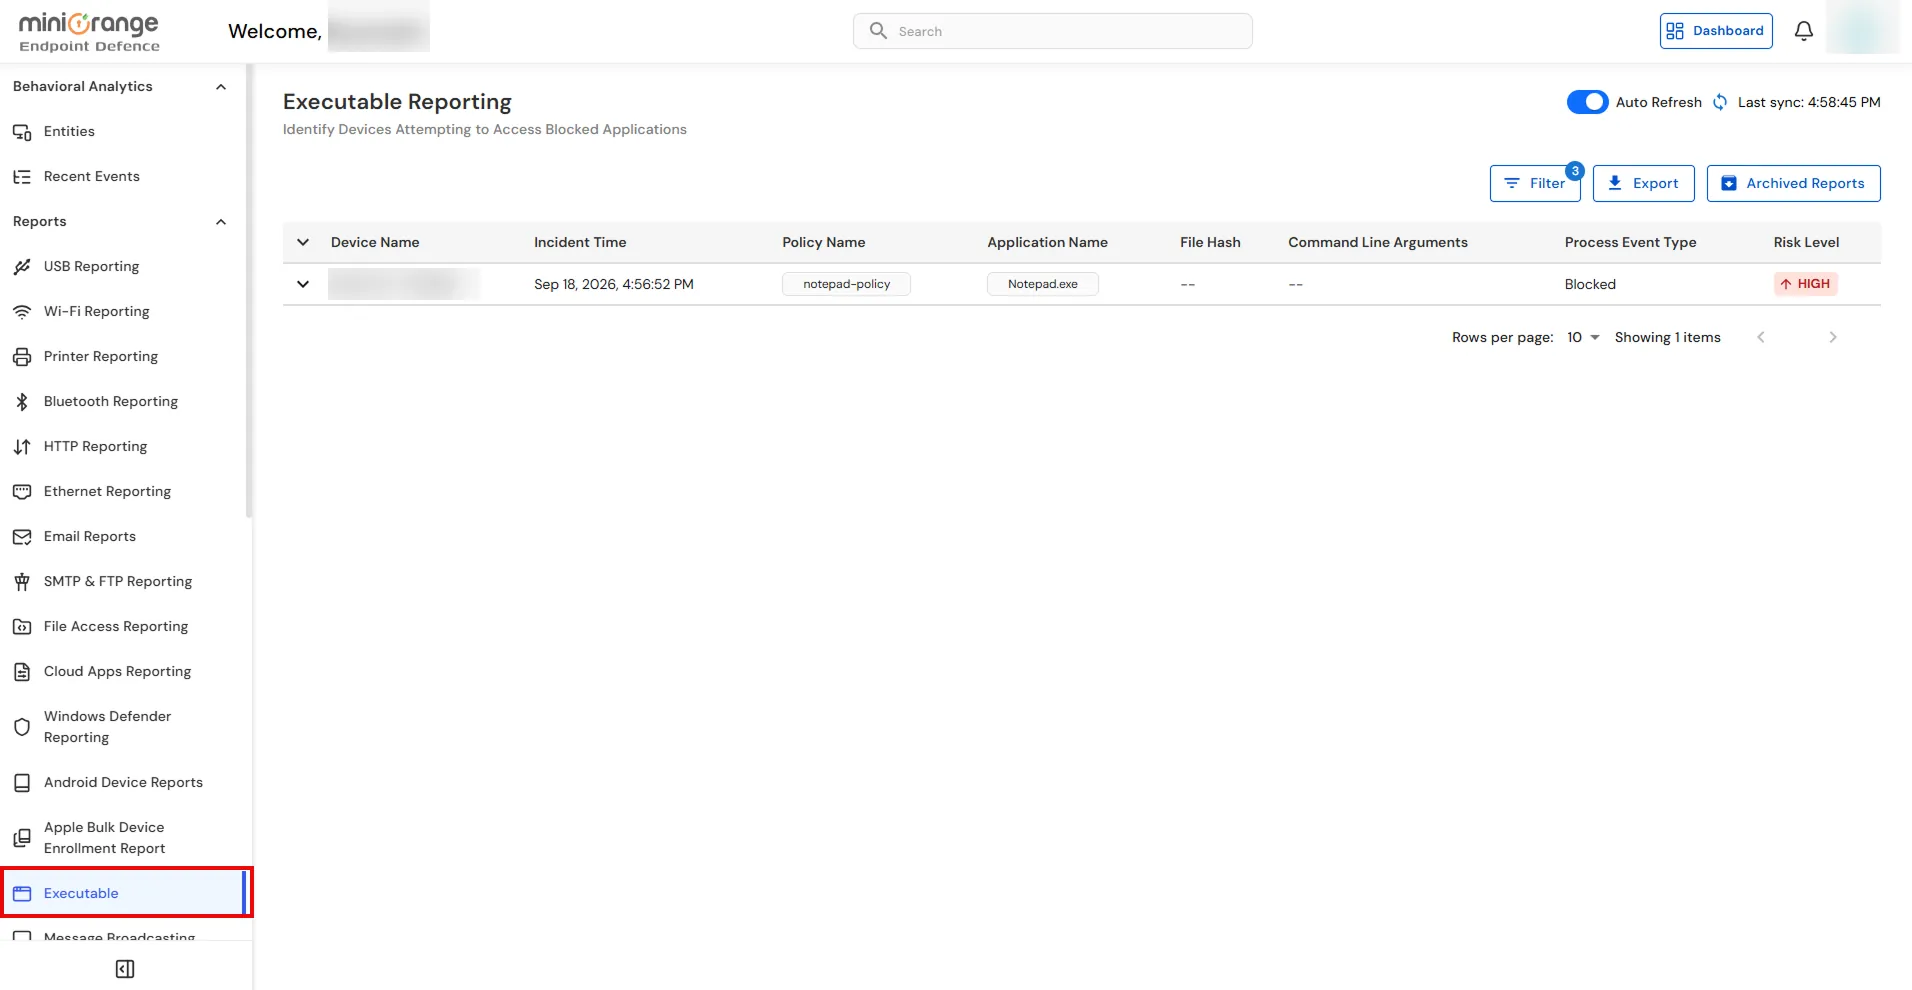
- Use the Filter option to narrow down executable reports by Device, Policy, and the required From and To dates, then click Apply to view the filtered report.
- Click Export to download the executable report for auditing, investigation, and compliance purposes.
- To download an archived report, click Archived Reports, select the required Year, Quarter, and Chunk, and then click Download.
In this way you have successfully setup the Executable App Policy and accessed its reports using our DLP solution. Also if you are facing any issues that you are not able to resolve please feel free to reach out to us at uemsupport@xecurify.com