Hello there!
Need Help? We are right here!

Need Help? We are right here!
Search Results:
×Thunderbird is an application, so it does not provide email addresses, nor the service to transmit emails. But Thunderbird can be used with your existing email address and service provider to send, receive, sort and search your email messages.
Internet Service Providers (ISPs): When you sign up for internet access through an ISP they usually give you one or more email accounts.
Web-based: Many web sites provide email accounts. These include email providers like Google, Yahoo!, Outlook, Hotmail and many others.
Corporate: Employers often provide their employees with email accounts.

miniOrange supports both IdP (Identity Provider) and SP (Service Provider) initiated Single Sign On (SSO)
In IdP Initiated Login, SAML request is initiated from miniOrange IdP.
In SP Initiated Login, SAML request is initiated by Thunderbird.
miniOrange Identity Management Features
miniOrange Single Sign-On (SSO) Solution provides easy and seamless access to all enterprise resources with one set of credentials. miniOrange also provides secure authentication by establishing a trust relationship between the Service Provider and Identity Provider. miniOrange Single Sign-On supports SSO to any type of device or application whether they are in the cloud or on-premise. Learn More
Secure your Thunderbird application from password theft using multi-factor authentication methods with 15+ authentication types provided by miniOrange. Our multi-factor authentication methods prevent unauthorized users from accessing information and resources having passwords alone as an authentication factor. Enabling second-factor authentication for Thunderbird protects you against password thefts. Learn More
miniOrange provides IP blocking/IP restriction for Thunderbird login which adds security to Gmail, Web, and other applications. In this, we provide you option for IP blocking which includes both automatic (based on user behavior) and manual IP blocking which includes blacklisting and whitelisting of IP addresses to provide access restriction, the office only access, intranet access & network restriction. Learn More
miniOrange Adaptive Authentication aims to provide a better experience to reduce the authentication burden on users while enforcing strong authentication where it is needed the most. For example, when a user attempts to access an application via an unregistered device then they may be prompted to register it. If the user logs in from a geographical location other than their office, they may be asked to answer security questions. Learn More
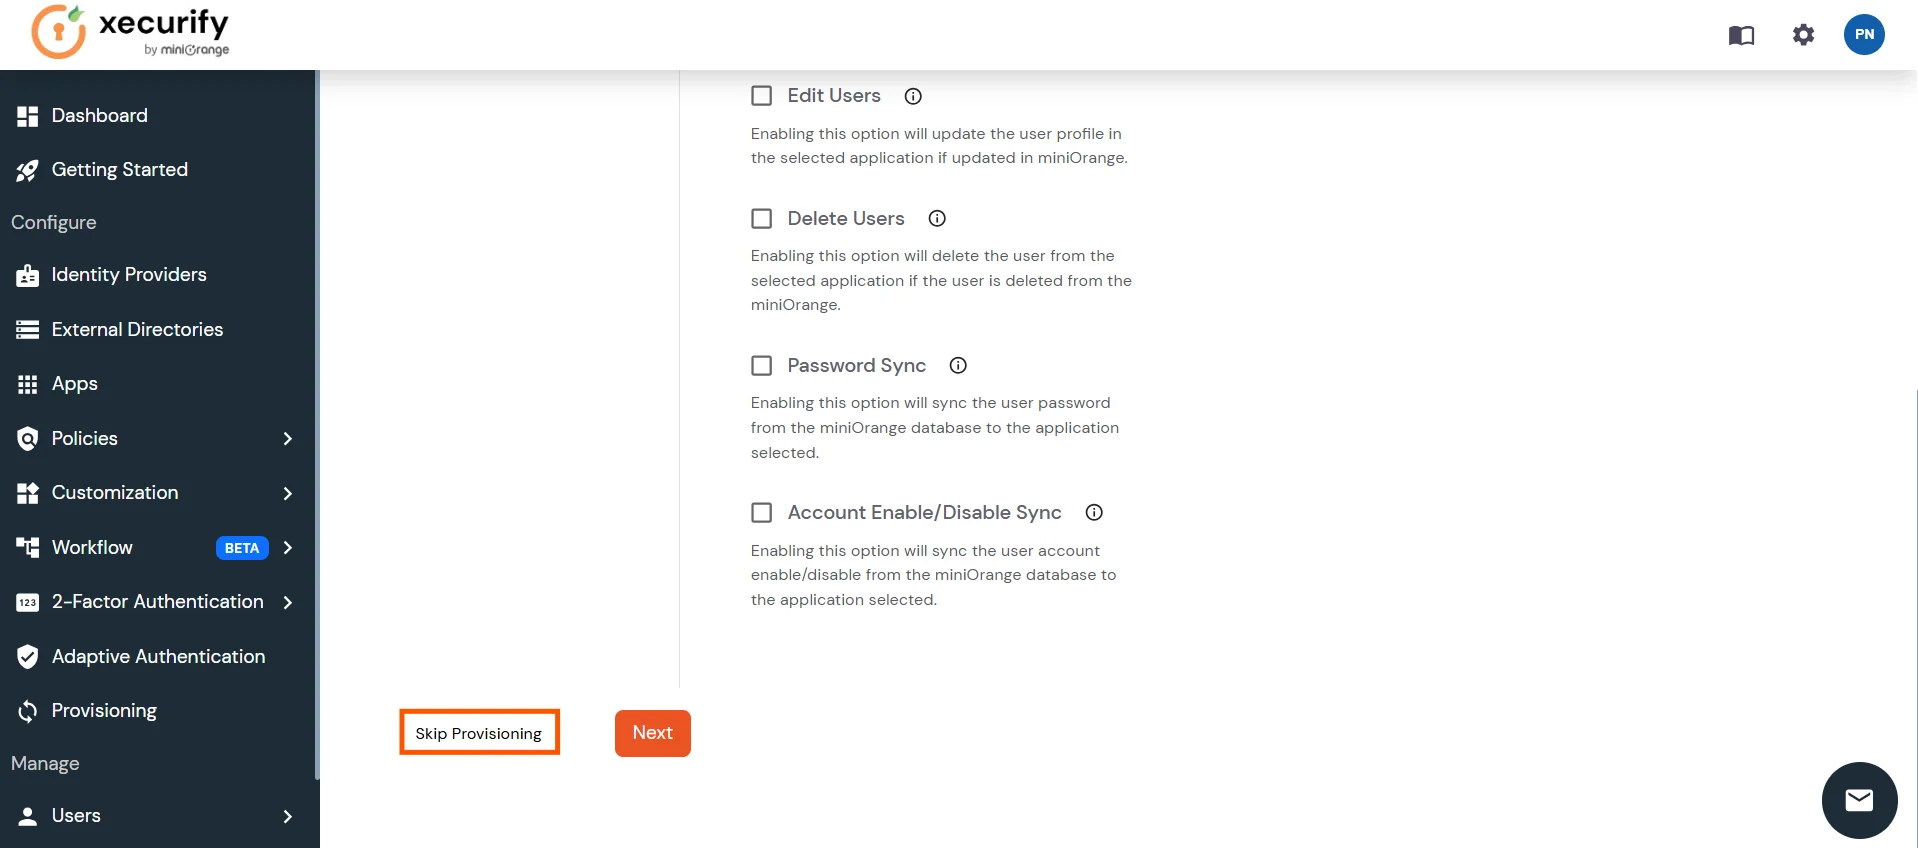
miniOrange User Provisioning provides an easy way of creation, management, and maintenance of end-users especially for large enterprises to reduce the risk for unauthorized access of information. User provisioning includes the creation, updating and deletion of user accounts. User provisioning makes life easier for admins because they do not have to manually arrange access for each user. Learn More
miniOrange provides user authentication from external directories like ADFS, Microsoft Active Directory, Microsoft Entra ID, OpenLDAP, Google, AWS Cognito etc. It also provides user authentication with other IDPs like Shibboleth, PING, Okta, OneLogin, KeyCloak and many more.
Can't find your IDP ? Contact us on idpsupport@xecurify.com. We'll help you set it up in no time.
1.1: Setup AD as User Directory










Here's the list of the attributes and what it does when we enable it. You can enable/disable accordingly.
| Attribute | Description |
|---|---|
| Activate LDAP | All user authentications will be done with LDAP credentials if you Activate it |
| Fallback Authentication | If LDAP credentials fail then user will be authenticated through miniOrange |
| Enable administrator login | On enabling this, your miniOrange Administrator login authenticates using your LDAP server |
| Show IdP to users | If you enable this option, this IdP will be visible to users |
| Sync users in miniOrange | Users will be created in miniOrange after authentication with LDAP |
Attribute Name sent to SP = organization
Attribute Name from IDP = company








Set up AD as External Directory configuration is complete.
Note: Refer our guide to setup LDAP on windows server.
1.2: Setup miniOrange as a User Store
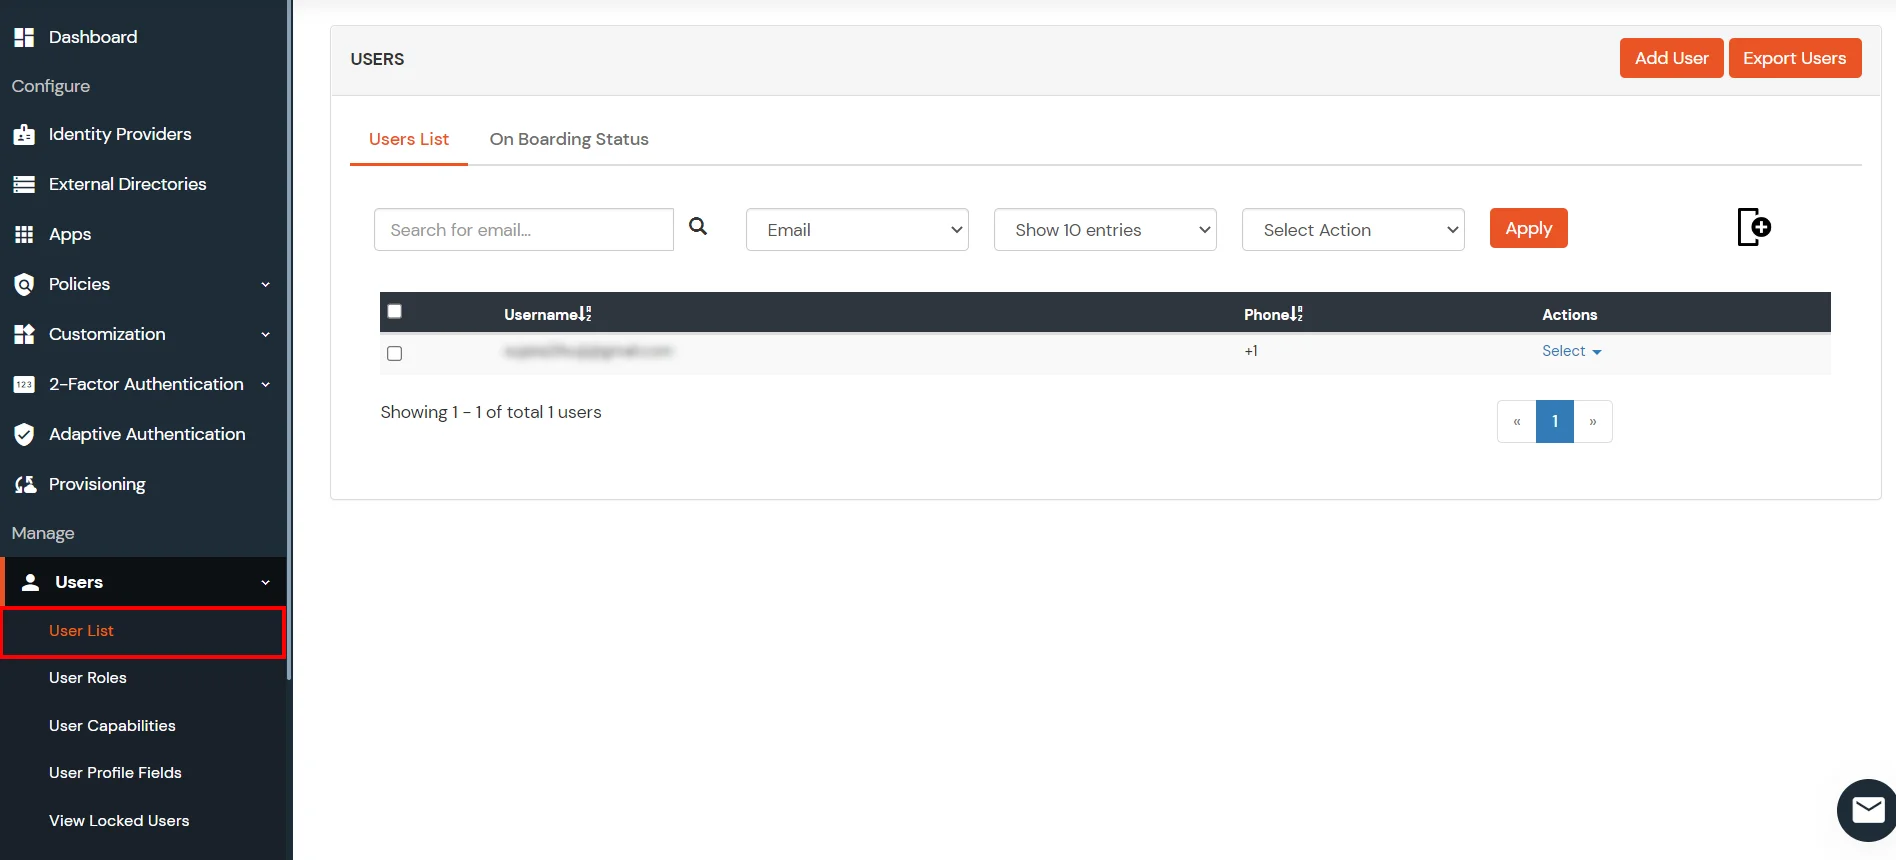
1.2.1 Create User in miniOrange





1.2.2 Bulk Upload Users in miniOrange via Uploading CSV File.


1.2.3 Self User Registration
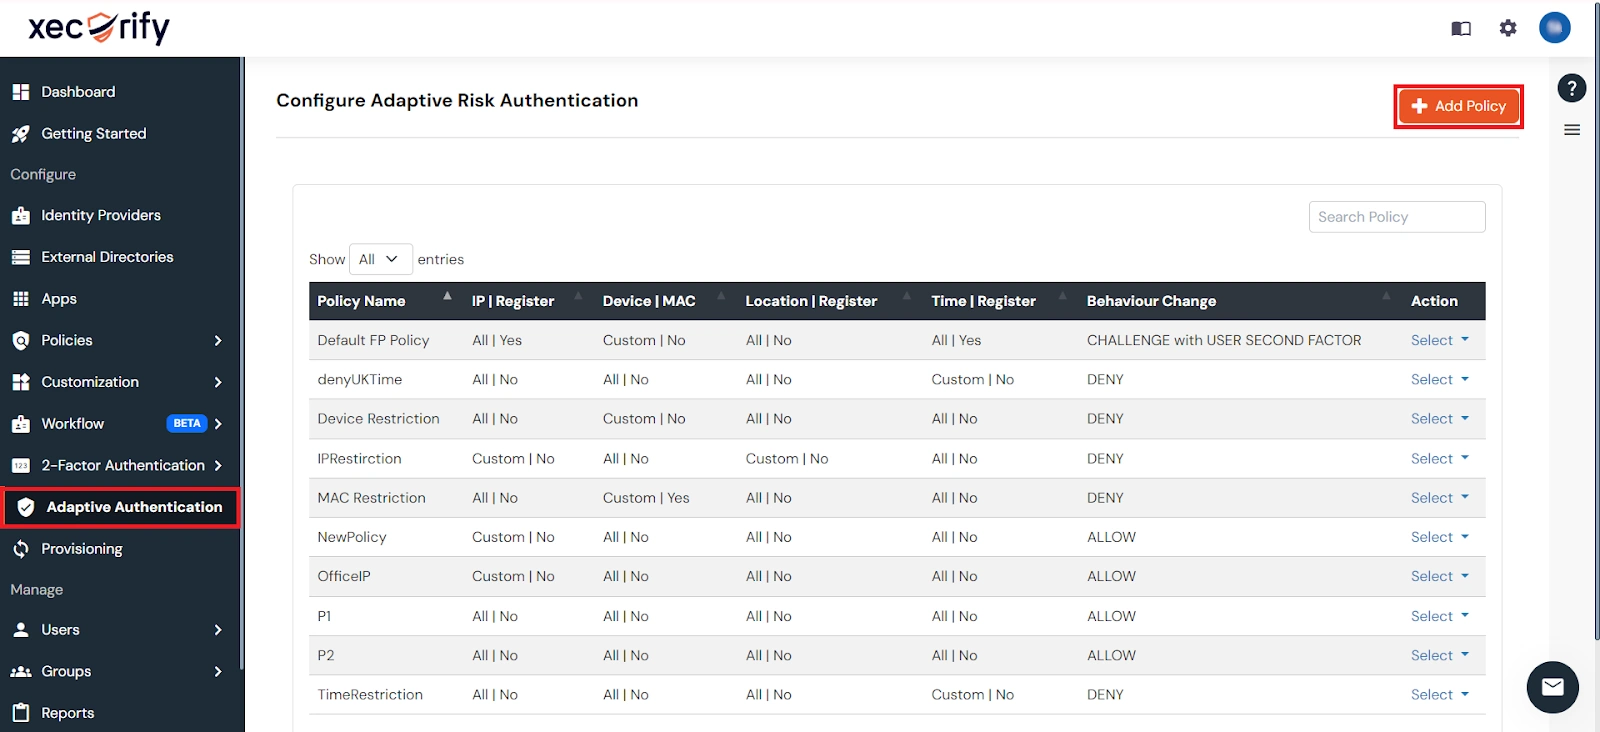
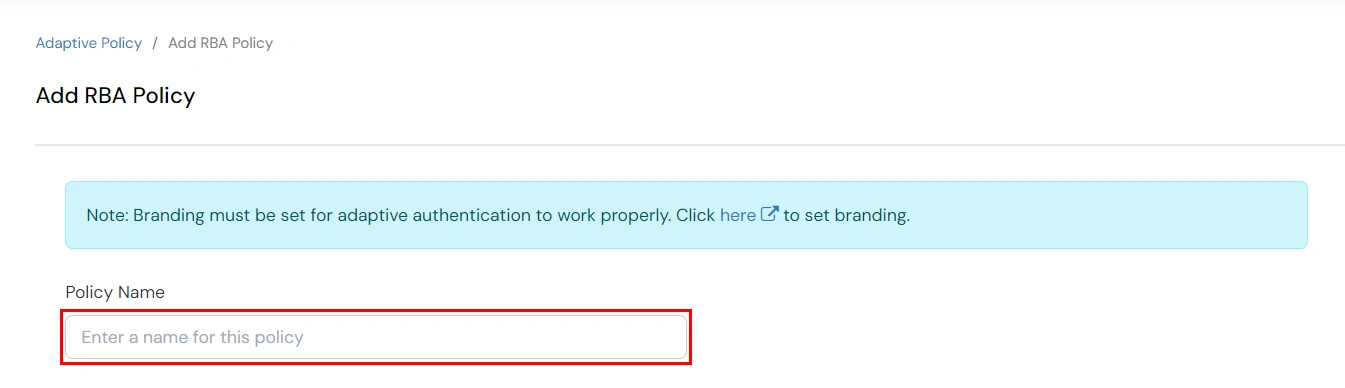
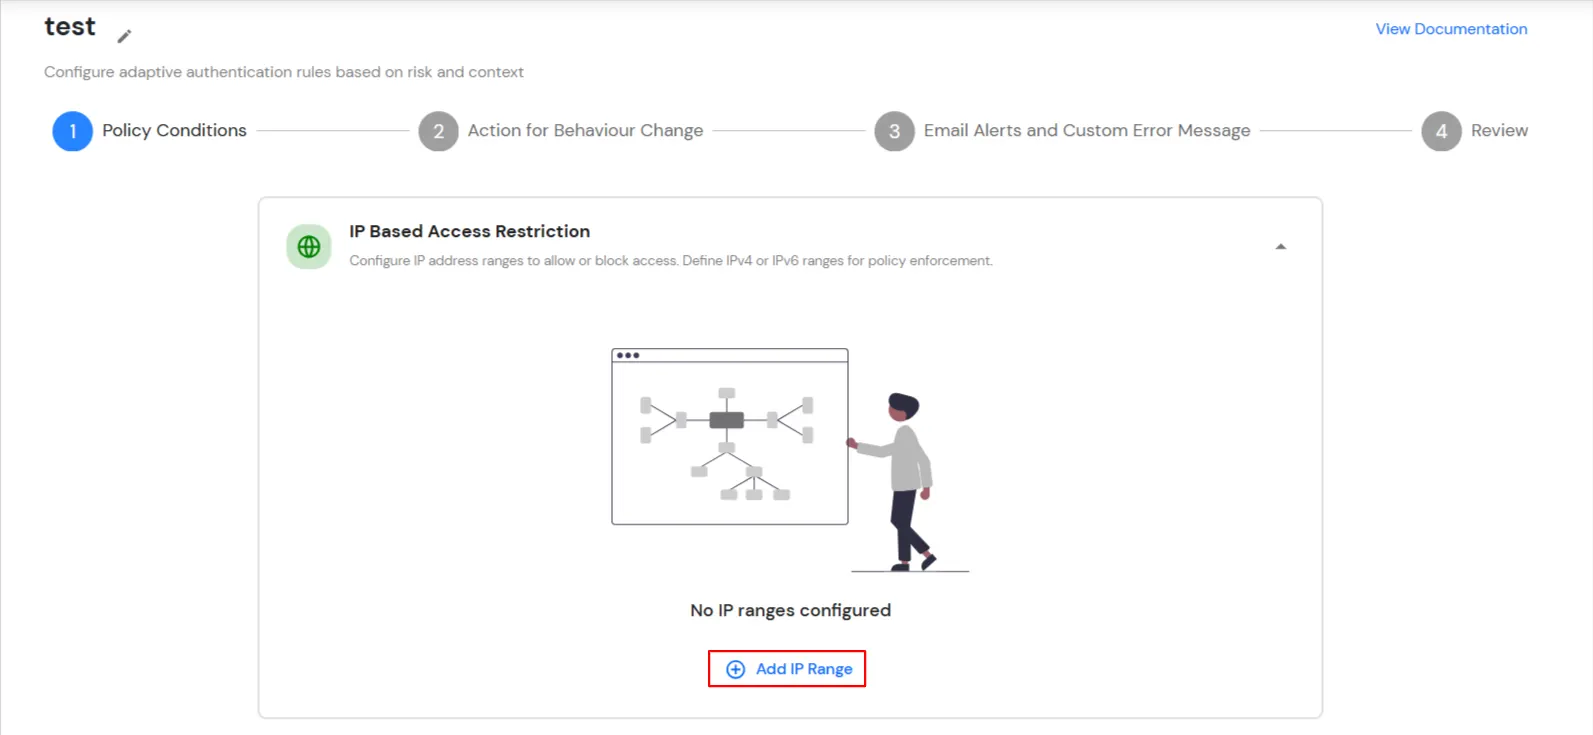
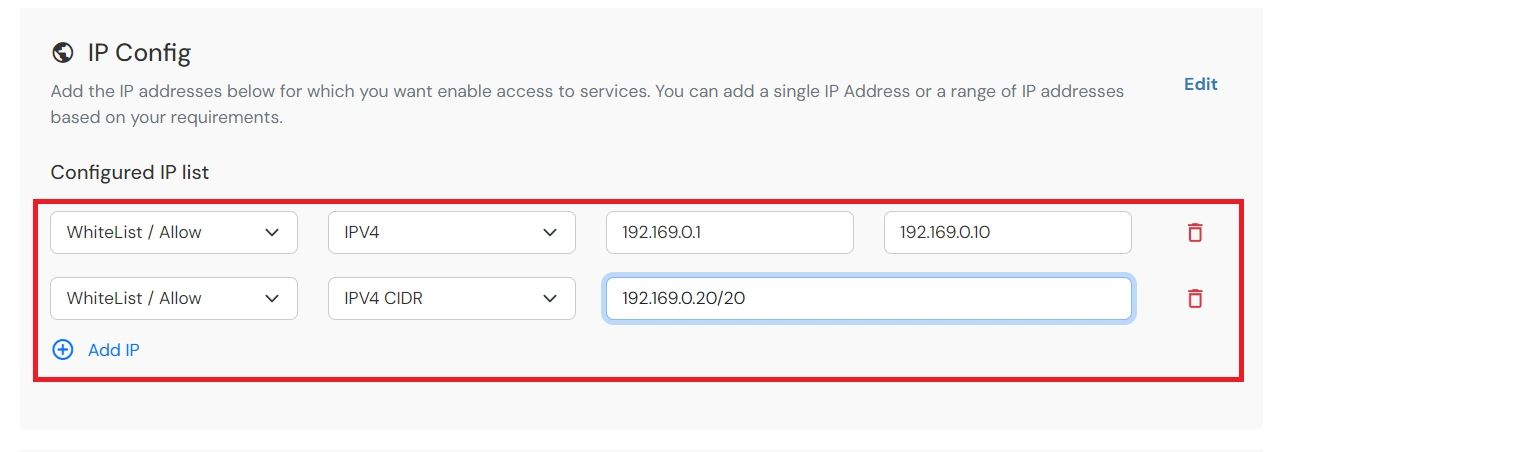
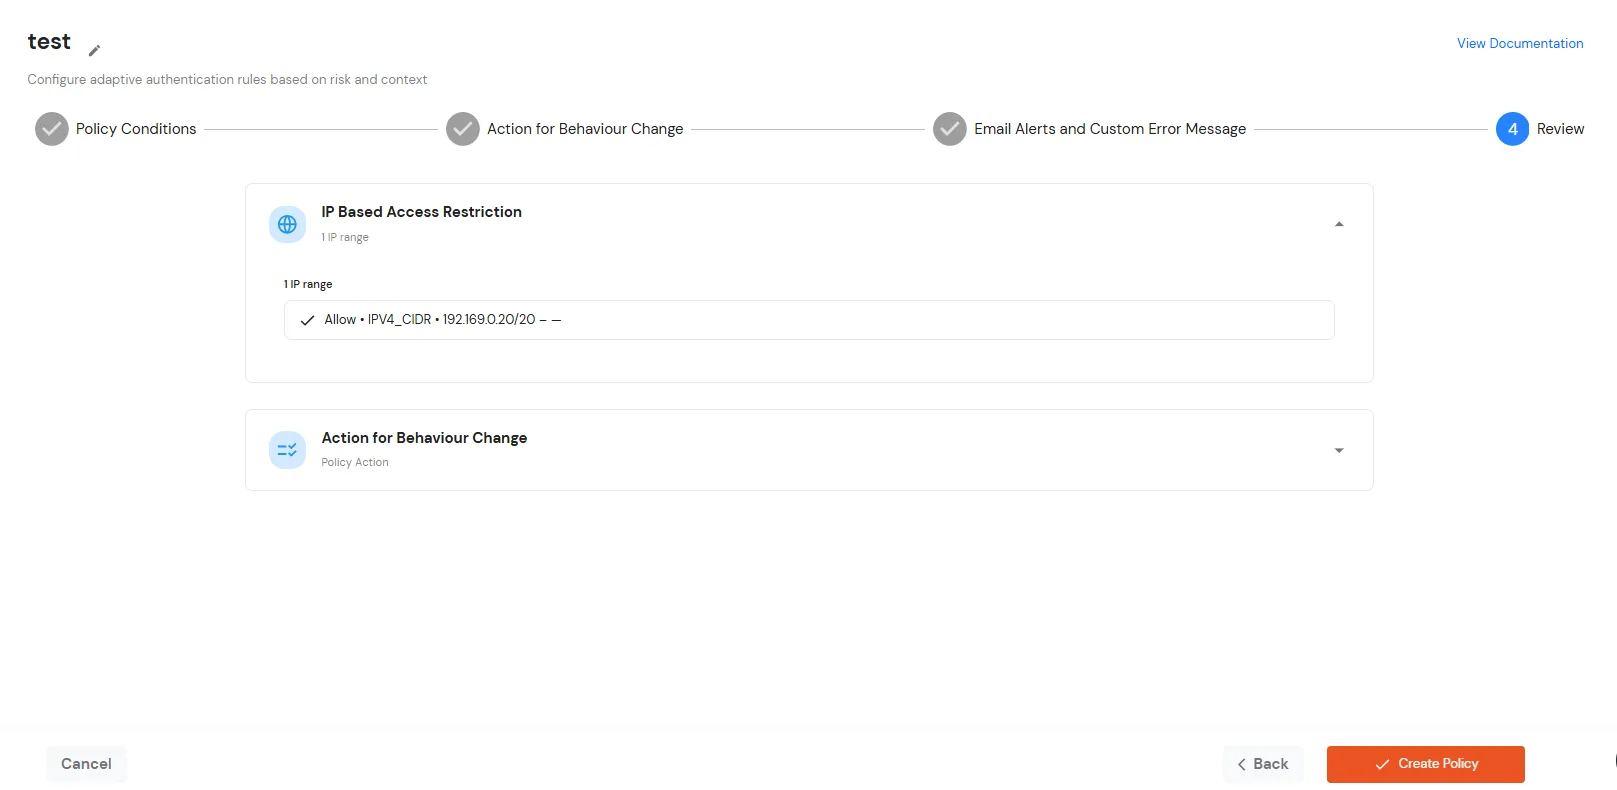
IP Based Access Restriction allows administrators to control user access based on the source IP address of the login request. Administrators can configure trusted or restricted IP addresses and IP ranges and define the action to be taken when a user's IP address matches the configured criteria. During authentication, the user's IP address is evaluated against the configured policy and access is either Allowed, Denied or Challenged based on the selected configuration.
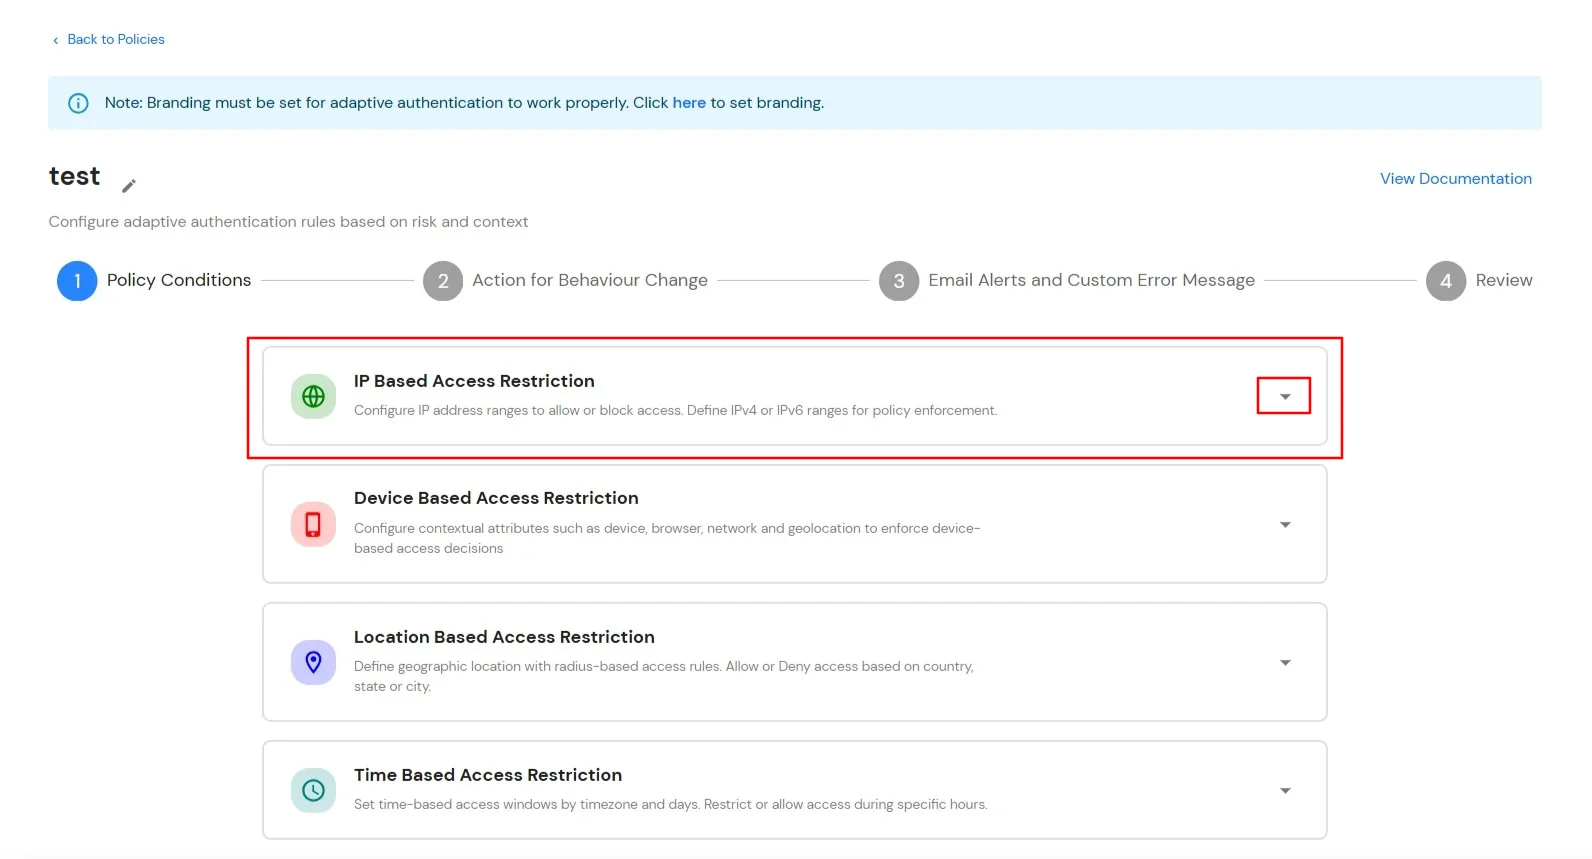
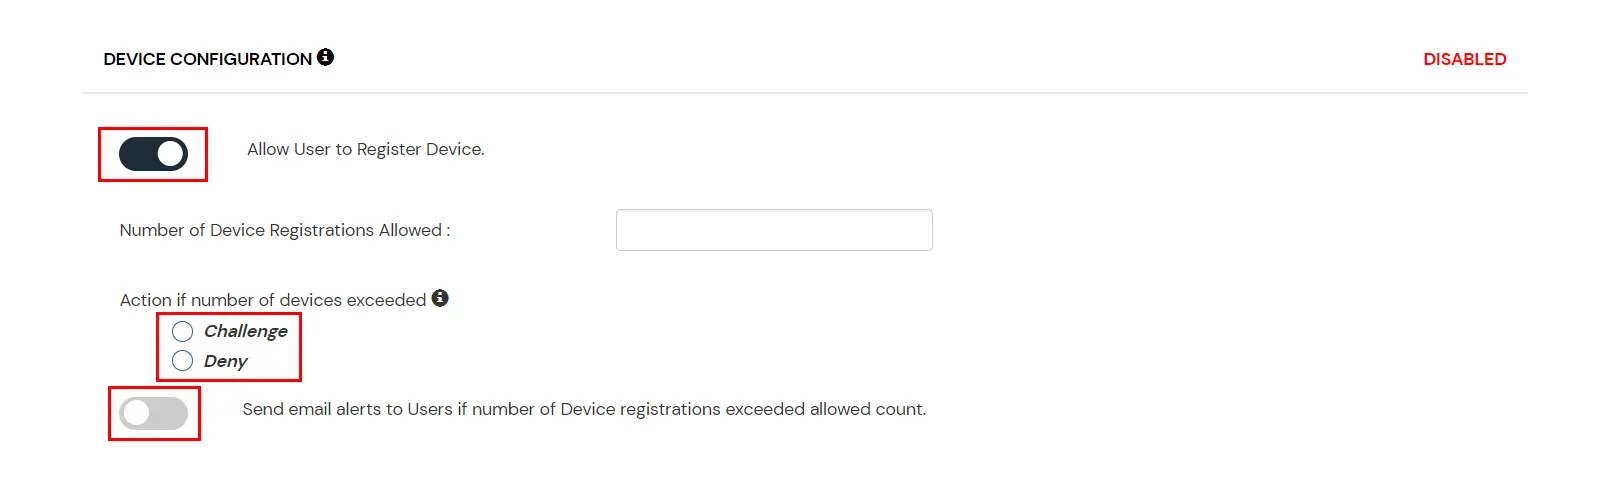
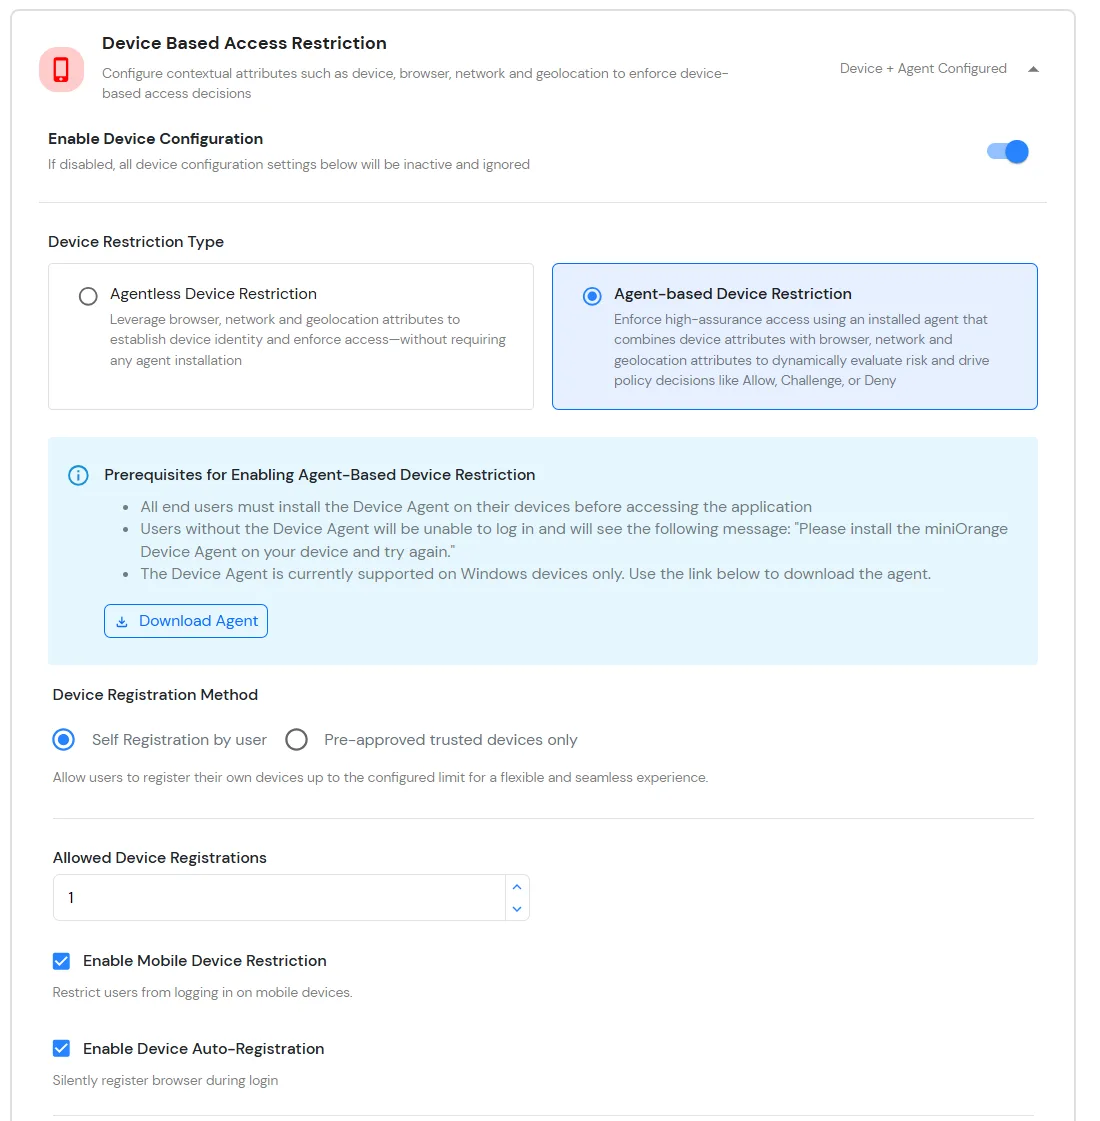
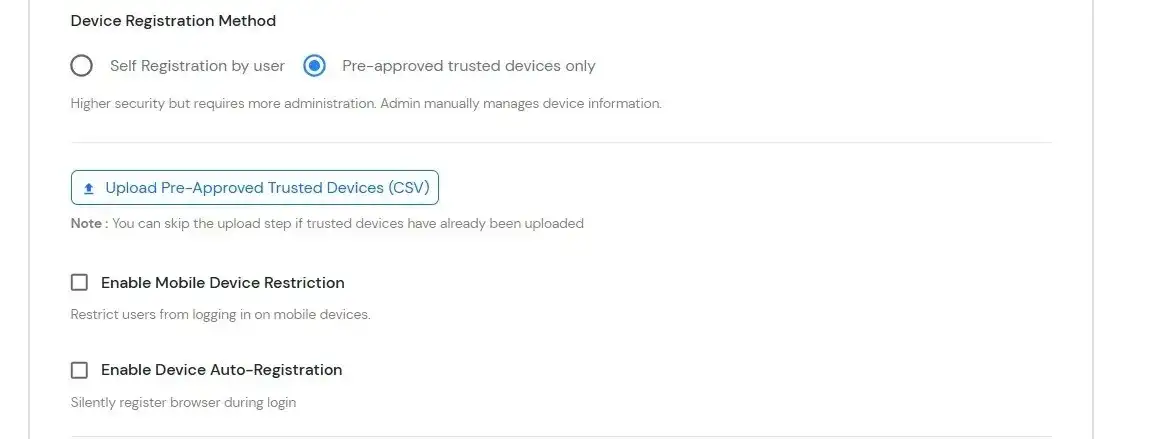
Device restriction lets admins control application access using device trust. You can use Agentless Device Restriction (browser-based fingerprinting) or Agent-Based Device Restriction (installed agent with risk scoring) depending on your security requirements.
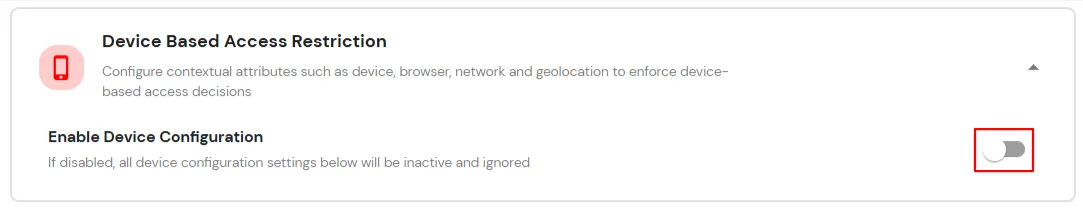
Agentless Device Restriction
Agent-Based Device Restriction
The Risk Engine allows you to evaluate device trustworthiness by analyzing multiple device attributes and calculating a risk score. Based on this score, user access is allowed, challenged or denied during login and device registration.

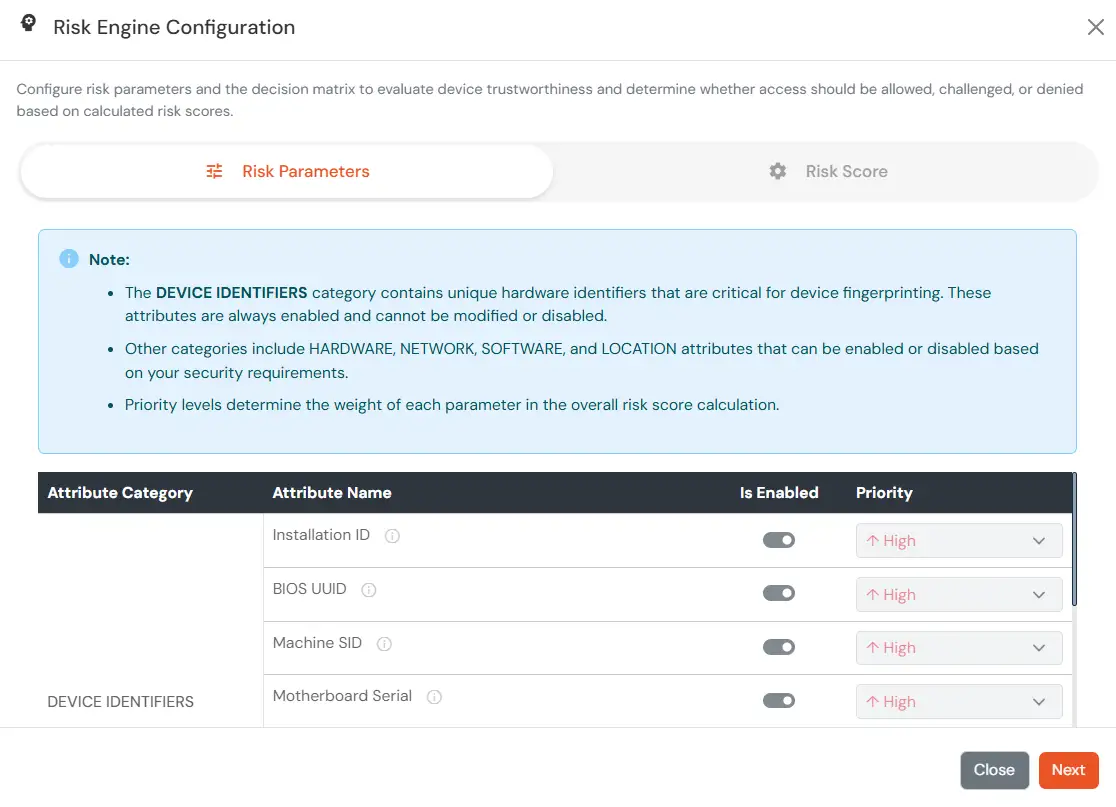
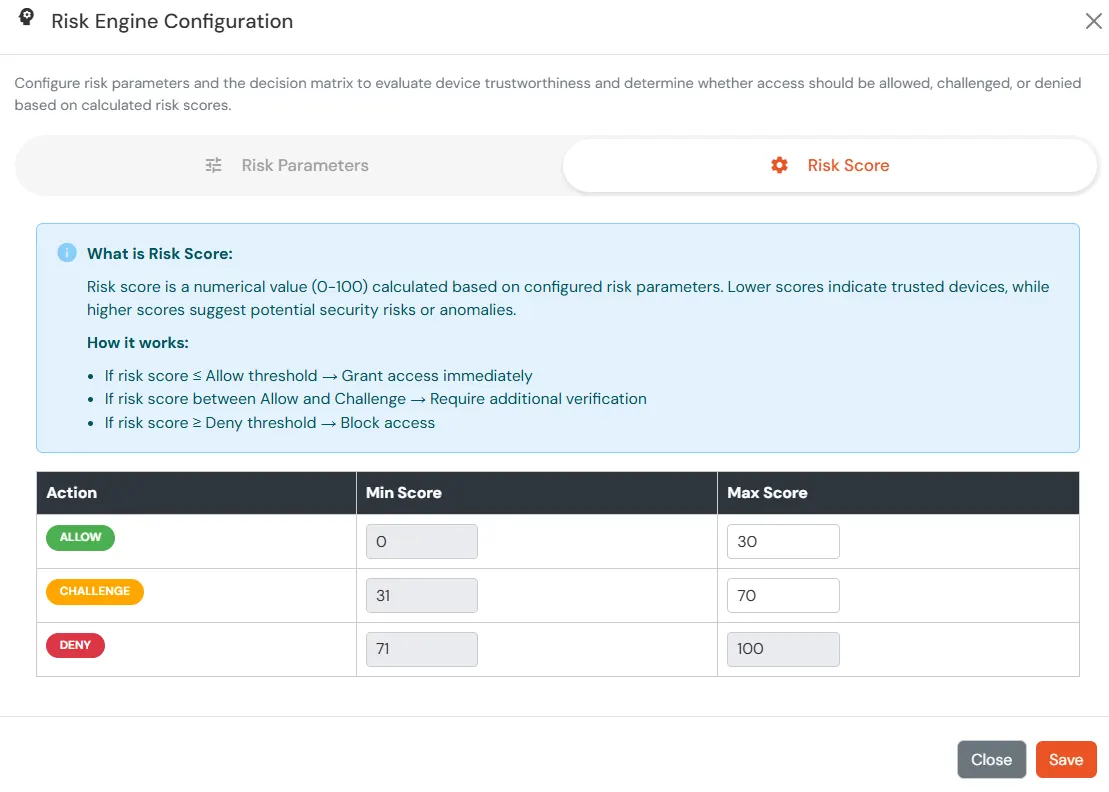
In location restrictions, the admin configures a list of locations where they want to allow or deny end-user access based on the condition set by the admin. When a user tries to log in with Adaptive Access Policy enabled, their location attributes, such as latitude, longitude and country code, are verified against the location list configured by the admin. Based on this, the user will be either allowed, challenged or denied.
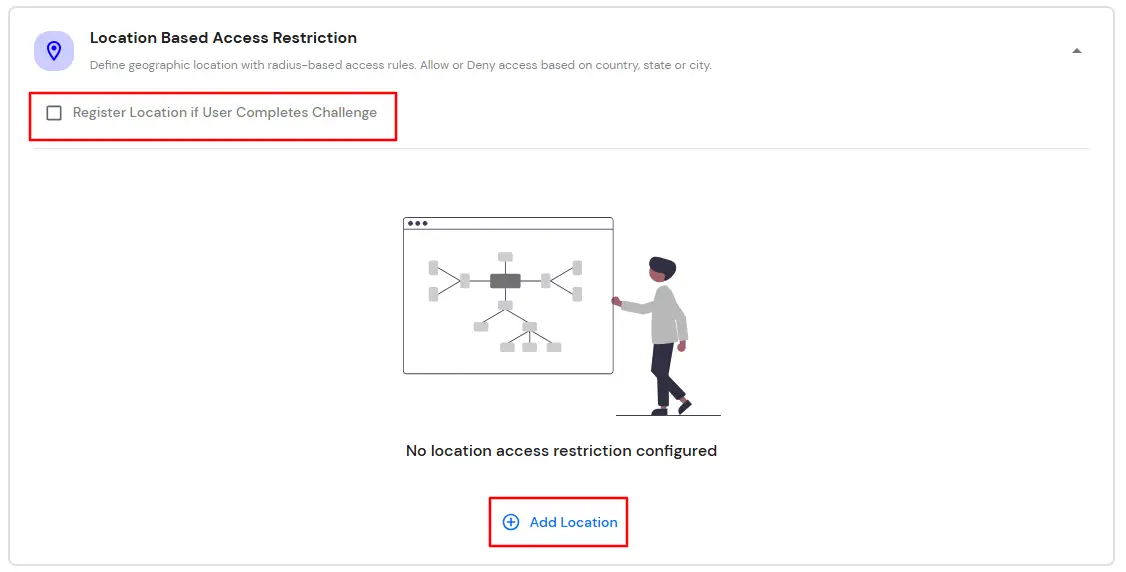
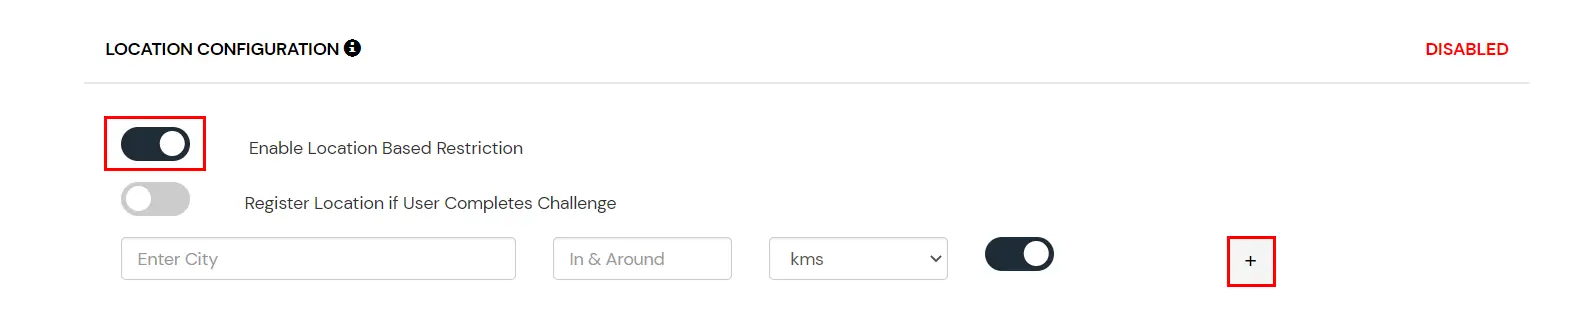
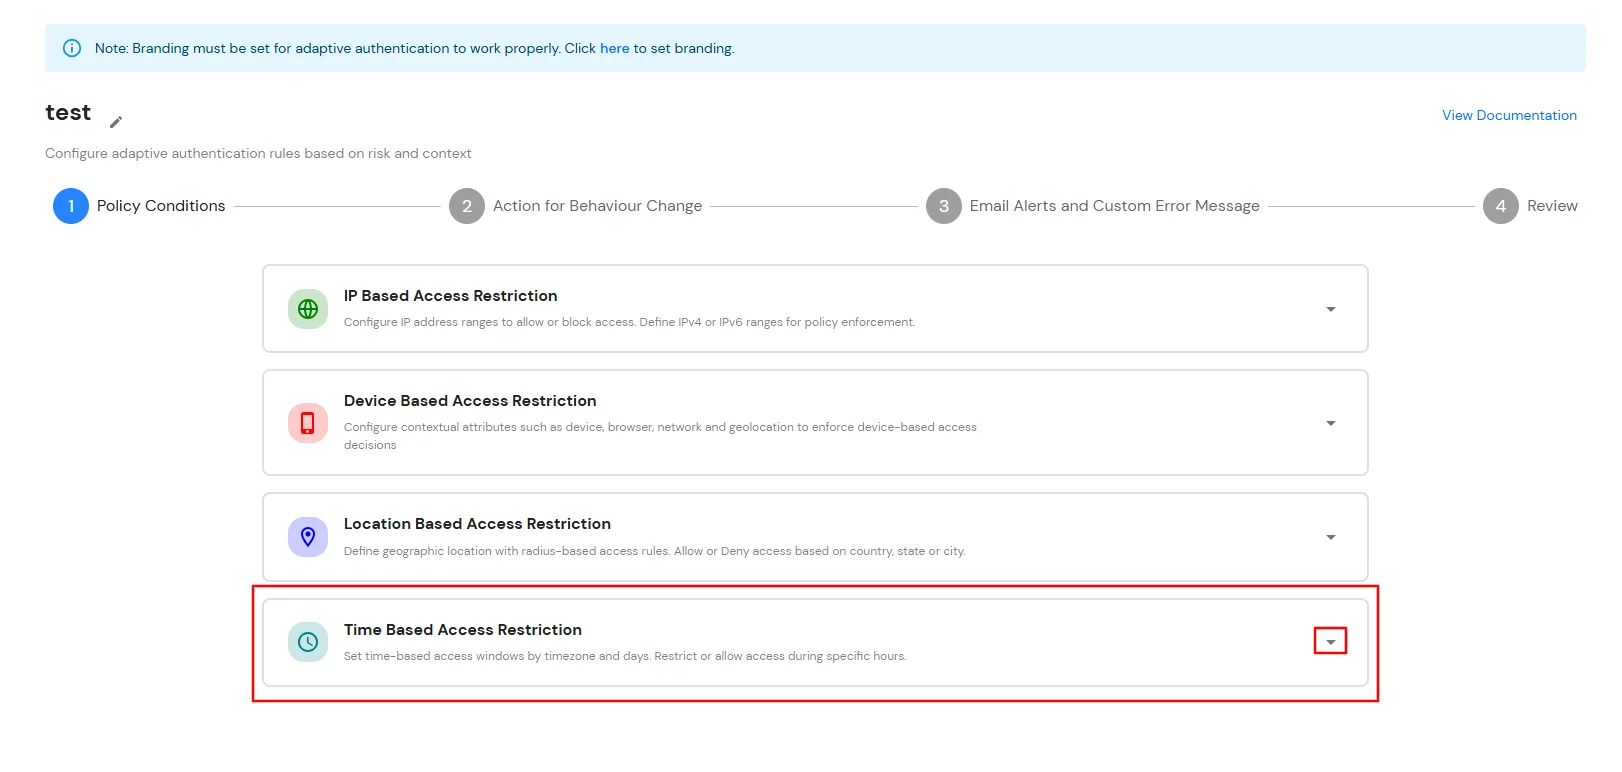
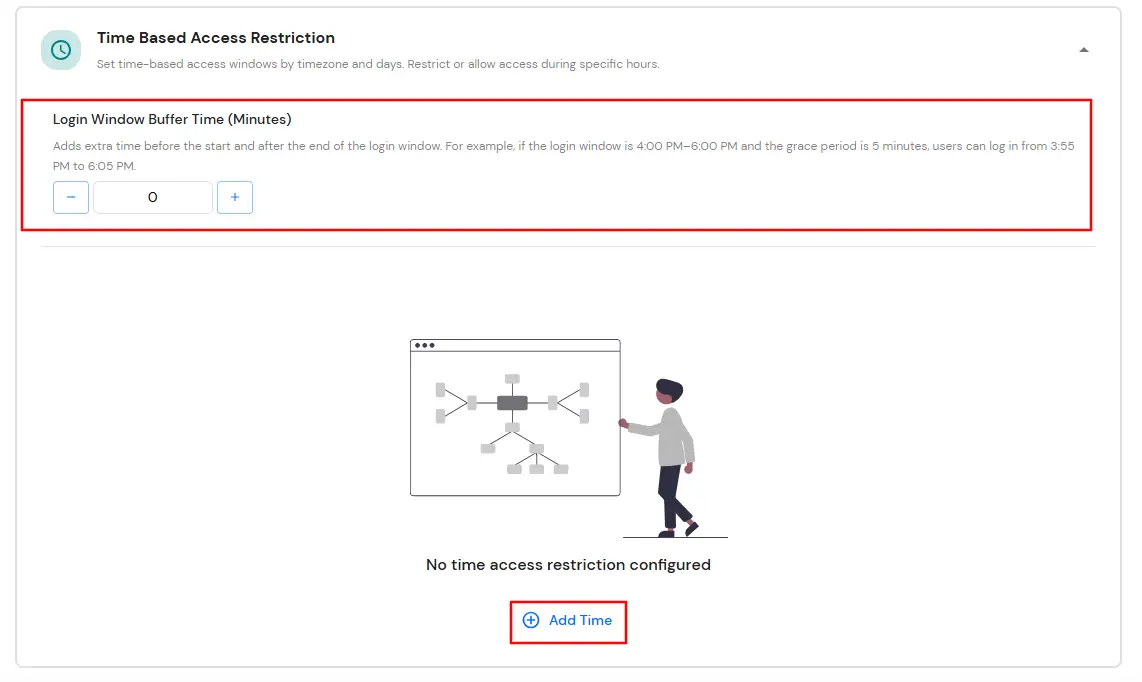
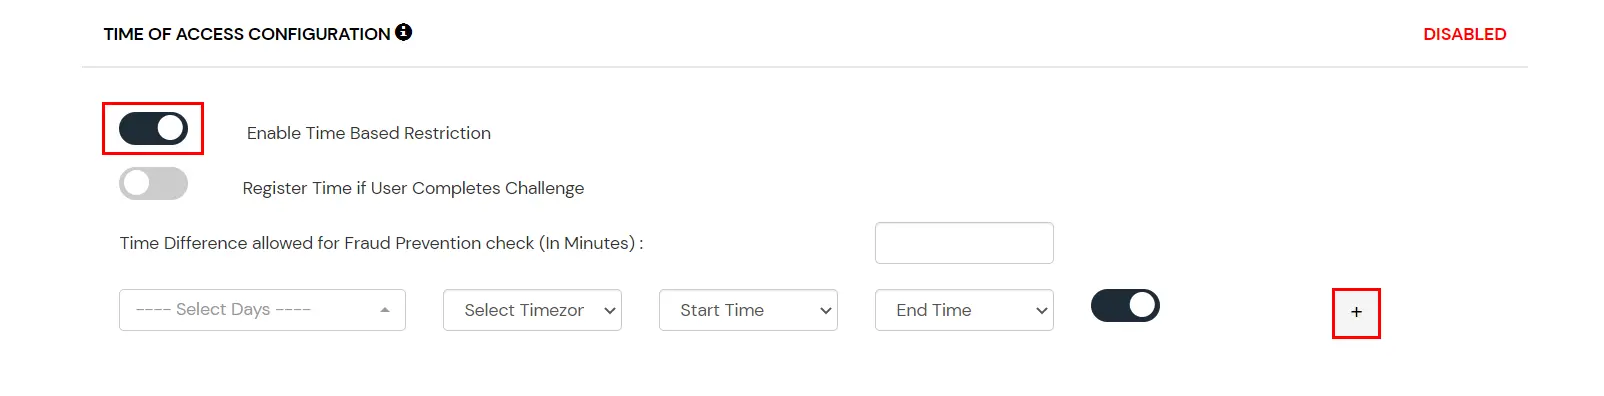
In time restriction, the admin configures a time zone with start and end times and users are either allowed, denied or challenged based on the condition in the policy. When an end-user tries to log in with Adaptive Access Policy enabled, their time zone-related attributes, such as time zone and current system time, are verified against the list configured by the admin. Based on the configuration, the user is either allowed, denied or challenged.
| Attribute | Description |
|---|---|
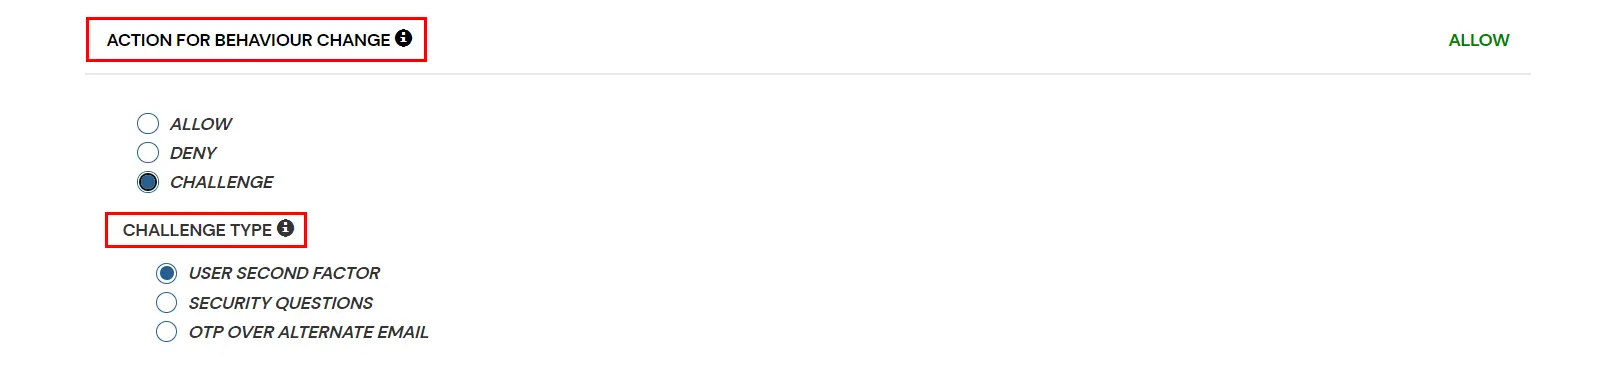
| Allow | Allow users to authenticate and use services if Adaptive Access Policy condition is true. |
| Deny | Deny user authentications and access to services if Adaptive Access Policy condition is true. |
| Challenge | Challenge users with one of the three methods mentioned below for verifying user authenticity. |
Challenge Type Options:
| Factors | Description |
|---|---|
| User Second Factor |
The user needs to authenticate using the second factor they have selected or been assigned, such as
|
| KBA | The system will ask the user for 2 of 3 questions they have configured in their Self-Service Console. Only after the correct answers to both questions will the user be allowed to proceed further. |
| OTP over Alternate Email | User will receive an OTP on the alternate email they have configured through the Self Service Console. Once the user provides the correct OTP, they are allowed to proceed further. |
This section handles the notifications and alerts related to Adaptive Authentication. It provides the following options:
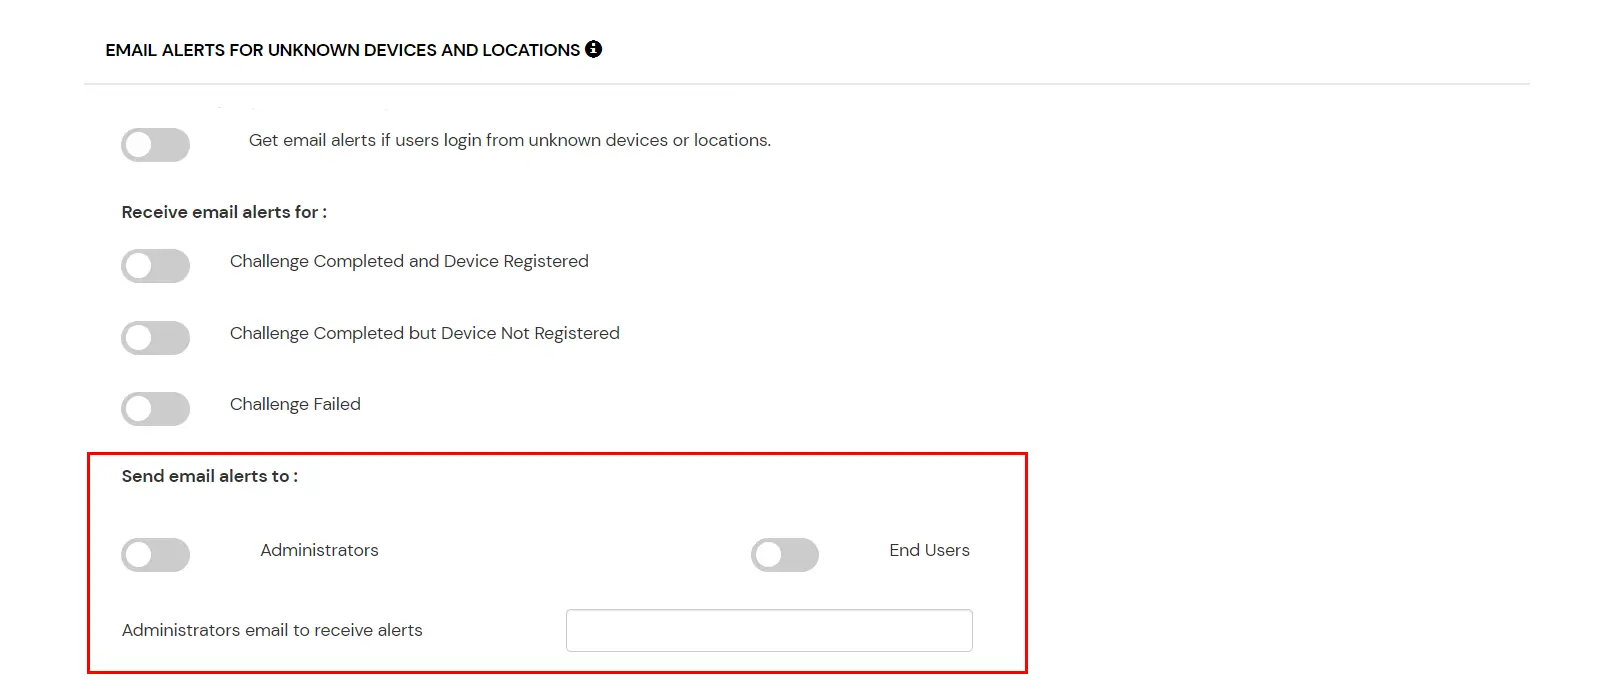
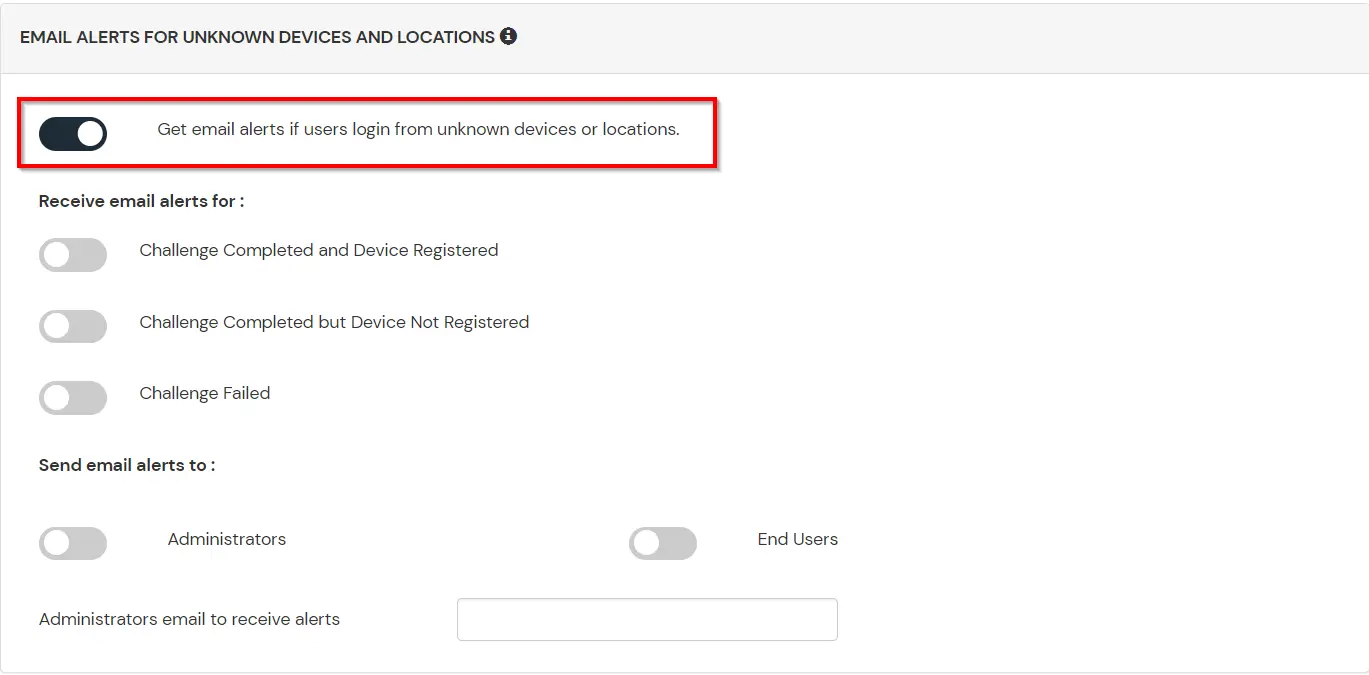
| Option | Description |
|---|---|
| Users login from unknown IP addresses, devices or locations | Enabling this option allows you to login from unknown IP addresses or devices and even locations. |
| Challenge Completed and Device Registered | Enabling this option allows you to send an email alert when an end-user completes a challenge and registers a device. |
| Challenge Completed but Device Not Registered | Enabling this option allows you to send an email alert when an end-user completes a challenge but do not registers the device. |
| Challenge Failed | Enabling this option allows you to send an email alert when an end-user fails to complete the challenge. |
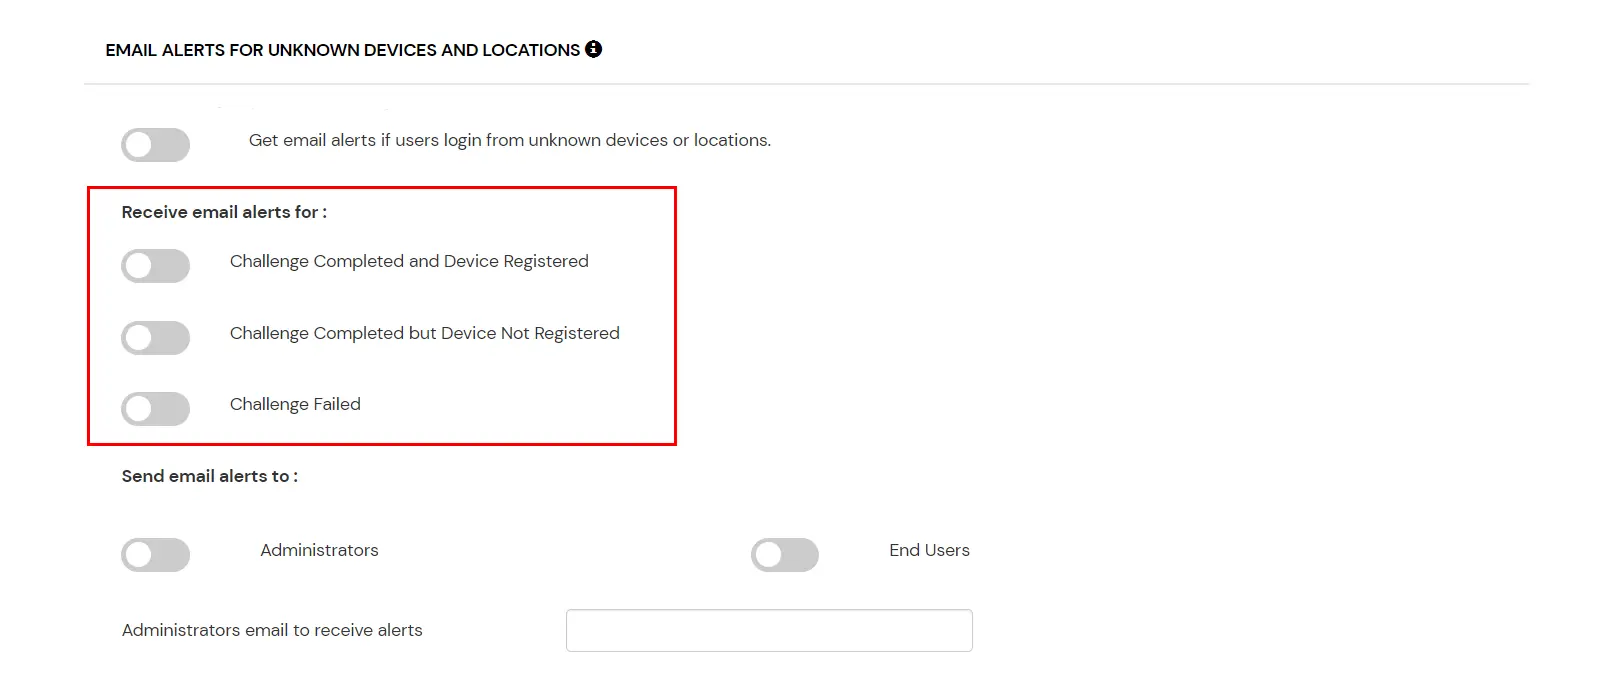
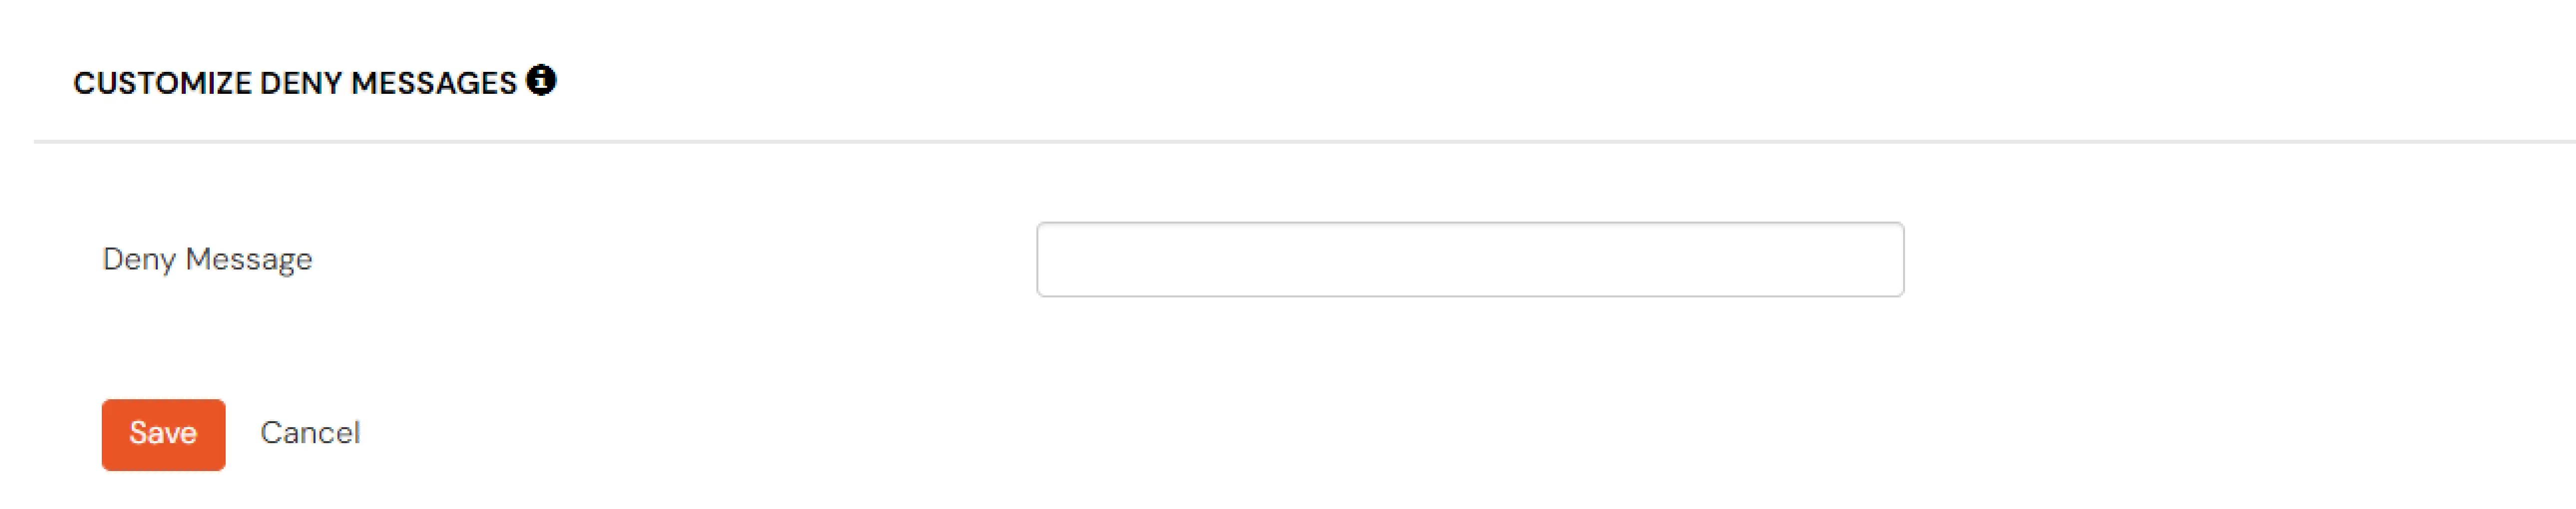
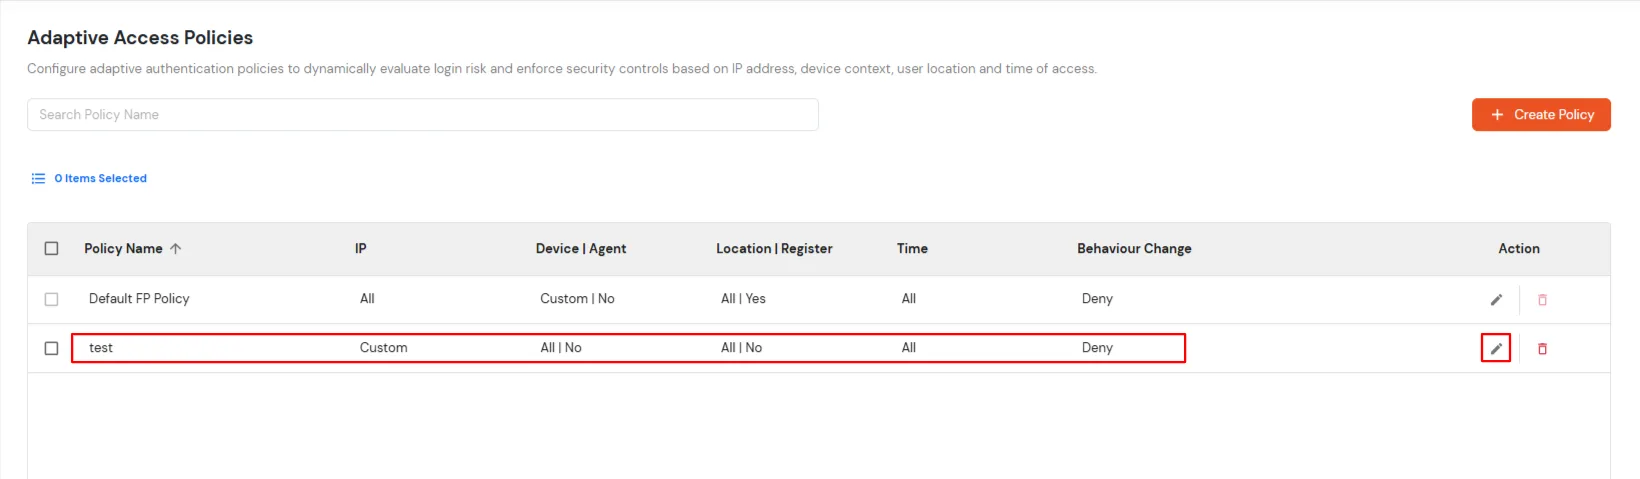
Review the configured policy conditions, behavior change actions, email alert settings and custom error messages before creating the adaptive authentication policy. This step provides a consolidated view of all configured settings, allowing you to verify the policy configuration and make any necessary changes before saving.
The most practical way to strengthen authentication is to require a second factor after the username/password stage. Since a password is something that a user knows, ensuring that the user also has something or using biometrics thwarts attackers that steal or gain access to passwords.
Traditional two-factor authentication solutions use hardware tokens (or "fobs") that users carry on their keychains. These tokens generate one-time passwords for the second stage of the login process. However, hardware tokens can cost up to $40 each. It takes time and effort to distribute them, tracks who has which one, and replace them when they break. They're easy to lose, hard to use, and users consistently report high levels of frustration with token-based systems.
miniOrange authentication service has 15+ authentication methods.
You can choose from any of the above authentication methods to augment your password based authentication. miniOrange authentication service works with all phone types, from landlines to smart-phone platforms. In the simplest case, users just answer a phone call and press a button to authenticate. miniOrange authentication service works internationally and has customers authenticating from many countries around the world.